
The website of the Toila SPA Hotell spa hotel — four pages, 425 requests. The CookieYes script loads, but there is no visitor decision in the capture, while the Meta pixel, Google Ads, Google Analytics and Google AdSense advertising run from the first seconds on every page, without consent mode and with the same identifiers throughout. In the booking system, the banner offers only 'Nõustun kõigiga'. The policy says nothing about cookies or about Meta and Google, does not link legal bases to purposes and lists rights incompletely.
Request timeline
Declared versus actual
Transfer timings
AdSense ad request, ca-pub-8077567627350879.
Google Ads ccm/collect, page_view without a consent state.
Meta pixel 226432978018098 PageView.
ads/ga-audiences with a client identifier.
PageView on the privacy policy page.
Google Ads, the same advertising identifier as on the first page.
Detected trackers
- Meta Pixel (226432978018098) — connect.facebook.net, www.facebook.com/tr; PageView at +2.5 s and on each of the four pages. Not named in the policy
- Google Ads AW-805168673 (www.google.com/ccm, ad.doubleclick.net) — on every page without consent mode, with a persistent advertising identifier
- Google Analytics 4 (G-02Q06JSVJ6) via region1.analytics.google.com, stats.g.doubleclick.net, www.google.ee/ads/ga-audiences — without consent mode, one client identifier across all pages
- Google AdSense (ca-pub-8077567627350879) — pagead2.googlesyndication.com, ep1/ep2.adtrafficquality.google; ad request and traffic check on every page
- Google Tag Manager (GTM-NM34R8M) — container on every page
- Meta Conversions API parameter script (unpkg.com/meta-capi-param-builder-clientjs)
- Cloudflare Turnstile (challenges.cloudflare.com), Google Fonts, unpkg, jsDelivr, jQuery CDN
- CookieYes (cdn-cookieyes.com) — the consent platform script loads; no decision in the capture
- First party: toilaspa.ee (WordPress)
Indicators of GDPR non-compliance
- ePrivacy — Directive 2002/58/EC, Art. 5(3) (in conjunction with GDPR Art. 6(1)(a)) — Meta pixel, Google Ads, Google Analytics and AdSense without consentThe CookieYes script loads at +0.9 s, but the tags do not wait for it, and there is no request carrying the visitor's decision in the capture. At +2.4 s Google Ads AW-805168673 sends a page view with an advertising identifier, at +2.5 s the Meta pixel (226432978018098) sends PageView with the page address, at +2.8 s Google Analytics 4 sends page_view with a client identifier. The same identifier goes to Google's advertising nodes stats.g.doubleclick.net and www.google.ee/ads/ga-audiences. At +2.1 s a Google AdSense ad is requested, followed by the adtrafficquality.google ad traffic check. Google's tags have no consent mode: the gcd parameter contains no set state, and there is no gcs parameter. All of this repeats on each of the four pages, with the same identifiers.
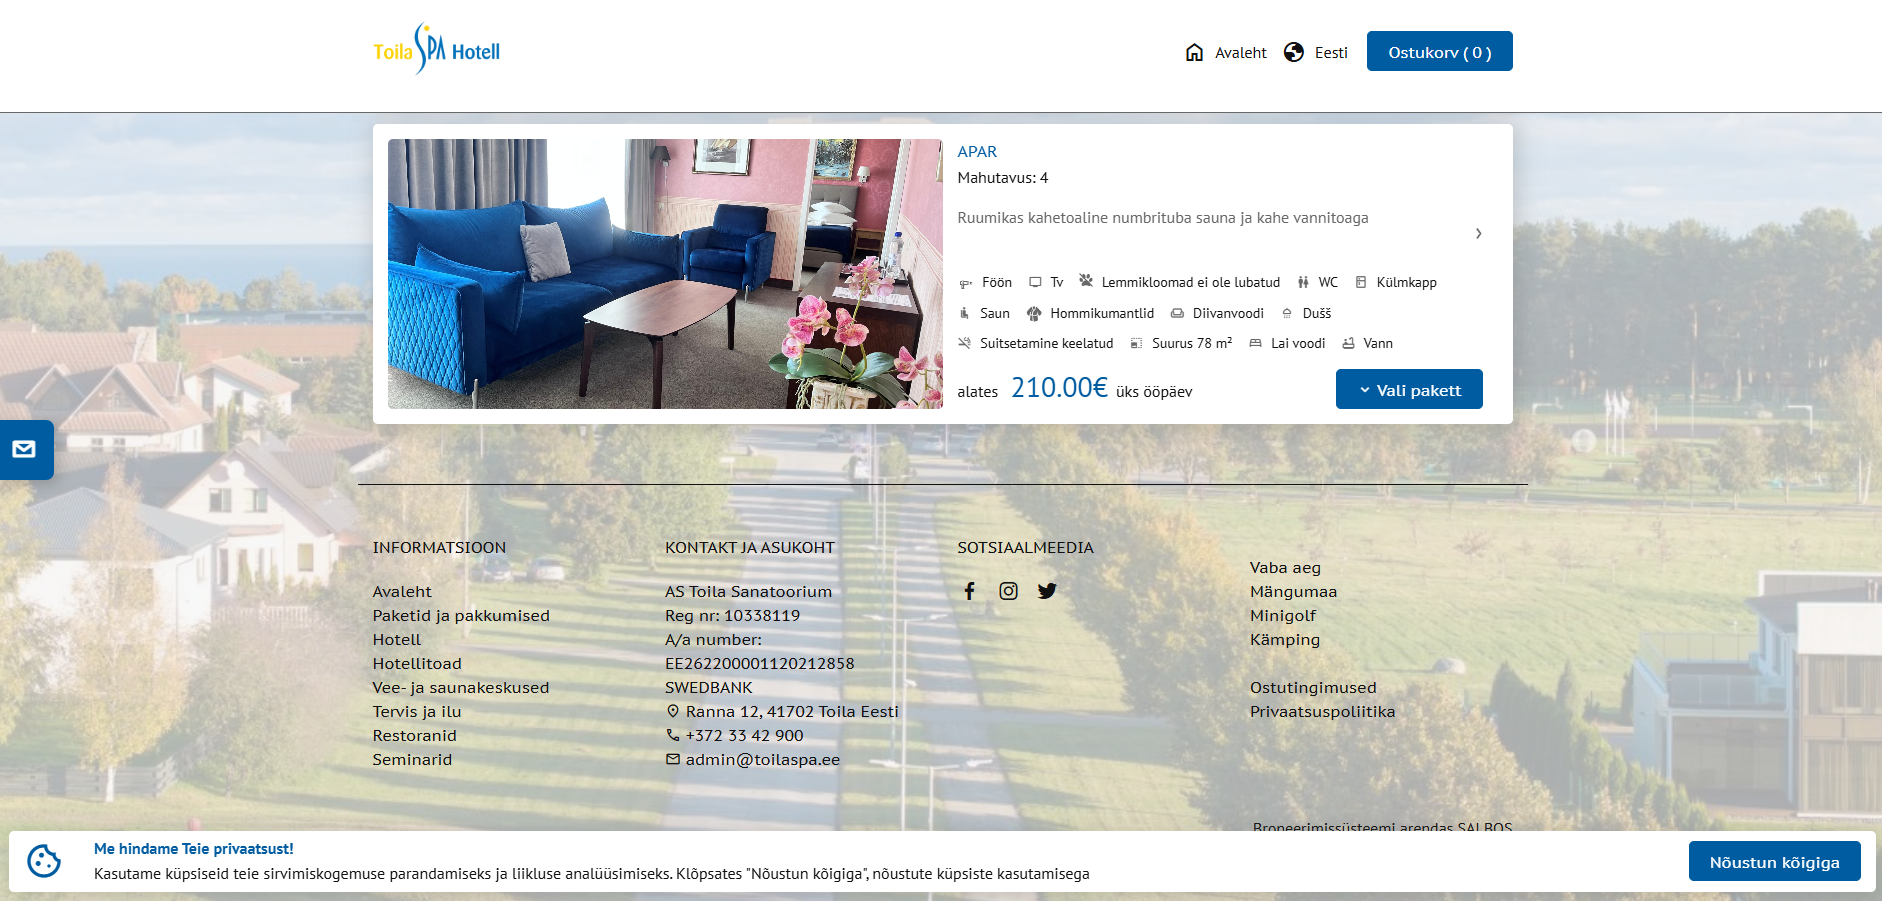
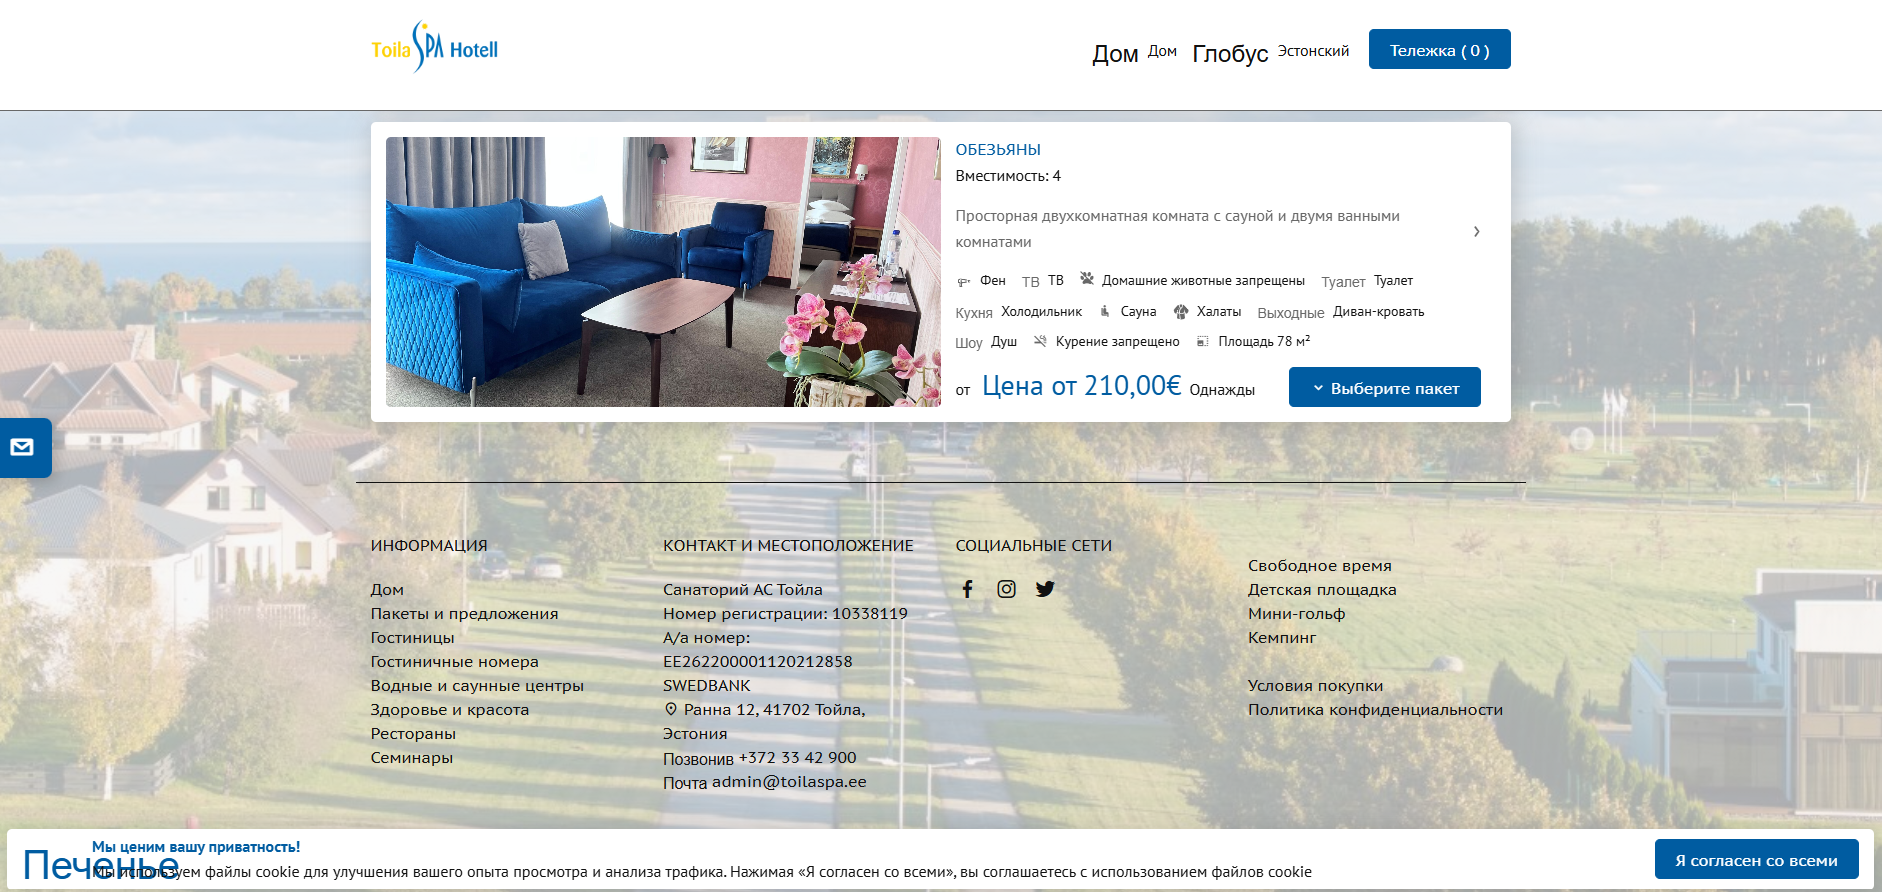
- GDPR Art. 4(11) / Art. 7(3) — no refusal in the booking systemIn the Toila SPA room booking system (developer SALBOS), the banner reads: 'Kasutame küpsiseid teie sirvimiskogemuse parandamiseks ja liikluse analüüsimiseks. Klõpsates „Nõustun kõigiga“, nõustute küpsiste kasutamisega.' There is one button — 'Nõustun kõigiga'. Refusing is impossible, neither on the first layer nor anywhere else in the banner. The Russian version is built the same way: a single button, 'Я согласен со всеми'.
- GDPR Art. 13(1)(c) — legal bases not linked to purposesThe policy of AS Toila Sanatoorium lists four legal bases — consent, contract, legal obligation and legitimate interest — in a single list, and separately lists six purposes, including marketing, but links no purpose to any basis. Which legitimate interest is pursued is not stated.
- GDPR Art. 13(1)(e), 13(1)(f) / Art. 5(1)(a) — Meta and Google not named, transfers to the US not describedThe policy names recipients by category and, by name, only Maksekeskus AS and Montonio Finance OÜ. It says not a word about cookies, web analytics or advertising. Meta, Google Ads, Google Analytics and Google AdSense, which in the capture receive visitor data on every page, are not named. The policy says nothing about data transfers outside the EU. Meanwhile, the terms of purchase claim that Toila SPA Hotell does not disclose a customer's personal data to other parties without the customer's consent.
- GDPR Art. 13(2)(b) — rights listed incompletelyThe policy names the rights of access, to information, to rectification and to withdraw consent. The rights to erasure, restriction of processing, objection and data portability are not mentioned.
Context
toilaspa.ee is the website of the Toila SPA Hotell spa hotel: rooms, packages, the water park and saunas, treatments, restaurants, seminars, a gift card shop and booking. The controller is AS Toila Sanatoorium (registration code 10338119, Ranna 12, Toila). The CookieYes consent platform script is connected on the site. Room booking runs in a separate system by the developer SALBOS, with its own banner.
The measurement is a single capture of four page loads: the homepage, the privacy policy, the terms of purchase, and the homepage again. In total, 425 requests, more than half of them to the site itself. The booking system is documented by screenshots.
Who receives data directly
Meta — through the pixel. Google — Ads, Analytics with the DoubleClick and ga-audiences advertising nodes, AdSense with an ad traffic check, Tag Manager, Fonts. Cloudflare — Turnstile. CookieYes — the consent platform script.
Declared versus actual
First — advertising without a choice. Two and a half seconds after entry, the Meta pixel sends a page view, Google Ads sends one with an advertising identifier, and Google Analytics sends one with a client identifier that immediately goes on to Google’s advertising nodes. At the same time, the site requests a Google AdSense ad. Google’s tags have no consent mode. This happens on every page, and the identifiers stay the same from page to page.
Second — no refusal in booking. The booking system banner states that pressing “Nõustun kõigiga” means consent, and offers no other button.
Third — the policy is silent about cookies and about who receives data. The AS Toila Sanatoorium policy names only two payment services. It has not a word about cookies, analytics or advertising, nor about Meta and Google, nor about transfers outside the EU. Meanwhile, the terms of purchase promise not to disclose customer data to other parties without the customer’s consent.
Fourth — legal bases and rights. Four legal bases are listed separately from the purposes. Of the rights, erasure, restriction, objection and portability are missing.
Consent: what is proven and what is not
Proven: the Meta pixel, Google Ads, Google Analytics and AdSense send data without a visitor decision. From +2.1 s on the first page and anew on each of the next three.
Proven: Google’s tags have no consent mode. The gcd parameter has no set states, and no request carries a gcs parameter.
Proven: there is no refusal in the booking system. Screenshots 3 and 4.
Proven: Meta and Google are not named in the policy. A search of the saved text.
Not established: whether the CookieYes banner was shown on toilaspa.ee. The script loads, but there are no decision requests in the capture, and no banner is visible on the homepage screenshot. This is not decisive for the conclusion: data leaves in the first seconds, before a visitor could choose anything.
Not established: what the booking system transmits. Its traffic is not part of the measurement.
Boundaries of this observation
The measurement covers public pages of toilaspa.ee. The shop, booking and payment are not in the capture; the booking system is documented only by screenshots. The observation records browser behavior, not server-side processing. The file has been published cleaned: Cookie headers and POST bodies were removed. Google identifiers are not reproduced in full in this review.
Legal assessment falls to the competent authority — the Andmekaitse Inspektsioon, which is named in the policy itself.
Conclusion
Toila SPA gives the visitor no choice. The Meta pixel, Google Ads, Google Analytics and AdSense advertising run from the first seconds on every page, with persistent identifiers, and the consent platform script has no effect on this. The booking system offers only a consent button. The policy says nothing about cookies or about Meta and Google, and the terms of purchase promise something the capture shows is not kept.
Remedy: configure CookieYes so that the Meta pixel, Google Ads, Google Analytics and AdSense do not load before consent, and enable Google consent mode with a denied default; add a refusal button to the booking system banner; add a cookie section to the policy, name Meta and Google as recipients, describe transfers outside the EU, link each purpose to a legal basis and list all data subject rights.
How to verify: download the file and compute its checksum — sha256sum file.har (Linux, macOS) or certutil -hashfile file.har SHA256 (Windows); it must match the one shown. The conclusions apply to the scope of this measurement — see the limitations of the method.
8c3878b8129bb4a37cf19d7cef91b6ab06ea690e46b6a4048c73d68412c97c95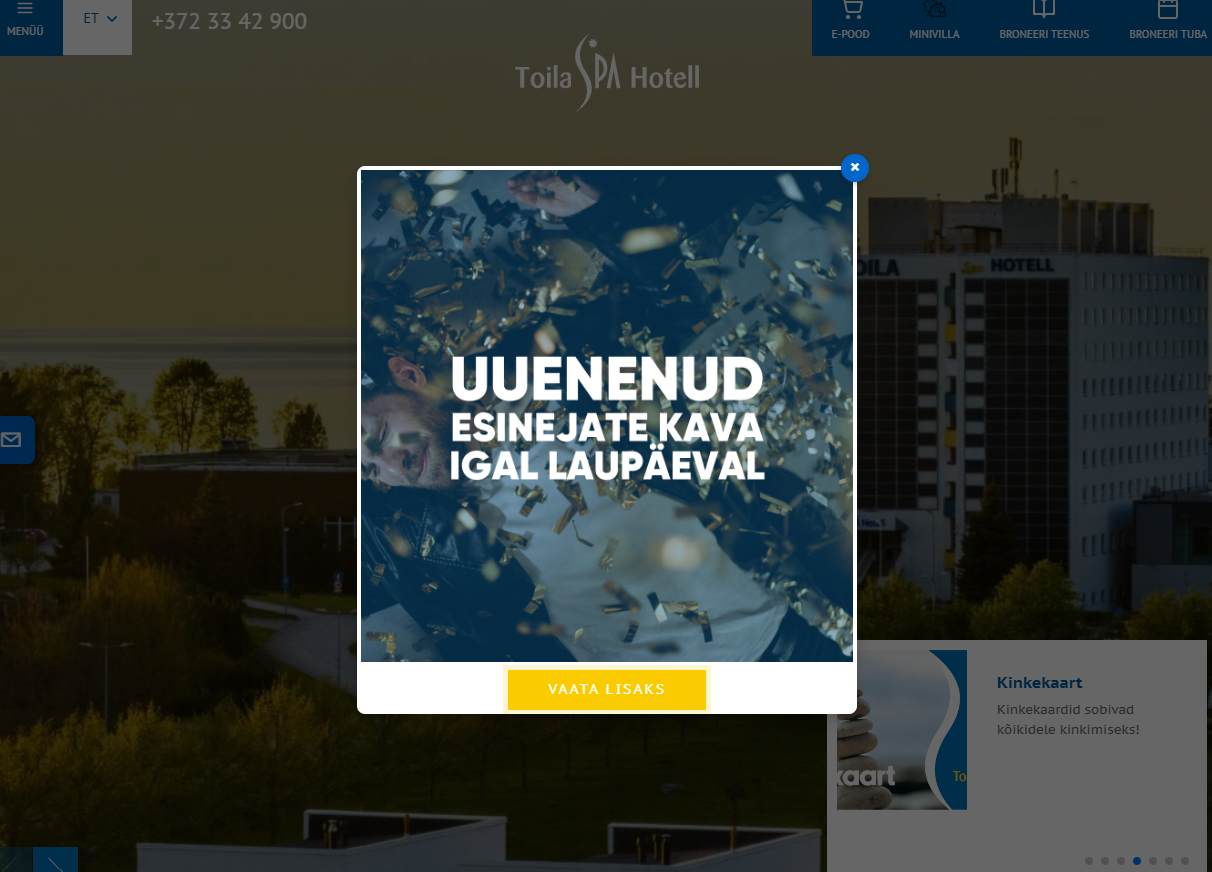
Want a response from the company about this audit? → Open the tool
Fill in once — it will be inserted into every letter below:
All fields are required to print the document — this is a formal requirement of the letter itself (the particulars of an official submission), not data collection: nothing is sent or saved anywhere, it all stays in your browser and disappears when you close the page. See the methodology for details.
RIA DigiDoc — phone · Smart-ID / Mobile-ID
Send this letter directly to the company first — before contacting the regulator it has the right to respond (GDPR Art. 12(3) — 30 days).
Тема: Запрос доступа к персональным данным (ст. 15 GDPR) — toilaspa.ee

Кому: [укажите адрес компании — DPO / поддержка / юридический отдел]
От: [Ваше имя], [контактный email]

Прошу предоставить доступ к моим персональным данным, обрабатываемым в связи с использованием сайта toilaspa.ee.

1. Категории данных и цели обработки (ст. 15(1)(a)-(c))
На основании независимого технического анализа сайта прошу подтвердить и подробно раскрыть следующие категории обработки:

1) Сценарий CookieYes загружается на +0,9 с, но теги его не ждут, и запроса с решением посетителя в записи нет. На +2,4 с Google Ads AW-805168673 отправляет просмотр страницы с рекламным идентификатором, на +2,5 с пиксель Meta (226432978018098) отправляет PageView с адресом страницы, на +2,8 с Google Analytics 4 отправляет page_view с идентификатором клиента. Тот же идентификатор уходит на рекламные узлы Google stats.g.doubleclick.net и www.google.ee/ads/ga-audiences. На +2,1 с запрашивается реклама Google AdSense, затем подключается проверка рекламного трафика adtrafficquality.google. Режима согласия у тегов Google нет: параметр gcd не содержит ни одного заданного состояния, параметра gcs нет. Всё это повторяется на каждой из четырёх страниц, с одними и теми же идентификаторами.

2) В системе бронирования номеров Toila SPA (разработчик SALBOS) баннер гласит: «Kasutame küpsiseid teie sirvimiskogemuse parandamiseks ja liikluse analüüsimiseks. Klõpsates „Nõustun kõigiga“, nõustute küpsiste kasutamisega.» Кнопка одна — «Nõustun kõigiga». Отказаться нельзя ни на первом слое, ни где-либо ещё в баннере. Так же устроена русская версия: единственная кнопка «Я согласен со всеми».

3) Политика AS Toila Sanatoorium перечисляет четыре основания — согласие, договор, юридическую обязанность и законный интерес — одним списком и отдельно от этого перечисляет шесть целей, включая маркетинг, но не связывает ни одну цель ни с одним основанием. Какой именно законный интерес преследуется, не сказано.

4) Политика называет получателей категориями и по имени — только Maksekeskus AS и Montonio Finance OÜ. О cookie, веб-аналитике и рекламе в ней нет ни слова. Meta, Google Ads, Google Analytics и Google AdSense, которые в замере получают данные посетителя на каждой странице, не названы. О передаче данных за пределы ЕС политика не говорит ничего. Условия покупки при этом утверждают, что Toila SPA Hotell не раскрывает персональные данные клиента другим сторонам без его согласия.

5) Политика называет право на доступ, на информацию, на исправление и на отзыв согласия. Права на удаление, ограничение обработки, возражение и переносимость данных не упомянуты.


2. Получатели, сроки хранения и передача за пределы ЕЭЗ (ст. 15(1)(c)-(d), 46)
Прошу также указать полный список третьих лиц-получателей, применимые сроки хранения по каждой категории и правовые основания передачи данных за пределы ЕЭЗ, если таковая происходит. Полный технический разбор с доказательствами (сохранённый сетевой журнал, контрольная сумма SHA-256) опубликован по адресу: https://gdpru.eu/en/audits/ee-toilaspa-ee/

3. Автоматизированная обработка и профилирование (ст. 15(1)(h))
Прошу сообщить, применяется ли в отношении меня автоматизированное принятие решений или профилирование, и если да — раскрыть логику такой обработки.

С уважением,

[Ваше имя]
[контактный email]
[Страна]


[Дата]
Subject: Data access request (GDPR Art. 15) — toilaspa.ee

To: [insert the company's address — DPO / support / legal department]
From: [Your name], [contact email]

I request access to my personal data processed in connection with the website toilaspa.ee.

1. Categories of data and purposes of processing (Art. 15(1)(a)-(c))
Based on an independent technical analysis of the site, I request confirmation and detailed disclosure of the following categories of processing:

1) The CookieYes script loads at +0.9 s, but the tags do not wait for it, and there is no request carrying the visitor's decision in the capture. At +2.4 s Google Ads AW-805168673 sends a page view with an advertising identifier, at +2.5 s the Meta pixel (226432978018098) sends PageView with the page address, at +2.8 s Google Analytics 4 sends page_view with a client identifier. The same identifier goes to Google's advertising nodes stats.g.doubleclick.net and www.google.ee/ads/ga-audiences. At +2.1 s a Google AdSense ad is requested, followed by the adtrafficquality.google ad traffic check. Google's tags have no consent mode: the gcd parameter contains no set state, and there is no gcs parameter. All of this repeats on each of the four pages, with the same identifiers.

2) In the Toila SPA room booking system (developer SALBOS), the banner reads: 'Kasutame küpsiseid teie sirvimiskogemuse parandamiseks ja liikluse analüüsimiseks. Klõpsates „Nõustun kõigiga“, nõustute küpsiste kasutamisega.' There is one button — 'Nõustun kõigiga'. Refusing is impossible, neither on the first layer nor anywhere else in the banner. The Russian version is built the same way: a single button, 'Я согласен со всеми'.

3) The policy of AS Toila Sanatoorium lists four legal bases — consent, contract, legal obligation and legitimate interest — in a single list, and separately lists six purposes, including marketing, but links no purpose to any basis. Which legitimate interest is pursued is not stated.

4) The policy names recipients by category and, by name, only Maksekeskus AS and Montonio Finance OÜ. It says not a word about cookies, web analytics or advertising. Meta, Google Ads, Google Analytics and Google AdSense, which in the capture receive visitor data on every page, are not named. The policy says nothing about data transfers outside the EU. Meanwhile, the terms of purchase claim that Toila SPA Hotell does not disclose a customer's personal data to other parties without the customer's consent.

5) The policy names the rights of access, to information, to rectification and to withdraw consent. The rights to erasure, restriction of processing, objection and data portability are not mentioned.


2. Recipients, retention periods, and transfers outside the EEA (Art. 15(1)(c)-(d), 46)
I also request the full list of third-party recipients, the applicable retention period for each category, and the legal basis for any transfer of data outside the EEA. The full technical audit with evidence (saved network log, SHA-256 checksum) is published at: https://gdpru.eu/en/audits/ee-toilaspa-ee/

3. Automated processing and profiling (Art. 15(1)(h))
Please state whether I am subject to automated decision-making or profiling, and if so, disclose the logic involved.

Sincerely,

[Your name]
[contact email]
[Country]


[Date]
Teema: Isikuandmetele juurdepääsu taotlus (IKÜM art 15) — toilaspa.ee

Kellele: [märkige ettevõtte aadress — DPO / tugi / juriidiline osakond]
Kellelt: [Teie nimi], [kontakt-e-post]

Palun anda mulle juurdepääs minu isikuandmetele, mida töödeldakse seoses veebisaidi toilaspa.ee kasutamisega.

1. Andmekategooriad ja töötlemise eesmärgid (IKÜM art 15(1)(a)-(c))
Sõltumatu tehnilise analüüsi põhjal palun kinnitada ja üksikasjalikult avaldada järgmised töötlemiskategooriad:

1) CookieYesi skript laaditakse +0,9 s juures, kuid sildid seda ei oota ning külastaja otsusega päringut salvestuses ei ole. +2,4 s juures saadab Google Ads AW-805168673 lehevaatamise koos reklaamiidentifikaatoriga, +2,5 s juures saadab Meta piksel (226432978018098) sündmuse PageView koos lehe aadressiga, +2,8 s juures saadab Google Analytics 4 page_view sündmuse koos kliendiidentifikaatoriga. Sama identifikaator saadetakse Google'i reklaamisõlmedele stats.g.doubleclick.net ja www.google.ee/ads/ga-audiences. +2,1 s juures küsitakse Google AdSense'i reklaami ning seejärel lülitub sisse reklaamiliikluse kontroll adtrafficquality.google. Google'i siltidel puudub nõusolekurežiim: parameeter gcd ei sisalda ühtegi määratud olekut ja parameeter gcs puudub. Kõik see kordub kõigil neljal lehel samade identifikaatoritega.

2) Toila SPA toabroneerimissüsteemis (arendaja SALBOS) ütleb bänner: „Kasutame küpsiseid teie sirvimiskogemuse parandamiseks ja liikluse analüüsimiseks. Klõpsates „Nõustun kõigiga“, nõustute küpsiste kasutamisega.“ Nuppe on üks – „Nõustun kõigiga“. Keelduda ei saa ei esimesel kihil ega mujal bänneris. Samamoodi on üles ehitatud venekeelne versioon: ainus nupp „Я согласен со всеми“.

3) AS Toila Sanatoorium'i privaatsuspoliitika loetleb neli alust – nõusolek, leping, juriidiline kohustus ja õigustatud huvi – ühes loetelus ning eraldi kuus eesmärki, sh turundus, kuid ei seo ühtegi eesmärki ühegi alusega. Millist õigustatud huvi järgitakse, ei ole öeldud.

4) Poliitika nimetab vastuvõtjaid kategooriatena ja nimeliselt ainult Maksekeskus AS-i ja Montonio Finance OÜ-d. Küpsistest, veebianalüütikast ja reklaamist ei ole selles sõnagi. Metat, Google Adsi, Google Analyticsit ja Google AdSense'i, kes mõõtmise käigus saavad igal lehel külastaja andmeid, ei nimetata. Andmete edastamisest väljapoole ELi poliitika ei räägi. Samal ajal väidavad ostutingimused, et Toila SPA Hotell ei avalikusta kliendi isikuandmeid teistele osapooltele ilma Kliendi nõusolekuta.

5) Poliitika nimetab õigust tutvuda andmetega, saada teavet, parandada andmeid ja võtta nõusolek tagasi. Õigust andmete kustutamisele, töötlemise piiramisele, vastuväidete esitamisele ja andmete ülekandmisele ei mainita.


2. Vastuvõtjad, säilitustähtajad ja edastamine väljapoole EMP-d (IKÜM art 15(1)(c)-(d), 46)
Palun samuti esitada täielik loetelu kolmandatest isikutest vastuvõtjatest, iga kategooria puhul kohaldatavad säilitustähtajad ning andmete EMP-välisele edastamisele kohaldatav õiguslik alus, kui selline edastamine toimub. Täielik tehniline analüüs koos tõenditega (salvestatud võrgulogi, SHA-256 kontrollsumma) on avaldatud aadressil: https://gdpru.eu/en/audits/ee-toilaspa-ee/

3. Automatiseeritud töötlemine ja profiilianalüüs (IKÜM art 15(1)(h))
Palun teatada, kas minu suhtes kohaldatakse automatiseeritud otsuste tegemist või profiilianalüüsi, ning kui jah, siis avaldada selle loogika.

Lugupidamisega,

[Teie nimi]
[kontakt-e-post]
[Riik]


[Kuupäev]
RIA DigiDoc — phone · Smart-ID / Mobile-ID
Where to file: Estonian Data Protection Inspectorate (AKI) — write to info@aki.ee
Important: AKI only handles submissions in Estonian. Translate the letter before sending.
The regulator reviews complaints in its national language. There is an officially translated template from the European Data Protection Board (EDPB) — you can use it instead of or alongside this letter: Official EDPB complaint form (PDF, your language)
Тема: Жалоба на обработку персональных данных — toilaspa.ee

1. Предмет жалобы
Я подаю жалобу в отношении обработки моих персональных данных сайтом toilaspa.ee.

2. Обстоятельства
Я посетил сайт toilaspa.ee и обнаружил признаки несоответствия обработки моих персональных данных требованиям GDPR. Технический разбор, опубликованный на gdpru.eu 08.10.2026 (открытая методология, воспроизводимые измерения), документирует следующие признаки:

1) Сценарий CookieYes загружается на +0,9 с, но теги его не ждут, и запроса с решением посетителя в записи нет. На +2,4 с Google Ads AW-805168673 отправляет просмотр страницы с рекламным идентификатором, на +2,5 с пиксель Meta (226432978018098) отправляет PageView с адресом страницы, на +2,8 с Google Analytics 4 отправляет page_view с идентификатором клиента. Тот же идентификатор уходит на рекламные узлы Google stats.g.doubleclick.net и www.google.ee/ads/ga-audiences. На +2,1 с запрашивается реклама Google AdSense, затем подключается проверка рекламного трафика adtrafficquality.google. Режима согласия у тегов Google нет: параметр gcd не содержит ни одного заданного состояния, параметра gcs нет. Всё это повторяется на каждой из четырёх страниц, с одними и теми же идентификаторами.

2) В системе бронирования номеров Toila SPA (разработчик SALBOS) баннер гласит: «Kasutame küpsiseid teie sirvimiskogemuse parandamiseks ja liikluse analüüsimiseks. Klõpsates „Nõustun kõigiga“, nõustute küpsiste kasutamisega.» Кнопка одна — «Nõustun kõigiga». Отказаться нельзя ни на первом слое, ни где-либо ещё в баннере. Так же устроена русская версия: единственная кнопка «Я согласен со всеми».

3) Политика AS Toila Sanatoorium перечисляет четыре основания — согласие, договор, юридическую обязанность и законный интерес — одним списком и отдельно от этого перечисляет шесть целей, включая маркетинг, но не связывает ни одну цель ни с одним основанием. Какой именно законный интерес преследуется, не сказано.

4) Политика называет получателей категориями и по имени — только Maksekeskus AS и Montonio Finance OÜ. О cookie, веб-аналитике и рекламе в ней нет ни слова. Meta, Google Ads, Google Analytics и Google AdSense, которые в замере получают данные посетителя на каждой странице, не названы. О передаче данных за пределы ЕС политика не говорит ничего. Условия покупки при этом утверждают, что Toila SPA Hotell не раскрывает персональные данные клиента другим сторонам без его согласия.

5) Политика называет право на доступ, на информацию, на исправление и на отзыв согласия. Права на удаление, ограничение обработки, возражение и переносимость данных не упомянуты.

Полная техническая документация опубликована по адресу: https://gdpru.eu/en/audits/ee-toilaspa-ee/

3. Положения GDPR, соблюдение которых прошу проверить
ePrivacy — Директива 2002/58/EC, ст. 5(3) (в связке с GDPR Art. 6(1)(a)) — пиксель Meta, Google Ads, Google Analytics и AdSense без согласия; GDPR Art. 4(11) / Art. 7(3) — в системе бронирования отказа нет; GDPR Art. 13(1)(c) — основания не связаны с целями; GDPR Art. 13(1)(e), 13(1)(f) / Art. 5(1)(a) — Meta и Google не названы, передача в США не описана; GDPR Art. 13(2)(b) — права перечислены не полностью

4. Требование
Прошу проверить изложенные обстоятельства и, если несоответствие подтвердится, принять меры, предусмотренные статьёй 58(2) GDPR.

5. Приложения
Полная доказательная база — HAR-файл, контрольная сумма SHA-256 и цитата из политики конфиденциальности сайта, документирующая указанное противоречие — опубликована и проверяема по ссылке в пункте 2 выше.

С уважением,

[Ваше имя]
[контактный email]
[Страна]


[Дата]
Subject: Complaint regarding personal data processing — toilaspa.ee

1. Subject of the complaint
I am filing a complaint regarding the processing of my personal data by the website toilaspa.ee.

2. Circumstances
I visited the website toilaspa.ee and found indications that the processing of my personal data does not comply with the GDPR. The technical analysis published on gdpru.eu on 8 October 2026 (open methodology, reproducible measurements) documents the following indications:

1) The CookieYes script loads at +0.9 s, but the tags do not wait for it, and there is no request carrying the visitor's decision in the capture. At +2.4 s Google Ads AW-805168673 sends a page view with an advertising identifier, at +2.5 s the Meta pixel (226432978018098) sends PageView with the page address, at +2.8 s Google Analytics 4 sends page_view with a client identifier. The same identifier goes to Google's advertising nodes stats.g.doubleclick.net and www.google.ee/ads/ga-audiences. At +2.1 s a Google AdSense ad is requested, followed by the adtrafficquality.google ad traffic check. Google's tags have no consent mode: the gcd parameter contains no set state, and there is no gcs parameter. All of this repeats on each of the four pages, with the same identifiers.

2) In the Toila SPA room booking system (developer SALBOS), the banner reads: 'Kasutame küpsiseid teie sirvimiskogemuse parandamiseks ja liikluse analüüsimiseks. Klõpsates „Nõustun kõigiga“, nõustute küpsiste kasutamisega.' There is one button — 'Nõustun kõigiga'. Refusing is impossible, neither on the first layer nor anywhere else in the banner. The Russian version is built the same way: a single button, 'Я согласен со всеми'.

3) The policy of AS Toila Sanatoorium lists four legal bases — consent, contract, legal obligation and legitimate interest — in a single list, and separately lists six purposes, including marketing, but links no purpose to any basis. Which legitimate interest is pursued is not stated.

4) The policy names recipients by category and, by name, only Maksekeskus AS and Montonio Finance OÜ. It says not a word about cookies, web analytics or advertising. Meta, Google Ads, Google Analytics and Google AdSense, which in the capture receive visitor data on every page, are not named. The policy says nothing about data transfers outside the EU. Meanwhile, the terms of purchase claim that Toila SPA Hotell does not disclose a customer's personal data to other parties without the customer's consent.

5) The policy names the rights of access, to information, to rectification and to withdraw consent. The rights to erasure, restriction of processing, objection and data portability are not mentioned.

Full technical documentation is published at: https://gdpru.eu/en/audits/ee-toilaspa-ee/

3. GDPR provisions I ask you to examine
ePrivacy — Directive 2002/58/EC, Art. 5(3) (in conjunction with GDPR Art. 6(1)(a)) — Meta pixel, Google Ads, Google Analytics and AdSense without consent; GDPR Art. 4(11) / Art. 7(3) — no refusal in the booking system; GDPR Art. 13(1)(c) — legal bases not linked to purposes; GDPR Art. 13(1)(e), 13(1)(f) / Art. 5(1)(a) — Meta and Google not named, transfers to the US not described; GDPR Art. 13(2)(b) — rights listed incompletely

4. Request
I request that you examine the circumstances described and, if non-compliance is confirmed, apply the measures provided for in Article 58(2) GDPR.

5. Attachments
The full evidence base — the HAR file, its SHA-256 checksum and the quotation from the site's privacy policy documenting the stated contradiction — is published and verifiable at the link in point 2 above.

Sincerely,

[Your name]
[contact email]
[Country]


[Date]
1. Kaebuse ese
Esitan kaebuse seoses minu isikuandmete töötlemisega veebisaidil toilaspa.ee.

2. Asjaolud
Külastasin veebisaiti toilaspa.ee ja tuvastasin märke sellest, et minu isikuandmete töötlemine ei vasta isikuandmete kaitse üldmääruse (IKÜM) nõuetele. Tehniline analüüs, mis on avaldatud aadressil gdpru.eu 08.10.2026 (avatud metoodika, korratavad mõõtmised), dokumenteerib järgmist:

1) CookieYesi skript laaditakse +0,9 s juures, kuid sildid seda ei oota ning külastaja otsusega päringut salvestuses ei ole. +2,4 s juures saadab Google Ads AW-805168673 lehevaatamise koos reklaamiidentifikaatoriga, +2,5 s juures saadab Meta piksel (226432978018098) sündmuse PageView koos lehe aadressiga, +2,8 s juures saadab Google Analytics 4 page_view sündmuse koos kliendiidentifikaatoriga. Sama identifikaator saadetakse Google'i reklaamisõlmedele stats.g.doubleclick.net ja www.google.ee/ads/ga-audiences. +2,1 s juures küsitakse Google AdSense'i reklaami ning seejärel lülitub sisse reklaamiliikluse kontroll adtrafficquality.google. Google'i siltidel puudub nõusolekurežiim: parameeter gcd ei sisalda ühtegi määratud olekut ja parameeter gcs puudub. Kõik see kordub kõigil neljal lehel samade identifikaatoritega.

2) Toila SPA toabroneerimissüsteemis (arendaja SALBOS) ütleb bänner: „Kasutame küpsiseid teie sirvimiskogemuse parandamiseks ja liikluse analüüsimiseks. Klõpsates „Nõustun kõigiga“, nõustute küpsiste kasutamisega.“ Nuppe on üks – „Nõustun kõigiga“. Keelduda ei saa ei esimesel kihil ega mujal bänneris. Samamoodi on üles ehitatud venekeelne versioon: ainus nupp „Я согласен со всеми“.

3) AS Toila Sanatoorium'i privaatsuspoliitika loetleb neli alust – nõusolek, leping, juriidiline kohustus ja õigustatud huvi – ühes loetelus ning eraldi kuus eesmärki, sh turundus, kuid ei seo ühtegi eesmärki ühegi alusega. Millist õigustatud huvi järgitakse, ei ole öeldud.

4) Poliitika nimetab vastuvõtjaid kategooriatena ja nimeliselt ainult Maksekeskus AS-i ja Montonio Finance OÜ-d. Küpsistest, veebianalüütikast ja reklaamist ei ole selles sõnagi. Metat, Google Adsi, Google Analyticsit ja Google AdSense'i, kes mõõtmise käigus saavad igal lehel külastaja andmeid, ei nimetata. Andmete edastamisest väljapoole ELi poliitika ei räägi. Samal ajal väidavad ostutingimused, et Toila SPA Hotell ei avalikusta kliendi isikuandmeid teistele osapooltele ilma Kliendi nõusolekuta.

5) Poliitika nimetab õigust tutvuda andmetega, saada teavet, parandada andmeid ja võtta nõusolek tagasi. Õigust andmete kustutamisele, töötlemise piiramisele, vastuväidete esitamisele ja andmete ülekandmisele ei mainita.

Täielik tehniline dokumentatsioon on avaldatud aadressil: https://gdpru.eu/en/audits/ee-toilaspa-ee/

3. Sätted, mille järgimist palun kontrollida
Eraelu puutumatust ja elektroonilist sidet käsitlev direktiiv 2002/58/EÜ art 5 lg 3 (koostoimes IKÜM art 6 lg 1 p-ga a) — Meta piksel, Google Ads, Google Analytics ja AdSense ilma nõusolekuta; IKÜM art 4 p 11 / art 7 lg 3 — broneerimissüsteemis puudub keeldumine; IKÜM art 13 lg 1 p c — alused ei ole seotud eesmärkidega; IKÜM art 13 lg 1 p e, f / art 5 lg 1 p a — Meta ja Google on nimetamata, edastamine USAsse on kirjeldamata; IKÜM art 13 lg 2 p b — õigused on loetletud mittetäielikult

4. Nõue
Palun kontrollida kirjeldatud asjaolusid ja mittevastavuse kinnitamisel kohaldada IKÜM artikli 58 lõikes 2 ette nähtud meetmeid.

5. Lisad
Täielik tõendusmaterjal — HAR-fail, kontrollsumma SHA-256 ning veebisaidi privaatsuspoliitika tsitaat, mis dokumenteerib nimetatud vastuolu — on avaldatud ja kontrollitav punktis 2 viidatud lingil.

Lugupidamisega,

[Teie nimi]
[kontakt-e-post]
[Riik]


[Kuupäev]