
The site of the pizza chain Peetri Pizza — a single capture of an order page, 43 requests, 8 nodes. The case is close to exemplary: the CookieYes consent management platform loads first, the banner offers refusal on the first screen («Keeldu kõigist») alongside «Nõustun kõigiga», and the categories in the settings are off by default. Google analytics respect the denial — the GA4 events carry status gcs=G100, cookieless; Facebook loads only the SDK without pixel events. The policy is detailed and names all recipients individually, including the Facebook Pixel. The only caveat is that the Facebook SDK and the GA requests load before the choice is recorded (but under denial).
Request timeline
Declared versus actual
Transfer timings
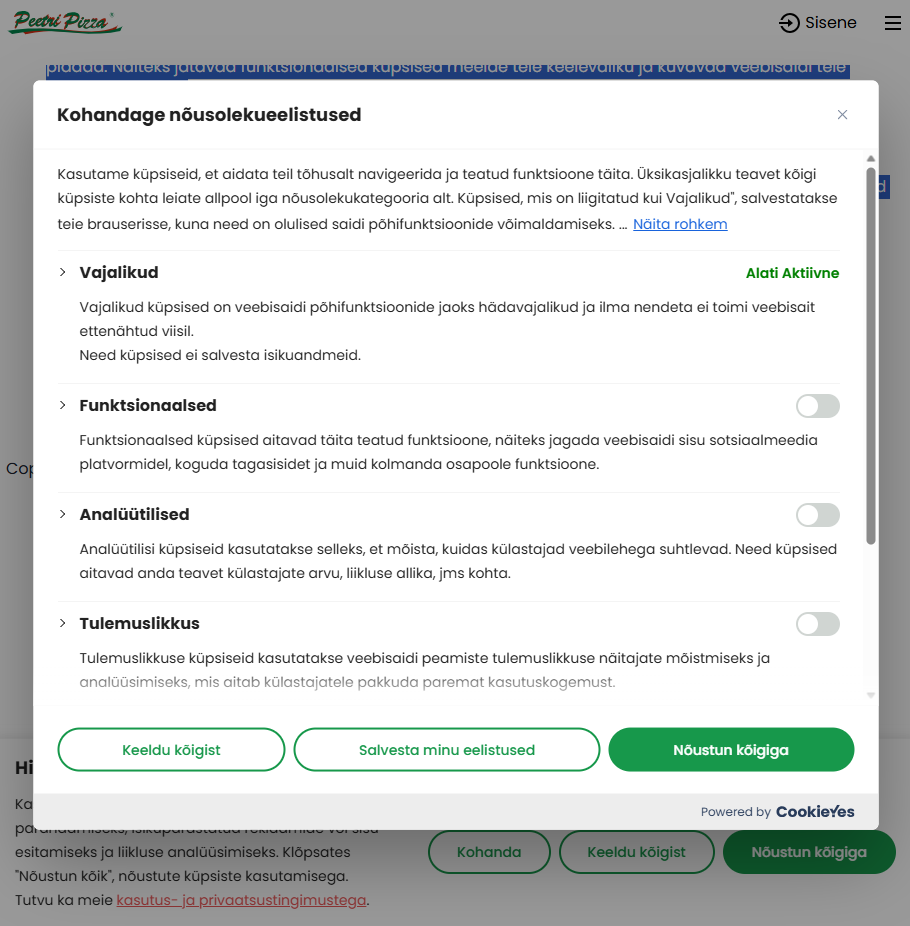
Consent platform; a banner with «Keeldu kõigist» on the first screen.
fbevents.js; the _fbp cookie is named in the policy.
GA4 page_view, gcs=G100.
Detected trackers
- CookieYes (cdn-cookieyes.com, log.cookieyes.com, ID 63bea1e1…) — consent management platform; loads first (+188 ms), a banner with three buttons («Kohanda» / «Keeldu kõigist» / «Nõustun kõigiga»), categories off by default — refusal on the first screen. Named in the policy
- Google Analytics 4 (region1.google-analytics.com) — analytics; the page_view, first_visit, session_start and measurement/conversion events carry status gcs=G100 (both storages denied), cookieless. The denial is respected. Named in the policy
- Facebook / Meta (connect.facebook.net) — only the SDK fbevents.js loads (+189 ms); no pixel /tr events observed in the capture. The _fbp cookie is named in the policy (Facebook Pixel, showing advertising)
- Google Tag Manager (www.googletagmanager.com) — tag container; +188 ms
- First party and infrastructure: peetripizza.ee (Laravel, behind Cloudflare), Google fonts, reCAPTCHA (form protection)
Context
peetripizza.ee is the site of the pizza-delivery chain Peetri Pizza (controller — PP Trading OÜ, contact paula@peetripizza.ee). The site runs on Laravel and is served via Cloudflare. The processing is described by a detailed policy and cookie declaration running on the CookieYes engine; consent is managed by CookieYes.
The capture is a single recording of an order page (/telli/…, adding a combo): 43 requests, 8 nodes.
Who data goes to directly
Analytics — Google Analytics 4 (under denial, gcs=G100, cookieless). Consent management — CookieYes. Facebook loads only the SDK, without events. Functionally — reCAPTCHA (form protection), fonts. The first party is the Laravel site behind Cloudflare.
Declared versus actual
Here the declared and the actual agree — a tidy case.
The consent mechanism is exemplary. The CookieYes platform loads first (+188 ms), the banner «Hindame teie privaatsust» offers three buttons — «Kohanda», «Keeldu kõigist» (reject all), «Nõustun kõigiga» — with refusal on the first screen equivalent to consent. In the settings the Funktsionaalsed, Analüütilised, Tulemuslikkus categories are off by default (not pre-ticked). As for the consent mechanism there is no complaint.
Google analytics respect the denial. The GA4 events — page_view, first_visit, session_start, measurement/conversion — carry status gcs=G100: both storages denied, pings cookieless. One event carries the address of a pizzeria page (dl=/pizzeria/aardla), but without a cookie binding. This is correct behaviour when consent has not been given.
Facebook is present only as an SDK. connect.facebook.net/fbevents.js loads at +189 ms, but there are no pixel /tr events in the capture — the pixel is initialised but transferred no data.
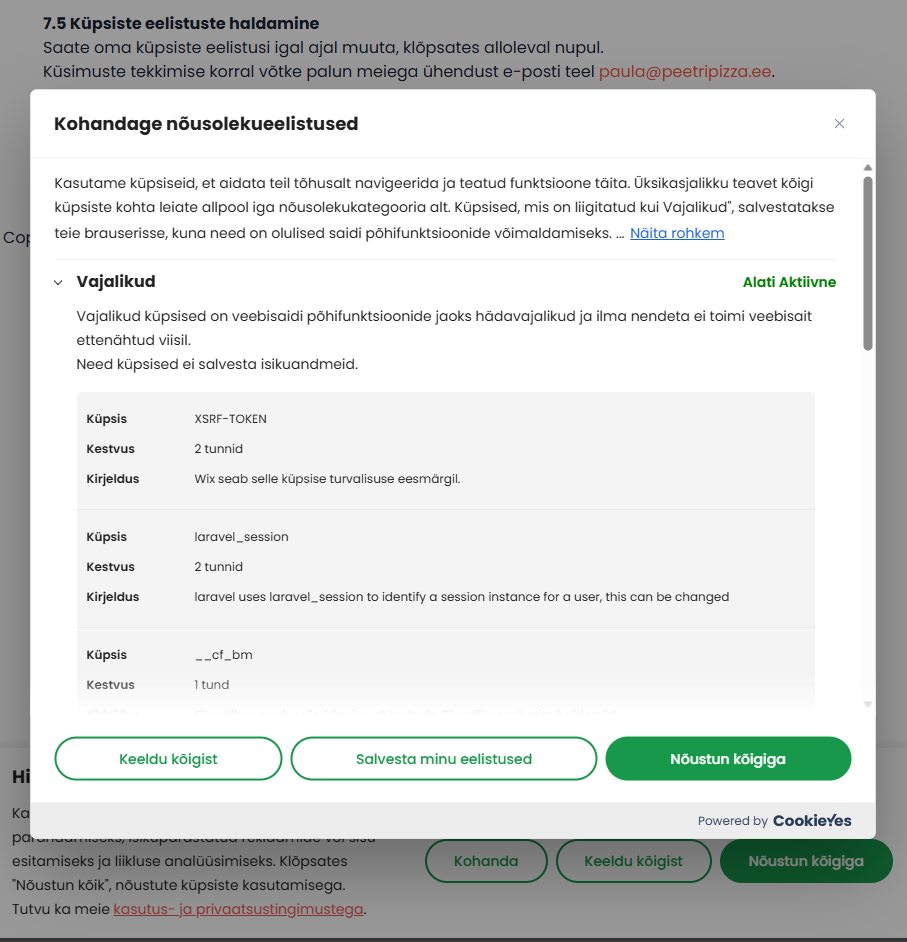
Recipients are disclosed individually. The policy and cookie declaration name them all: CookieYes, Google reCAPTCHA, Google Analytics, Facebook (with the _fbp cookie — Facebook Pixel, «showing advertising»), Wix, Laravel, Cloudflare — with categories and retention periods. Disclosure at a good level.
The only caveat is the load order. The Facebook SDK (+189 ms) and the GA requests (+869 ms) load before the user’s choice is recorded in the banner. No actual transfer was recorded, however: GA runs under denial (gcs=G100, cookieless), and the Facebook SDK sent no events. This is a caveat about initialisation order, not a transfer of data before consent; the clean fix is to gate the loading of the SDK and the GA requests until the choice.
Consent: what is proven and what is not
Proven: the CMP loads first. CookieYes — +188 ms, before the rest of the stack.
Proven: the banner offers refusal on the first screen. The screenshots record «Keeldu kõigist» and the categories off by default.
Proven: analytics respect the denial. All GA4 requests carry gcs=G100, cookielessly.
Proven: Facebook is only the SDK, without events. In the capture there is only fbevents.js, no /tr requests.
Proven: recipients are named. The policy lists CookieYes, Google, Facebook, Wix, Laravel, Cloudflare individually.
Not established: the consent decision. The choice is not recorded in the capture; gcs=G100 indicates a denied state (by default or by refusal).
Observation boundaries
The capture covers the order page and records browser behaviour, not server-side processing: what Google does with the received (storage-denied) signals is not verified by a browser capture. Facebook is named in the policy, but in the capture it only loaded the SDK without events — the pixel’s actual activity in this session was not observed. reCAPTCHA and fonts are attributed to the functional part.
The file is published cleaned of personal data (39 redactions, self-check clean; the URL parameters of the order page redacted); the load order (CookieYes first), the gcs=G100 status of GA and the absence of Facebook /tr events can be verified directly against the published file and the screenshots. The banner and the settings are from the screenshots (live UI).
The legal assessment is made by the competent authority — Andmekaitse Inspektsioon.
Conclusion
The pizza chain leaves a tidy impression, close to exemplary. The CookieYes consent management platform loads first, the banner offers refusal on the first screen alongside consent, and the categories in the settings are off by default. Google analytics run under denial (gcs=G100, cookieless), Facebook is limited to loading the SDK without events, and the policy is detailed and names all recipients individually, including the Facebook Pixel with its cookie.
The only observation is the initialisation order: the Facebook SDK and the GA requests load before the choice is recorded in the banner. No actual transfer of data before consent was recorded — GA is under denial, Facebook without events — so this is a minor caveat about order, not a violation, and the severity here is zero.
Remediation (optional, for cleanliness): gate the loading of the Facebook SDK and the GA requests until the actual choice in the banner, so that the «consent → loading» order is observed strictly; otherwise the current configuration — CookieYes first, refusal on the first screen, unticked categories, the analytics denial respected and the individual disclosure of recipients — can serve as a reference.
How to verify: download the file and compute its checksum — sha256sum file.har (Linux, macOS) or certutil -hashfile file.har SHA256 (Windows); it must match the one shown. The conclusions apply to the scope of this measurement — see the limitations of the method.
3ff0c18df88c9b03cea6d54134a3236a30e5daf3d97efe6b13f626eabc9dd1f3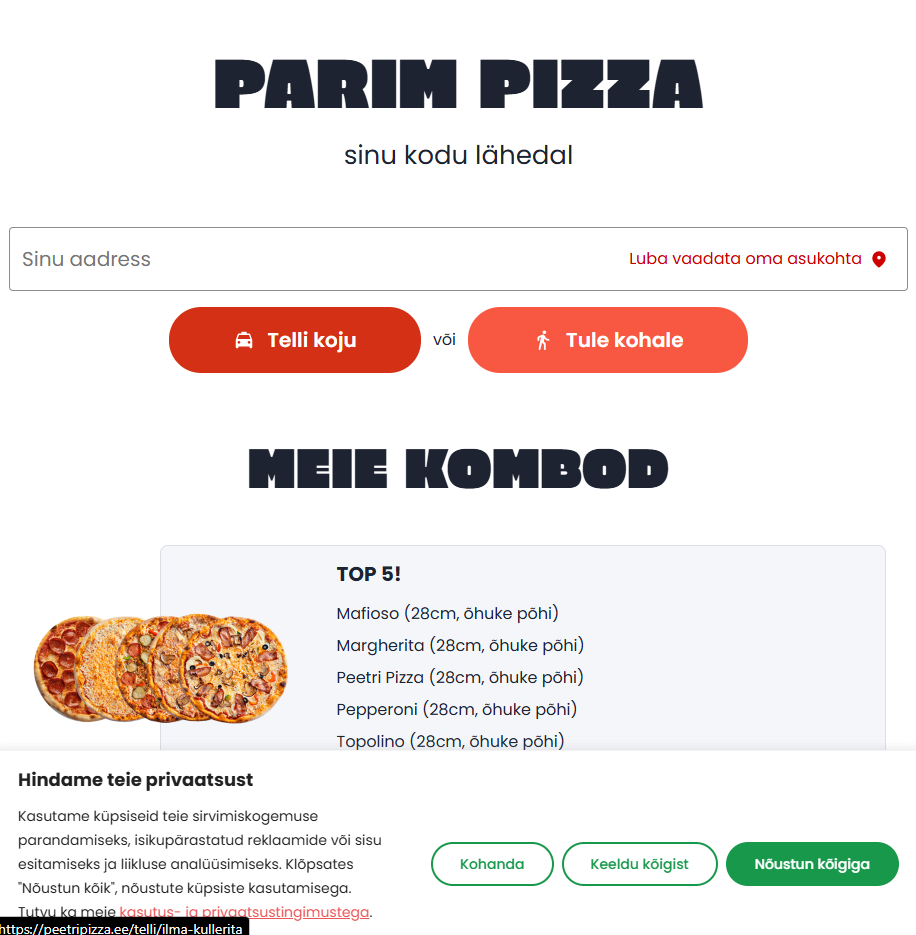
Want a response from the company about this audit? → Open the tool
Fill in once — it will be inserted into every letter below:
All fields are required to print the document — this is a formal requirement of the letter itself (the particulars of an official submission), not data collection: nothing is sent or saved anywhere, it all stays in your browser and disappears when you close the page. See the methodology for details.
RIA DigiDoc — phone · Smart-ID / Mobile-ID
Send this letter directly to the company first — before contacting the regulator it has the right to respond (GDPR Art. 12(3) — 30 days).
Тема: Запрос доступа к персональным данным (ст. 15 GDPR) — peetripizza.ee

Кому: [укажите адрес компании — DPO / поддержка / юридический отдел]
От: [Ваше имя], [контактный email]

Прошу предоставить доступ к моим персональным данным, обрабатываемым в связи с использованием сайта peetripizza.ee.

1. Категории данных и цели обработки (ст. 15(1)(a)-(c))
Прошу предоставить информацию по всем категориям, целям и получателям обработки моих данных на этом сайте — независимо от того, выявлены ли на сегодняшний день какие-либо несоответствия.

2. Получатели, сроки хранения и передача за пределы ЕЭЗ (ст. 15(1)(c)-(d), 46)
Прошу также указать полный список третьих лиц-получателей, применимые сроки хранения по каждой категории и правовые основания передачи данных за пределы ЕЭЗ, если таковая происходит. Полный технический разбор с доказательствами (сохранённый сетевой журнал, контрольная сумма SHA-256) опубликован по адресу: https://gdpru.eu/en/audits/ee-peetripizza-ee/

3. Автоматизированная обработка и профилирование (ст. 15(1)(h))
Прошу сообщить, применяется ли в отношении меня автоматизированное принятие решений или профилирование, и если да — раскрыть логику такой обработки.

С уважением,

[Ваше имя]
[контактный email]
[Страна]


[Дата]
Subject: Data access request (GDPR Art. 15) — peetripizza.ee

To: [insert the company's address — DPO / support / legal department]
From: [Your name], [contact email]

I request access to my personal data processed in connection with the website peetripizza.ee.

1. Categories of data and purposes of processing (Art. 15(1)(a)-(c))
I request information on all categories, purposes, and recipients of my data processed on this site — regardless of whether any non-compliance has been identified to date.

2. Recipients, retention periods, and transfers outside the EEA (Art. 15(1)(c)-(d), 46)
I also request the full list of third-party recipients, the applicable retention period for each category, and the legal basis for any transfer of data outside the EEA. The full technical audit with evidence (saved network log, SHA-256 checksum) is published at: https://gdpru.eu/en/audits/ee-peetripizza-ee/

3. Automated processing and profiling (Art. 15(1)(h))
Please state whether I am subject to automated decision-making or profiling, and if so, disclose the logic involved.

Sincerely,

[Your name]
[contact email]
[Country]


[Date]
Teema: Isikuandmetele juurdepääsu taotlus (IKÜM art 15) — peetripizza.ee

Kellele: [märkige ettevõtte aadress — DPO / tugi / juriidiline osakond]
Kellelt: [Teie nimi], [kontakt-e-post]

Palun anda mulle juurdepääs minu isikuandmetele, mida töödeldakse seoses veebisaidi peetripizza.ee kasutamisega.

1. Andmekategooriad ja töötlemise eesmärgid (IKÜM art 15(1)(a)-(c))
Palun esitada teave kõigi minu andmete töötlemise kategooriate, eesmärkide ja vastuvõtjate kohta sellel veebisaidil — sõltumata sellest, kas praeguseks on tuvastatud mingeid mittevastavusi.

2. Vastuvõtjad, säilitustähtajad ja edastamine väljapoole EMP-d (IKÜM art 15(1)(c)-(d), 46)
Palun samuti esitada täielik loetelu kolmandatest isikutest vastuvõtjatest, iga kategooria puhul kohaldatavad säilitustähtajad ning andmete EMP-välisele edastamisele kohaldatav õiguslik alus, kui selline edastamine toimub. Täielik tehniline analüüs koos tõenditega (salvestatud võrgulogi, SHA-256 kontrollsumma) on avaldatud aadressil: https://gdpru.eu/en/audits/ee-peetripizza-ee/

3. Automatiseeritud töötlemine ja profiilianalüüs (IKÜM art 15(1)(h))
Palun teatada, kas minu suhtes kohaldatakse automatiseeritud otsuste tegemist või profiilianalüüsi, ning kui jah, siis avaldada selle loogika.

Lugupidamisega,

[Teie nimi]
[kontakt-e-post]
[Riik]


[Kuupäev]