
Website of the MyFitness fitness club chain — one recording, seven minutes, seven pages, 723 requests. There is almost nothing superfluous in the traffic: the Cookiebot consent platform with an equal-weight reject button, the refusal is recorded, and neither Google Analytics, nor Meta, nor Adform, nor Hotjar fired across the whole recording. The problem lies in the configuration of the consent platform itself: its declaration classifies as necessary — i.e. not requiring consent — Google cookies that it itself describes as advertising cookies, and the external Chatbase AI chatbot is executed by the Cookiebot loader before a choice and after refusal. The policy promises not to transfer data outside the EEA, whereas the same site's cookie declaration speaks of Google Analytics data being stored in the USA. The browser did not send a DNT header.
Request timeline
Declared versus actual
Transfer timings
uc.js, leveloptin mode.
embed.min.js, executed by the Cookiebot loader.
logconsent.ashx?action=decline.
embed.min.js and chatbot styling; repeats on every page.
Detected trackers
- Cookiebot (consent.cookiebot.com, consentcdn.cookiebot.com; configuration 55f5a28d-63a8-4ea4-86bc-b…) — consent-management platform in opt-in mode; records the decision via logconsent.ashx
- Chatbase (www.chatbase.co; chatbot _E95DMJAN9J_wpTKT61Oj) — an AI chatbot; loads before a choice and after refusal, executed by the Cookiebot loader
Indicators of GDPR non-compliance
- ePrivacy — Directive 2002/58/EC, Art. 5(3); GDPR Art. 4(11), Art. 7 — advertising cookies classified as necessaryThe Cookiebot cookie declaration (updated 14.09.2026) assigns the Google cookies test_cookie, AEC, CONSENT (retention period 20 years), NID and SOCS to the 'Vajalik' (necessary) category, and in the same place states that part of the data collected by this provider is intended for personalisation and measuring advertising effectiveness, and that the provider may use IP addresses to measure and personalise advertising. The site's cookie page likewise assigns test_cookie from the doubleclick.net domain and NID to the necessary category. Necessary cookies are set without consent and cannot be refused, so this classification takes Google's advertising cookies outside the scope of a refusal. There are no requests to Google in the recording, but the consent mechanism is configured such that, if they appeared, the user's refusal would not extend to these cookies.
- ePrivacy — Directive 2002/58/EC, Art. 5(3) (in conjunction with GDPR Art. 6(1)(a)) — an external chatbot after refusalThe Chatbase AI chatbot loads at +5184 ms — before any choice — and then on each of the six pages after the recorded refusal (consent.cookiebot.com/logconsent.ashx?action=decline at +323061 ms). The script is executed through the Cookiebot loader (uc.js), meaning the consent platform does not block it. The Cookiebot declaration lists Chatbase as 'unclassified' with the identifier chatbase_anon_id and the status 'Ootel' (pending). The user did not open the chat; loading a third-party service with a visitor identifier is not strictly necessary for a service the user requested.
- GDPR Art. 5(1)(a), Art. 13(1)(e), (f) — transparency: contradictions between documentsThe MyFitness AS privacy policy has no cookie section, names recipients only by category and states: 'we do not store or transfer your personal data outside the European Economic Area or to countries for which no adequacy decision has been adopted'. The same site's cookie declaration, meanwhile, states that Google Analytics data is stored on Google servers in the USA. Chatbase is named neither in the policy nor on the site's cookie page; the Cookiebot declaration and the site's cookie page differ in the set of necessary cookies (the site page lists New Relic, reCAPTCHA and Vimeo; the declaration does not).
Context
myfitness.ee is the website of the MyFitness fitness club chain in Estonia: clubs, workouts, a timetable, services and the MOVE blog. The controller is MY FITNESS AS, registration code 11273563, Haabersti 5, 13516 Tallinn; the data-protection contact is andmekaitse@myfitness.ee. The site is built on WordPress (Elementor, WPML).
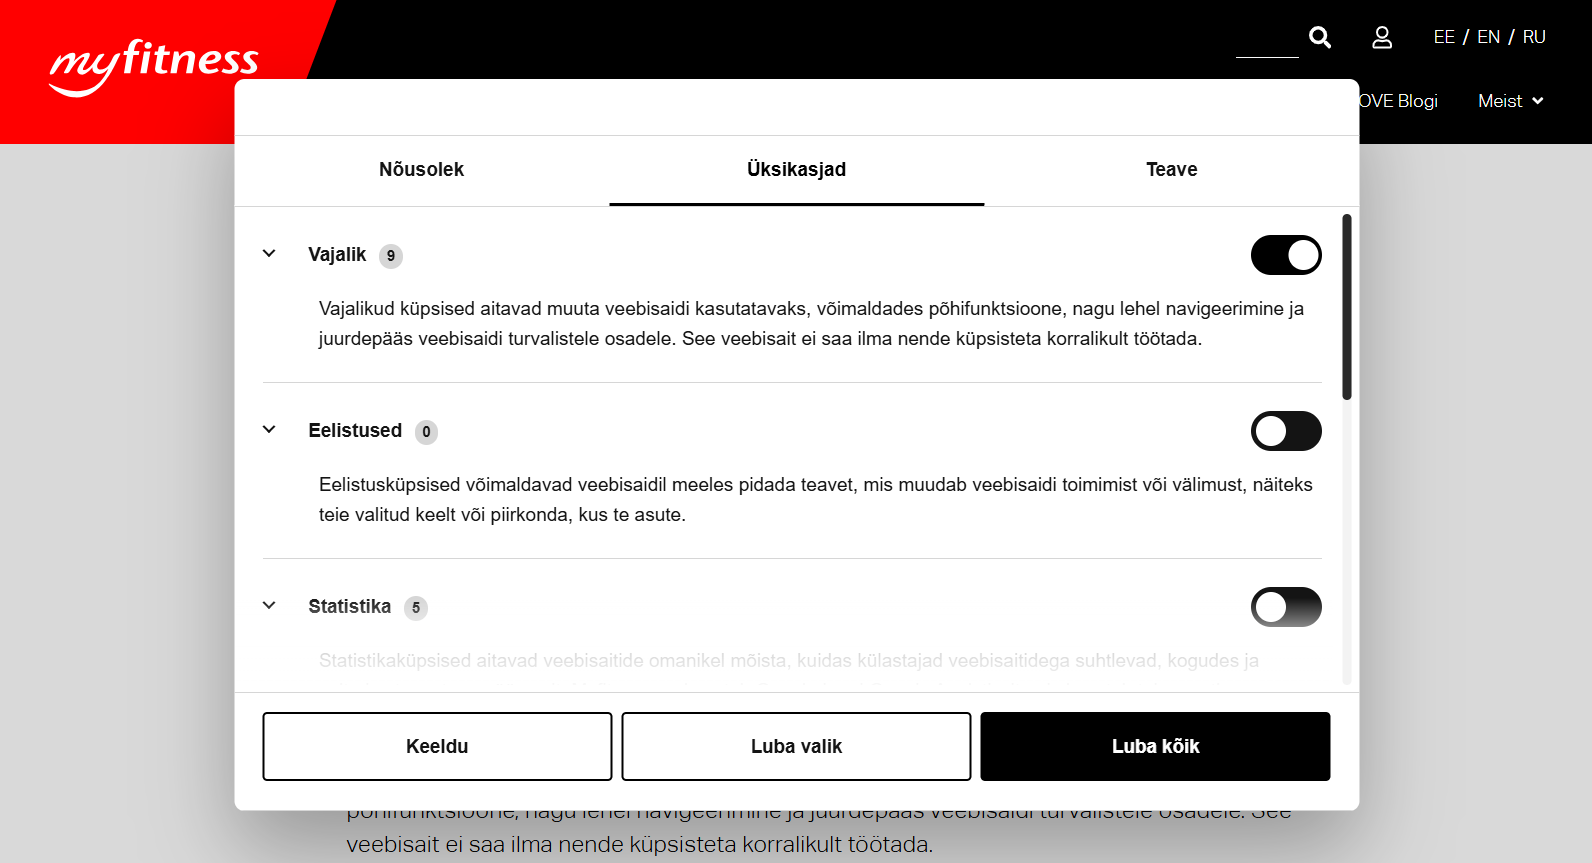
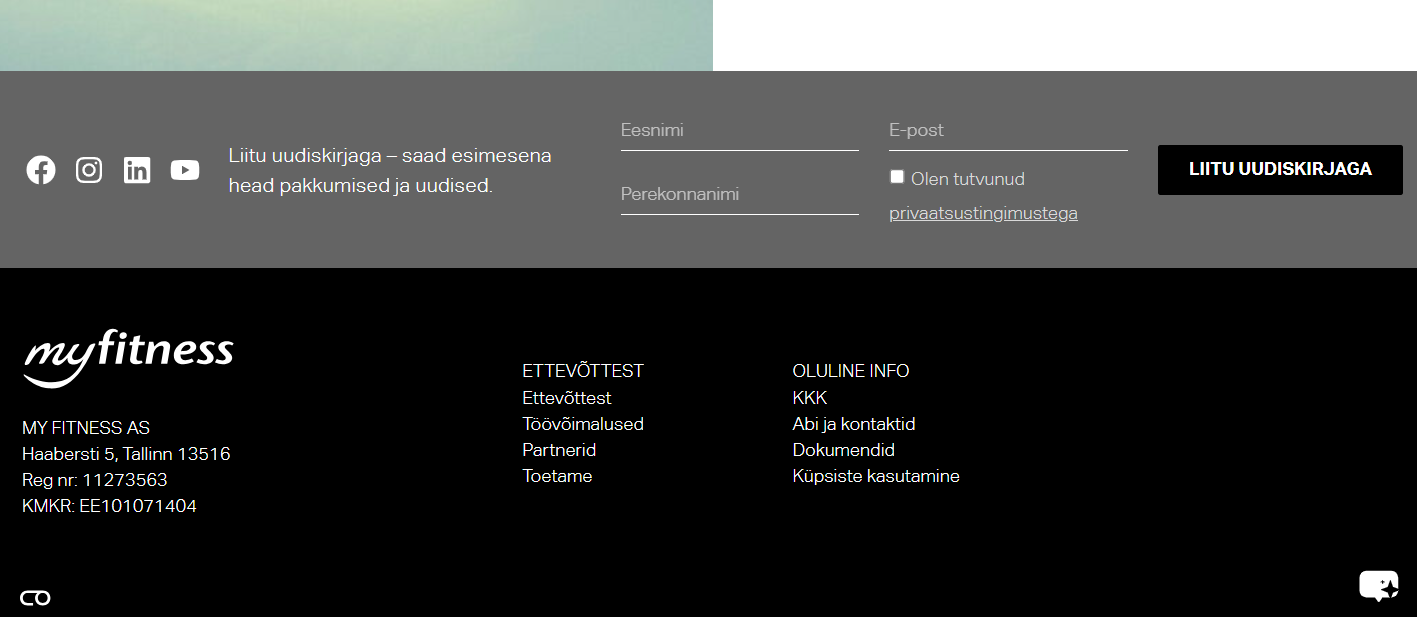
Processing is described by three documents: the MyFitness AS privacy notice (attached in its Russian version), the cookie declaration of the Cookiebot platform shown in the banner (updated 14 September 2026), and a separate site page, ‘Küpsiste kasutamine meie e-keskkondades’. Attached to the material are three screenshots: the banner, the details tab and the site footer.
The measurement consists of one recording lasting about seven minutes, seven navigations: the home page, a repeat visit to the home page, the workout timetable, partners, vacancies, ‘About us’ and questions. Seven hundred and twenty-three requests. The recording was made on 24 September 2026.
Who data goes to directly
Cookiebot (the consent platform), Chatbase (an AI chatbot). There is no Google Analytics, Meta, Adform, Hotjar or advertising network in the recording.
Declared versus actual
The documents declare a broad set of services: in statistics — Google Analytics and Hotjar; in marketing — Meta, Adform and Google advertising cookies; the site’s cookie page adds New Relic, reCAPTCHA and Vimeo. The privacy policy has no cookie section and names recipients only by category.
As regards transmissions, the measurement yields a discrepancy in the favourable direction; as regards the consent configuration, in the unfavourable one.
The consent platform works; advertising and analytics did not fire. Cookiebot loads at +2489 ms in leveloptin mode. The banner, as seen in the screenshot, offers ‘Keeldu’, ‘Luba valik’ and ‘Luba kõik’ — refusal is on equal footing with consent, and the preference, statistics and marketing categories are off. At +323061 ms the refusal is recorded (logconsent.ashx?action=decline). Across all 723 requests there is not a single request to Google Analytics, Meta, Adform, Hotjar or advertising networks — neither before the choice nor after.
Google advertising cookies are declared necessary. The Cookiebot declaration assigns the Google cookies test_cookie, AEC, CONSENT (retention period — 20 years), NID and SOCS to the ‘Vajalik’ category, and in the same place states that part of the data collected by this provider is intended for personalisation and measuring advertising effectiveness, and that IP addresses may be used to measure and personalise advertising. The site’s cookie page likewise assigns test_cookie from the doubleclick.net domain and NID to the necessary category. Necessary cookies are set without consent and cannot be refused, so this classification takes Google’s advertising cookies outside the scope of a refusal. In this recording there are no requests to Google, but if they appeared, the visitor’s refusal would not extend to these cookies.
The chatbot operates before a choice and after refusal. The Chatbase AI chatbot loads at +5184 ms, before any choice, and then on each of the six pages after the refusal — the embed script and the styling of chatbot _E95DMJAN9J_wpTKT61Oj. The script is executed through the Cookiebot loader (uc.js), meaning the consent platform lets it through. In the Cookiebot declaration Chatbase is listed as ‘unclassified’ with the identifier chatbase_anon_id and the status ‘Ootel’ (pending). The chat icon is visible in the screenshots over the banner and in the footer. The user did not open the chat.
The documents contradict each other. The policy states that data is not stored or transferred outside the EEA or to countries without an adequacy decision, whereas the same site’s cookie declaration states that Google Analytics data is stored on Google servers in the USA. The Cookiebot declaration and the site’s cookie page differ in the set of necessary cookies. Chatbase is named neither in the policy nor on the site’s cookie page.
Consent: what is proven and what is not
Proven: refusal is on equal footing with consent, and it is recorded. By the banner screenshot and the logconsent.ashx?action=decline request.
Proven: advertising and analytics did not fire. There are no requests to Google Analytics, Meta, Adform, Hotjar or advertising networks in the recording.
Proven: Chatbase loads before a choice and after refusal, through the Cookiebot loader. By the timings and the initiator stack of the www.chatbase.co requests.
Proven: Google cookies described as advertising cookies are classified as necessary. By the text of the Cookiebot declaration and the site’s cookie page.
Not proven and not asserted: the setting of the chatbase_anon_id cookie and Google cookies in this recording. The Set-Cookie headers are stripped in the published file; their existence follows from the declaration, not from the network recording. There are no requests to Google in the recording at all.
Separately: the browser did not send a DNT header in this recording.
Bounds of observation
The measurement covers seven pages of the site; no login to the client environment, workout booking or chat conversation was performed. Observation captures the browser’s behaviour, not the internal side of the services. The legal assessment is made by the competent authority — in Estonia, Andmekaitse Inspektsioon.
The file is published redacted under a “lean” profile: cookie values in requests have been removed, the Cookie and Set-Cookie headers stripped; the redaction registry records 322 redactions and a checksum. The consent decision is read from the action=decline parameter; information on the composition and classification of cookies is taken from the Cookiebot declaration and the site’s cookie page. The presence of Chatbase does not mean it transmits information about conversations: there was no conversation in the recording, only the loading of the chatbot is observed.
The identification of services relies on domains and address patterns: the consent platform — by cookiebot.com; the chatbot — by chatbase.co and the chatbot identifier. The absence of analytics and advertising is established by the absence of requests to google-analytics.com, facebook.com, adform.net, hotjar.com and other advertising nodes.
Conclusion
The MyFitness fitness club chain’s website transmits no data to analytics or advertising when browsed: the Cookiebot consent platform works with an equal-weight reject button, the refusal is recorded, and the declared Google Analytics, Meta, Adform and Hotjar do not fire in the recording. The violation lies in the configuration of the consent mechanism itself and in the documents. The Cookiebot declaration classifies as necessary Google cookies that it itself describes as advertising cookies — thereby taking them outside the scope of a refusal; the Chatbase AI chatbot is executed by the Cookiebot loader before a choice and after refusal and is named nowhere except in the declaration. The policy promises not to transfer data outside the EEA, whereas the same site’s cookie declaration speaks of Google Analytics data being stored in the USA.
Remediation: move the Google cookies test_cookie, NID, AEC, CONSENT and SOCS out of the necessary category into one requiring consent, and shorten the retention period of CONSENT; classify Chatbase and place its loading under consent, or load the chatbot only when the chat icon is clicked; name Chatbase in the policy and on the cookie page; reconcile the statement about not transferring data outside the EEA with the cookie declaration and describe the transfer mechanism; synchronise the Cookiebot declaration and the site’s cookie page.
How to verify: download the file and compute its checksum — sha256sum file.har (Linux, macOS) or certutil -hashfile file.har SHA256 (Windows); it must match the one shown. The conclusions apply to the scope of this measurement — see the limitations of the method.
cd83e0840cb73a5086bb04e547087d1d4abba52a16b273dbd23775b2d532efc6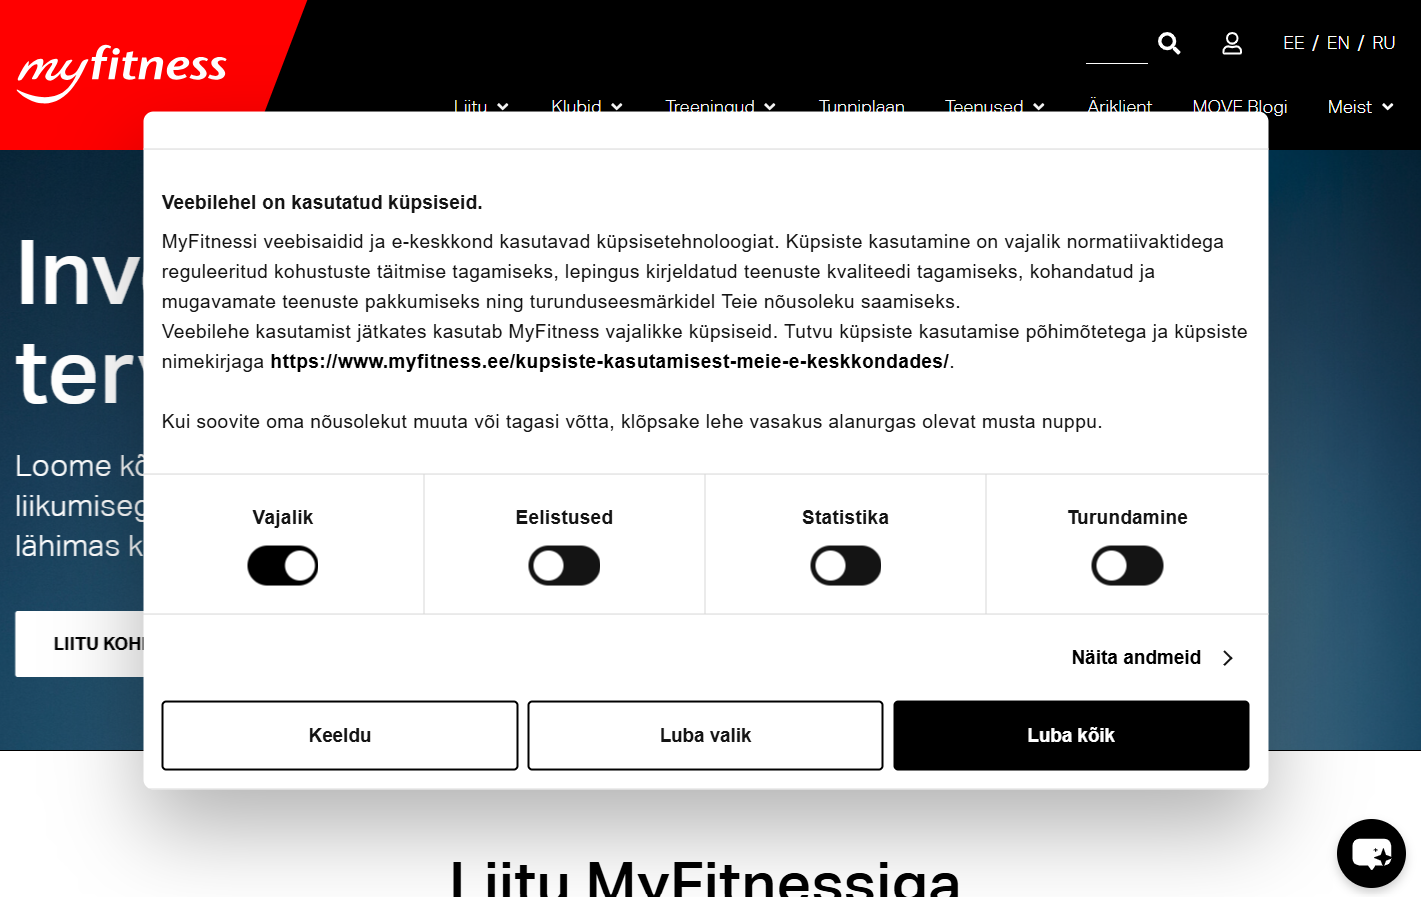
Want a response from the company about this audit? → Open the tool
Fill in once — it will be inserted into every letter below:
All fields are required to print the document — this is a formal requirement of the letter itself (the particulars of an official submission), not data collection: nothing is sent or saved anywhere, it all stays in your browser and disappears when you close the page. See the methodology for details.
RIA DigiDoc — phone · Smart-ID / Mobile-ID
Send this letter directly to the company first — before contacting the regulator it has the right to respond (GDPR Art. 12(3) — 30 days).
Тема: Запрос доступа к персональным данным (ст. 15 GDPR) — myfitness.ee

Кому: [укажите адрес компании — DPO / поддержка / юридический отдел]
От: [Ваше имя], [контактный email]

Прошу предоставить доступ к моим персональным данным, обрабатываемым в связи с использованием сайта myfitness.ee.

1. Категории данных и цели обработки (ст. 15(1)(a)-(c))
На основании независимого технического анализа сайта прошу подтвердить и подробно раскрыть следующие категории обработки:

1) Декларация cookie платформы Cookiebot (обновлена 14.09.2026) относит к категории «Vajalik» (необходимые) cookie Google test_cookie, AEC, CONSENT (срок хранения 20 лет), NID и SOCS и тут же указывает, что часть данных этого поставщика предназначена для персонализации и измерения эффективности рекламы и что поставщик может использовать адреса IP для измерения и персонализации рекламы. Страница cookie сайта также относит к необходимым test_cookie домена doubleclick.net и NID. Необходимые cookie устанавливаются без согласия и не могут быть отклонены, поэтому такая классификация выводит рекламные cookie Google из-под действия отказа. В записи обращений к Google нет, но механизм согласия настроен так, что при их появлении отказ пользователя на эти cookie не распространялся бы.

2) AI-чат-бот Chatbase загружается на +5184 мс — до какого-либо выбора — и далее на каждой из шести страниц после зафиксированного отказа (consent.cookiebot.com/logconsent.ashx?action=decline на +323061 мс). Скрипт исполняется через загрузчик Cookiebot (uc.js), то есть платформа согласия его не блокирует. Декларация Cookiebot относит Chatbase к «неклассифицированным» с идентификатором chatbase_anon_id и статусом «Ootel» (на рассмотрении). Пользователь чат не открывал; загрузка стороннего сервиса с идентификатором посетителя не является строго необходимой для услуги, которую он запросил.

3) Политика конфиденциальности MyFitness AS не содержит раздела о cookie, называет получателей только категориями и заявляет: «мы не храним и не передаём ваши личные данные за пределы Европейской экономической зоны или в страны, в отношении которых не принято решение о достаточности защиты». Декларация cookie того же сайта при этом сообщает, что данные Google Analytics сохраняются на серверах Google в США. Chatbase не назван ни в политике, ни на странице cookie сайта; декларация Cookiebot и страница cookie сайта расходятся по составу необходимых cookie (на странице сайта — New Relic, reCAPTCHA, Vimeo; в декларации — их нет).


2. Получатели, сроки хранения и передача за пределы ЕЭЗ (ст. 15(1)(c)-(d), 46)
Прошу также указать полный список третьих лиц-получателей, применимые сроки хранения по каждой категории и правовые основания передачи данных за пределы ЕЭЗ, если таковая происходит. Полный технический разбор с доказательствами (сохранённый сетевой журнал, контрольная сумма SHA-256) опубликован по адресу: https://gdpru.eu/en/audits/ee-myfitness-ee/

3. Автоматизированная обработка и профилирование (ст. 15(1)(h))
Прошу сообщить, применяется ли в отношении меня автоматизированное принятие решений или профилирование, и если да — раскрыть логику такой обработки.

С уважением,

[Ваше имя]
[контактный email]
[Страна]


[Дата]
Subject: Data access request (GDPR Art. 15) — myfitness.ee

To: [insert the company's address — DPO / support / legal department]
From: [Your name], [contact email]

I request access to my personal data processed in connection with the website myfitness.ee.

1. Categories of data and purposes of processing (Art. 15(1)(a)-(c))
Based on an independent technical analysis of the site, I request confirmation and detailed disclosure of the following categories of processing:

1) The Cookiebot cookie declaration (updated 14.09.2026) assigns the Google cookies test_cookie, AEC, CONSENT (retention period 20 years), NID and SOCS to the 'Vajalik' (necessary) category, and in the same place states that part of the data collected by this provider is intended for personalisation and measuring advertising effectiveness, and that the provider may use IP addresses to measure and personalise advertising. The site's cookie page likewise assigns test_cookie from the doubleclick.net domain and NID to the necessary category. Necessary cookies are set without consent and cannot be refused, so this classification takes Google's advertising cookies outside the scope of a refusal. There are no requests to Google in the recording, but the consent mechanism is configured such that, if they appeared, the user's refusal would not extend to these cookies.

2) The Chatbase AI chatbot loads at +5184 ms — before any choice — and then on each of the six pages after the recorded refusal (consent.cookiebot.com/logconsent.ashx?action=decline at +323061 ms). The script is executed through the Cookiebot loader (uc.js), meaning the consent platform does not block it. The Cookiebot declaration lists Chatbase as 'unclassified' with the identifier chatbase_anon_id and the status 'Ootel' (pending). The user did not open the chat; loading a third-party service with a visitor identifier is not strictly necessary for a service the user requested.

3) The MyFitness AS privacy policy has no cookie section, names recipients only by category and states: 'we do not store or transfer your personal data outside the European Economic Area or to countries for which no adequacy decision has been adopted'. The same site's cookie declaration, meanwhile, states that Google Analytics data is stored on Google servers in the USA. Chatbase is named neither in the policy nor on the site's cookie page; the Cookiebot declaration and the site's cookie page differ in the set of necessary cookies (the site page lists New Relic, reCAPTCHA and Vimeo; the declaration does not).


2. Recipients, retention periods, and transfers outside the EEA (Art. 15(1)(c)-(d), 46)
I also request the full list of third-party recipients, the applicable retention period for each category, and the legal basis for any transfer of data outside the EEA. The full technical audit with evidence (saved network log, SHA-256 checksum) is published at: https://gdpru.eu/en/audits/ee-myfitness-ee/

3. Automated processing and profiling (Art. 15(1)(h))
Please state whether I am subject to automated decision-making or profiling, and if so, disclose the logic involved.

Sincerely,

[Your name]
[contact email]
[Country]


[Date]
Teema: Isikuandmetele juurdepääsu taotlus (IKÜM art 15) — myfitness.ee

Kellele: [märkige ettevõtte aadress — DPO / tugi / juriidiline osakond]
Kellelt: [Teie nimi], [kontakt-e-post]

Palun anda mulle juurdepääs minu isikuandmetele, mida töödeldakse seoses veebisaidi myfitness.ee kasutamisega.

1. Andmekategooriad ja töötlemise eesmärgid (IKÜM art 15(1)(a)-(c))
Sõltumatu tehnilise analüüsi põhjal palun kinnitada ja üksikasjalikult avaldada järgmised töötlemiskategooriad:

1) Cookieboti platvormi küpsiste deklaratsioon (uuendatud 14.09.2026) liigitab kategooriasse „Vajalik“ Google'i küpsised test_cookie, AEC, CONSENT (säilitusaeg 20 aastat), NID ja SOCS ning märgib samas, et osa selle teenusepakkuja andmetest on mõeldud reklaami isikupärastamiseks ja tõhususe mõõtmiseks ning et teenusepakkuja võib kasutada IP-aadresse reklaami mõõtmiseks ja isikupärastamiseks. Ka saidi küpsiste leht liigitab vajalikeks domeeni doubleclick.net test_cookie ja NID. Vajalikud küpsised paigaldatakse ilma nõusolekuta ja neist ei saa keelduda, mistõttu selline liigitus jätab Google'i reklaamiküpsised keeldumise mõjualast välja. Salvestises päringuid Google'ile ei ole, kuid nõusolekumehhanism on seadistatud nii, et nende ilmumisel kasutaja keeldumine neile küpsistele ei laieneks.

2) Tehisintellektil põhinev vestlusrobot Chatbase laaditakse +5184 ms juures — enne mis tahes valikut — ja seejärel kõigil kuuel lehel pärast registreeritud keeldumist (consent.cookiebot.com/logconsent.ashx?action=decline +323061 ms juures). Skript käivitatakse Cookieboti laaduri (uc.js) kaudu, st nõusolekuplatvorm seda ei blokeeri. Cookieboti deklaratsioon liigitab Chatbase'i liigitamata küpsiste hulka identifikaatoriga chatbase_anon_id ja olekuga „Ootel“. Kasutaja vestlust ei avanud; kolmanda osapoole teenuse laadimine külastaja identifikaatoriga ei ole tema taotletud teenuse osutamiseks rangelt vajalik.

3) MyFitness AS-i privaatsuspoliitikas puudub küpsiseid käsitlev jaotis, vastuvõtjad on nimetatud üksnes kategooriate kaupa ning kinnitatakse, et isikuandmeid ei säilitata ega edastata väljapoole Euroopa Majanduspiirkonda ega riikidesse, mille kohta ei ole tehtud kaitse piisavuse otsust. Sama saidi küpsiste deklaratsioon teatab seejuures, et Google Analyticsi andmeid säilitatakse Google'i serverites USA-s. Chatbase'i ei nimetata ei poliitikas ega saidi küpsiste lehel; Cookieboti deklaratsioon ja saidi küpsiste leht erinevad vajalike küpsiste koosseisu poolest (saidi lehel on New Relic, reCAPTCHA ja Vimeo, deklaratsioonis neid ei ole).


2. Vastuvõtjad, säilitustähtajad ja edastamine väljapoole EMP-d (IKÜM art 15(1)(c)-(d), 46)
Palun samuti esitada täielik loetelu kolmandatest isikutest vastuvõtjatest, iga kategooria puhul kohaldatavad säilitustähtajad ning andmete EMP-välisele edastamisele kohaldatav õiguslik alus, kui selline edastamine toimub. Täielik tehniline analüüs koos tõenditega (salvestatud võrgulogi, SHA-256 kontrollsumma) on avaldatud aadressil: https://gdpru.eu/en/audits/ee-myfitness-ee/

3. Automatiseeritud töötlemine ja profiilianalüüs (IKÜM art 15(1)(h))
Palun teatada, kas minu suhtes kohaldatakse automatiseeritud otsuste tegemist või profiilianalüüsi, ning kui jah, siis avaldada selle loogika.

Lugupidamisega,

[Teie nimi]
[kontakt-e-post]
[Riik]


[Kuupäev]
RIA DigiDoc — phone · Smart-ID / Mobile-ID
Where to file: Estonian Data Protection Inspectorate (AKI) — write to info@aki.ee
Important: AKI only handles submissions in Estonian. Translate the letter before sending.
The regulator reviews complaints in its national language. There is an officially translated template from the European Data Protection Board (EDPB) — you can use it instead of or alongside this letter: Official EDPB complaint form (PDF, your language)
Тема: Жалоба на обработку персональных данных — myfitness.ee

1. Предмет жалобы
Я подаю жалобу в отношении обработки моих персональных данных сайтом myfitness.ee.

2. Обстоятельства
Я посетил сайт myfitness.ee и обнаружил признаки несоответствия обработки моих персональных данных требованиям GDPR. Технический разбор, опубликованный на gdpru.eu 24.09.2026 (открытая методология, воспроизводимые измерения), документирует следующие признаки:

1) Декларация cookie платформы Cookiebot (обновлена 14.09.2026) относит к категории «Vajalik» (необходимые) cookie Google test_cookie, AEC, CONSENT (срок хранения 20 лет), NID и SOCS и тут же указывает, что часть данных этого поставщика предназначена для персонализации и измерения эффективности рекламы и что поставщик может использовать адреса IP для измерения и персонализации рекламы. Страница cookie сайта также относит к необходимым test_cookie домена doubleclick.net и NID. Необходимые cookie устанавливаются без согласия и не могут быть отклонены, поэтому такая классификация выводит рекламные cookie Google из-под действия отказа. В записи обращений к Google нет, но механизм согласия настроен так, что при их появлении отказ пользователя на эти cookie не распространялся бы.

2) AI-чат-бот Chatbase загружается на +5184 мс — до какого-либо выбора — и далее на каждой из шести страниц после зафиксированного отказа (consent.cookiebot.com/logconsent.ashx?action=decline на +323061 мс). Скрипт исполняется через загрузчик Cookiebot (uc.js), то есть платформа согласия его не блокирует. Декларация Cookiebot относит Chatbase к «неклассифицированным» с идентификатором chatbase_anon_id и статусом «Ootel» (на рассмотрении). Пользователь чат не открывал; загрузка стороннего сервиса с идентификатором посетителя не является строго необходимой для услуги, которую он запросил.

3) Политика конфиденциальности MyFitness AS не содержит раздела о cookie, называет получателей только категориями и заявляет: «мы не храним и не передаём ваши личные данные за пределы Европейской экономической зоны или в страны, в отношении которых не принято решение о достаточности защиты». Декларация cookie того же сайта при этом сообщает, что данные Google Analytics сохраняются на серверах Google в США. Chatbase не назван ни в политике, ни на странице cookie сайта; декларация Cookiebot и страница cookie сайта расходятся по составу необходимых cookie (на странице сайта — New Relic, reCAPTCHA, Vimeo; в декларации — их нет).

Полная техническая документация опубликована по адресу: https://gdpru.eu/en/audits/ee-myfitness-ee/

3. Положения GDPR, соблюдение которых прошу проверить
ePrivacy — Директива 2002/58/EC, ст. 5(3); GDPR Art. 4(11), Art. 7 — классификация рекламных cookie как необходимых; ePrivacy — Директива 2002/58/EC, ст. 5(3) (в связке с GDPR Art. 6(1)(a)) — внешний чат-бот после отказа; GDPR Art. 5(1)(a), Art. 13(1)(e), (f) — прозрачность: противоречия в документах

4. Требование
Прошу проверить изложенные обстоятельства и, если несоответствие подтвердится, принять меры, предусмотренные статьёй 58(2) GDPR.

5. Приложения
Полная доказательная база — HAR-файл, контрольная сумма SHA-256 и цитата из политики конфиденциальности сайта, документирующая указанное противоречие — опубликована и проверяема по ссылке в пункте 2 выше.

С уважением,

[Ваше имя]
[контактный email]
[Страна]


[Дата]
Subject: Complaint regarding personal data processing — myfitness.ee

1. Subject of the complaint
I am filing a complaint regarding the processing of my personal data by the website myfitness.ee.

2. Circumstances
I visited the website myfitness.ee and found indications that the processing of my personal data does not comply with the GDPR. The technical analysis published on gdpru.eu on 24 September 2026 (open methodology, reproducible measurements) documents the following indications:

1) The Cookiebot cookie declaration (updated 14.09.2026) assigns the Google cookies test_cookie, AEC, CONSENT (retention period 20 years), NID and SOCS to the 'Vajalik' (necessary) category, and in the same place states that part of the data collected by this provider is intended for personalisation and measuring advertising effectiveness, and that the provider may use IP addresses to measure and personalise advertising. The site's cookie page likewise assigns test_cookie from the doubleclick.net domain and NID to the necessary category. Necessary cookies are set without consent and cannot be refused, so this classification takes Google's advertising cookies outside the scope of a refusal. There are no requests to Google in the recording, but the consent mechanism is configured such that, if they appeared, the user's refusal would not extend to these cookies.

2) The Chatbase AI chatbot loads at +5184 ms — before any choice — and then on each of the six pages after the recorded refusal (consent.cookiebot.com/logconsent.ashx?action=decline at +323061 ms). The script is executed through the Cookiebot loader (uc.js), meaning the consent platform does not block it. The Cookiebot declaration lists Chatbase as 'unclassified' with the identifier chatbase_anon_id and the status 'Ootel' (pending). The user did not open the chat; loading a third-party service with a visitor identifier is not strictly necessary for a service the user requested.

3) The MyFitness AS privacy policy has no cookie section, names recipients only by category and states: 'we do not store or transfer your personal data outside the European Economic Area or to countries for which no adequacy decision has been adopted'. The same site's cookie declaration, meanwhile, states that Google Analytics data is stored on Google servers in the USA. Chatbase is named neither in the policy nor on the site's cookie page; the Cookiebot declaration and the site's cookie page differ in the set of necessary cookies (the site page lists New Relic, reCAPTCHA and Vimeo; the declaration does not).

Full technical documentation is published at: https://gdpru.eu/en/audits/ee-myfitness-ee/

3. GDPR provisions I ask you to examine
ePrivacy — Directive 2002/58/EC, Art. 5(3); GDPR Art. 4(11), Art. 7 — advertising cookies classified as necessary; ePrivacy — Directive 2002/58/EC, Art. 5(3) (in conjunction with GDPR Art. 6(1)(a)) — an external chatbot after refusal; GDPR Art. 5(1)(a), Art. 13(1)(e), (f) — transparency: contradictions between documents

4. Request
I request that you examine the circumstances described and, if non-compliance is confirmed, apply the measures provided for in Article 58(2) GDPR.

5. Attachments
The full evidence base — the HAR file, its SHA-256 checksum and the quotation from the site's privacy policy documenting the stated contradiction — is published and verifiable at the link in point 2 above.

Sincerely,

[Your name]
[contact email]
[Country]


[Date]
1. Kaebuse ese
Esitan kaebuse seoses minu isikuandmete töötlemisega veebisaidil myfitness.ee.

2. Asjaolud
Külastasin veebisaiti myfitness.ee ja tuvastasin märke sellest, et minu isikuandmete töötlemine ei vasta isikuandmete kaitse üldmääruse (IKÜM) nõuetele. Tehniline analüüs, mis on avaldatud aadressil gdpru.eu 24.09.2026 (avatud metoodika, korratavad mõõtmised), dokumenteerib järgmist:

1) Cookieboti platvormi küpsiste deklaratsioon (uuendatud 14.09.2026) liigitab kategooriasse „Vajalik“ Google'i küpsised test_cookie, AEC, CONSENT (säilitusaeg 20 aastat), NID ja SOCS ning märgib samas, et osa selle teenusepakkuja andmetest on mõeldud reklaami isikupärastamiseks ja tõhususe mõõtmiseks ning et teenusepakkuja võib kasutada IP-aadresse reklaami mõõtmiseks ja isikupärastamiseks. Ka saidi küpsiste leht liigitab vajalikeks domeeni doubleclick.net test_cookie ja NID. Vajalikud küpsised paigaldatakse ilma nõusolekuta ja neist ei saa keelduda, mistõttu selline liigitus jätab Google'i reklaamiküpsised keeldumise mõjualast välja. Salvestises päringuid Google'ile ei ole, kuid nõusolekumehhanism on seadistatud nii, et nende ilmumisel kasutaja keeldumine neile küpsistele ei laieneks.

2) Tehisintellektil põhinev vestlusrobot Chatbase laaditakse +5184 ms juures — enne mis tahes valikut — ja seejärel kõigil kuuel lehel pärast registreeritud keeldumist (consent.cookiebot.com/logconsent.ashx?action=decline +323061 ms juures). Skript käivitatakse Cookieboti laaduri (uc.js) kaudu, st nõusolekuplatvorm seda ei blokeeri. Cookieboti deklaratsioon liigitab Chatbase'i liigitamata küpsiste hulka identifikaatoriga chatbase_anon_id ja olekuga „Ootel“. Kasutaja vestlust ei avanud; kolmanda osapoole teenuse laadimine külastaja identifikaatoriga ei ole tema taotletud teenuse osutamiseks rangelt vajalik.

3) MyFitness AS-i privaatsuspoliitikas puudub küpsiseid käsitlev jaotis, vastuvõtjad on nimetatud üksnes kategooriate kaupa ning kinnitatakse, et isikuandmeid ei säilitata ega edastata väljapoole Euroopa Majanduspiirkonda ega riikidesse, mille kohta ei ole tehtud kaitse piisavuse otsust. Sama saidi küpsiste deklaratsioon teatab seejuures, et Google Analyticsi andmeid säilitatakse Google'i serverites USA-s. Chatbase'i ei nimetata ei poliitikas ega saidi küpsiste lehel; Cookieboti deklaratsioon ja saidi küpsiste leht erinevad vajalike küpsiste koosseisu poolest (saidi lehel on New Relic, reCAPTCHA ja Vimeo, deklaratsioonis neid ei ole).

Täielik tehniline dokumentatsioon on avaldatud aadressil: https://gdpru.eu/en/audits/ee-myfitness-ee/

3. Sätted, mille järgimist palun kontrollida
e-privaatsuse direktiiv 2002/58/EÜ art 5 lg 3; IKÜM art 4 p 11, art 7 — reklaamiküpsiste liigitamine vajalikeks; e-privaatsuse direktiiv 2002/58/EÜ art 5 lg 3 (koostoimes IKÜM art 6 lg 1 p-ga a) — väline vestlusrobot pärast keeldumist; IKÜM art 5 lg 1 p a, art 13 lg 1 p e, f — läbipaistvus: vastuolud dokumentides

4. Nõue
Palun kontrollida kirjeldatud asjaolusid ja mittevastavuse kinnitamisel kohaldada IKÜM artikli 58 lõikes 2 ette nähtud meetmeid.

5. Lisad
Täielik tõendusmaterjal — HAR-fail, kontrollsumma SHA-256 ning veebisaidi privaatsuspoliitika tsitaat, mis dokumenteerib nimetatud vastuolu — on avaldatud ja kontrollitav punktis 2 viidatud lingil.

Lugupidamisega,

[Teie nimi]
[kontakt-e-post]
[Riik]


[Kuupäev]