
Website of the LIDO restaurant chain in Estonia, part of the Apollo Group holding — one recording, the contacts page, 96 requests, twelve nodes (all of the Google family). Google Analytics 4 sends a page_view on load, without consent and without a consent-mode signal. There is no valid consent mechanism: the eDream plugin displays a notice 'by continuing to use the site you agree' with a single 'Agree' button, no refusal and no tag blocking. The general Apollo Group policy does not name the recipients by name and itself acknowledges the presence of tracking cookies. The browser did not send a DNT header.
Request timeline
Declared versus actual
Transfer timings
GTM-N2B53T57.
maps/d/embed — the Google My Maps map on the contacts page.
Google Maps API; the visitor's IP address is visible to Google.
GA4 page_view (G-VRW2QE1E4V) without a gcs consent-mode signal.
Detected trackers
- Google Analytics 4 (G-VRW2QE1E4V) via region1.google-analytics.com — page_view without a consent-mode signal; goes out on load, before consent
- Google Tag Manager (www.googletagmanager.com, container GTM-N2B53T57) — tag container
- Google Maps (maps.googleapis.com, maps.gstatic.com, mt.googleapis.com, www.google.com/maps/d/embed) — an embedded Google My Maps map on the contacts page
- Google Fonts (fonts.googleapis.com, fonts.gstatic.com) — the Roboto font; on loading, the visitor's IP address is visible to Google
- Google reCAPTCHA (www.google.com/recaptcha, www.gstatic.com) — form protection, a functional resource
- eDream Privacy Policy & Cookie Consent (a WordPress plugin, first-party) — a cookie banner; operates on an implied-consent model and does not block tags
Indicators of GDPR non-compliance
- ePrivacy — Directive 2002/58/EC, Art. 5(3) (in conjunction with GDPR Art. 6(1)(a))There is no valid consent mechanism on the site. A WordPress plugin, eDream Privacy Policy & Cookie Consent, is installed, which displays a notice — 'This website uses cookies… continue using the page as usual' — with a single 'Agree' button, with no reject button and no category choice. This is an implied-consent-by-continued-browsing model, which is not valid consent under ePrivacy and the case law of the Court of Justice. The plugin does not block tags: Google Tag Manager (GTM-N2B53T57) loads at +735 ms, and Google Analytics 4 (G-VRW2QE1E4V) sends a page_view at +3272 ms without a consent-mode signal (gcs is absent) — before any interaction with the notice.
- GDPR Art. 13(1)(e) — disclosure of recipientsThe general Apollo Group privacy policy refers for cookie details to the 'cookie solution on the pages' (clause 1.8) and does not name by name the actual recipients of web data: Google Analytics 4 (G-VRW2QE1E4V), Google Tag Manager and Google Maps are not named as recipients in the document. At the same time the document itself (clause 1.10) acknowledges the presence of tracking cookies that collect data on user behaviour.
- GDPR Art. 5(1)(a) — transparency: the declared diverges from the actualThe site's cookie principles offer opting out of cookies only through browser settings (the opt-out model, clause 1.3) and acknowledge tracking cookies (clause 1.10). In fact Google analytics goes out on page load without consent, and the only on-screen mechanism is an implied-consent notice with no option to refuse. The declared arrangement (cookie management, consent) diverges from the actual behaviour.
- GDPR Art. 44 — transfer to a third countryGoogle Analytics 4 and the embedded Google Maps map entail the transmission of data and of the visitor's IP address to Google (nodes outside the EEA); fonts are loaded from Google servers. The legal basis for the cross-border transfer as regards these recipients is not disclosed by name in the document.
Context
lido.ee is the website of the LIDO restaurant-bistro chain in Estonia, part of the Apollo Group OÜ holding (registration code 12383236, Tartu mnt 80D, Tallinn). The site is built on WordPress, Apache server; processing is described by the general Apollo Group privacy policy and a section on cookie-use principles.
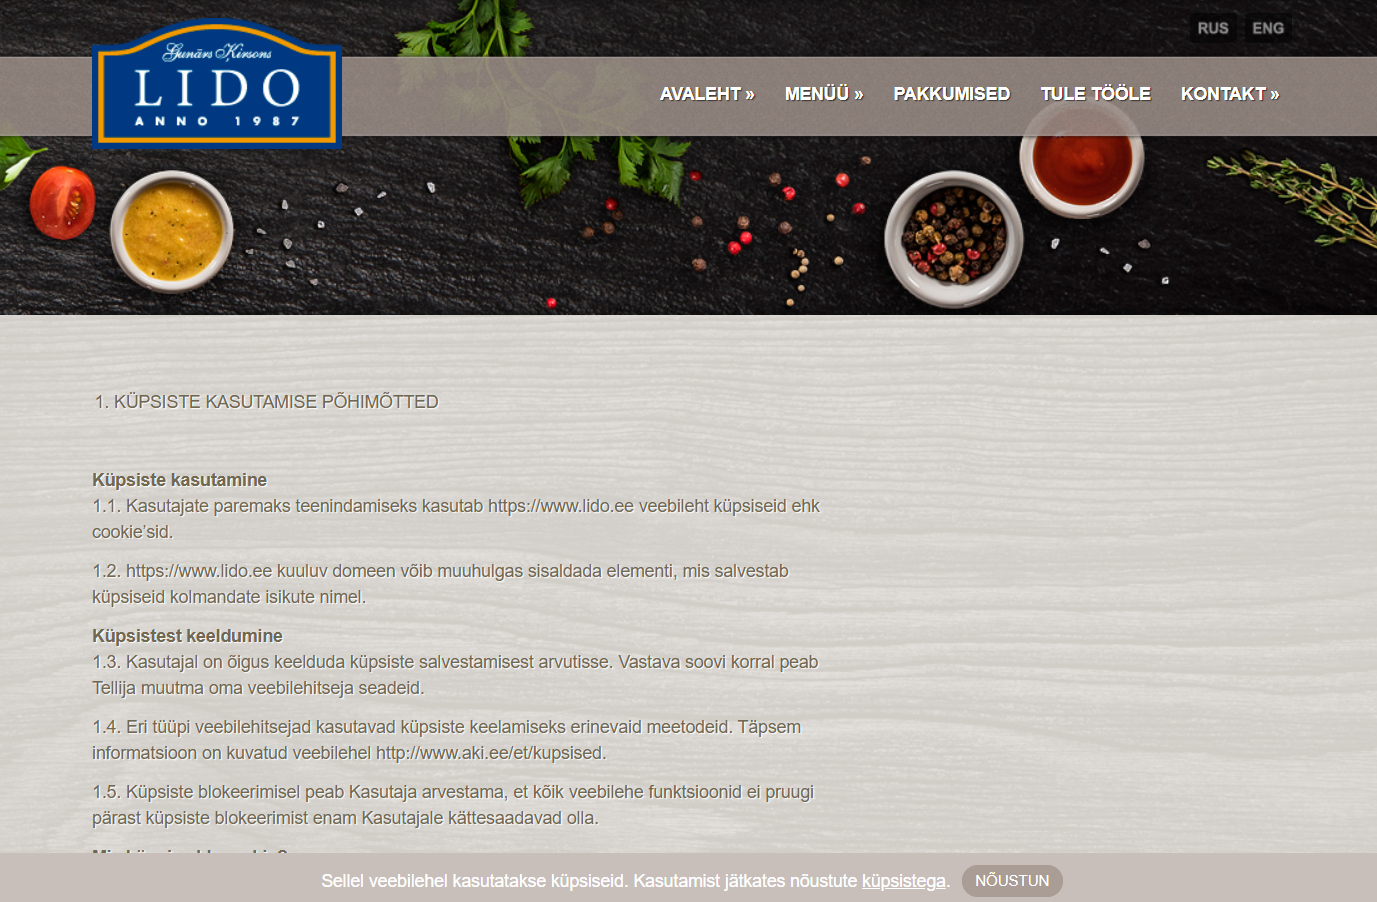
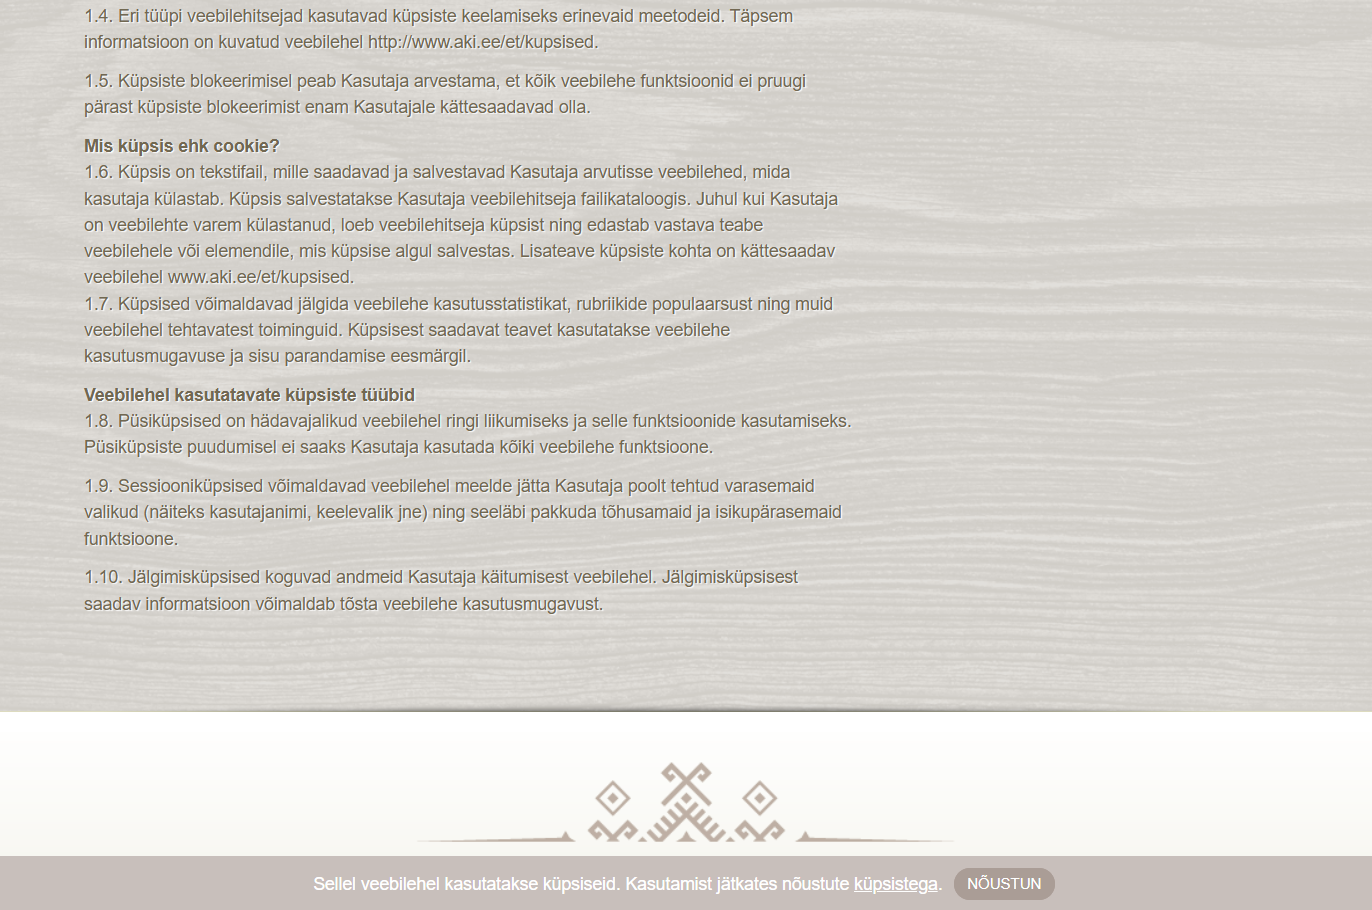
Attached to the material are a PDF snapshot of the site and three screenshots: the home page with the cookie notice and the cookie-use principles page.
The measurement consists of one recording, one navigation: the Russian version of the contacts page (/ru/контакт/), on which a Google map is embedded. Ninety-six requests, twelve nodes — all of the Google family. The recording was made on 18 September 2026.
Who data goes to directly
Google (Analytics 4, Tag Manager, Maps, Fonts, reCAPTCHA). There are no other third-party recipients — advertising, social networks, RTB — in the recording.
Declared versus actual
The general Apollo Group privacy policy refers for cookie details to the ‘cookie solution on the pages’ (clause 1.8), while a separate section on cookie principles acknowledges the presence of persistent, session and tracking cookies (jälgimisküpsised, ‘collect data on user behaviour on the site’, clause 1.10) and offers opting out only through browser settings (clause 1.3). Neither Google Analytics, nor Google Tag Manager, nor Google Maps is named by name as a recipient in the document.
The measurement shows a discrepancy.
There is no valid consent mechanism. A WordPress plugin, eDream Privacy Policy & Cookie Consent, operates on the site, displaying a notice: ‘This website uses cookies… If this is acceptable to you, continue using the page as usual’ with a single ‘Agree’ button (in the Estonian version, ‘Nõustun’). There is no reject button and no category choice. This is an implied-consent-by-continued-browsing model, which is not valid consent under ePrivacy.
Analytics goes out before consent. The Google Tag Manager container (GTM-N2B53T57) loads at +735 ms, and Google Analytics 4 (G-VRW2QE1E4V) sends a page_view at +3272 ms — without a consent-mode signal (gcs is absent) and without any interaction with the notice. The eDream plugin does not block the tags.
Embedded Google map. The contacts page contains a Google My Maps map (www.google.com/maps/d/embed and requests to maps.googleapis.com, maps.gstatic.com, mt.googleapis.com), which entails the transmission of data and of the visitor’s IP address to Google. Google Maps is not named as a recipient in the document.
Functional nodes: Google Fonts (fonts.gstatic.com) — the Roboto font, whose loading makes the IP address visible to Google; Google reCAPTCHA (www.google.com/recaptcha, www.gstatic.com) — form protection; csp.withgoogle.com — receiving content-security-policy violation reports.
Consent: what is proven and what is not
Proven: there is no valid consent mechanism. There is no dedicated consent-management platform in the recording; the site has the eDream plugin, displaying an implied-consent notice with a single ‘Agree’ button, no refusal and no categories (screenshots).
Proven: analytics operates before consent and without a consent-mode signal. The GA4 page_view goes out at +3272 ms, the gcs parameter is absent from the request; the transmission occurs without interaction with the notice.
Proven: the site acknowledges tracking cookies. The cookie-principles section (clause 1.10) expressly names jälgimisküpsised that collect data on user behaviour.
Not proven and not asserted: the exact user choice. An implied-consent notice does not imply a recordable choice; this is immaterial to the conclusion, since analytics goes out independently of it.
Separately: the browser did not send a DNT header in this recording.
Bounds of observation
The measurement covers a single page — contacts. Observation captures the browser’s behaviour, not the internal side of the services: server-side processing and contractual relationships with recipients are not verified by a browser measurement. The legal assessment is made by the competent authority — in Estonia, Andmekaitse Inspektsioon.
The file is published redacted under a “lean” profile: cookie values in requests have been removed, the Cookie and Set-Cookie headers stripped; the redaction registry records 155 redactions and a checksum. The composition of recipients, the identifiers, the consent signal and the timings are read from the parameters of the requests themselves. No security headers are observed on the domain’s own responses; full visitor-identifier values are not reproduced in the analysis.
The identification of services relies on domains and address patterns: analytics — by google-analytics.com and property G-VRW2QE1E4V; the tag container — by googletagmanager.com and GTM-N2B53T57; the map — by maps.googleapis.com and maps/d/embed; the fonts — by fonts.gstatic.com; the cookie banner — by the edream-privacy-policy-cookie-consent plugin. The absence of advertising and social networks is established by the absence of requests to the corresponding nodes.
Conclusion
When the contacts page of the LIDO restaurant chain’s website is browsed, it sends a page_view event to Google Analytics 4 on load — without consent and without a consent-mode signal. There is no valid consent mechanism on the site: the eDream plugin displays a notice ‘by continuing to use the site you agree’ with a single ‘Agree’ button, with no reject button and no category choice, and does not block the tags. The embedded Google Maps map on the contacts page transmits data and the visitor’s IP address to Google. The general Apollo Group privacy policy refers to the cookie solution on the pages, itself acknowledges the presence of tracking cookies and offers opting out only through browser settings, but does not name the actual recipients of web data — Google Analytics, Google Tag Manager, Google Maps — by name.
Remediation: place Google Analytics and the other tags under actual prior blocking until explicit consent, and replace the implied-consent notice with a valid mechanism offering an equal-weight reject button and a category choice; set the consent-mode signal (gcs) in the Google Analytics requests; place the embedded Google Maps map under consent or replace it with a solution that does not transmit data before consent; name the actual recipients of web data in the documents by name — Google Analytics, Google Tag Manager, Google Maps — with their purposes and the legal basis for cross-border transfer stated; set security headers on the domain.
How to verify: download the file and compute its checksum — sha256sum file.har (Linux, macOS) or certutil -hashfile file.har SHA256 (Windows); it must match the one shown. The conclusions apply to the scope of this measurement — see the limitations of the method.
2ff5a773b807343d4dd4ab6e7fb3e8f8619be0e485469d5f7f7b975f32c5466d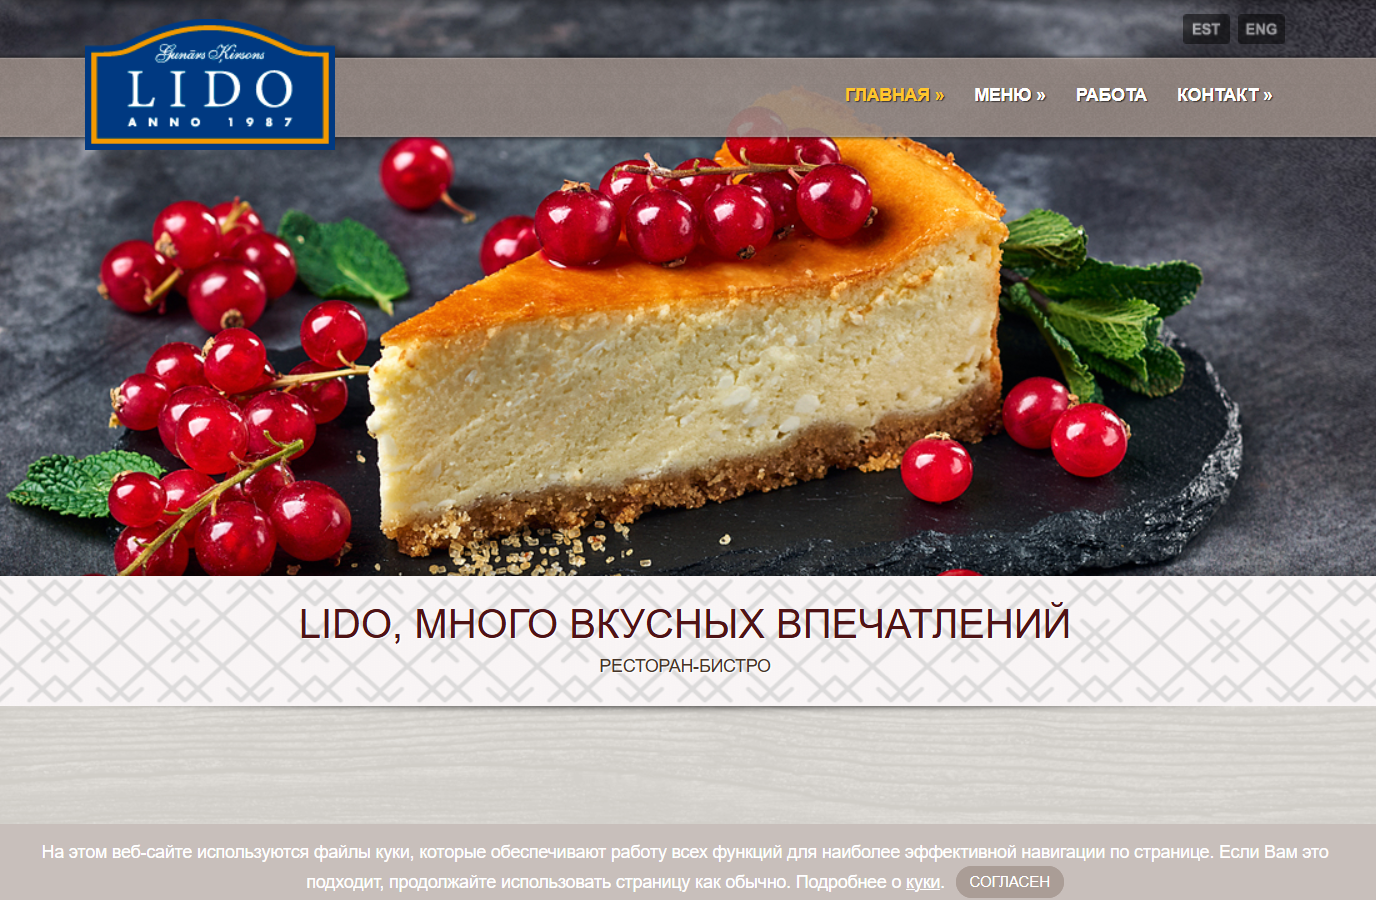
Want a response from the company about this audit? → Open the tool
Fill in once — it will be inserted into every letter below:
All fields are required to print the document — this is a formal requirement of the letter itself (the particulars of an official submission), not data collection: nothing is sent or saved anywhere, it all stays in your browser and disappears when you close the page. See the methodology for details.
RIA DigiDoc — phone · Smart-ID / Mobile-ID
Send this letter directly to the company first — before contacting the regulator it has the right to respond (GDPR Art. 12(3) — 30 days).
Тема: Запрос доступа к персональным данным (ст. 15 GDPR) — lido.ee

Кому: [укажите адрес компании — DPO / поддержка / юридический отдел]
От: [Ваше имя], [контактный email]

Прошу предоставить доступ к моим персональным данным, обрабатываемым в связи с использованием сайта lido.ee.

1. Категории данных и цели обработки (ст. 15(1)(a)-(c))
На основании независимого технического анализа сайта прошу подтвердить и подробно раскрыть следующие категории обработки:

1) Действительного механизма согласия на сайте нет. Установлен плагин WordPress eDream Privacy Policy & Cookie Consent, который выводит плашку «На этом веб-сайте используются файлы куки… продолжайте использовать страницу как обычно» с единственной кнопкой «Согласен» — без кнопки отказа и без выбора категорий. Это модель подразумеваемого согласия через продолжение просмотра, которая действительным согласием по ePrivacy и практике Суда ЕС не является. Плагин теги не блокирует: Google Tag Manager (GTM-N2B53T57) грузится на +735 мс, а Google Analytics 4 (G-VRW2QE1E4V) отправляет page_view на +3272 мс без сигнала режима согласия (gcs отсутствует) — до какого-либо взаимодействия с плашкой.

2) Общая политика приватности Apollo Group отсылает за деталями cookie к «cookie-решению на страницах» (п. 1.8) и не называет поимённо фактических получателей веб-данных: Google Analytics 4 (G-VRW2QE1E4V), Google Tag Manager и Google Maps как получатели в документе не названы. При этом сам документ (п. 1.10) признаёт наличие трекинговых cookie, собирающих данные о поведении пользователя.

3) Cookie-принципы сайта предлагают отказ от cookie только через настройки браузера (модель opt-out, п. 1.3) и признают трекинговые cookie (п. 1.10). Фактически аналитика Google уходит при загрузке страницы без согласия, а единственный экранный механизм — плашка подразумеваемого согласия без возможности отказа. Заявленный порядок (управление cookie, согласие) расходится с фактическим поведением.

4) Google Analytics 4 и встроенная карта Google Maps влекут передачу данных и адреса IP посетителя Google (узлы за пределами ЕЭЗ); шрифты подгружаются с серверов Google. Правовое основание трансграничной передачи в отношении этих получателей в документе поимённо не раскрыто.


2. Получатели, сроки хранения и передача за пределы ЕЭЗ (ст. 15(1)(c)-(d), 46)
Прошу также указать полный список третьих лиц-получателей, применимые сроки хранения по каждой категории и правовые основания передачи данных за пределы ЕЭЗ, если таковая происходит. Полный технический разбор с доказательствами (сохранённый сетевой журнал, контрольная сумма SHA-256) опубликован по адресу: https://gdpru.eu/en/audits/ee-lido-ee/

3. Автоматизированная обработка и профилирование (ст. 15(1)(h))
Прошу сообщить, применяется ли в отношении меня автоматизированное принятие решений или профилирование, и если да — раскрыть логику такой обработки.

С уважением,

[Ваше имя]
[контактный email]
[Страна]


[Дата]
Subject: Data access request (GDPR Art. 15) — lido.ee

To: [insert the company's address — DPO / support / legal department]
From: [Your name], [contact email]

I request access to my personal data processed in connection with the website lido.ee.

1. Categories of data and purposes of processing (Art. 15(1)(a)-(c))
Based on an independent technical analysis of the site, I request confirmation and detailed disclosure of the following categories of processing:

1) There is no valid consent mechanism on the site. A WordPress plugin, eDream Privacy Policy & Cookie Consent, is installed, which displays a notice — 'This website uses cookies… continue using the page as usual' — with a single 'Agree' button, with no reject button and no category choice. This is an implied-consent-by-continued-browsing model, which is not valid consent under ePrivacy and the case law of the Court of Justice. The plugin does not block tags: Google Tag Manager (GTM-N2B53T57) loads at +735 ms, and Google Analytics 4 (G-VRW2QE1E4V) sends a page_view at +3272 ms without a consent-mode signal (gcs is absent) — before any interaction with the notice.

2) The general Apollo Group privacy policy refers for cookie details to the 'cookie solution on the pages' (clause 1.8) and does not name by name the actual recipients of web data: Google Analytics 4 (G-VRW2QE1E4V), Google Tag Manager and Google Maps are not named as recipients in the document. At the same time the document itself (clause 1.10) acknowledges the presence of tracking cookies that collect data on user behaviour.

3) The site's cookie principles offer opting out of cookies only through browser settings (the opt-out model, clause 1.3) and acknowledge tracking cookies (clause 1.10). In fact Google analytics goes out on page load without consent, and the only on-screen mechanism is an implied-consent notice with no option to refuse. The declared arrangement (cookie management, consent) diverges from the actual behaviour.

4) Google Analytics 4 and the embedded Google Maps map entail the transmission of data and of the visitor's IP address to Google (nodes outside the EEA); fonts are loaded from Google servers. The legal basis for the cross-border transfer as regards these recipients is not disclosed by name in the document.


2. Recipients, retention periods, and transfers outside the EEA (Art. 15(1)(c)-(d), 46)
I also request the full list of third-party recipients, the applicable retention period for each category, and the legal basis for any transfer of data outside the EEA. The full technical audit with evidence (saved network log, SHA-256 checksum) is published at: https://gdpru.eu/en/audits/ee-lido-ee/

3. Automated processing and profiling (Art. 15(1)(h))
Please state whether I am subject to automated decision-making or profiling, and if so, disclose the logic involved.

Sincerely,

[Your name]
[contact email]
[Country]


[Date]
Teema: Isikuandmetele juurdepääsu taotlus (IKÜM art 15) — lido.ee

Kellele: [märkige ettevõtte aadress — DPO / tugi / juriidiline osakond]
Kellelt: [Teie nimi], [kontakt-e-post]

Palun anda mulle juurdepääs minu isikuandmetele, mida töödeldakse seoses veebisaidi lido.ee kasutamisega.

1. Andmekategooriad ja töötlemise eesmärgid (IKÜM art 15(1)(a)-(c))
Sõltumatu tehnilise analüüsi põhjal palun kinnitada ja üksikasjalikult avaldada järgmised töötlemiskategooriad:

1) Veebilehel puudub kehtiv nõusoleku mehhanism. Paigaldatud on WordPressi eDreami privaatsuspoliitika ja küpsiste nõusoleku plugin, mis kuvab "Küpsised on sellel veebisaidil kasutatud ... jätkake lehe kasutamist nagu tavaliselt" sildiga, millel on üks "Nõustun" nupp - loobumisnupp ja kategooria valik puudub. See on kaudse nõusoleku mudel pideva sirvimise kaudu, mis ei kujuta endast kehtivat nõusolekut e-privaatsuse ja Euroopa Liidu Kohtu praktika kohaselt. Sildiplugin ei blokeeri: Google Tag Manager (GTM-N2B53T57) laadib +735 ms-le ja Google Analytics 4 (G-VRW2QE1E4V) saadab lehevaate +3272 ms-le ilma nõusolekurežiimi signaalita (gcs puudub) - enne mis tahes suhtlust plaadiga.

2) Apollo Groupi üldine privaatsuspoliitika viitab küpsiste üksikasjadele "küpsiste lahendusele lehtedel" (punkt 1.8) ega nimeta veebiandmete tegelikke saajaid: Google Analytics 4 (G-VRW2QE1E4V), Google Tag Manager ja Google Maps kui dokumendi saajad ei ole nimetatud. Samal ajal tunnistab dokument ise (punkt 1.10) jälgimisküpsiste olemasolu, mis koguvad andmeid kasutaja käitumise kohta.

3) Veebisaidi küpsiste põhimõtted soovitavad küpsistest keelduda ainult brauseri seadete kaudu (opt-out mudel, punkt 1.3) ja tuvastada jälgimisküpsised (punkt 1.10). Tegelikult läheb Google'i analüütika ära, kui leht laadib ilma nõusolekuta, ja ainus ekraanimehhanism on kaudse nõusoleku tahvel ilma keeldumise võimaluseta. Nimetatud menetlus (küpsiste haldamine, nõusolek) erineb tegelikust käitumisest.

4) Google Analytics 4 ja sisseehitatud Google Maps hõlmavad Google'i külastaja andmete ja IP-aadresside edastamist (sõlmed väljaspool EMP-d); fondid laaditakse alla Google'i serveritest. Nende vastuvõtjate piiriülese üleandmise õiguslikku alust dokumendis nimeliselt ei avaldata.


2. Vastuvõtjad, säilitustähtajad ja edastamine väljapoole EMP-d (IKÜM art 15(1)(c)-(d), 46)
Palun samuti esitada täielik loetelu kolmandatest isikutest vastuvõtjatest, iga kategooria puhul kohaldatavad säilitustähtajad ning andmete EMP-välisele edastamisele kohaldatav õiguslik alus, kui selline edastamine toimub. Täielik tehniline analüüs koos tõenditega (salvestatud võrgulogi, SHA-256 kontrollsumma) on avaldatud aadressil: https://gdpru.eu/en/audits/ee-lido-ee/

3. Automatiseeritud töötlemine ja profiilianalüüs (IKÜM art 15(1)(h))
Palun teatada, kas minu suhtes kohaldatakse automatiseeritud otsuste tegemist või profiilianalüüsi, ning kui jah, siis avaldada selle loogika.

Lugupidamisega,

[Teie nimi]
[kontakt-e-post]
[Riik]


[Kuupäev]
RIA DigiDoc — phone · Smart-ID / Mobile-ID
Where to file: Estonian Data Protection Inspectorate (AKI) — write to info@aki.ee
Important: AKI only handles submissions in Estonian. Translate the letter before sending.
The regulator reviews complaints in its national language. There is an officially translated template from the European Data Protection Board (EDPB) — you can use it instead of or alongside this letter: Official EDPB complaint form (PDF, your language)
Тема: Жалоба на обработку персональных данных — lido.ee

1. Предмет жалобы
Я подаю жалобу в отношении обработки моих персональных данных сайтом lido.ee.

2. Обстоятельства
Я посетил сайт lido.ee и обнаружил признаки несоответствия обработки моих персональных данных требованиям GDPR. Технический разбор, опубликованный на gdpru.eu 19.09.2026 (открытая методология, воспроизводимые измерения), документирует следующие признаки:

1) Действительного механизма согласия на сайте нет. Установлен плагин WordPress eDream Privacy Policy & Cookie Consent, который выводит плашку «На этом веб-сайте используются файлы куки… продолжайте использовать страницу как обычно» с единственной кнопкой «Согласен» — без кнопки отказа и без выбора категорий. Это модель подразумеваемого согласия через продолжение просмотра, которая действительным согласием по ePrivacy и практике Суда ЕС не является. Плагин теги не блокирует: Google Tag Manager (GTM-N2B53T57) грузится на +735 мс, а Google Analytics 4 (G-VRW2QE1E4V) отправляет page_view на +3272 мс без сигнала режима согласия (gcs отсутствует) — до какого-либо взаимодействия с плашкой.

2) Общая политика приватности Apollo Group отсылает за деталями cookie к «cookie-решению на страницах» (п. 1.8) и не называет поимённо фактических получателей веб-данных: Google Analytics 4 (G-VRW2QE1E4V), Google Tag Manager и Google Maps как получатели в документе не названы. При этом сам документ (п. 1.10) признаёт наличие трекинговых cookie, собирающих данные о поведении пользователя.

3) Cookie-принципы сайта предлагают отказ от cookie только через настройки браузера (модель opt-out, п. 1.3) и признают трекинговые cookie (п. 1.10). Фактически аналитика Google уходит при загрузке страницы без согласия, а единственный экранный механизм — плашка подразумеваемого согласия без возможности отказа. Заявленный порядок (управление cookie, согласие) расходится с фактическим поведением.

4) Google Analytics 4 и встроенная карта Google Maps влекут передачу данных и адреса IP посетителя Google (узлы за пределами ЕЭЗ); шрифты подгружаются с серверов Google. Правовое основание трансграничной передачи в отношении этих получателей в документе поимённо не раскрыто.

Полная техническая документация опубликована по адресу: https://gdpru.eu/en/audits/ee-lido-ee/

3. Положения GDPR, соблюдение которых прошу проверить
ePrivacy — Директива 2002/58/EC, ст. 5(3) (в связке с GDPR Art. 6(1)(a)); GDPR Art. 13(1)(e) — раскрытие получателей; GDPR Art. 5(1)(a) — прозрачность: заявленное расходится с фактическим; GDPR Art. 44 — передача в третью страну

4. Требование
Прошу проверить изложенные обстоятельства и, если несоответствие подтвердится, принять меры, предусмотренные статьёй 58(2) GDPR.

5. Приложения
Полная доказательная база — HAR-файл, контрольная сумма SHA-256 и цитата из политики конфиденциальности сайта, документирующая указанное противоречие — опубликована и проверяема по ссылке в пункте 2 выше.

С уважением,

[Ваше имя]
[контактный email]
[Страна]


[Дата]
Subject: Complaint regarding personal data processing — lido.ee

1. Subject of the complaint
I am filing a complaint regarding the processing of my personal data by the website lido.ee.

2. Circumstances
I visited the website lido.ee and found indications that the processing of my personal data does not comply with the GDPR. The technical analysis published on gdpru.eu on 19 September 2026 (open methodology, reproducible measurements) documents the following indications:

1) There is no valid consent mechanism on the site. A WordPress plugin, eDream Privacy Policy & Cookie Consent, is installed, which displays a notice — 'This website uses cookies… continue using the page as usual' — with a single 'Agree' button, with no reject button and no category choice. This is an implied-consent-by-continued-browsing model, which is not valid consent under ePrivacy and the case law of the Court of Justice. The plugin does not block tags: Google Tag Manager (GTM-N2B53T57) loads at +735 ms, and Google Analytics 4 (G-VRW2QE1E4V) sends a page_view at +3272 ms without a consent-mode signal (gcs is absent) — before any interaction with the notice.

2) The general Apollo Group privacy policy refers for cookie details to the 'cookie solution on the pages' (clause 1.8) and does not name by name the actual recipients of web data: Google Analytics 4 (G-VRW2QE1E4V), Google Tag Manager and Google Maps are not named as recipients in the document. At the same time the document itself (clause 1.10) acknowledges the presence of tracking cookies that collect data on user behaviour.

3) The site's cookie principles offer opting out of cookies only through browser settings (the opt-out model, clause 1.3) and acknowledge tracking cookies (clause 1.10). In fact Google analytics goes out on page load without consent, and the only on-screen mechanism is an implied-consent notice with no option to refuse. The declared arrangement (cookie management, consent) diverges from the actual behaviour.

4) Google Analytics 4 and the embedded Google Maps map entail the transmission of data and of the visitor's IP address to Google (nodes outside the EEA); fonts are loaded from Google servers. The legal basis for the cross-border transfer as regards these recipients is not disclosed by name in the document.

Full technical documentation is published at: https://gdpru.eu/en/audits/ee-lido-ee/

3. GDPR provisions I ask you to examine
ePrivacy — Directive 2002/58/EC, Art. 5(3) (in conjunction with GDPR Art. 6(1)(a)); GDPR Art. 13(1)(e) — disclosure of recipients; GDPR Art. 5(1)(a) — transparency: the declared diverges from the actual; GDPR Art. 44 — transfer to a third country

4. Request
I request that you examine the circumstances described and, if non-compliance is confirmed, apply the measures provided for in Article 58(2) GDPR.

5. Attachments
The full evidence base — the HAR file, its SHA-256 checksum and the quotation from the site's privacy policy documenting the stated contradiction — is published and verifiable at the link in point 2 above.

Sincerely,

[Your name]
[contact email]
[Country]


[Date]
1. Kaebuse ese
Esitan kaebuse seoses minu isikuandmete töötlemisega veebisaidil lido.ee.

2. Asjaolud
Külastasin veebisaiti lido.ee ja tuvastasin märke sellest, et minu isikuandmete töötlemine ei vasta isikuandmete kaitse üldmääruse (IKÜM) nõuetele. Tehniline analüüs, mis on avaldatud aadressil gdpru.eu 19.09.2026 (avatud metoodika, korratavad mõõtmised), dokumenteerib järgmist:

1) Veebilehel puudub kehtiv nõusoleku mehhanism. Paigaldatud on WordPressi eDreami privaatsuspoliitika ja küpsiste nõusoleku plugin, mis kuvab "Küpsised on sellel veebisaidil kasutatud ... jätkake lehe kasutamist nagu tavaliselt" sildiga, millel on üks "Nõustun" nupp - loobumisnupp ja kategooria valik puudub. See on kaudse nõusoleku mudel pideva sirvimise kaudu, mis ei kujuta endast kehtivat nõusolekut e-privaatsuse ja Euroopa Liidu Kohtu praktika kohaselt. Sildiplugin ei blokeeri: Google Tag Manager (GTM-N2B53T57) laadib +735 ms-le ja Google Analytics 4 (G-VRW2QE1E4V) saadab lehevaate +3272 ms-le ilma nõusolekurežiimi signaalita (gcs puudub) - enne mis tahes suhtlust plaadiga.

2) Apollo Groupi üldine privaatsuspoliitika viitab küpsiste üksikasjadele "küpsiste lahendusele lehtedel" (punkt 1.8) ega nimeta veebiandmete tegelikke saajaid: Google Analytics 4 (G-VRW2QE1E4V), Google Tag Manager ja Google Maps kui dokumendi saajad ei ole nimetatud. Samal ajal tunnistab dokument ise (punkt 1.10) jälgimisküpsiste olemasolu, mis koguvad andmeid kasutaja käitumise kohta.

3) Veebisaidi küpsiste põhimõtted soovitavad küpsistest keelduda ainult brauseri seadete kaudu (opt-out mudel, punkt 1.3) ja tuvastada jälgimisküpsised (punkt 1.10). Tegelikult läheb Google'i analüütika ära, kui leht laadib ilma nõusolekuta, ja ainus ekraanimehhanism on kaudse nõusoleku tahvel ilma keeldumise võimaluseta. Nimetatud menetlus (küpsiste haldamine, nõusolek) erineb tegelikust käitumisest.

4) Google Analytics 4 ja sisseehitatud Google Maps hõlmavad Google'i külastaja andmete ja IP-aadresside edastamist (sõlmed väljaspool EMP-d); fondid laaditakse alla Google'i serveritest. Nende vastuvõtjate piiriülese üleandmise õiguslikku alust dokumendis nimeliselt ei avaldata.

Täielik tehniline dokumentatsioon on avaldatud aadressil: https://gdpru.eu/en/audits/ee-lido-ee/

3. Sätted, mille järgimist palun kontrollida
e-privaatsus – direktiiv 2002/58/EÜ, artikli 5 lõige 3 (koosmõjus GDPRi artikli 6 lõike 1 punktiga a); GDPR – artikli 13 lõike 1 punkt e – vastuvõtjate avalikustamine; GDPR art 5(1)(a) Läbipaistvus: väide on vastuolus tegeliku; GDPR artikkel 44 – Andmete edastamine kolmandasse riiki

4. Nõue
Palun kontrollida kirjeldatud asjaolusid ja mittevastavuse kinnitamisel kohaldada IKÜM artikli 58 lõikes 2 ette nähtud meetmeid.

5. Lisad
Täielik tõendusmaterjal — HAR-fail, kontrollsumma SHA-256 ning veebisaidi privaatsuspoliitika tsitaat, mis dokumenteerib nimetatud vastuolu — on avaldatud ja kontrollitav punktis 2 viidatud lingil.

Lugupidamisega,

[Teie nimi]
[kontakt-e-post]
[Riik]


[Kuupäev]