
Website of the La Bocca pizzeria chain in Tallinn — one recording, 4 navigations, 493 requests, ten nodes. On load, a full Google and Facebook stack launches immediately and without consent: Google Analytics 4, Google Ads and DoubleClick with remarketing audiences, and the Facebook Pixel with a booking-conversion event (Schedule). A consent banner exists on the site, but in the recording it does not block the tags, and in the screenshots all of its categories — analytics, Google, Facebook, TikTok — are on by default. The policy declares processing 'on the basis of consent', which diverges from the actual behaviour. The browser did not send a DNT header.
Request timeline
Declared versus actual
Transfer timings
GTM-5ZLM5QFT.
Facebook Pixel fbevents.js, identifier 1181274603647499.
ccm/s/collect — Google Ads / DoubleClick.
GA4 page_view (G-5ZNJL5JS4M) without a gcs consent-mode signal.
ads/ga-audiences — remarketing audiences.
/tr — a PageView event; later — Schedule (conversion).
Detected trackers
- Google Analytics 4 (G-5ZNJL5JS4M) via region1.analytics.google.com — page_view and scroll events without a consent-mode signal; go out on load
- Google Ads / DoubleClick (ad.doubleclick.net/ccm/s/collect, stats.g.doubleclick.net, www.google.com/ccm/collect, www.google.ee/ads/ga-audiences) — conversions and remarketing audiences
- Facebook Pixel (1181274603647499) via connect.facebook.net and www.facebook.com/tr — PageView and Schedule events (a booking conversion)
- Google Tag Manager (www.googletagmanager.com, container GTM-5ZLM5QFT) — tag container
- Booking engine (mv-prod-1-1053047382554.us-central1.run.app) — receives /events (Google Cloud Run)
- Adyen — payment processing (declared in the policy; not observed as a separate node in the recording)
Indicators of GDPR non-compliance
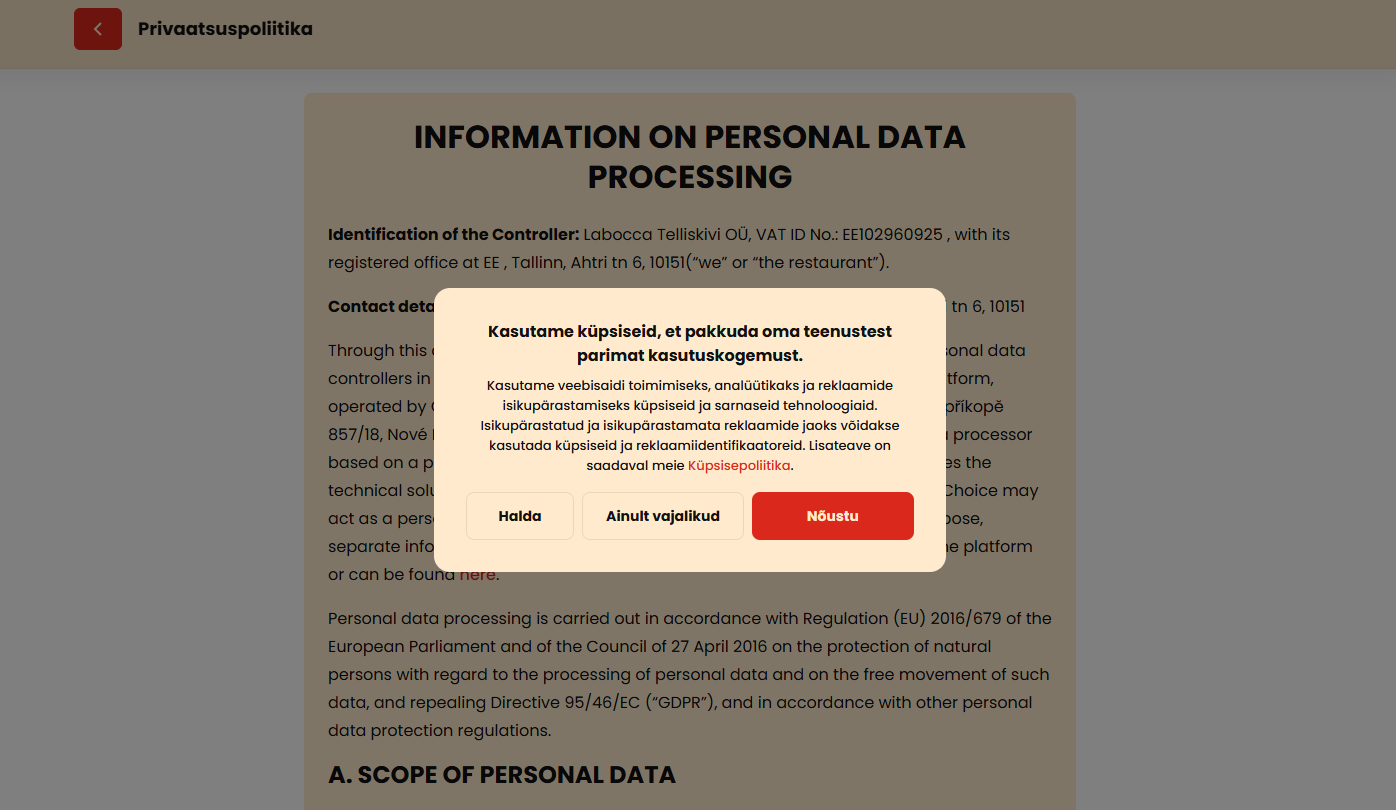
- ePrivacy — Directive 2002/58/EC, Art. 5(3) (in conjunction with GDPR Art. 6(1)(a))A consent banner exists on the site (visible in the screenshots, on the policy page), but in the recording it does not block tags, and its categories are on by default. Google Tag Manager (GTM-5ZLM5QFT) loads at +1277 ms, the Facebook Pixel (fbevents.js) at +1278 ms, and at +2523…+2766 ms the following go out at once: a Google Ads conversion (www.google.com/ccm/collect), DoubleClick (ad.doubleclick.net/ccm/s/collect), a Google Analytics 4 page_view (G-5ZNJL5JS4M), the DoubleClick link (stats.g.doubleclick.net), remarketing audiences (www.google.ee/ads/ga-audiences) and a Facebook PageView event. All of this happens immediately on load, before any user choice. There is no dedicated consent-management platform (Cookiebot, CookieYes, Funding Choices and the like) in the recording: not a single request to a CMP, no Consent Mode signal.
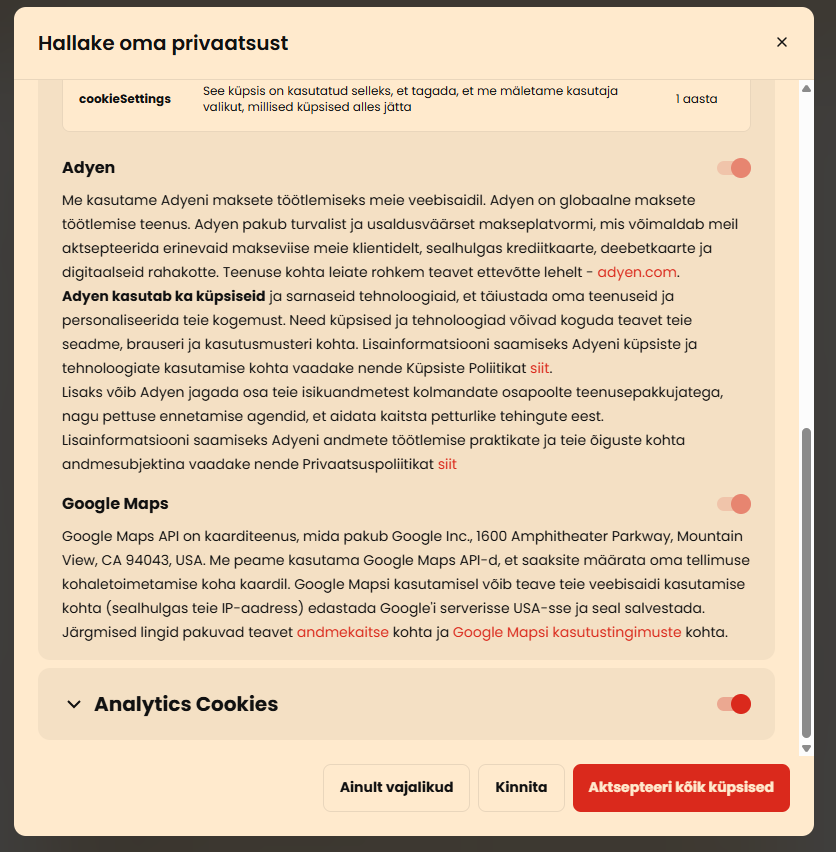
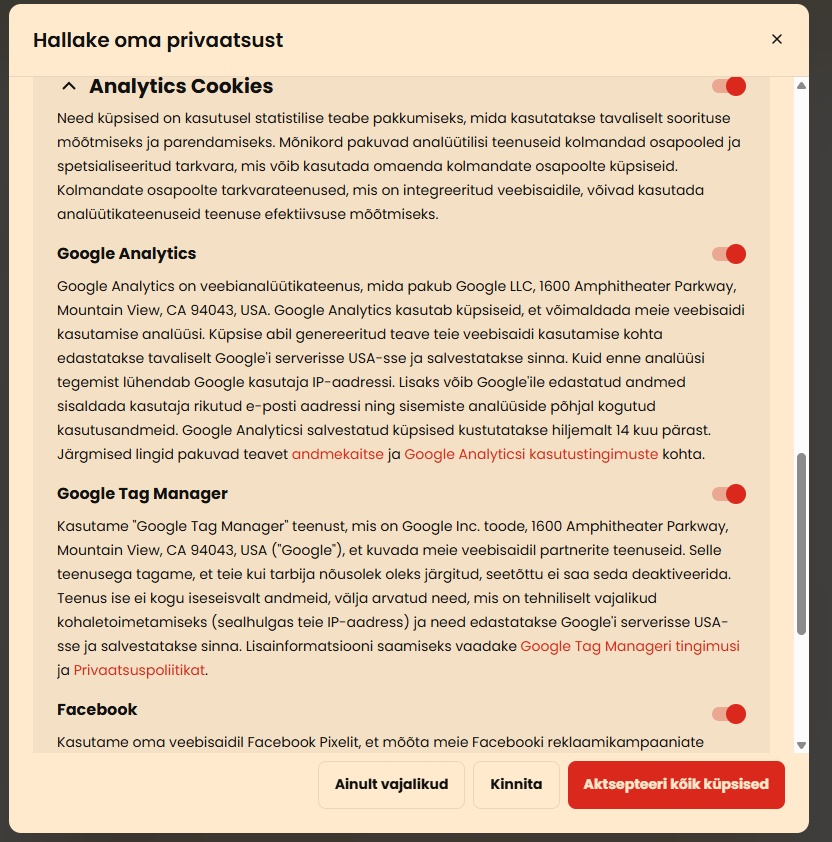
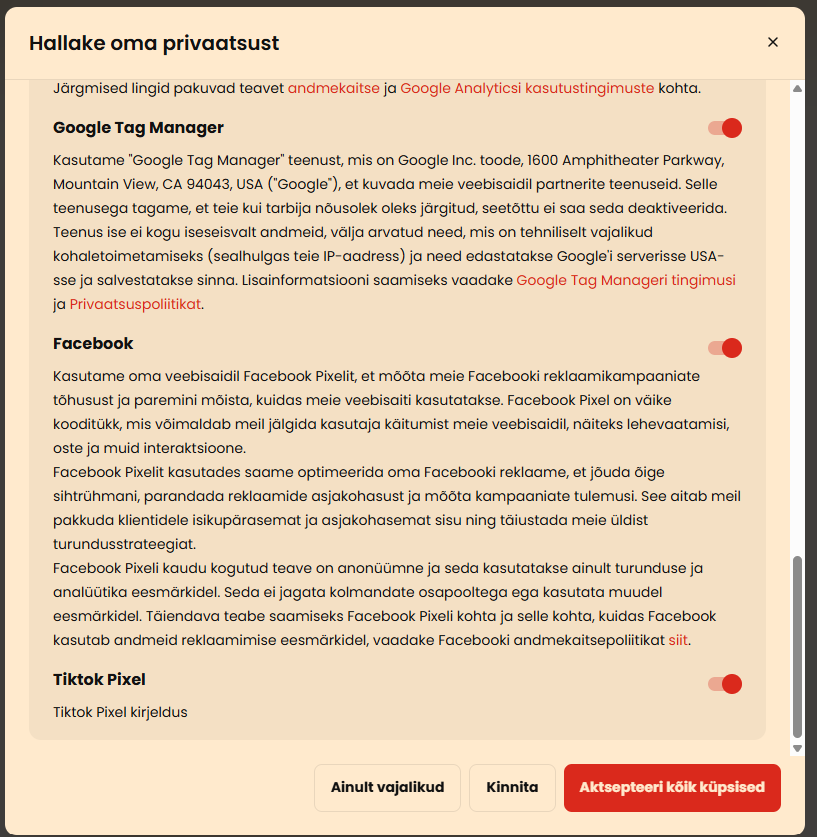
- GDPR Art. 4(11), Art. 7 — invalid consent (pre-ticked categories)In the cookie-settings window in the screenshots, all categories — 'Analytics Cookies', Google Maps, Google Analytics, Google Tag Manager, Facebook, TikTok Pixel, Adyen — are on by default (the toggles are in the 'on' position). Pre-ticked consent is invalid: consent must be an affirmative action, not a pre-set box. This is consistent with the actual behaviour: the analytics and advertising tags fire before any interaction with the banner.
- GDPR Art. 5(1)(a) — transparency: the declared diverges from the actualThe policy states that Google and its partners process data 'on the basis of your consent' and that consent can be managed through the cookie settings. In fact processing begins before consent and with the categories pre-ticked. In addition, the Facebook Pixel is described in the policy as collecting 'anonymous' information used only for marketing and analytics and not shared with third parties; in fact the pixel (identifier 1181274603647499) sends a Schedule conversion event in addition to PageView, which is not an anonymous count. The TikTok Pixel description in the policy is left as an unfilled template ('Tiktok Pixel kirjeldus').
- GDPR Art. 13(1)(e) / Art. 44 — disclosure of recipients and transfer to a third countryThe policy names recipients (Google Analytics, Google Tag Manager, Google Maps, Facebook Pixel, TikTok Pixel, Adyen) but does not disclose by name the Google Ads / DoubleClick remarketing chain (ga-audiences, ccm/collect) that actually operates in the recording. Transfer to Google, Facebook and (per the policy) the US is described in general terms; the legal basis for the cross-border transfer as regards advertising remarketing and the Facebook Pixel is not detailed.
Context
labocca.ee is the website of the La Bocca (Pizza e Pasta) pizzeria chain in Tallinn. The controller is Labocca Telliskivi OÜ (VAT EE102960925), Ahtri tn 6, Tallinn. The site is built on WordPress (Elementor, WPML multilingual), Apache/ZoneOS server; booking is served by an engine on Google Cloud Run.
Processing is described by the attached data-protection and cookie document (Privaatsuspoliitika / cookie terms), which references Regulation (EU) 2016/679. Attached to the material are a PDF snapshot of the site and five screenshots: the home page and the cookie-management window with its categories.
The measurement consists of one recording, four navigations: the home page, /restoranid/, /uritused/. Four hundred and ninety-three requests, ten nodes. The recording was made on 20 September 2026.
Who data goes to directly
Google (Analytics 4, Ads/DoubleClick with remarketing, Tag Manager), Facebook (Pixel); the booking engine on Google Cloud Run. Adyen and the TikTok Pixel are declared in the policy but were not observed as separate nodes in this recording.
Declared versus actual
The cookie document is detailed and names recipients by name: Adyen (payments), Google Maps, Google Analytics, Google Tag Manager, Facebook Pixel, TikTok Pixel. The policy states plainly that Google and its partners process data ‘on the basis of your consent’ and that consent can be managed through the cookie settings; it references the GDPR.
The measurement shows several discrepancies.
The Google and Facebook stack launches immediately, without consent. The Google Tag Manager container (GTM-5ZLM5QFT) loads at +1277 ms, the Facebook Pixel (fbevents.js) at +1278 ms. At +2523…+2766 ms the following go out at once: a Google Ads conversion (www.google.com/ccm/collect), DoubleClick (ad.doubleclick.net/ccm/s/collect), a Google Analytics 4 page_view (region1.analytics.google.com, G-5ZNJL5JS4M), the DoubleClick link (stats.g.doubleclick.net), remarketing audiences (www.google.ee/ads/ga-audiences) and a Facebook PageView event (1181274603647499). All of this is on load, before any user choice. Google Analytics 4 sends its requests without a consent-mode signal (gcs is absent).
A consent banner exists, but does not block and is pre-ticked. There is no dedicated consent-management platform (Cookiebot, CookieYes, Funding Choices and the like) in the recording — not a single request to a CMP, no Consent Mode signal. Yet a consent banner is present on the site: the screenshots show a ‘Hallake oma privaatsust’ window with the categories Adyen, Google Maps, Analytics, Google Analytics, Google Tag Manager, Facebook, TikTok Pixel. All of them are on by default (the toggles are in the ‘on’ position), meaning consent is pre-ticked rather than requested by an affirmative action. The banner is therefore decorative: the tags fire independently of it and before any choice.
The Facebook Pixel sends a conversion, not an ‘anonymous’ count. The policy describes the Facebook Pixel as collecting ‘anonymous’ information for marketing and analytics only. In fact the pixel sends not only PageView but also a Schedule event (+69388 ms) — a conversion linked to booking, with the pixel identifier. This is behavioural conversion tracking, not anonymous statistics.
Google remarketing is not disclosed in the policy; TikTok is a template. The Google Ads / DoubleClick remarketing chain (ga-audiences, ccm/collect) actually operates but is not described by name in the policy. The TikTok Pixel description is left as an unfilled template (‘Tiktok Pixel kirjeldus’), although TikTok did not fire in the recording.
Functional and first-party nodes: the booking engine (mv-prod-1-…run.app/events, Google Cloud Run) receives booking events; Adyen is declared for payments but was not observed as a separate node in this recording (no payment was completed).
Consent: what is proven and what is not
Proven: the Google and Facebook stack transmits data before consent. GTM and the Facebook Pixel load at +1277…+1278 ms, the first transmissions (GA4, Google Ads, DoubleClick, remarketing, Facebook PageView) at +2523…+2766 ms, on page load, without interaction with the banner.
Proven: there is no dedicated consent platform in the recording. A check against the domains of known CMPs and against Consent Mode signals (gtag('consent'), gcs=, __tcfapi) yielded no matches.
Proven: the categories in the banner are on by default. In the screenshots the toggles for Analytics, Google Analytics, Google Tag Manager, Facebook, TikTok, Google Maps, Adyen are in the ‘on’ position.
Proven: the Facebook Pixel sends a conversion event. By the www.facebook.com/tr requests with the PageView and Schedule events and the identifier 1181274603647499.
Not proven and not asserted: the exact user choice. What was chosen in the banner is not established by the recording and is immaterial to the conclusion: the tags fired before any choice and with the categories pre-ticked.
Separately: the browser did not send a DNT header in this recording.
Bounds of observation
The measurement covers four pages of the site. Observation captures the browser’s behaviour, not the internal side of the services: server-side processing and contractual relationships with recipients are not verified by a browser measurement. The legal assessment is made by the competent authority — in Estonia, Andmekaitse Inspektsioon.
The file is published redacted under a “lean” profile: cookie values in requests have been removed, the Cookie and Set-Cookie headers stripped; the redaction registry records 635 redactions and a checksum. The composition of recipients, the identifiers, the events and the timings are read from the parameters of the requests themselves. The presence and state of the consent banner are established from the attached screenshots, since there is no dedicated consent service in the network recording itself; no security headers are observed on the domain’s responses; full visitor-identifier values are not reproduced in the analysis.
The identification of services relies on domains and address patterns: the tag container — by googletagmanager.com and GTM-5ZLM5QFT; Google Analytics — by analytics.google.com and G-5ZNJL5JS4M; Google Ads / DoubleClick — by doubleclick.net, google.com/ccm, google.ee/ads/ga-audiences; the Facebook Pixel — by connect.facebook.net, www.facebook.com/tr and the identifier 1181274603647499; the booking engine — by run.app.
Conclusion
The La Bocca pizzeria chain’s website, on load, immediately and without consent launches a full Google and Facebook stack: Google Analytics 4, Google Ads and DoubleClick with remarketing audiences, and the Facebook Pixel with a booking-conversion event. A consent banner exists on the site, but in the recording it does not block the tags, and in the screenshots all of its categories — analytics, Google, Facebook, TikTok — are on by default, meaning consent is pre-ticked and invalid. The policy declares processing ‘on the basis of consent’ and describes the Facebook Pixel as ‘anonymous’, which diverges from the actual behaviour: the tags operate before consent, and the pixel sends a conversion event with an identifier. The Google Ads / DoubleClick remarketing is not disclosed by name in the policy, and the TikTok Pixel description is left unfilled.
Remediation: place Google Analytics, Google Ads / DoubleClick, the Facebook Pixel and the other analytics and advertising tags under actual prior blocking until explicit consent; make the categories in the banner off by default, so that consent is an affirmative action rather than a pre-ticked box; bring the description of the Facebook Pixel into line with the facts (sending conversion events with an identifier, not an anonymous count); disclose the Google Ads / DoubleClick remarketing in the policy by name and fill in the TikTok Pixel description or remove it; set the consent-mode signal (gcs) in the Google Analytics requests; set security headers on the domain.
How to verify: download the file and compute its checksum — sha256sum file.har (Linux, macOS) or certutil -hashfile file.har SHA256 (Windows); it must match the one shown. The conclusions apply to the scope of this measurement — see the limitations of the method.
09b1646c93af7fefaf6ebbc706bdad06c8a6d990c19282580090d29627568a2d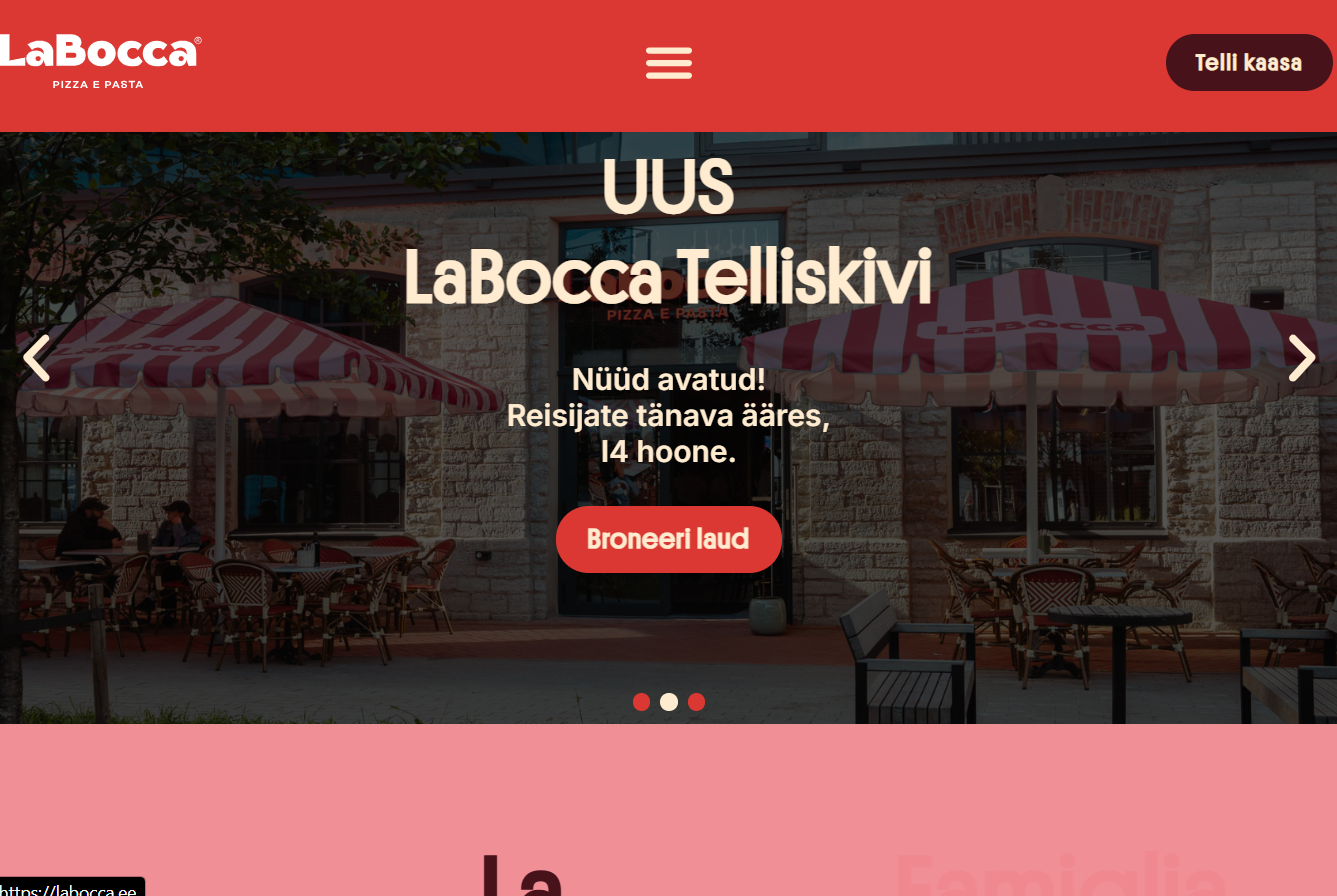
Want a response from the company about this audit? → Open the tool
Fill in once — it will be inserted into every letter below:
All fields are required to print the document — this is a formal requirement of the letter itself (the particulars of an official submission), not data collection: nothing is sent or saved anywhere, it all stays in your browser and disappears when you close the page. See the methodology for details.
RIA DigiDoc — phone · Smart-ID / Mobile-ID
Send this letter directly to the company first — before contacting the regulator it has the right to respond (GDPR Art. 12(3) — 30 days).
Тема: Запрос доступа к персональным данным (ст. 15 GDPR) — labocca.ee

Кому: [укажите адрес компании — DPO / поддержка / юридический отдел]
От: [Ваше имя], [контактный email]

Прошу предоставить доступ к моим персональным данным, обрабатываемым в связи с использованием сайта labocca.ee.

1. Категории данных и цели обработки (ст. 15(1)(a)-(c))
На основании независимого технического анализа сайта прошу подтвердить и подробно раскрыть следующие категории обработки:

1) Баннер согласия на сайте есть (виден на снимках экрана, на странице политики), но в записи он не блокирует теги, а его категории включены по умолчанию. Google Tag Manager (GTM-5ZLM5QFT) грузится на +1277 мс, Facebook Pixel (fbevents.js) на +1278 мс, а на +2523…+2766 мс разом уходят: конверсия Google Ads (www.google.com/ccm/collect), DoubleClick (ad.doubleclick.net/ccm/s/collect), page_view Google Analytics 4 (G-5ZNJL5JS4M), связка DoubleClick (stats.g.doubleclick.net), ремаркетинг-аудитории (www.google.ee/ads/ga-audiences) и событие Facebook PageView. Всё это происходит немедленно при загрузке, до какого-либо выбора пользователя. Отдельной платформы управления согласием (Cookiebot, CookieYes, Funding Choices и подобных) в записи нет: ни одного обращения к CMP, ни сигнала Consent Mode.

2) В окне настройки cookie на снимках экрана все категории — «Analytics Cookies», Google Maps, Google Analytics, Google Tag Manager, Facebook, TikTok Pixel, Adyen — включены по умолчанию (переключатели в положении «включено»). Предварительно проставленное согласие недействительно: согласие должно быть активным действием, а не заранее выставленным флажком. Это согласуется с фактическим поведением: аналитические и рекламные теги срабатывают до какого-либо взаимодействия с баннером.

3) Политика заявляет, что Google и партнёры обрабатывают данные «на основании вашего согласия» и что согласием можно управлять через настройки cookie. Фактически обработка начинается до согласия и при предвыбранных категориях. Кроме того, Facebook Pixel в политике описан как собирающий «анонимную» информацию, используемую только для маркетинга и аналитики и не передаваемую третьим лицам; фактически пиксель (идентификатор 1181274603647499) отправляет событие конверсии Schedule помимо PageView, что не является анонимным подсчётом. Описание TikTok Pixel в политике оставлено незаполненным шаблоном («Tiktok Pixel kirjeldus»).

4) Политика называет получателей (Google Analytics, Google Tag Manager, Google Maps, Facebook Pixel, TikTok Pixel, Adyen), но не раскрывает поимённо связку ремаркетинга Google Ads / DoubleClick (ga-audiences, ccm/collect), фактически работающую в записи. Передача в Google, Facebook и (по политике) в США описана в общем виде; правовое основание трансграничной передачи в отношении рекламного ремаркетинга и Facebook Pixel не детализировано.


2. Получатели, сроки хранения и передача за пределы ЕЭЗ (ст. 15(1)(c)-(d), 46)
Прошу также указать полный список третьих лиц-получателей, применимые сроки хранения по каждой категории и правовые основания передачи данных за пределы ЕЭЗ, если таковая происходит. Полный технический разбор с доказательствами (сохранённый сетевой журнал, контрольная сумма SHA-256) опубликован по адресу: https://gdpru.eu/en/audits/ee-labocca-ee/

3. Автоматизированная обработка и профилирование (ст. 15(1)(h))
Прошу сообщить, применяется ли в отношении меня автоматизированное принятие решений или профилирование, и если да — раскрыть логику такой обработки.

С уважением,

[Ваше имя]
[контактный email]
[Страна]


[Дата]
Subject: Data access request (GDPR Art. 15) — labocca.ee

To: [insert the company's address — DPO / support / legal department]
From: [Your name], [contact email]

I request access to my personal data processed in connection with the website labocca.ee.

1. Categories of data and purposes of processing (Art. 15(1)(a)-(c))
Based on an independent technical analysis of the site, I request confirmation and detailed disclosure of the following categories of processing:

1) A consent banner exists on the site (visible in the screenshots, on the policy page), but in the recording it does not block tags, and its categories are on by default. Google Tag Manager (GTM-5ZLM5QFT) loads at +1277 ms, the Facebook Pixel (fbevents.js) at +1278 ms, and at +2523…+2766 ms the following go out at once: a Google Ads conversion (www.google.com/ccm/collect), DoubleClick (ad.doubleclick.net/ccm/s/collect), a Google Analytics 4 page_view (G-5ZNJL5JS4M), the DoubleClick link (stats.g.doubleclick.net), remarketing audiences (www.google.ee/ads/ga-audiences) and a Facebook PageView event. All of this happens immediately on load, before any user choice. There is no dedicated consent-management platform (Cookiebot, CookieYes, Funding Choices and the like) in the recording: not a single request to a CMP, no Consent Mode signal.

2) In the cookie-settings window in the screenshots, all categories — 'Analytics Cookies', Google Maps, Google Analytics, Google Tag Manager, Facebook, TikTok Pixel, Adyen — are on by default (the toggles are in the 'on' position). Pre-ticked consent is invalid: consent must be an affirmative action, not a pre-set box. This is consistent with the actual behaviour: the analytics and advertising tags fire before any interaction with the banner.

3) The policy states that Google and its partners process data 'on the basis of your consent' and that consent can be managed through the cookie settings. In fact processing begins before consent and with the categories pre-ticked. In addition, the Facebook Pixel is described in the policy as collecting 'anonymous' information used only for marketing and analytics and not shared with third parties; in fact the pixel (identifier 1181274603647499) sends a Schedule conversion event in addition to PageView, which is not an anonymous count. The TikTok Pixel description in the policy is left as an unfilled template ('Tiktok Pixel kirjeldus').

4) The policy names recipients (Google Analytics, Google Tag Manager, Google Maps, Facebook Pixel, TikTok Pixel, Adyen) but does not disclose by name the Google Ads / DoubleClick remarketing chain (ga-audiences, ccm/collect) that actually operates in the recording. Transfer to Google, Facebook and (per the policy) the US is described in general terms; the legal basis for the cross-border transfer as regards advertising remarketing and the Facebook Pixel is not detailed.


2. Recipients, retention periods, and transfers outside the EEA (Art. 15(1)(c)-(d), 46)
I also request the full list of third-party recipients, the applicable retention period for each category, and the legal basis for any transfer of data outside the EEA. The full technical audit with evidence (saved network log, SHA-256 checksum) is published at: https://gdpru.eu/en/audits/ee-labocca-ee/

3. Automated processing and profiling (Art. 15(1)(h))
Please state whether I am subject to automated decision-making or profiling, and if so, disclose the logic involved.

Sincerely,

[Your name]
[contact email]
[Country]


[Date]
Teema: Isikuandmetele juurdepääsu taotlus (IKÜM art 15) — labocca.ee Kellele: [märkige ettevõtte aadress — DPO / tugi / juriidiline osakond] Kellelt: [Teie nimi], [kontakt-e-post] Palun anda mulle juurdepääs minu isikuandmetele, mida töödeldakse seoses veebisaidi labocca.ee kasutamisega. 1. Andmekategooriad ja töötlemise eesmärgid (IKÜM art 15(1)(a)-(c)) Sõltumatu tehnilise analüüsi põhjal palun kinnitada ja üksikasjalikult avaldada järgmised töötlemiskategooriad: 1) Saidil olev nõusoleku bänner on olemas (näidatud ekraanipiltides, poliitika lehel), kuid kirjes ei blokeeri see silte ja selle kategooriad on vaikimisi kaasatud. Google Tag Manager (GTM-5ZLM5QFT) laadib +1277 ms, Facebook Pixel (fbevents.js) +1278 ms ja +2523. +2766 ms on läinud: Google Adsi teisendamine (www.google.com/ccm/collect), DoubleClick (ad.doubleclick.net/ccm/s/collect), Google Analytics 4 lehevaade (G-5ZNJL5JS4M), DoubleClicki pakett (stats.g. doubleclick.net), uuesti turundamise vaatajaskond (www.google.ee/ads/ga-audiences) ja Facebook PageView sündmus. Kõik see toimub kohe pärast allalaadimist, enne kasutaja valikut. Puudub eraldi nõusoleku haldamise platvorm (Cookiebot, CookieYes, Funding Choices jne) kirjes: puudub CMP juurdepääs, puudub nõusoleku režiimi signaal. 2) Ekraanipiltide küpsiseseadete aknas on vaikimisi lubatud kõik kategooriad – «Analytics Cookies», Google Maps, Google Analytics, Google Tag Manager, Facebook, TikTok Pixel, Adyen – (lülitid asendis „on). Eelnev nõusolek on kehtetu: nõusolek peab olema aktiivne tegevus, mitte eelkontroll. See on kooskõlas tegeliku käitumisega: analüütilised ja reklaamisildid käivituvad enne mis tahes interaktsiooni bänneriga. 3) Poliitika sätestab, et Google ja tema partnerid töötlevad andmeid „teie nõusoleku alusel ja et nõusolekut saab hallata küpsiste seadete kaudu. Tegelikult algab töötlemine enne nõusoleku andmist ja valitud kategooriates. Lisaks kirjeldatakse poliitikas Facebook Pixelit kui anonüümse teabe kogumist, mida kasutatakse ainult turunduse ja analüüsi jaoks ning mida ei jagata kolmandate osapooltega; tegelikult saadab piksel (identifikaator 1181274603647499) ajakava teisendamise sündmuse, mis ei ole PageView, mis ei ole anonüümne arv. TikToki Pixeli kirjeldus poliitikas on jäetud tühjaks malliks («Tiktok Pixel kirjeldus»). 4) Poliitika nimetab saajaid (Google Analytics, Google Tag Manager, Google Maps, Facebook Pixel, TikTok Pixel, Adyen), kuid ei avalda nimeliselt Google Ads/DoubleClicki uuesti turundamise paketti (ga-audiences, ccm/collect), mis tegelikult rekordis töötab. Edastamist Google'ile, Facebookile ja (poliitika) USA-le kirjeldatakse üldiselt; reklaami taasturundamise ja Facebooki Pixeliga seotud piiriüleste ülekannete õiguslik alus ei ole üksikasjalik. 2. Vastuvõtjad, säilitustähtajad ja edastamine väljapoole EMP-d (IKÜM art 15(1)(c)-(d), 46) Palun samuti esitada täielik loetelu kolmandatest isikutest vastuvõtjatest, iga kategooria puhul kohaldatavad säilitustähtajad ning andmete EMP-välisele edastamisele kohaldatav õiguslik alus, kui selline edastamine toimub. Täielik tehniline analüüs koos tõenditega (salvestatud võrgulogi, SHA-256 kontrollsumma) on avaldatud aadressil: https://gdpru.eu/en/audits/ee-labocca-ee/ 3. Automatiseeritud töötlemine ja profiilianalüüs (IKÜM art 15(1)(h)) Palun teatada, kas minu suhtes kohaldatakse automatiseeritud otsuste tegemist või profiilianalüüsi, ning kui jah, siis avaldada selle loogika. Lugupidamisega, [Teie nimi] [kontakt-e-post] [Riik] [Kuupäev]
RIA DigiDoc — phone · Smart-ID / Mobile-ID
Where to file: Estonian Data Protection Inspectorate (AKI) — write to info@aki.ee
Important: AKI only handles submissions in Estonian. Translate the letter before sending.
The regulator reviews complaints in its national language. There is an officially translated template from the European Data Protection Board (EDPB) — you can use it instead of or alongside this letter: Official EDPB complaint form (PDF, your language)
Тема: Жалоба на обработку персональных данных — labocca.ee

1. Предмет жалобы
Я подаю жалобу в отношении обработки моих персональных данных сайтом labocca.ee.

2. Обстоятельства
Я посетил сайт labocca.ee и обнаружил признаки несоответствия обработки моих персональных данных требованиям GDPR. Технический разбор, опубликованный на gdpru.eu 20.09.2026 (открытая методология, воспроизводимые измерения), документирует следующие признаки:

1) Баннер согласия на сайте есть (виден на снимках экрана, на странице политики), но в записи он не блокирует теги, а его категории включены по умолчанию. Google Tag Manager (GTM-5ZLM5QFT) грузится на +1277 мс, Facebook Pixel (fbevents.js) на +1278 мс, а на +2523…+2766 мс разом уходят: конверсия Google Ads (www.google.com/ccm/collect), DoubleClick (ad.doubleclick.net/ccm/s/collect), page_view Google Analytics 4 (G-5ZNJL5JS4M), связка DoubleClick (stats.g.doubleclick.net), ремаркетинг-аудитории (www.google.ee/ads/ga-audiences) и событие Facebook PageView. Всё это происходит немедленно при загрузке, до какого-либо выбора пользователя. Отдельной платформы управления согласием (Cookiebot, CookieYes, Funding Choices и подобных) в записи нет: ни одного обращения к CMP, ни сигнала Consent Mode.

2) В окне настройки cookie на снимках экрана все категории — «Analytics Cookies», Google Maps, Google Analytics, Google Tag Manager, Facebook, TikTok Pixel, Adyen — включены по умолчанию (переключатели в положении «включено»). Предварительно проставленное согласие недействительно: согласие должно быть активным действием, а не заранее выставленным флажком. Это согласуется с фактическим поведением: аналитические и рекламные теги срабатывают до какого-либо взаимодействия с баннером.

3) Политика заявляет, что Google и партнёры обрабатывают данные «на основании вашего согласия» и что согласием можно управлять через настройки cookie. Фактически обработка начинается до согласия и при предвыбранных категориях. Кроме того, Facebook Pixel в политике описан как собирающий «анонимную» информацию, используемую только для маркетинга и аналитики и не передаваемую третьим лицам; фактически пиксель (идентификатор 1181274603647499) отправляет событие конверсии Schedule помимо PageView, что не является анонимным подсчётом. Описание TikTok Pixel в политике оставлено незаполненным шаблоном («Tiktok Pixel kirjeldus»).

4) Политика называет получателей (Google Analytics, Google Tag Manager, Google Maps, Facebook Pixel, TikTok Pixel, Adyen), но не раскрывает поимённо связку ремаркетинга Google Ads / DoubleClick (ga-audiences, ccm/collect), фактически работающую в записи. Передача в Google, Facebook и (по политике) в США описана в общем виде; правовое основание трансграничной передачи в отношении рекламного ремаркетинга и Facebook Pixel не детализировано.

Полная техническая документация опубликована по адресу: https://gdpru.eu/en/audits/ee-labocca-ee/

3. Положения GDPR, соблюдение которых прошу проверить
ePrivacy — Директива 2002/58/EC, ст. 5(3) (в связке с GDPR Art. 6(1)(a)); GDPR Art. 4(11), Art. 7 — недействительное согласие (предвыбранные категории); GDPR Art. 5(1)(a) — прозрачность: заявленное расходится с фактическим; GDPR Art. 13(1)(e) / Art. 44 — раскрытие получателей и передача в третью страну

4. Требование
Прошу проверить изложенные обстоятельства и, если несоответствие подтвердится, принять меры, предусмотренные статьёй 58(2) GDPR.

5. Приложения
Полная доказательная база — HAR-файл, контрольная сумма SHA-256 и цитата из политики конфиденциальности сайта, документирующая указанное противоречие — опубликована и проверяема по ссылке в пункте 2 выше.

С уважением,

[Ваше имя]
[контактный email]
[Страна]


[Дата]
Subject: Complaint regarding personal data processing — labocca.ee

1. Subject of the complaint
I am filing a complaint regarding the processing of my personal data by the website labocca.ee.

2. Circumstances
I visited the website labocca.ee and found indications that the processing of my personal data does not comply with the GDPR. The technical analysis published on gdpru.eu on 20 September 2026 (open methodology, reproducible measurements) documents the following indications:

1) A consent banner exists on the site (visible in the screenshots, on the policy page), but in the recording it does not block tags, and its categories are on by default. Google Tag Manager (GTM-5ZLM5QFT) loads at +1277 ms, the Facebook Pixel (fbevents.js) at +1278 ms, and at +2523…+2766 ms the following go out at once: a Google Ads conversion (www.google.com/ccm/collect), DoubleClick (ad.doubleclick.net/ccm/s/collect), a Google Analytics 4 page_view (G-5ZNJL5JS4M), the DoubleClick link (stats.g.doubleclick.net), remarketing audiences (www.google.ee/ads/ga-audiences) and a Facebook PageView event. All of this happens immediately on load, before any user choice. There is no dedicated consent-management platform (Cookiebot, CookieYes, Funding Choices and the like) in the recording: not a single request to a CMP, no Consent Mode signal.

2) In the cookie-settings window in the screenshots, all categories — 'Analytics Cookies', Google Maps, Google Analytics, Google Tag Manager, Facebook, TikTok Pixel, Adyen — are on by default (the toggles are in the 'on' position). Pre-ticked consent is invalid: consent must be an affirmative action, not a pre-set box. This is consistent with the actual behaviour: the analytics and advertising tags fire before any interaction with the banner.

3) The policy states that Google and its partners process data 'on the basis of your consent' and that consent can be managed through the cookie settings. In fact processing begins before consent and with the categories pre-ticked. In addition, the Facebook Pixel is described in the policy as collecting 'anonymous' information used only for marketing and analytics and not shared with third parties; in fact the pixel (identifier 1181274603647499) sends a Schedule conversion event in addition to PageView, which is not an anonymous count. The TikTok Pixel description in the policy is left as an unfilled template ('Tiktok Pixel kirjeldus').

4) The policy names recipients (Google Analytics, Google Tag Manager, Google Maps, Facebook Pixel, TikTok Pixel, Adyen) but does not disclose by name the Google Ads / DoubleClick remarketing chain (ga-audiences, ccm/collect) that actually operates in the recording. Transfer to Google, Facebook and (per the policy) the US is described in general terms; the legal basis for the cross-border transfer as regards advertising remarketing and the Facebook Pixel is not detailed.

Full technical documentation is published at: https://gdpru.eu/en/audits/ee-labocca-ee/

3. GDPR provisions I ask you to examine
ePrivacy — Directive 2002/58/EC, Art. 5(3) (in conjunction with GDPR Art. 6(1)(a)); GDPR Art. 4(11), Art. 7 — invalid consent (pre-ticked categories); GDPR Art. 5(1)(a) — transparency: the declared diverges from the actual; GDPR Art. 13(1)(e) / Art. 44 — disclosure of recipients and transfer to a third country

4. Request
I request that you examine the circumstances described and, if non-compliance is confirmed, apply the measures provided for in Article 58(2) GDPR.

5. Attachments
The full evidence base — the HAR file, its SHA-256 checksum and the quotation from the site's privacy policy documenting the stated contradiction — is published and verifiable at the link in point 2 above.

Sincerely,

[Your name]
[contact email]
[Country]


[Date]
1. Kaebuse ese Esitan kaebuse seoses minu isikuandmete töötlemisega veebisaidil labocca.ee. 2. Asjaolud Külastasin veebisaiti labocca.ee ja tuvastasin märke sellest, et minu isikuandmete töötlemine ei vasta isikuandmete kaitse üldmääruse (IKÜM) nõuetele. Tehniline analüüs, mis on avaldatud aadressil gdpru.eu 20.09.2026 (avatud metoodika, korratavad mõõtmised), dokumenteerib järgmist: 1) Saidil olev nõusoleku bänner on olemas (näidatud ekraanipiltides, poliitika lehel), kuid kirjes ei blokeeri see silte ja selle kategooriad on vaikimisi kaasatud. Google Tag Manager (GTM-5ZLM5QFT) laadib +1277 ms, Facebook Pixel (fbevents.js) +1278 ms ja +2523. +2766 ms on läinud: Google Adsi teisendamine (www.google.com/ccm/collect), DoubleClick (ad.doubleclick.net/ccm/s/collect), Google Analytics 4 lehevaade (G-5ZNJL5JS4M), DoubleClicki pakett (stats.g. doubleclick.net), uuesti turundamise vaatajaskond (www.google.ee/ads/ga-audiences) ja Facebook PageView sündmus. Kõik see toimub kohe pärast allalaadimist, enne kasutaja valikut. Puudub eraldi nõusoleku haldamise platvorm (Cookiebot, CookieYes, Funding Choices jne) kirjes: puudub CMP juurdepääs, puudub nõusoleku režiimi signaal. 2) Ekraanipiltide küpsiseseadete aknas on vaikimisi lubatud kõik kategooriad – «Analytics Cookies», Google Maps, Google Analytics, Google Tag Manager, Facebook, TikTok Pixel, Adyen – (lülitid asendis „on). Eelnev nõusolek on kehtetu: nõusolek peab olema aktiivne tegevus, mitte eelkontroll. See on kooskõlas tegeliku käitumisega: analüütilised ja reklaamisildid käivituvad enne mis tahes interaktsiooni bänneriga. 3) Poliitika sätestab, et Google ja tema partnerid töötlevad andmeid „teie nõusoleku alusel ja et nõusolekut saab hallata küpsiste seadete kaudu. Tegelikult algab töötlemine enne nõusoleku andmist ja valitud kategooriates. Lisaks kirjeldatakse poliitikas Facebook Pixelit kui anonüümse teabe kogumist, mida kasutatakse ainult turunduse ja analüüsi jaoks ning mida ei jagata kolmandate osapooltega; tegelikult saadab piksel (identifikaator 1181274603647499) ajakava teisendamise sündmuse, mis ei ole PageView, mis ei ole anonüümne arv. TikToki Pixeli kirjeldus poliitikas on jäetud tühjaks malliks («Tiktok Pixel kirjeldus»). 4) Poliitika nimetab saajaid (Google Analytics, Google Tag Manager, Google Maps, Facebook Pixel, TikTok Pixel, Adyen), kuid ei avalda nimeliselt Google Ads/DoubleClicki uuesti turundamise paketti (ga-audiences, ccm/collect), mis tegelikult rekordis töötab. Edastamist Google'ile, Facebookile ja (poliitika) USA-le kirjeldatakse üldiselt; reklaami taasturundamise ja Facebooki Pixeliga seotud piiriüleste ülekannete õiguslik alus ei ole üksikasjalik. Täielik tehniline dokumentatsioon on avaldatud aadressil: https://gdpru.eu/en/audits/ee-labocca-ee/ 3. Sätted, mille järgimist palun kontrollida e-privaatsus – direktiiv 2002/58/EÜ, artikli 5 lõige 3 (koosmõjus GDPRi artikli 6 lõike 1 punktiga a); GDPR artikli 4 lõige 11, artikkel 7 – kehtetu nõusolek (eelvalitud kategooriad); GDPR art 5(1)(a) Läbipaistvus: väide on vastuolus tegeliku; GDPR artikli 13 lõike 1 punkt e / artikkel 44 Vastuvõtjate avalikustamine ja üleandmine kolmandale riigile 4. Nõue Palun kontrollida kirjeldatud asjaolusid ja mittevastavuse kinnitamisel kohaldada IKÜM artikli 58 lõikes 2 ette nähtud meetmeid. 5. Lisad Täielik tõendusmaterjal — HAR-fail, kontrollsumma SHA-256 ning veebisaidi privaatsuspoliitika tsitaat, mis dokumenteerib nimetatud vastuolu — on avaldatud ja kontrollitav punktis 2 viidatud lingil. Lugupidamisega, [Teie nimi] [kontakt-e-post] [Riik] [Kuupäev]