
kristiinekeskus.ee
Website of the Kristiine Keskus shopping centre in Tallinn — one recording, 10 navigations, 864 requests, sixteen nodes. The site has a Cookiebot consent-management platform, and in its banner the 'Statistics' and 'Marketing' categories are switched off by default — but it does not block tags: the Facebook Pixel sends a PageView event at +1364 ms, Plausible analytics an event at +730 ms, while consent is recorded only at +21470 ms. That is, the advertising pixel and the analytics transmit data roughly twenty seconds before consent is even recorded. The data-protection notice does not name the actual web recipients by name. The browser did not send a DNT header.
Request timeline
Declared versus actual
Transfer timings
GTM-N8F62LJ8; launches Facebook Pixel, Plausible and Cookiebot.
Facebook Pixel fbevents.js, identifier 773150295616793.
uc.js; the statistics and marketing categories in the banner are off by default.
/api/event — an analytics event before consent is recorded.
/tr — Facebook Pixel PageView event, before consent is recorded.
logconsent.ashx — recording of the decision, ~20 seconds after the first transmissions.
Detected trackers
- Facebook Pixel (773150295616793) via connect.facebook.net and www.facebook.com/tr — a PageView event, initiated by the GTM container; the first request goes out before consent is recorded
- Plausible Analytics (plausible.io) — visit analytics; the /api/event request goes out before consent is recorded
- Google Tag Manager (www.googletagmanager.com, container GTM-N8F62LJ8) — tag container; launches Facebook Pixel, Plausible and Cookiebot
- Cookiebot (consent.cookiebot.com, consentcdn.cookiebot.com, identifier f0ba0b50-945e-4ff0-add6-bb9fcebce0) — consent-management platform; does not block tags before consent
- Sentry (o227862.ingest.us.sentry.io) — application error monitoring, a technical service
- Hyperin (cdn.websites.hyperin.com, cdn-assets.hyperin.com, d19usf5dbescr.cloudfront.net) — shopping-centre website platform, delivery infrastructure
- Google Fonts (fonts.googleapis.com, fonts.gstatic.com) — the Figtree font; on loading, the visitor's IP address goes to Google
- Google reCAPTCHA (www.google.com/recaptcha, www.gstatic.com/recaptcha) — protection of the feedback form, a functional resource
Indicators of GDPR non-compliance
- ePrivacy — Directive 2002/58/EC, Art. 5(3) (in conjunction with GDPR Art. 6(1)(a))A consent-management platform is present on the site — Cookiebot, its uc.js script loads at +481 ms, and in the banner the 'Preferences', 'Statistics' and 'Marketing' categories are switched off by default. However, the platform does not block tags before consent: the Facebook Pixel (fbevents.js) loads at +469 ms and sends a PageView event at +1364 ms, and Plausible Analytics sends /api/event as early as +730 ms. The recording of the consent decision (Cookiebot logconsent.ashx) occurs only at +21470 ms — that is, both the advertising pixel and the analytics transmitted data roughly twenty seconds before consent was even recorded. The Facebook Pixel is initiated by the Google Tag Manager container, bypassing the consent platform's prior blocking.
- GDPR Art. 5(1)(a) — transparency: the declared diverges from the actualThe Cookiebot banner shows the 'Statistics' and 'Marketing' categories switched off by default, which means the corresponding cookies and tags should not be set or fire before consent. In fact Plausible analytics (the statistics category) and the Facebook Pixel (the marketing category) transmit data on page load, before any user choice and before consent is recorded. The site's behaviour contradicts the state shown by its own consent banner.
- GDPR Art. 13(1)(e) — disclosure of recipientsThe EfTEN Kristiine OÜ data-protection notice describes categories of recipients (service providers: servers, mail, marketing, analytics) and mentions social networks (Facebook, LinkedIn, Instagram) as a source of data, but does not name by name the actual recipients of web data: the Facebook Pixel (identifier 773150295616793), Plausible Analytics, Google Tag Manager and Sentry are not named as recipients in the document.
- GDPR Art. 44 — transfer to a third countryThe Facebook Pixel (773150295616793) sends events to www.facebook.com/tr, which entails the transmission of data to Meta Platforms and of the visitor's IP address outside the EEA; Sentry error monitoring is sent to a node in the US (o227862.ingest.us.sentry.io); fonts are loaded from Google servers. The data-protection notice describes cross-border transfer in general terms with a reference to an adequacy decision and standard contractual clauses, but as regards these specific recipients the legal basis is not disclosed.
Context
kristiinekeskus.ee is the website of the Kristiine Keskus shopping centre in Tallinn. The controller is EfTEN Kristiine OÜ (registration code 17116468), the operator of the shopping centre. The site is built on the Hyperin platform (dedicated shopping-centre websites), with an Astro front end and an nginx server.
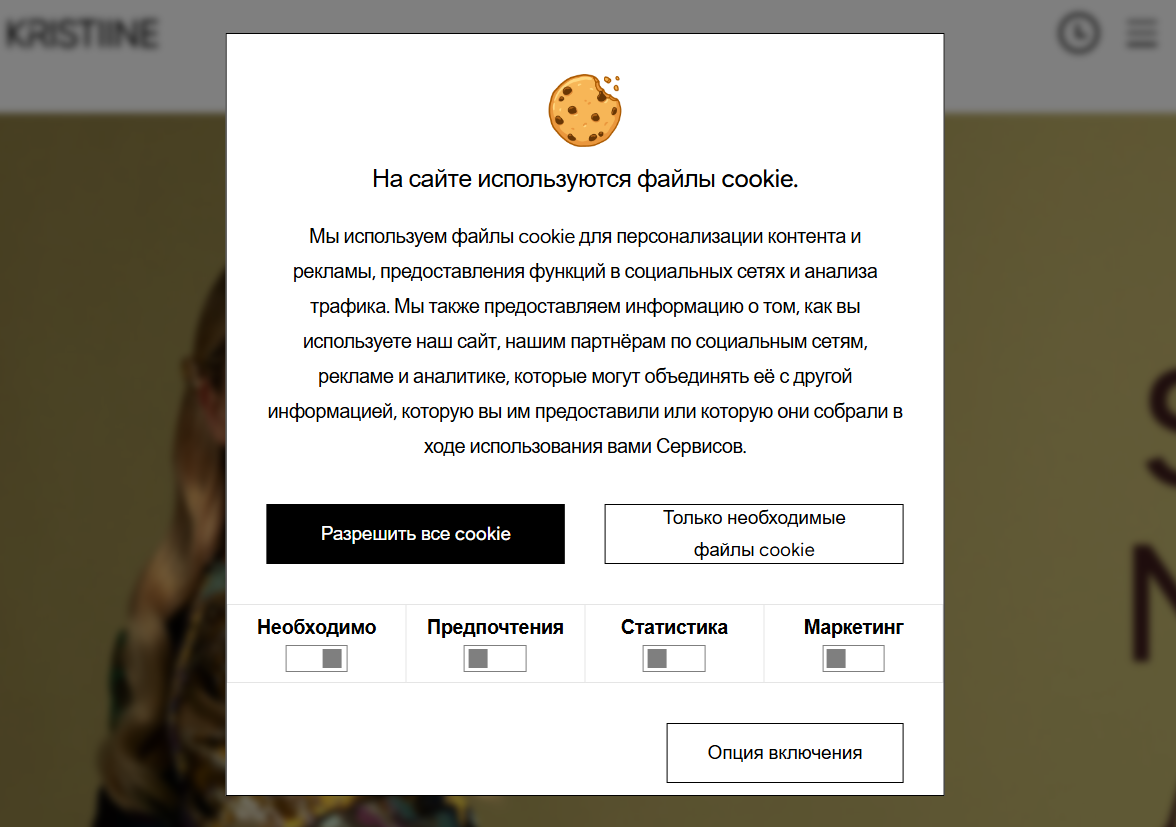
Processing is described by the attached data-protection notice (Privaatsustingimused), which includes sections on cookies and data processing. Two screenshots of the Cookiebot consent banner — in Estonian and Russian — are attached to the material.
The measurement consists of one recording, ten navigations: the home page and moves through sections and language versions. Eight hundred and sixty-four requests, sixteen nodes. The recording was made on 20 September 2026.
Who data goes to directly
Facebook (Pixel), Plausible, Google (Tag Manager, Fonts, reCAPTCHA), Sentry, Cookiebot (the consent platform), Hyperin (delivery infrastructure).
Declared versus actual
The EfTEN Kristiine OÜ data-protection notice is detailed and speaks plainly of the use of cookies, pixel tags, profiling and targeted marketing; cookie management is offered through a section at the bottom of the site backed by the Cookiebot platform. The document assigns marketing and statistics to processing on the basis of legitimate interest, and specific purposes to processing only with consent.
The measurement yields the key discrepancy — the consent platform is present but does not block tags.
The consent platform is present, the categories in the banner are off by default. The Cookiebot script (consent.cookiebot.com/uc.js) loads at +481 ms. In the attached screenshots the banner offers ‘Allow all cookies’ and ‘Only necessary cookies’, while the toggles for the ‘Preferences’, ‘Statistics’ and ‘Marketing’ categories are in the off position (the necessary ones are locked). That is, the interface declares that statistics and marketing are inactive before consent.
In fact the tags transmit data before consent. The Facebook Pixel (fbevents.js) loads at +469 ms and sends a PageView event (identifier 773150295616793) at +1364 ms. Plausible analytics (plausible.io) sends an /api/event event as early as +730 ms. Meanwhile the recording of the consent decision — the request consent.cookiebot.com/logconsent.ashx — occurs only at +21470 ms. That is, the advertising pixel and the analytics transmitted data roughly twenty seconds before consent was even recorded. The Facebook Pixel is initiated by the Google Tag Manager container (GTM-N8F62LJ8) rather than being placed under the consent platform’s prior blocking. The site’s behaviour contradicts the state shown by its own banner: the statistics and marketing categories are off in the interface, but the corresponding tags have already fired.
The Facebook PageView repeats on every navigation. Over the session the pixel’s event goes out again and again; some of the later transmissions fall in the period after consent is recorded, but the first firing precedes it.
Recipients are not named by name in the document. The notice lists categories of recipients (service providers: servers, mail, marketing, analytics tools) and mentions social networks (Facebook, LinkedIn, Instagram) as a source of data, but does not give the actual web recipients — Facebook Pixel, Plausible, Google Tag Manager, Sentry — by name.
Separately, on the functional and technical nodes: Sentry (o227862.ingest.us.sentry.io) is application error monitoring, sending an envelope to a node in the US; Hyperin (cdn.websites.hyperin.com, cdn-assets.hyperin.com, d19usf5dbescr.cloudfront.net) is the delivery platform for shopping-centre websites; Google Fonts (fonts.gstatic.com) is the Figtree font, whose loading makes the IP address visible to Google; Google reCAPTCHA (www.google.com/recaptcha) loads late, on the feedback form. The capture-tool artefact is edge.microsoft.com/translate (the browser’s built-in translator).
Consent: what is proven and what is not
Proven: the consent platform is present but does not block tags. The Cookiebot script loads at +481 ms; meanwhile the Facebook Pixel and Plausible load and transmit data (+469…+1364 ms) in parallel with it, not after consent.
Proven: the transmissions precede the recording of consent. The first Plausible event (+730 ms) and the first Facebook PageView event (+1364 ms) occur before the Cookiebot logconsent.ashx request (+21470 ms) that records consent. The order is legible from the timings and initiators of the recording.
Proven: in the banner, statistics and marketing are off by default. This is visible in both screenshots; nonetheless the corresponding tags fired.
Proven: the Facebook Pixel and Plausible are operating. By the pixel identifier 773150295616793 in the www.facebook.com/tr requests and by the plausible.io/api/event requests.
Not proven and not asserted: the exact user choice. What exactly was chosen in the banner is not unambiguously established by the recording and is immaterial to the conclusion: the pixel and the analytics transmitted data before any choice and before consent was recorded.
Separately: the browser did not send a DNT header in this recording.
Bounds of observation
The measurement covers ten pages of the site. Observation captures the browser’s behaviour, not the internal side of the services: server-side processing and contractual relationships with recipients are not verified by a browser measurement. The legal assessment is made by the competent authority — in Estonia, Andmekaitse Inspektsioon.
The file is published redacted under a “lean” profile: cookie values in requests have been removed, the Cookie and Set-Cookie headers stripped; the redaction registry records 1,023 redactions and a checksum. The composition of recipients, the identifiers, the timings and the order of requests are read from the parameters of the requests themselves and from the initiators. On the domain’s own responses no security headers are observed in the recording; full visitor-identifier values are not reproduced in the analysis.
The identification of services relies on domains and address patterns: the consent platform — by cookiebot.com and the identifier f0ba0b50-945e-4ff0-add6-bb9fcebce0; the tag container — by googletagmanager.com and GTM-N8F62LJ8; the Facebook Pixel — by connect.facebook.net, www.facebook.com/tr and the identifier 773150295616793; the analytics — by plausible.io; the error monitoring — by sentry.io; the fonts — by fonts.googleapis.com and fonts.gstatic.com; the delivery infrastructure — by hyperin.com and cloudfront.net.
Conclusion
The website of the Kristiine Keskus shopping centre has a Cookiebot consent-management platform, and in its banner the statistics and marketing categories are off by default — but the platform does not block tags before consent. The Facebook Pixel sends a PageView event at +1364 ms, Plausible analytics an event at +730 ms, while the consent decision is recorded only at +21470 ms: the advertising pixel and the analytics transmit data roughly twenty seconds before consent is even recorded, and the pixel is launched through the Google Tag Manager container, bypassing the prior blocking. The site’s behaviour contradicts the state shown by its own banner. The data-protection notice describes categories of recipients and mentions social networks as a source, but does not name the actual web recipients — Facebook Pixel, Plausible, Google Tag Manager, Sentry — by name; the transmission to Facebook and the sending of Sentry monitoring entail the transfer of data outside the EEA.
Remediation: place the Facebook Pixel, Plausible and the other statistics and marketing tags under the consent platform’s actual prior blocking, so that they neither load nor transmit data before explicit consent and in accordance with the state of the categories in the banner; ensure that launching through the Google Tag Manager container is also subject to the blocking; name the actual recipients of web data in the data-protection notice by name — Facebook Pixel, Plausible, Google Tag Manager, Sentry — with their purposes and the legal basis for cross-border transfer stated; set security headers on the domain.
How to verify: download the file and compute its checksum — sha256sum file.har (Linux, macOS) or certutil -hashfile file.har SHA256 (Windows); it must match the one shown. The conclusions apply to the scope of this measurement — see the limitations of the method.
e50cd936b7ad50ff6409621630cac4685bca3c98e748d83ff88bc3960c9bc060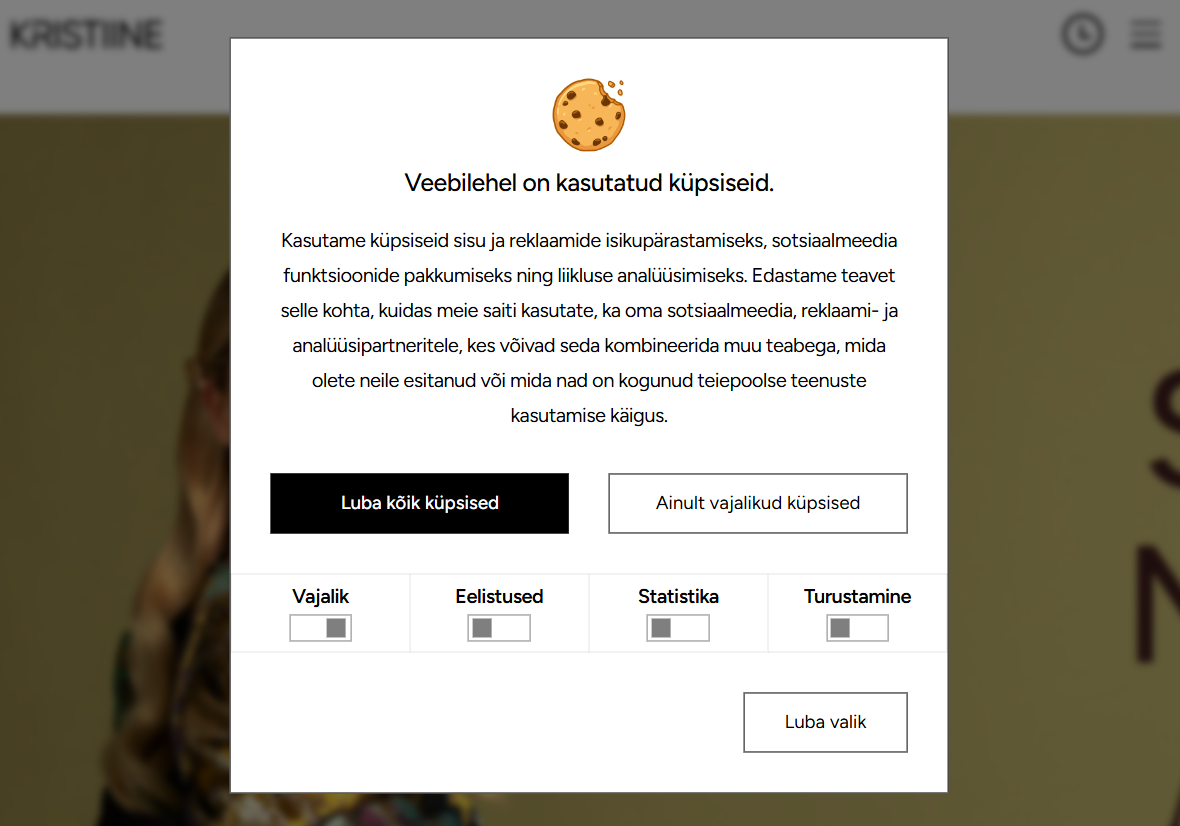
Want a response from the company about this audit? → Open the tool
Fill in once — it will be inserted into every letter below:
All fields are required to print the document — this is a formal requirement of the letter itself (the particulars of an official submission), not data collection: nothing is sent or saved anywhere, it all stays in your browser and disappears when you close the page. See the methodology for details.
RIA DigiDoc — phone · Smart-ID / Mobile-ID
Send this letter directly to the company first — before contacting the regulator it has the right to respond (GDPR Art. 12(3) — 30 days).
Тема: Запрос доступа к персональным данным (ст. 15 GDPR) — kristiinekeskus.ee

Кому: [укажите адрес компании — DPO / поддержка / юридический отдел]
От: [Ваше имя], [контактный email]

Прошу предоставить доступ к моим персональным данным, обрабатываемым в связи с использованием сайта kristiinekeskus.ee.

1. Категории данных и цели обработки (ст. 15(1)(a)-(c))
На основании независимого технического анализа сайта прошу подтвердить и подробно раскрыть следующие категории обработки:

1) Платформа управления согласием на сайте есть — Cookiebot, её скрипт uc.js грузится на +481 мс, а в баннере категории «Предпочтения», «Статистика» и «Маркетинг» по умолчанию выключены. Однако платформа не блокирует теги до согласия: Facebook Pixel (fbevents.js) грузится на +469 мс и отправляет событие PageView на +1364 мс, а Plausible Analytics отправляет /api/event уже на +730 мс. Фиксация решения согласия (Cookiebot logconsent.ashx) происходит только на +21470 мс — то есть и рекламный пиксель, и аналитика передали данные примерно за двадцать секунд до того, как согласие вообще было зафиксировано. Facebook Pixel инициируется контейнером Google Tag Manager, минуя предварительную блокировку платформы согласия.

2) Баннер Cookiebot показывает категории «Статистика» и «Маркетинг» выключенными по умолчанию, что означает: соответствующие cookie и теги не должны устанавливаться и срабатывать до согласия. Фактически аналитика Plausible (категория статистики) и Facebook Pixel (категория маркетинга) передают данные при загрузке страницы, до какого-либо выбора пользователя и до фиксации согласия. Поведение сайта противоречит состоянию, которое показывает его собственный баннер согласия.

3) Уведомление о защите данных EfTEN Kristiine OÜ описывает категории получателей (поставщики услуг: серверы, почта, маркетинг, аналитика) и упоминает социальные сети (Facebook, LinkedIn, Instagram) как источник данных, но не называет поимённо фактических получателей веб-данных: Facebook Pixel (идентификатор 773150295616793), Plausible Analytics, Google Tag Manager и Sentry как получатели в документе не названы.

4) Facebook Pixel (773150295616793) отправляет события на www.facebook.com/tr, что влечёт передачу данных Meta Platforms и адреса IP посетителя за пределы ЕЭЗ; мониторинг ошибок Sentry отправляется на узел в США (o227862.ingest.us.sentry.io); шрифты подгружаются с серверов Google. Уведомление о защите данных описывает трансграничную передачу в общем виде со ссылкой на решение о достаточности защиты и типовые договорные условия, но применительно к этим конкретным получателям правовое основание не раскрыто.


2. Получатели, сроки хранения и передача за пределы ЕЭЗ (ст. 15(1)(c)-(d), 46)
Прошу также указать полный список третьих лиц-получателей, применимые сроки хранения по каждой категории и правовые основания передачи данных за пределы ЕЭЗ, если таковая происходит. Полный технический разбор с доказательствами (сохранённый сетевой журнал, контрольная сумма SHA-256) опубликован по адресу: https://gdpru.eu/en/audits/ee-kristiinekeskus-ee/

3. Автоматизированная обработка и профилирование (ст. 15(1)(h))
Прошу сообщить, применяется ли в отношении меня автоматизированное принятие решений или профилирование, и если да — раскрыть логику такой обработки.

С уважением,

[Ваше имя]
[контактный email]
[Страна]


[Дата]
Subject: Data access request (GDPR Art. 15) — kristiinekeskus.ee

To: [insert the company's address — DPO / support / legal department]
From: [Your name], [contact email]

I request access to my personal data processed in connection with the website kristiinekeskus.ee.

1. Categories of data and purposes of processing (Art. 15(1)(a)-(c))
Based on an independent technical analysis of the site, I request confirmation and detailed disclosure of the following categories of processing:

1) A consent-management platform is present on the site — Cookiebot, its uc.js script loads at +481 ms, and in the banner the 'Preferences', 'Statistics' and 'Marketing' categories are switched off by default. However, the platform does not block tags before consent: the Facebook Pixel (fbevents.js) loads at +469 ms and sends a PageView event at +1364 ms, and Plausible Analytics sends /api/event as early as +730 ms. The recording of the consent decision (Cookiebot logconsent.ashx) occurs only at +21470 ms — that is, both the advertising pixel and the analytics transmitted data roughly twenty seconds before consent was even recorded. The Facebook Pixel is initiated by the Google Tag Manager container, bypassing the consent platform's prior blocking.

2) The Cookiebot banner shows the 'Statistics' and 'Marketing' categories switched off by default, which means the corresponding cookies and tags should not be set or fire before consent. In fact Plausible analytics (the statistics category) and the Facebook Pixel (the marketing category) transmit data on page load, before any user choice and before consent is recorded. The site's behaviour contradicts the state shown by its own consent banner.

3) The EfTEN Kristiine OÜ data-protection notice describes categories of recipients (service providers: servers, mail, marketing, analytics) and mentions social networks (Facebook, LinkedIn, Instagram) as a source of data, but does not name by name the actual recipients of web data: the Facebook Pixel (identifier 773150295616793), Plausible Analytics, Google Tag Manager and Sentry are not named as recipients in the document.

4) The Facebook Pixel (773150295616793) sends events to www.facebook.com/tr, which entails the transmission of data to Meta Platforms and of the visitor's IP address outside the EEA; Sentry error monitoring is sent to a node in the US (o227862.ingest.us.sentry.io); fonts are loaded from Google servers. The data-protection notice describes cross-border transfer in general terms with a reference to an adequacy decision and standard contractual clauses, but as regards these specific recipients the legal basis is not disclosed.


2. Recipients, retention periods, and transfers outside the EEA (Art. 15(1)(c)-(d), 46)
I also request the full list of third-party recipients, the applicable retention period for each category, and the legal basis for any transfer of data outside the EEA. The full technical audit with evidence (saved network log, SHA-256 checksum) is published at: https://gdpru.eu/en/audits/ee-kristiinekeskus-ee/

3. Automated processing and profiling (Art. 15(1)(h))
Please state whether I am subject to automated decision-making or profiling, and if so, disclose the logic involved.

Sincerely,

[Your name]
[contact email]
[Country]


[Date]
Teema: Isikuandmetele juurdepääsu taotlus (IKÜM art 15) — kristiinekeskus.ee

Kellele: [märkige ettevõtte aadress — DPO / tugi / juriidiline osakond]
Kellelt: [Teie nimi], [kontakt-e-post]

Palun anda mulle juurdepääs minu isikuandmetele, mida töödeldakse seoses veebisaidi kristiinekeskus.ee kasutamisega.

1. Andmekategooriad ja töötlemise eesmärgid (IKÜM art 15(1)(a)-(c))
Sõltumatu tehnilise analüüsi põhjal palun kinnitada ja üksikasjalikult avaldada järgmised töötlemiskategooriad:

1) Nõusoleku haldamise platvorm saidil on - Cookiebot, selle skript uc.js on laaditud +481 ms-le ja bännerikategoorias "Preferences", "Statistika" ja "Marketing" on vaikimisi välja lülitatud. Kuid platvorm ei blokeeri silte enne nõusoleku andmist: Facebook Pixel (fbevents.js) laadib +469 ms-le ja saadab PageView sündmuse +1364 ms-le ning Usutav Analytics saadab /api/sündmuse juba +730 ms-le. Nõusoleku otsuse (Cookiebot logconsent.ashx) fikseerimine toimub ainult +21470 ms - see tähendab, et nii reklaamipiksel kui ka analüütika edastasid andmed umbes kakskümmend sekundit enne nõusoleku üldse salvestamist. Facebook Pixeli käivitab Google Tag Manageri konteiner, mis möödub nõusoleku platvormist enne blokeerimist.

2) Küpsiseroboti bänneril on vaikimisi välja lülitatud kategooriad „Statistika” ja „Turundus”, mis tähendab, et vastavaid küpsiseid ja silte ei tohiks enne nõusoleku andmist seadistada ega käivitada. Tegelikult edastavad usutav analüütika (statistika kategooria) ja Facebook Pixel (turunduskategooria) andmeid, kui leht laadib, enne kasutaja valikut ja enne nõusoleku kinnitamist. Saidi käitumine on vastuolus riigiga, mida näitab tema enda nõusoleku bänner.

3) EfTENi andmekaitseteatis Kristiine OÜ kirjeldab vastuvõtjate kategooriaid (teenusepakkujad: serverid, post, turundus, analüütika) ning mainib andmeallikana suhtlusvõrgustikke (Facebook, LinkedIn, Instagram), kuid ei nimeta veebiandmete tegelikke saajaid: Facebook Pixel (identifikaator 773150295616793), Usutav Analytics, Google Tag Manager ja Sentry dokumendi saajatena ei nimeta.

4) Facebook Pixel (773150295616793) saadab sündmused www.facebook.com/tr-le, mis hõlmab Meta platvormide andmete ja külastajate IP-aadresside edastamist väljaspool EMP-d; Sentry vigade jälgimine saadetakse Ameerika Ühendriikide hostile (o227862.ingest.us.sentry.io); fonte laaditakse alla Google'i serveritest. Andmekaitseteatises kirjeldatakse piiriülest edastamist üldiselt, viidates kaitse piisavuse otsusele ja lepingu tüüptingimustele, kuid nende konkreetsete vastuvõtjate õiguslikku alust ei avalikustata.


2. Vastuvõtjad, säilitustähtajad ja edastamine väljapoole EMP-d (IKÜM art 15(1)(c)-(d), 46)
Palun samuti esitada täielik loetelu kolmandatest isikutest vastuvõtjatest, iga kategooria puhul kohaldatavad säilitustähtajad ning andmete EMP-välisele edastamisele kohaldatav õiguslik alus, kui selline edastamine toimub. Täielik tehniline analüüs koos tõenditega (salvestatud võrgulogi, SHA-256 kontrollsumma) on avaldatud aadressil: https://gdpru.eu/en/audits/ee-kristiinekeskus-ee/

3. Automatiseeritud töötlemine ja profiilianalüüs (IKÜM art 15(1)(h))
Palun teatada, kas minu suhtes kohaldatakse automatiseeritud otsuste tegemist või profiilianalüüsi, ning kui jah, siis avaldada selle loogika.

Lugupidamisega,

[Teie nimi]
[kontakt-e-post]
[Riik]


[Kuupäev]
RIA DigiDoc — phone · Smart-ID / Mobile-ID
Where to file: Estonian Data Protection Inspectorate (AKI) — write to info@aki.ee
Important: AKI only handles submissions in Estonian. Translate the letter before sending.
The regulator reviews complaints in its national language. There is an officially translated template from the European Data Protection Board (EDPB) — you can use it instead of or alongside this letter: Official EDPB complaint form (PDF, your language)
Тема: Жалоба на обработку персональных данных — kristiinekeskus.ee

1. Предмет жалобы
Я подаю жалобу в отношении обработки моих персональных данных сайтом kristiinekeskus.ee.

2. Обстоятельства
Я посетил сайт kristiinekeskus.ee и обнаружил признаки несоответствия обработки моих персональных данных требованиям GDPR. Технический разбор, опубликованный на gdpru.eu 20.09.2026 (открытая методология, воспроизводимые измерения), документирует следующие признаки:

1) Платформа управления согласием на сайте есть — Cookiebot, её скрипт uc.js грузится на +481 мс, а в баннере категории «Предпочтения», «Статистика» и «Маркетинг» по умолчанию выключены. Однако платформа не блокирует теги до согласия: Facebook Pixel (fbevents.js) грузится на +469 мс и отправляет событие PageView на +1364 мс, а Plausible Analytics отправляет /api/event уже на +730 мс. Фиксация решения согласия (Cookiebot logconsent.ashx) происходит только на +21470 мс — то есть и рекламный пиксель, и аналитика передали данные примерно за двадцать секунд до того, как согласие вообще было зафиксировано. Facebook Pixel инициируется контейнером Google Tag Manager, минуя предварительную блокировку платформы согласия.

2) Баннер Cookiebot показывает категории «Статистика» и «Маркетинг» выключенными по умолчанию, что означает: соответствующие cookie и теги не должны устанавливаться и срабатывать до согласия. Фактически аналитика Plausible (категория статистики) и Facebook Pixel (категория маркетинга) передают данные при загрузке страницы, до какого-либо выбора пользователя и до фиксации согласия. Поведение сайта противоречит состоянию, которое показывает его собственный баннер согласия.

3) Уведомление о защите данных EfTEN Kristiine OÜ описывает категории получателей (поставщики услуг: серверы, почта, маркетинг, аналитика) и упоминает социальные сети (Facebook, LinkedIn, Instagram) как источник данных, но не называет поимённо фактических получателей веб-данных: Facebook Pixel (идентификатор 773150295616793), Plausible Analytics, Google Tag Manager и Sentry как получатели в документе не названы.

4) Facebook Pixel (773150295616793) отправляет события на www.facebook.com/tr, что влечёт передачу данных Meta Platforms и адреса IP посетителя за пределы ЕЭЗ; мониторинг ошибок Sentry отправляется на узел в США (o227862.ingest.us.sentry.io); шрифты подгружаются с серверов Google. Уведомление о защите данных описывает трансграничную передачу в общем виде со ссылкой на решение о достаточности защиты и типовые договорные условия, но применительно к этим конкретным получателям правовое основание не раскрыто.

Полная техническая документация опубликована по адресу: https://gdpru.eu/en/audits/ee-kristiinekeskus-ee/

3. Положения GDPR, соблюдение которых прошу проверить
ePrivacy — Директива 2002/58/EC, ст. 5(3) (в связке с GDPR Art. 6(1)(a)); GDPR Art. 5(1)(a) — прозрачность: заявленное расходится с фактическим; GDPR Art. 13(1)(e) — раскрытие получателей; GDPR Art. 44 — передача в третью страну

4. Требование
Прошу проверить изложенные обстоятельства и, если несоответствие подтвердится, принять меры, предусмотренные статьёй 58(2) GDPR.

5. Приложения
Полная доказательная база — HAR-файл, контрольная сумма SHA-256 и цитата из политики конфиденциальности сайта, документирующая указанное противоречие — опубликована и проверяема по ссылке в пункте 2 выше.

С уважением,

[Ваше имя]
[контактный email]
[Страна]


[Дата]
Subject: Complaint regarding personal data processing — kristiinekeskus.ee

1. Subject of the complaint
I am filing a complaint regarding the processing of my personal data by the website kristiinekeskus.ee.

2. Circumstances
I visited the website kristiinekeskus.ee and found indications that the processing of my personal data does not comply with the GDPR. The technical analysis published on gdpru.eu on 20 September 2026 (open methodology, reproducible measurements) documents the following indications:

1) A consent-management platform is present on the site — Cookiebot, its uc.js script loads at +481 ms, and in the banner the 'Preferences', 'Statistics' and 'Marketing' categories are switched off by default. However, the platform does not block tags before consent: the Facebook Pixel (fbevents.js) loads at +469 ms and sends a PageView event at +1364 ms, and Plausible Analytics sends /api/event as early as +730 ms. The recording of the consent decision (Cookiebot logconsent.ashx) occurs only at +21470 ms — that is, both the advertising pixel and the analytics transmitted data roughly twenty seconds before consent was even recorded. The Facebook Pixel is initiated by the Google Tag Manager container, bypassing the consent platform's prior blocking.

2) The Cookiebot banner shows the 'Statistics' and 'Marketing' categories switched off by default, which means the corresponding cookies and tags should not be set or fire before consent. In fact Plausible analytics (the statistics category) and the Facebook Pixel (the marketing category) transmit data on page load, before any user choice and before consent is recorded. The site's behaviour contradicts the state shown by its own consent banner.

3) The EfTEN Kristiine OÜ data-protection notice describes categories of recipients (service providers: servers, mail, marketing, analytics) and mentions social networks (Facebook, LinkedIn, Instagram) as a source of data, but does not name by name the actual recipients of web data: the Facebook Pixel (identifier 773150295616793), Plausible Analytics, Google Tag Manager and Sentry are not named as recipients in the document.

4) The Facebook Pixel (773150295616793) sends events to www.facebook.com/tr, which entails the transmission of data to Meta Platforms and of the visitor's IP address outside the EEA; Sentry error monitoring is sent to a node in the US (o227862.ingest.us.sentry.io); fonts are loaded from Google servers. The data-protection notice describes cross-border transfer in general terms with a reference to an adequacy decision and standard contractual clauses, but as regards these specific recipients the legal basis is not disclosed.

Full technical documentation is published at: https://gdpru.eu/en/audits/ee-kristiinekeskus-ee/

3. GDPR provisions I ask you to examine
ePrivacy — Directive 2002/58/EC, Art. 5(3) (in conjunction with GDPR Art. 6(1)(a)); GDPR Art. 5(1)(a) — transparency: the declared diverges from the actual; GDPR Art. 13(1)(e) — disclosure of recipients; GDPR Art. 44 — transfer to a third country

4. Request
I request that you examine the circumstances described and, if non-compliance is confirmed, apply the measures provided for in Article 58(2) GDPR.

5. Attachments
The full evidence base — the HAR file, its SHA-256 checksum and the quotation from the site's privacy policy documenting the stated contradiction — is published and verifiable at the link in point 2 above.

Sincerely,

[Your name]
[contact email]
[Country]


[Date]
1. Kaebuse ese
Esitan kaebuse seoses minu isikuandmete töötlemisega veebisaidil kristiinekeskus.ee.

2. Asjaolud
Külastasin veebisaiti kristiinekeskus.ee ja tuvastasin märke sellest, et minu isikuandmete töötlemine ei vasta isikuandmete kaitse üldmääruse (IKÜM) nõuetele. Tehniline analüüs, mis on avaldatud aadressil gdpru.eu 20.09.2026 (avatud metoodika, korratavad mõõtmised), dokumenteerib järgmist:

1) Nõusoleku haldamise platvorm saidil on - Cookiebot, selle skript uc.js on laaditud +481 ms-le ja bännerikategoorias "Preferences", "Statistika" ja "Marketing" on vaikimisi välja lülitatud. Kuid platvorm ei blokeeri silte enne nõusoleku andmist: Facebook Pixel (fbevents.js) laadib +469 ms-le ja saadab PageView sündmuse +1364 ms-le ning Usutav Analytics saadab /api/sündmuse juba +730 ms-le. Nõusoleku otsuse (Cookiebot logconsent.ashx) fikseerimine toimub ainult +21470 ms - see tähendab, et nii reklaamipiksel kui ka analüütika edastasid andmed umbes kakskümmend sekundit enne nõusoleku üldse salvestamist. Facebook Pixeli käivitab Google Tag Manageri konteiner, mis möödub nõusoleku platvormist enne blokeerimist.

2) Küpsiseroboti bänneril on vaikimisi välja lülitatud kategooriad „Statistika” ja „Turundus”, mis tähendab, et vastavaid küpsiseid ja silte ei tohiks enne nõusoleku andmist seadistada ega käivitada. Tegelikult edastavad usutav analüütika (statistika kategooria) ja Facebook Pixel (turunduskategooria) andmeid, kui leht laadib, enne kasutaja valikut ja enne nõusoleku kinnitamist. Saidi käitumine on vastuolus riigiga, mida näitab tema enda nõusoleku bänner.

3) EfTENi andmekaitseteatis Kristiine OÜ kirjeldab vastuvõtjate kategooriaid (teenusepakkujad: serverid, post, turundus, analüütika) ning mainib andmeallikana suhtlusvõrgustikke (Facebook, LinkedIn, Instagram), kuid ei nimeta veebiandmete tegelikke saajaid: Facebook Pixel (identifikaator 773150295616793), Usutav Analytics, Google Tag Manager ja Sentry dokumendi saajatena ei nimeta.

4) Facebook Pixel (773150295616793) saadab sündmused www.facebook.com/tr-le, mis hõlmab Meta platvormide andmete ja külastajate IP-aadresside edastamist väljaspool EMP-d; Sentry vigade jälgimine saadetakse Ameerika Ühendriikide hostile (o227862.ingest.us.sentry.io); fonte laaditakse alla Google'i serveritest. Andmekaitseteatises kirjeldatakse piiriülest edastamist üldiselt, viidates kaitse piisavuse otsusele ja lepingu tüüptingimustele, kuid nende konkreetsete vastuvõtjate õiguslikku alust ei avalikustata.

Täielik tehniline dokumentatsioon on avaldatud aadressil: https://gdpru.eu/en/audits/ee-kristiinekeskus-ee/

3. Sätted, mille järgimist palun kontrollida
e-privaatsus – direktiiv 2002/58/EÜ, artikli 5 lõige 3 (koosmõjus GDPRi artikli 6 lõike 1 punktiga a); GDPR art 5(1)(a) Läbipaistvus: väide on vastuolus tegeliku; GDPR – artikli 13 lõike 1 punkt e – vastuvõtjate avalikustamine; GDPR artikkel 44 – Andmete edastamine kolmandasse riiki

4. Nõue
Palun kontrollida kirjeldatud asjaolusid ja mittevastavuse kinnitamisel kohaldada IKÜM artikli 58 lõikes 2 ette nähtud meetmeid.

5. Lisad
Täielik tõendusmaterjal — HAR-fail, kontrollsumma SHA-256 ning veebisaidi privaatsuspoliitika tsitaat, mis dokumenteerib nimetatud vastuolu — on avaldatud ja kontrollitav punktis 2 viidatud lingil.

Lugupidamisega,

[Teie nimi]
[kontakt-e-post]
[Riik]


[Kuupäev]