
Website of the Artis cinema in Tallinn — one recording, eight pages, 324 requests. There is no consent mechanism: a notice 'by continuing to use the site you agree' with a single 'Agree' button. Within the first 2.7 seconds, without any choice, Google Analytics 4, Google Ads remarketing and the Facebook Pixel fire; Google's consent mode is not configured, and the client identifier is the same for the whole session. Sentry monitoring, in a build with a session-replay module, sends large packets to a node in the USA. The attached policy describes only the cinema club, is silent about the site, cookies and advertising, and promises that data is stored in the EU or the EEA. The browser did not send a DNT header.
Request timeline
Declared versus actual
Transfer timings
Sentry loader; a build with tracing and session-replay modules.
Facebook Pixel fbevents.js.
GA4 page_view G-H5X6LY021S, gcd not set, cid 1751470220.1790282709.
ads/ga-audiences — Google Ads advertising audiences.
/tr — PageView, pixel 474915813583881.
envelope, 41,346 bytes; then 24,251 and 25,933 bytes.
Detected trackers
- Google Analytics 4 (G-H5X6LY021S) via region1.analytics.google.com — page_view, scroll and form_start with a client identifier on every page, consent mode not configured
- Google Ads / DoubleClick (stats.g.doubleclick.net, www.google.ee/ads/ga-audiences) — the Google Ads link and remarketing audiences
- Google Tag (www.googletagmanager.com/gtag/js) — the Google tag
- Facebook Pixel (474915813583881) via connect.facebook.net and www.facebook.com/tr — a PageView event on every page
- Sentry (js.sentry-cdn.com, browser.sentry-cdn.com — build 7.120.4 with tracing and session-replay modules; o4506223313944576.ingest.us.sentry.io, project 4507498428891136) — error and performance monitoring, node in the USA
- Markus (images.markus.live, mcsazure.blob.core.windows.net, mcswebsites.blob.core.windows.net) — the APL Digital Solutions OÜ ticketing platform, images and materials
- kinoartis.ee — the cinema's former domain, redirects to www.kino.ee
Indicators of GDPR non-compliance
- ePrivacy — Directive 2002/58/EC, Art. 5(3) (in conjunction with GDPR Art. 6(1)(a))There is no consent mechanism on the site: a notice at the bottom of the page states that continued use of the site means consent to cookies and offers a single 'NÕUSTUN' button, with no refusal. Implied consent by continued browsing is not valid consent. From the markup, Sentry (+717 ms), the Google tag (+719 ms) and the Facebook Pixel (+886 ms) load; at +2541…+2661 ms the following go out: a page_view to Google Analytics 4 (G-H5X6LY021S), a request to the Google Ads link (stats.g.doubleclick.net), a remarketing-audiences request (www.google.ee/ads/ga-audiences) and a Facebook Pixel PageView event (474915813583881). Google's consent mode is not configured: in every request gcd=13l3l3l2l1l1 ('not set'), and the gcs parameter is absent.
- GDPR Art. 6(1), Art. 5(1)(b) — advertising tracking without a legal basisThe visitor is passed into Google Ads remarketing audiences, and the Facebook Pixel sends a PageView event with a browser identifier (fbp) on each of the nine page loads. All Google requests carry a single client identifier, 1751470220.1790282709, created 2.1 seconds after the start of the recording; besides page views and scrolls, a form_start event — the start of filling in a form on the schedule page — goes to Google. The attached policy declares no advertising purposes at all.
- GDPR Art. 5(1)(a), Art. 13(1)(e), (f), Art. 44 — transparency and transfer to a third countryThe attached Tallinnfilm OÜ policy describes only the processing of data of members of the Artišokk cinema club, names APL Digital Solutions OÜ (the Markus platform) and Grant Thornton Baltic OÜ as authorised processors, and states that personal data is stored within the EU or the EEA. It says nothing about cookies, web analytics or advertising; Google, Meta and Sentry are not named. In fact Facebook Pixel events go to Meta Platforms (USA), and Sentry sends packets of 24–41 KB to the ingest.us.sentry.io node in the USA.
Context
kino.ee is the website of the Artis cinema (Kino Artis) in Tallinn: listings, the schedule, ticket purchase, school cinema, events and advertising at the cinema. The former domain kinoartis.ee redirects to www.kino.ee. The site runs on the Markus ticketing platform of APL Digital Solutions OÜ. The operator of the Artišokk cinema club and the controller under the attached policy is Tallinnfilm OÜ; the contact is info@kino.ee.
The attached privacy policy is devoted solely to the processing of data of members of the Artišokk cinema club. The notice on the site refers to separate ‘cookie terms’, which are not in the material. Attached to the material are two screenshots: the home page with the cookie notice and a page about advertising at the cinema.
The measurement consists of one recording lasting about four minutes, eight navigations: the home page, the schedule, the Russian version of the schedule, the advertising page, school cinema and the account privacy terms. Three hundred and twenty-four requests. The recording was made on 24 September 2026.
Who data goes to directly
Google (Analytics 4, Ads — remarketing, the Google tag), Meta (Facebook Pixel), Sentry (a node in the USA), Markus / APL Digital Solutions (the ticketing platform).
Declared versus actual
The policy describes the data of cinema-club members — name, optional personal ID code, phone, email, date of birth, ticket purchases — names APL Digital Solutions OÜ and Grant Thornton Baltic OÜ as authorised processors, and states that personal data is stored in the EU or the EEA. It has no section on the site, cookies, web analytics or advertising. The notice on the site states that continued use of the site means consent to cookies.
The measurement shows the following.
There is no consent mechanism. The notice, as seen in the screenshot, offers a single ‘NÕUSTUN’ button and declares continued browsing itself to be consent. There is no reject button and no category choice, and no consent-management platform in the recording. Google’s consent mode is not configured: gcd=13l3l3l2l1l1, and the gcs parameter is absent.
Advertising and analytics start within 2.7 seconds. From the markup, Sentry (+717 ms), the Google tag (+719 ms) and the Facebook Pixel (+886 ms) load. At +2541 ms a page_view goes to Google Analytics 4 (G-H5X6LY021S), at +2545 ms a request to the Google Ads link, at +2547 ms a Google Ads remarketing-audiences request, and at +2661 ms a Facebook Pixel PageView event (474915813583881) with the browser identifier fbp.
One identifier for the whole session. All Google requests carry the client identifier 1751470220.1790282709, created at 20:45:09 UTC — 2.1 seconds after the start of the recording. On each of the eight pages page_view and scroll go out; on the schedule page also form_start, the start of filling in a form. The Facebook Pixel sends a PageView on every page load.
Sentry monitoring is in the USA. Sentry is connected in build 7.120.4 with tracing and session-replay modules and sends packets three times to o4506223313944576.ingest.us.sentry.io — 41,346, 24,251 and 25,933 bytes. The content of the packets is redacted in the published file.
The documents do not reflect this. Neither Google, nor Meta, nor Sentry is named in the policy; it describes neither advertising purposes nor web analytics; the statement that data is stored in the EU or the EEA diverges from the transmission of Meta events and Sentry packets to the USA. Images and listings material are served by the Markus platform (images.markus.live, mcsazure.blob.core.windows.net, mcswebsites.blob.core.windows.net), which is named in the policy as a processor.
Consent: what is proven and what is not
Proven: there is no consent mechanism. A notice with a single ‘Agree’ button and the formula of consent through continued browsing; not a single request to a consent platform.
Proven: Google’s consent mode is not configured. By the value gcd=13l3l3l2l1l1 and the absence of gcs in every request.
Proven: analytics, remarketing and the pixel fire without consent. By the requests to analytics.google.com, stats.g.doubleclick.net, google.ee/ads/ga-audiences and facebook.com/tr within the first 2.7 seconds and then on every page.
Proven: Sentry packets go to a node in the USA. By the address ingest.us.sentry.io.
Not proven and not asserted: whether a Sentry packet contains a session recording. The build includes a session-replay module, but the packet bodies are redacted; this file cannot distinguish a session recording from tracing data.
Separately: the browser did not send a DNT header in this recording.
Bounds of observation
The measurement covers eight pages of the site; no tickets were purchased and no account login was performed. Observation captures the browser’s behaviour, not the internal side of the services. The legal assessment is made by the competent authority — in Estonia, Andmekaitse Inspektsioon.
The attached policy relates to the Artišokk cinema club; the ‘cookie terms’ referred to by the notice are absent from the material, so the content of that document is not taken into account in this review.
The file is published redacted under a “lean” profile: cookie values in requests have been removed, the Cookie and Set-Cookie headers stripped; the redaction registry records 479 redactions and a checksum. The consent-mode parameters, identifiers and timings are read from the parameters of the requests themselves; the Sentry packet bodies are redacted, while their sizes are fully legible.
The identification of services relies on domains and address patterns: analytics — by analytics.google.com and property G-H5X6LY021S; Google Ads — by stats.g.doubleclick.net and google.ee/ads/ga-audiences; Facebook — by connect.facebook.net, facebook.com/tr and the pixel identifier; Sentry — by sentry-cdn.com and ingest.us.sentry.io; the platform — by markus.live and blob.core.windows.net. The gcd values are interpreted according to Google’s documentation on consent-mode parameters.
Conclusion
The Artis cinema’s website has no consent mechanism — only a notice ‘by continuing to use the site you agree’ with a single ‘Agree’ button — and within the first 2.7 seconds launches Google Analytics 4, Google Ads remarketing and the Facebook Pixel; Google’s consent mode is not configured, and all Google requests over the session are linked by one client identifier. Sentry monitoring, in a build with a session-replay module, sends large packets to a node in the USA. The attached policy describes only the Artišokk cinema club, does not cover the site, cookies or advertising, names neither Google, nor Meta, nor Sentry, and states that data is stored in the EU or the EEA.
Remediation: deploy a consent mechanism with an equal-weight reject button and prior blocking, so that Google Analytics, Google Ads, the Facebook Pixel and Sentry neither load nor transmit data before consent; connect Google’s consent mode; if Sentry session replay is used, place it under consent and enable masking; publish a policy for the site with a cookie section, a named list of recipients, purposes, legal bases and a description of the transfer to the USA, and bring the statement about data being stored in the EU or the EEA into line with the facts.
How to verify: download the file and compute its checksum — sha256sum file.har (Linux, macOS) or certutil -hashfile file.har SHA256 (Windows); it must match the one shown. The conclusions apply to the scope of this measurement — see the limitations of the method.
e0a9d87683f71c7884cfc5d42902acd33a354a042f1040f68f4d0b98454a13e5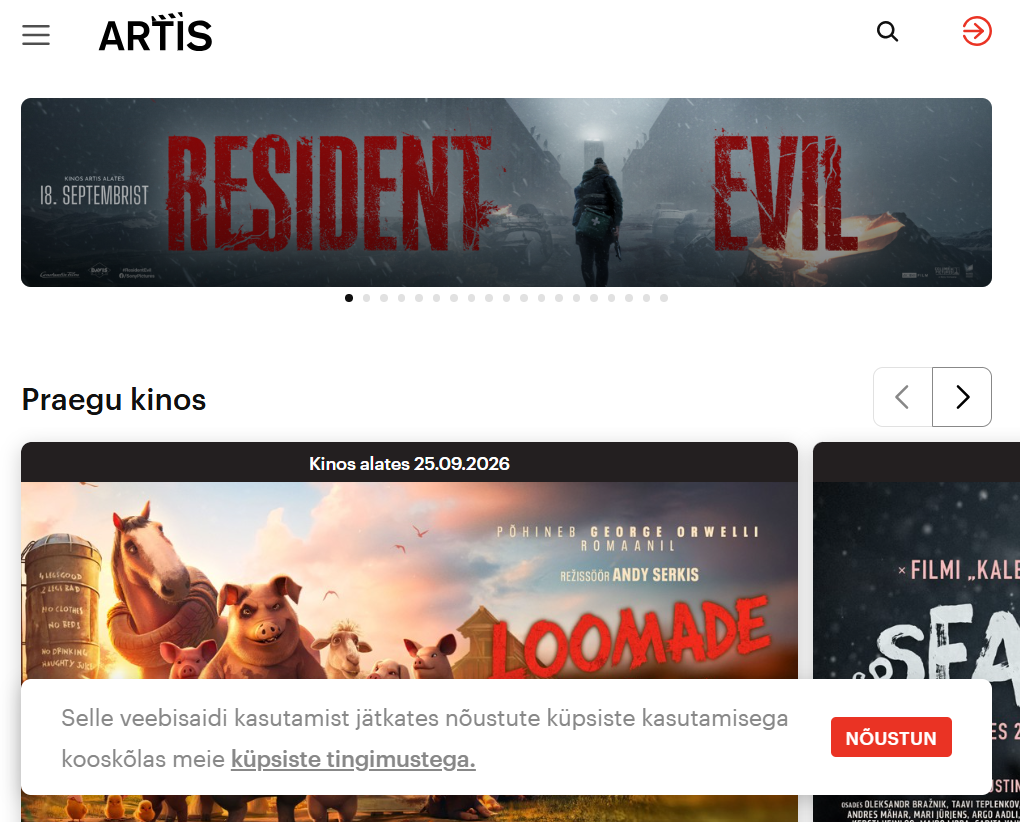
Want a response from the company about this audit? → Open the tool
Fill in once — it will be inserted into every letter below:
All fields are required to print the document — this is a formal requirement of the letter itself (the particulars of an official submission), not data collection: nothing is sent or saved anywhere, it all stays in your browser and disappears when you close the page. See the methodology for details.
RIA DigiDoc — phone · Smart-ID / Mobile-ID
Send this letter directly to the company first — before contacting the regulator it has the right to respond (GDPR Art. 12(3) — 30 days).
Тема: Запрос доступа к персональным данным (ст. 15 GDPR) — kino.ee

Кому: [укажите адрес компании — DPO / поддержка / юридический отдел]
От: [Ваше имя], [контактный email]

Прошу предоставить доступ к моим персональным данным, обрабатываемым в связи с использованием сайта kino.ee.

1. Категории данных и цели обработки (ст. 15(1)(a)-(c))
На основании независимого технического анализа сайта прошу подтвердить и подробно раскрыть следующие категории обработки:

1) Механизма согласия на сайте нет: плашка внизу страницы сообщает, что продолжение использования сайта означает согласие на cookie, и предлагает единственную кнопку «NÕUSTUN», без отказа. Подразумеваемое согласие через продолжение просмотра действительным согласием не является. Из разметки грузятся Sentry (+717 мс), тег Google (+719 мс) и Facebook Pixel (+886 мс); на +2541…+2661 мс уходят page_view в Google Analytics 4 (G-H5X6LY021S), обращение к связке Google Ads (stats.g.doubleclick.net), запрос ремаркетинг-аудиторий (www.google.ee/ads/ga-audiences) и событие PageView Facebook Pixel (474915813583881). Режим согласия Google не настроен: во всех обращениях gcd=13l3l3l2l1l1 («не задано»), параметр gcs отсутствует.

2) Посетитель передаётся в ремаркетинг-аудитории Google Ads, а Facebook Pixel отправляет событие PageView с идентификатором браузера (fbp) на каждой из девяти загрузок страниц. Все обращения Google несут единый идентификатор клиента 1751470220.1790282709, созданный через 2,1 секунды после начала записи; помимо просмотров и прокрутки в Google уходит событие form_start — начало заполнения формы на странице расписания. Приложенная политика рекламных целей не заявляет вовсе.

3) Приложенная политика Tallinnfilm OÜ описывает только обработку данных членов киноклуба Artišokk, называет уполномоченными обработчиками APL Digital Solutions OÜ (платформа Markus) и Grant Thornton Baltic OÜ и утверждает, что персональные данные хранятся на территории ЕС или ЕЭЗ. О cookie, веб-аналитике и рекламе в ней нет ни слова; Google, Meta и Sentry не названы. Фактически события Facebook Pixel уходят Meta Platforms (США), а Sentry отправляет пакеты по 24–41 КБ на узел ingest.us.sentry.io в США.


2. Получатели, сроки хранения и передача за пределы ЕЭЗ (ст. 15(1)(c)-(d), 46)
Прошу также указать полный список третьих лиц-получателей, применимые сроки хранения по каждой категории и правовые основания передачи данных за пределы ЕЭЗ, если таковая происходит. Полный технический разбор с доказательствами (сохранённый сетевой журнал, контрольная сумма SHA-256) опубликован по адресу: https://gdpru.eu/en/audits/ee-kino-ee/

3. Автоматизированная обработка и профилирование (ст. 15(1)(h))
Прошу сообщить, применяется ли в отношении меня автоматизированное принятие решений или профилирование, и если да — раскрыть логику такой обработки.

С уважением,

[Ваше имя]
[контактный email]
[Страна]


[Дата]
Subject: Data access request (GDPR Art. 15) — kino.ee

To: [insert the company's address — DPO / support / legal department]
From: [Your name], [contact email]

I request access to my personal data processed in connection with the website kino.ee.

1. Categories of data and purposes of processing (Art. 15(1)(a)-(c))
Based on an independent technical analysis of the site, I request confirmation and detailed disclosure of the following categories of processing:

1) There is no consent mechanism on the site: a notice at the bottom of the page states that continued use of the site means consent to cookies and offers a single 'NÕUSTUN' button, with no refusal. Implied consent by continued browsing is not valid consent. From the markup, Sentry (+717 ms), the Google tag (+719 ms) and the Facebook Pixel (+886 ms) load; at +2541…+2661 ms the following go out: a page_view to Google Analytics 4 (G-H5X6LY021S), a request to the Google Ads link (stats.g.doubleclick.net), a remarketing-audiences request (www.google.ee/ads/ga-audiences) and a Facebook Pixel PageView event (474915813583881). Google's consent mode is not configured: in every request gcd=13l3l3l2l1l1 ('not set'), and the gcs parameter is absent.

2) The visitor is passed into Google Ads remarketing audiences, and the Facebook Pixel sends a PageView event with a browser identifier (fbp) on each of the nine page loads. All Google requests carry a single client identifier, 1751470220.1790282709, created 2.1 seconds after the start of the recording; besides page views and scrolls, a form_start event — the start of filling in a form on the schedule page — goes to Google. The attached policy declares no advertising purposes at all.

3) The attached Tallinnfilm OÜ policy describes only the processing of data of members of the Artišokk cinema club, names APL Digital Solutions OÜ (the Markus platform) and Grant Thornton Baltic OÜ as authorised processors, and states that personal data is stored within the EU or the EEA. It says nothing about cookies, web analytics or advertising; Google, Meta and Sentry are not named. In fact Facebook Pixel events go to Meta Platforms (USA), and Sentry sends packets of 24–41 KB to the ingest.us.sentry.io node in the USA.


2. Recipients, retention periods, and transfers outside the EEA (Art. 15(1)(c)-(d), 46)
I also request the full list of third-party recipients, the applicable retention period for each category, and the legal basis for any transfer of data outside the EEA. The full technical audit with evidence (saved network log, SHA-256 checksum) is published at: https://gdpru.eu/en/audits/ee-kino-ee/

3. Automated processing and profiling (Art. 15(1)(h))
Please state whether I am subject to automated decision-making or profiling, and if so, disclose the logic involved.

Sincerely,

[Your name]
[contact email]
[Country]


[Date]
Teema: Isikuandmetele juurdepääsu taotlus (IKÜM art 15) — kino.ee Kellele: [märkige ettevõtte aadress — DPO / tugi / juriidiline osakond] Kellelt: [Teie nimi], [kontakt-e-post] Palun anda mulle juurdepääs minu isikuandmetele, mida töödeldakse seoses veebisaidi kino.ee kasutamisega. 1. Andmekategooriad ja töötlemise eesmärgid (IKÜM art 15(1)(a)-(c)) Sõltumatu tehnilise analüüsi põhjal palun kinnitada ja üksikasjalikult avaldada järgmised töötlemiskategooriad: 1) Nõusolekumehhanismi veebisaidil ei ole: lehe allosas olev teade ütleb, et saidi kasutamise jätkamine tähendab nõusolekut küpsistele, ja pakub ainult üht nuppu «NÕUSTUN», keeldumisvõimalust ei ole. Kaudne nõusolek sirvimise jätkamise kaudu ei ole kehtiv nõusolek. Märgistusest laaditakse Sentry (+717 ms), Google'i silt (+719 ms) ja Facebook Pixel (+886 ms); +2541…+2661 ms juures saadetakse page_view Google Analytics 4-le (G-H5X6LY021S), päring Google Adsi ahelasse (stats.g.doubleclick.net), remarketingi sihtrühmade küsimine (www.google.ee/ads/ga-audiences) ja Facebook Pixeli sündmus PageView (474915813583881). Google'i nõusolekurežiim ei ole seadistatud: kõigis päringutes on gcd=13l3l3l2l1l1 («ei ole määratud»), parameeter gcs puudub. 2) Külastaja lisatakse Google Adsi remarketingi sihtrühmadesse, ja Facebook Pixel saadab sündmuse PageView koos brauseri tuvastajaga (fbp) igal üheksast lehelaadimisest. Kõik Google'i päringud kannavad üht ja sama kliendi tuvastajat 1751470220.1790282709, mis loodi 2,1 sekundit pärast salvestuse algust; lisaks vaatamistele ja kerimisele saadetakse Google'ile sündmus form_start — vormi täitmise algus tunniplaani lehel. Lisatud poliitika reklaamieesmärke ei deklareeri üldse. 3) Lisatud Tallinnfilm OÜ poliitika kirjeldab ainult kinoklubi Artišokk liikmete andmete töötlemist, nimetab volitatud töötlejatena APL Digital Solutions OÜ (Markuse platvorm) ja Grant Thornton Baltic OÜ ning väidab, et isikuandmeid säilitatakse ELi või EMP territooriumil. Küpsistest, veebianalüütikast ja reklaamist selles pole sõnagi; Google'it, Metat ja Sentryt ei nimetata. Tegelikult saadetakse Facebook Pixeli sündmused Meta Platforms'ile (USA), ja Sentry saadab 24–41 KB suurusi pakette sõlme ingest.us.sentry.io USA-s. 2. Vastuvõtjad, säilitustähtajad ja edastamine väljapoole EMP-d (IKÜM art 15(1)(c)-(d), 46) Palun samuti esitada täielik loetelu kolmandatest isikutest vastuvõtjatest, iga kategooria puhul kohaldatavad säilitustähtajad ning andmete EMP-välisele edastamisele kohaldatav õiguslik alus, kui selline edastamine toimub. Täielik tehniline analüüs koos tõenditega (salvestatud võrgulogi, SHA-256 kontrollsumma) on avaldatud aadressil: https://gdpru.eu/en/audits/ee-kino-ee/ 3. Automatiseeritud töötlemine ja profiilianalüüs (IKÜM art 15(1)(h)) Palun teatada, kas minu suhtes kohaldatakse automatiseeritud otsuste tegemist või profiilianalüüsi, ning kui jah, siis avaldada selle loogika. Lugupidamisega, [Teie nimi] [kontakt-e-post] [Riik] [Kuupäev]
RIA DigiDoc — phone · Smart-ID / Mobile-ID
Where to file: Estonian Data Protection Inspectorate (AKI) — write to info@aki.ee
Important: AKI only handles submissions in Estonian. Translate the letter before sending.
The regulator reviews complaints in its national language. There is an officially translated template from the European Data Protection Board (EDPB) — you can use it instead of or alongside this letter: Official EDPB complaint form (PDF, your language)
Тема: Жалоба на обработку персональных данных — kino.ee

1. Предмет жалобы
Я подаю жалобу в отношении обработки моих персональных данных сайтом kino.ee.

2. Обстоятельства
Я посетил сайт kino.ee и обнаружил признаки несоответствия обработки моих персональных данных требованиям GDPR. Технический разбор, опубликованный на gdpru.eu 24.09.2026 (открытая методология, воспроизводимые измерения), документирует следующие признаки:

1) Механизма согласия на сайте нет: плашка внизу страницы сообщает, что продолжение использования сайта означает согласие на cookie, и предлагает единственную кнопку «NÕUSTUN», без отказа. Подразумеваемое согласие через продолжение просмотра действительным согласием не является. Из разметки грузятся Sentry (+717 мс), тег Google (+719 мс) и Facebook Pixel (+886 мс); на +2541…+2661 мс уходят page_view в Google Analytics 4 (G-H5X6LY021S), обращение к связке Google Ads (stats.g.doubleclick.net), запрос ремаркетинг-аудиторий (www.google.ee/ads/ga-audiences) и событие PageView Facebook Pixel (474915813583881). Режим согласия Google не настроен: во всех обращениях gcd=13l3l3l2l1l1 («не задано»), параметр gcs отсутствует.

2) Посетитель передаётся в ремаркетинг-аудитории Google Ads, а Facebook Pixel отправляет событие PageView с идентификатором браузера (fbp) на каждой из девяти загрузок страниц. Все обращения Google несут единый идентификатор клиента 1751470220.1790282709, созданный через 2,1 секунды после начала записи; помимо просмотров и прокрутки в Google уходит событие form_start — начало заполнения формы на странице расписания. Приложенная политика рекламных целей не заявляет вовсе.

3) Приложенная политика Tallinnfilm OÜ описывает только обработку данных членов киноклуба Artišokk, называет уполномоченными обработчиками APL Digital Solutions OÜ (платформа Markus) и Grant Thornton Baltic OÜ и утверждает, что персональные данные хранятся на территории ЕС или ЕЭЗ. О cookie, веб-аналитике и рекламе в ней нет ни слова; Google, Meta и Sentry не названы. Фактически события Facebook Pixel уходят Meta Platforms (США), а Sentry отправляет пакеты по 24–41 КБ на узел ingest.us.sentry.io в США.

Полная техническая документация опубликована по адресу: https://gdpru.eu/en/audits/ee-kino-ee/

3. Положения GDPR, соблюдение которых прошу проверить
ePrivacy — Директива 2002/58/EC, ст. 5(3) (в связке с GDPR Art. 6(1)(a)); GDPR Art. 6(1), Art. 5(1)(b) — рекламное отслеживание без правового основания; GDPR Art. 5(1)(a), Art. 13(1)(e), (f), Art. 44 — прозрачность и передача в третью страну

4. Требование
Прошу проверить изложенные обстоятельства и, если несоответствие подтвердится, принять меры, предусмотренные статьёй 58(2) GDPR.

5. Приложения
Полная доказательная база — HAR-файл, контрольная сумма SHA-256 и цитата из политики конфиденциальности сайта, документирующая указанное противоречие — опубликована и проверяема по ссылке в пункте 2 выше.

С уважением,

[Ваше имя]
[контактный email]
[Страна]


[Дата]
Subject: Complaint regarding personal data processing — kino.ee

1. Subject of the complaint
I am filing a complaint regarding the processing of my personal data by the website kino.ee.

2. Circumstances
I visited the website kino.ee and found indications that the processing of my personal data does not comply with the GDPR. The technical analysis published on gdpru.eu on 24 September 2026 (open methodology, reproducible measurements) documents the following indications:

1) There is no consent mechanism on the site: a notice at the bottom of the page states that continued use of the site means consent to cookies and offers a single 'NÕUSTUN' button, with no refusal. Implied consent by continued browsing is not valid consent. From the markup, Sentry (+717 ms), the Google tag (+719 ms) and the Facebook Pixel (+886 ms) load; at +2541…+2661 ms the following go out: a page_view to Google Analytics 4 (G-H5X6LY021S), a request to the Google Ads link (stats.g.doubleclick.net), a remarketing-audiences request (www.google.ee/ads/ga-audiences) and a Facebook Pixel PageView event (474915813583881). Google's consent mode is not configured: in every request gcd=13l3l3l2l1l1 ('not set'), and the gcs parameter is absent.

2) The visitor is passed into Google Ads remarketing audiences, and the Facebook Pixel sends a PageView event with a browser identifier (fbp) on each of the nine page loads. All Google requests carry a single client identifier, 1751470220.1790282709, created 2.1 seconds after the start of the recording; besides page views and scrolls, a form_start event — the start of filling in a form on the schedule page — goes to Google. The attached policy declares no advertising purposes at all.

3) The attached Tallinnfilm OÜ policy describes only the processing of data of members of the Artišokk cinema club, names APL Digital Solutions OÜ (the Markus platform) and Grant Thornton Baltic OÜ as authorised processors, and states that personal data is stored within the EU or the EEA. It says nothing about cookies, web analytics or advertising; Google, Meta and Sentry are not named. In fact Facebook Pixel events go to Meta Platforms (USA), and Sentry sends packets of 24–41 KB to the ingest.us.sentry.io node in the USA.

Full technical documentation is published at: https://gdpru.eu/en/audits/ee-kino-ee/

3. GDPR provisions I ask you to examine
ePrivacy — Directive 2002/58/EC, Art. 5(3) (in conjunction with GDPR Art. 6(1)(a)); GDPR Art. 6(1), Art. 5(1)(b) — advertising tracking without a legal basis; GDPR Art. 5(1)(a), Art. 13(1)(e), (f), Art. 44 — transparency and transfer to a third country

4. Request
I request that you examine the circumstances described and, if non-compliance is confirmed, apply the measures provided for in Article 58(2) GDPR.

5. Attachments
The full evidence base — the HAR file, its SHA-256 checksum and the quotation from the site's privacy policy documenting the stated contradiction — is published and verifiable at the link in point 2 above.

Sincerely,

[Your name]
[contact email]
[Country]


[Date]
1. Kaebuse ese Esitan kaebuse seoses minu isikuandmete töötlemisega veebisaidil kino.ee. 2. Asjaolud Külastasin veebisaiti kino.ee ja tuvastasin märke sellest, et minu isikuandmete töötlemine ei vasta isikuandmete kaitse üldmääruse (IKÜM) nõuetele. Tehniline analüüs, mis on avaldatud aadressil gdpru.eu 24.09.2026 (avatud metoodika, korratavad mõõtmised), dokumenteerib järgmist: 1) Nõusolekumehhanismi veebisaidil ei ole: lehe allosas olev teade ütleb, et saidi kasutamise jätkamine tähendab nõusolekut küpsistele, ja pakub ainult üht nuppu «NÕUSTUN», keeldumisvõimalust ei ole. Kaudne nõusolek sirvimise jätkamise kaudu ei ole kehtiv nõusolek. Märgistusest laaditakse Sentry (+717 ms), Google'i silt (+719 ms) ja Facebook Pixel (+886 ms); +2541…+2661 ms juures saadetakse page_view Google Analytics 4-le (G-H5X6LY021S), päring Google Adsi ahelasse (stats.g.doubleclick.net), remarketingi sihtrühmade küsimine (www.google.ee/ads/ga-audiences) ja Facebook Pixeli sündmus PageView (474915813583881). Google'i nõusolekurežiim ei ole seadistatud: kõigis päringutes on gcd=13l3l3l2l1l1 («ei ole määratud»), parameeter gcs puudub. 2) Külastaja lisatakse Google Adsi remarketingi sihtrühmadesse, ja Facebook Pixel saadab sündmuse PageView koos brauseri tuvastajaga (fbp) igal üheksast lehelaadimisest. Kõik Google'i päringud kannavad üht ja sama kliendi tuvastajat 1751470220.1790282709, mis loodi 2,1 sekundit pärast salvestuse algust; lisaks vaatamistele ja kerimisele saadetakse Google'ile sündmus form_start — vormi täitmise algus tunniplaani lehel. Lisatud poliitika reklaamieesmärke ei deklareeri üldse. 3) Lisatud Tallinnfilm OÜ poliitika kirjeldab ainult kinoklubi Artišokk liikmete andmete töötlemist, nimetab volitatud töötlejatena APL Digital Solutions OÜ (Markuse platvorm) ja Grant Thornton Baltic OÜ ning väidab, et isikuandmeid säilitatakse ELi või EMP territooriumil. Küpsistest, veebianalüütikast ja reklaamist selles pole sõnagi; Google'it, Metat ja Sentryt ei nimetata. Tegelikult saadetakse Facebook Pixeli sündmused Meta Platforms'ile (USA), ja Sentry saadab 24–41 KB suurusi pakette sõlme ingest.us.sentry.io USA-s. Täielik tehniline dokumentatsioon on avaldatud aadressil: https://gdpru.eu/en/audits/ee-kino-ee/ 3. Sätted, mille järgimist palun kontrollida ePrivacy direktiiv 2002/58/EU art 5(3) (koos IKÜM art 6(1)(a)-ga); IKÜM art 6(1), art 5(1)(b) — reklaami jälgimine õigusliku aluseta; IKÜM art 5(1)(a), art 13(1)(e), (f), art 44 — läbipaistvus ja edastamine kolmandasse riiki 4. Nõue Palun kontrollida kirjeldatud asjaolusid ja mittevastavuse kinnitamisel kohaldada IKÜM artikli 58 lõikes 2 ette nähtud meetmeid. 5. Lisad Täielik tõendusmaterjal — HAR-fail, kontrollsumma SHA-256 ning veebisaidi privaatsuspoliitika tsitaat, mis dokumenteerib nimetatud vastuolu — on avaldatud ja kontrollitav punktis 2 viidatud lingil. Lugupidamisega, [Teie nimi] [kontakt-e-post] [Riik] [Kuupäev]