
The site of the insurer If — a single capture of the private-client page, 73 requests, 14 nodes. The OneTrust consent management platform is in place and runs normally, the banner offers refusal on the first screen («Necessary only»), and Google's consent mode is respected — the GA4 and Google Ads events carry status gcs=G100, both storages denied, cookieless. There are two observations, both moderate. The Google Ads conversion tag and the measurement requests fire before the choice is recorded (under denial, but they fire). And the chat platform Puzzel, which sends tracking analytics, is not named in the cookie declaration, although the declaration is otherwise detailed and lists a dozen and a half recipients.
Request timeline
Declared versus actual
Transfer timings
otSDKStub.js; auto-blocking works, not 404.
ccm/collect, gcs=G100; conversion tag at +1136 ms.
GA4 page_view, gcs=G100.
api/v1/tracking; Puzzel not named in the declaration.
Detected trackers
- OneTrust (cdn.cookielaw.org, ID dc48f488-…) — consent management platform; runs normally, all requests with status 200. A banner with «Necessary only» and «Accept all» buttons — refusal is available on the first screen
- Google Analytics 4 (region1.google-analytics.com) — analytics; the page_view and PageLoad events carry status gcs=G100 (both storages denied), cookieless. The denial is respected
- Google Ads / Conversion (pagead2.googlesyndication.com — ccm/collect, pagead/conversion/11312138045) — conversion measurement; six requests with status gcs=G100, but they fire before the choice (the conversion tag at +1136 ms). The denial is respected at the consent-mode level
- Google Tag Manager (www.googletagmanager.com — GTM + four gtag) — tag container; +369 ms
- Puzzel (app-cdn.puzzel.com, app-state.puzzel.com, app-commsrv.puzzel.com, app-statistics.puzzel.com) — chat / contact-centre platform; sends persistent_state and tracking (chat analytics, +2239 ms). Not named in the cookie declaration
- Microsoft Azure Application Insights (js.monitor.azure.com, westeurope-5.in.applicationinsights.azure.com) — performance monitoring; v2/track at +1328 ms. Named in the declaration (Microsoft Application Insights)
- First party and infrastructure: www.if.ee, static.design.if.eu (design system), v.imgi.no (images, If's infrastructure in Norway), unpkg.com (web-vitals)
Indicators of GDPR non-compliance
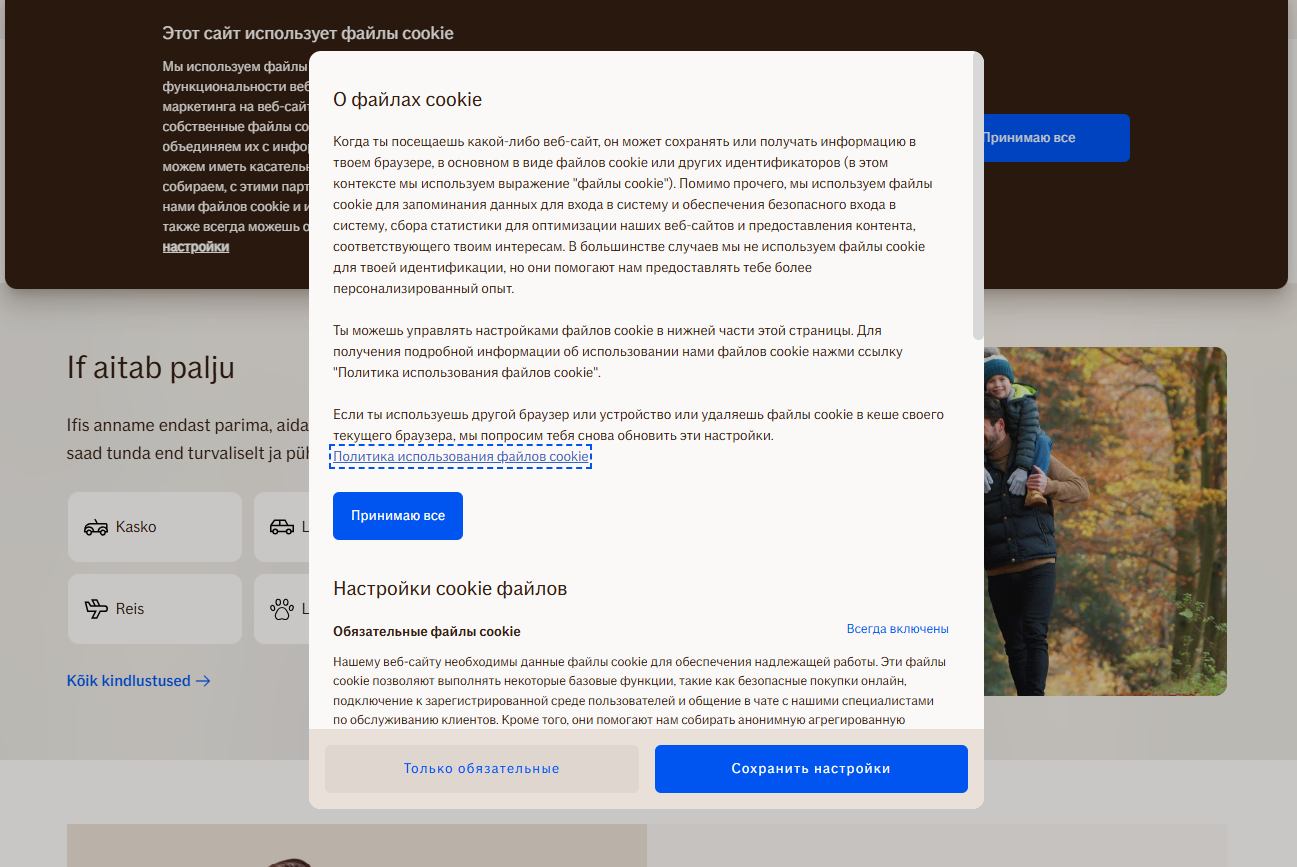
- GDPR Art. 13(1)(e) — undisclosed recipient (Puzzel)The cookie declaration (in ODT) names recipients individually: EPIServer, Google reCAPTCHA, Microsoft Application Insights, Visual Website Optimizer, Google Analytics, Confirmit, Sleeknote, HotJar, Adform, Bing, DoubleClick/Google Ads, Facebook, LinkedIn, Microsoft Ads, YouTube. However, the chat platform Puzzel (app-cdn/state/commsrv/statistics.puzzel.com), which loads in the capture and sends persistent_state and tracking analytics (app-statistics.puzzel.com/api/v1/tracking), is not mentioned in the declaration by name. In the OneTrust settings panel the chat is classified as «necessary» («chatting with our customer-service specialists»), which explains its loading as a functional component — but its separate analytics (tracking) and the recipient Puzzel itself are not disclosed.
- ePrivacy — Directive 2002/58/EC, Art. 5(3) — the Google Ads conversion tag fires before the choiceThe OneTrust consent platform is installed and runs normally (unlike the broken auto-block on some sites — here all cookielaw.org requests carry status 200), and Google's consent mode is respected: the GA4 and Google Ads events carry status gcs=G100. However, the Google Ads conversion tag (pagead2.googlesyndication.com/pagead/conversion/11312138045, en=conversion) and six ccm/collect requests fire at +692…+1269 ms — before the user's choice is recorded in the banner (no decision POST is observed in this short capture, gcs=G100 being the default denied state). The actual data transfer is held by consent mode (gcs=G100, cookieless), but the conversion tag itself initialises and sends requests before consent. For an insurance site, where the visitor chooses products relating to health, property and vehicles, the gating of advertising tags should be strict.
Context
if.ee is the site of the insurer If P&C Insurance AS (Lõõtsa 8a, Tallinn), part of the Scandinavian insurance group If. Insurance is a sensitive area: the visitor chooses products relating to health, vehicles, home, travel, pets. The processing is described by a policy (data-subject rights, DPO@if.ee, dsar@if.ee) and a detailed cookie declaration; consent is managed by the OneTrust platform.
The capture is a single recording of the private-client page (/eraklient): 73 requests, 14 nodes. The infrastructure is Scandinavian: the design system on if.eu, images from imgi.no (Norway).
Who data goes to directly
Analytics — Google Analytics 4 and Google Ads (both under denial, gcs=G100, cookieless). Consent management — OneTrust. Monitoring — Microsoft Azure Application Insights. Chat platform — Puzzel (sends state and analytics). Functionally — reCAPTCHA, web-vitals, the design system, images. The first party is If’s infrastructure.
Declared versus actual
The site is built tidily, and the observations here are moderate — two points.
Consent works, Google’s mode is respected. The OneTrust platform runs normally: all cookielaw.org requests carry status 200 (the auto-block is not broken), the banner offers refusal on the first screen — the «Necessary only» button next to «Accept all». The GA4 events (page_view, PageLoad) and Google Ads carry status gcs=G100: both storages denied, pings cookieless. This is correct behaviour when consent has not been given.
But the Google Ads conversion tag fires before the choice. The pagead2.googlesyndication.com/ccm/collect requests (six of them) and the conversion tag /pagead/conversion/11312138045 (en=conversion, +1136 ms) go out at +692…+1269 ms — before the user made a choice in the banner (no decision POST is observed in this short capture; gcs=G100 is the default denied state). The actual transfer is held by consent mode — the data is under denial, cookieless — but the conversion tag itself initialises and sends requests before consent. For an insurance site the gating of advertising tags should be made strict: before the choice they should not fire even under denial.
And the chat platform is not disclosed. The cookie declaration is detailed — it names a dozen and a half recipients individually (EPIServer, reCAPTCHA, App Insights, VWO, Google Analytics, Confirmit, Sleeknote, HotJar, Adform, Bing, DoubleClick/Google Ads, Facebook, LinkedIn, Microsoft Ads, YouTube). But the chat platform Puzzel, which in the capture loads and sends persistent_state and tracking analytics (app-statistics.puzzel.com/api/v1/tracking), is not mentioned in the declaration by name. In the OneTrust settings panel the chat is classified as «necessary» («chatting with our customer-service specialists»), which explains its loading as a functional component. But its separate analytics and the recipient Puzzel itself remain undisclosed — and this is a Norwegian contact-centre platform, a separate recipient of data.
Consent: what is proven and what is not
Proven: OneTrust runs normally. All cookielaw.org requests carry status 200; the banner with refusal on the first screen is recorded in the screenshots.
Proven: Google’s consent mode is respected. All GA4 and Google Ads requests carry gcs=G100, cookielessly.
Proven: the Google Ads conversion tag fires before the choice. /pagead/conversion/… at +1136 ms, ccm/collect at +692…+1269 ms — before the decision POST (which is absent from the capture).
Proven: Puzzel sends analytics and is not named in the declaration. app-statistics.puzzel.com/tracking at +2239 ms; a search of the declaration does not find the name Puzzel.
Not established: the consent decision. In this short capture no OneTrust decision POST is observed; gcs=G100 indicates the default denied state, the action itself is not visible in the recording.
Not proven: profile persistence. The GA cid was set in the same second as the capture — a fresh session; «a profile from previous visits» is not asserted.
Not proven: the content of the Puzzel and Google Ads requests. What tracking and ccm/collect carry beyond service fields cannot be read from the cleaned file.
Observation boundaries
The capture covers a single page (private client) and records browser behaviour, not server-side processing: what the parties do with the received (storage-denied) signals and how the GTM container is configured is not verified by a browser capture. The classification of the Puzzel chat as «necessary» is the site’s position from the settings panel; the chat’s functionality justifies it, but its separate analytics (tracking) and the disclosure of the recipient are a separate question. The images from imgi.no and the design system from if.eu are attributed to the If group’s infrastructure.
The file is published cleaned of personal data (63 redactions, self-check clean); the load order, the gcs=G100 status of the Google requests, the 200 statuses of OneTrust and the Puzzel requests can be verified directly against the published file and the screenshots. The banner and its buttons are from the screenshots (live UI).
The legal assessment is made by the competent authority — Andmekaitse Inspektsioon.
Conclusion
The insurance site is built tidily and is noticeably closer to the norm than many. The OneTrust consent platform runs normally, the banner offers refusal on the first screen («Necessary only»), and Google’s consent mode is respected: analytics and conversion measurement run under denial, gcs=G100, cookieless. The cookie declaration is detailed and names a dozen and a half recipients individually.
There are two observations, and both are moderate. The Google Ads conversion tag and the ccm/collect requests initialise and fire before the user made a choice in the banner — this time without a data leak, because consent mode held them; but for an insurance site the gating should be made strict, so that advertising tags do not fire before consent even under denial. And the chat platform Puzzel, which sends analytics, is not named in the otherwise detailed declaration — even though it is a separate Norwegian contact-centre platform and a separate recipient.
Remediation: condition the initialisation of the Google Ads conversion tag and the ccm/collect requests on actual consent, so that before the choice they do not fire; name the chat platform Puzzel in the cookie declaration as a recipient with its purpose stated (chat) and its separate analytics (tracking); otherwise the current configuration — a working OneTrust, refusal on the first screen, Google’s consent mode respected — can serve as a reference.
How to verify: download the file and compute its checksum — sha256sum file.har (Linux, macOS) or certutil -hashfile file.har SHA256 (Windows); it must match the one shown. The conclusions apply to the scope of this measurement — see the limitations of the method.
f9fe19fdce6ab9060eb4a15c63fd44e24555cb7afcd16da89acdbcfc50fb8b73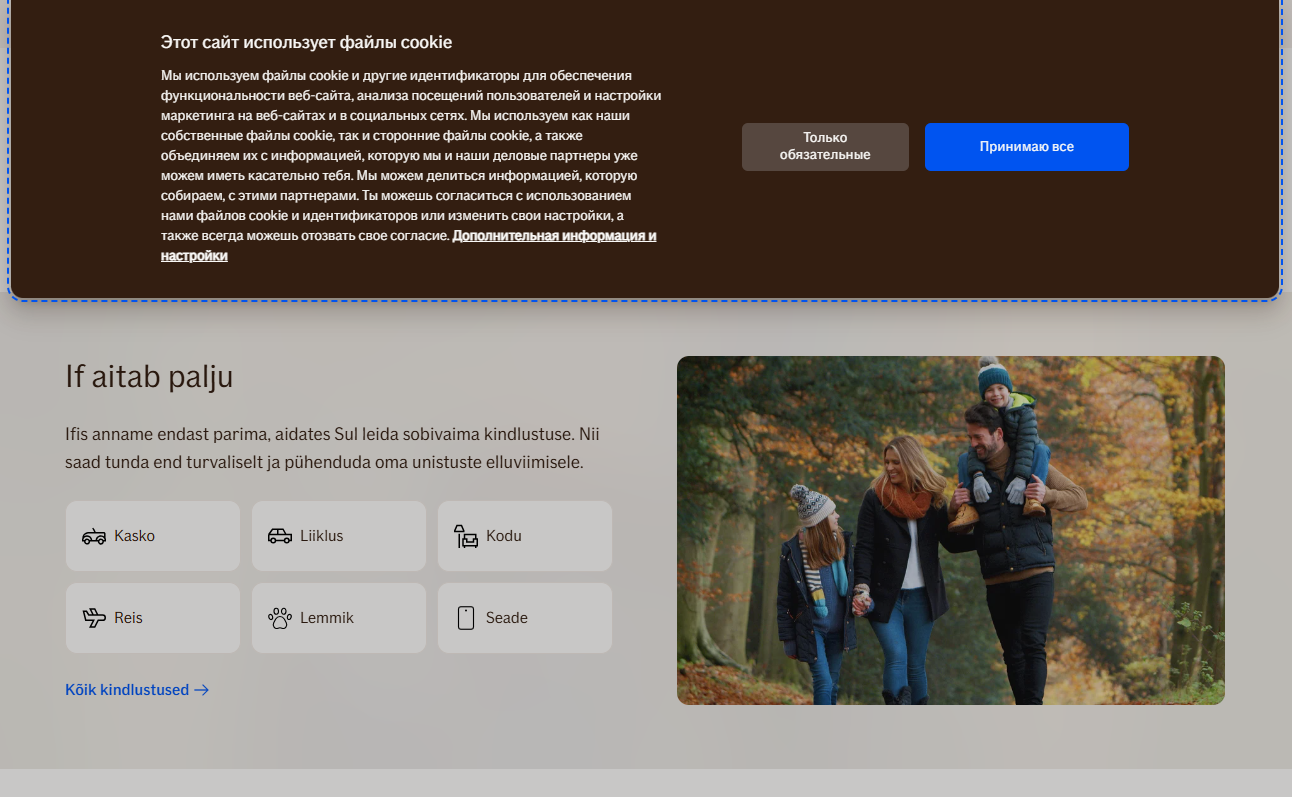
Want a response from the company about this audit? → Open the tool
Fill in once — it will be inserted into every letter below:
All fields are required to print the document — this is a formal requirement of the letter itself (the particulars of an official submission), not data collection: nothing is sent or saved anywhere, it all stays in your browser and disappears when you close the page. See the methodology for details.
RIA DigiDoc — phone · Smart-ID / Mobile-ID
Send this letter directly to the company first — before contacting the regulator it has the right to respond (GDPR Art. 12(3) — 30 days).
Тема: Запрос доступа к персональным данным (ст. 15 GDPR) — if.ee

Кому: [укажите адрес компании — DPO / поддержка / юридический отдел]
От: [Ваше имя], [контактный email]

Прошу предоставить доступ к моим персональным данным, обрабатываемым в связи с использованием сайта if.ee.

1. Категории данных и цели обработки (ст. 15(1)(a)-(c))
На основании независимого технического анализа сайта прошу подтвердить и подробно раскрыть следующие категории обработки:

1) Куки-декларация (в ODT) называет получателей поимённо: EPIServer, Google reCAPTCHA, Microsoft Application Insights, Visual Website Optimizer, Google Analytics, Confirmit, Sleeknote, HotJar, Adform, Bing, DoubleClick/Google Ads, Facebook, LinkedIn, Microsoft Ads, YouTube. Однако платформа чата Puzzel (app-cdn/state/commsrv/statistics.puzzel.com), которая грузится в замере и отправляет persistent_state и аналитику tracking (app-statistics.puzzel.com/api/v1/tracking), в декларации по имени не упомянута. В панели настроек OneTrust чат отнесён к «обязательным» («общение в чате с нашими специалистами»), что объясняет его загрузку как функционального компонента, — но его отдельная аналитика (tracking) и сам получатель Puzzel в декларации не раскрыты.

2) Платформа согласия OneTrust установлена и работает штатно (в отличие от сломанной автоблокировки на некоторых сайтах — здесь все обращения cookielaw.org со статусом 200), а режим согласия Google соблюдён: события GA4 и Google Ads идут со статусом gcs=G100. Однако конверсионный тег Google Ads (pagead2.googlesyndication.com/pagead/conversion/11312138045, en=conversion) и шесть обращений ccm/collect срабатывают на +692…+1269 мс — до фиксации выбора пользователя в баннере (POST решения в этом коротком замере не наблюдается, gcs=G100 — дефолтное запрещённое состояние). Фактическая передача данных удержана consent mode (gcs=G100, бескуково), но сам конверсионный тег инициализируется и отправляет обращения до согласия. Для страхового сайта, где посетитель выбирает продукты по здоровью, имуществу и авто, гейтинг рекламных тегов должен быть строгим.


2. Получатели, сроки хранения и передача за пределы ЕЭЗ (ст. 15(1)(c)-(d), 46)
Прошу также указать полный список третьих лиц-получателей, применимые сроки хранения по каждой категории и правовые основания передачи данных за пределы ЕЭЗ, если таковая происходит. Полный технический разбор с доказательствами (сохранённый сетевой журнал, контрольная сумма SHA-256) опубликован по адресу: https://gdpru.eu/en/audits/ee-if-ee/

3. Автоматизированная обработка и профилирование (ст. 15(1)(h))
Прошу сообщить, применяется ли в отношении меня автоматизированное принятие решений или профилирование, и если да — раскрыть логику такой обработки.

С уважением,

[Ваше имя]
[контактный email]
[Страна]


[Дата]
Subject: Data access request (GDPR Art. 15) — if.ee

To: [insert the company's address — DPO / support / legal department]
From: [Your name], [contact email]

I request access to my personal data processed in connection with the website if.ee.

1. Categories of data and purposes of processing (Art. 15(1)(a)-(c))
Based on an independent technical analysis of the site, I request confirmation and detailed disclosure of the following categories of processing:

1) The cookie declaration (in ODT) names recipients individually: EPIServer, Google reCAPTCHA, Microsoft Application Insights, Visual Website Optimizer, Google Analytics, Confirmit, Sleeknote, HotJar, Adform, Bing, DoubleClick/Google Ads, Facebook, LinkedIn, Microsoft Ads, YouTube. However, the chat platform Puzzel (app-cdn/state/commsrv/statistics.puzzel.com), which loads in the capture and sends persistent_state and tracking analytics (app-statistics.puzzel.com/api/v1/tracking), is not mentioned in the declaration by name. In the OneTrust settings panel the chat is classified as «necessary» («chatting with our customer-service specialists»), which explains its loading as a functional component — but its separate analytics (tracking) and the recipient Puzzel itself are not disclosed.

2) The OneTrust consent platform is installed and runs normally (unlike the broken auto-block on some sites — here all cookielaw.org requests carry status 200), and Google's consent mode is respected: the GA4 and Google Ads events carry status gcs=G100. However, the Google Ads conversion tag (pagead2.googlesyndication.com/pagead/conversion/11312138045, en=conversion) and six ccm/collect requests fire at +692…+1269 ms — before the user's choice is recorded in the banner (no decision POST is observed in this short capture, gcs=G100 being the default denied state). The actual data transfer is held by consent mode (gcs=G100, cookieless), but the conversion tag itself initialises and sends requests before consent. For an insurance site, where the visitor chooses products relating to health, property and vehicles, the gating of advertising tags should be strict.


2. Recipients, retention periods, and transfers outside the EEA (Art. 15(1)(c)-(d), 46)
I also request the full list of third-party recipients, the applicable retention period for each category, and the legal basis for any transfer of data outside the EEA. The full technical audit with evidence (saved network log, SHA-256 checksum) is published at: https://gdpru.eu/en/audits/ee-if-ee/

3. Automated processing and profiling (Art. 15(1)(h))
Please state whether I am subject to automated decision-making or profiling, and if so, disclose the logic involved.

Sincerely,

[Your name]
[contact email]
[Country]


[Date]
Teema: Isikuandmetele juurdepääsu taotlus (IKÜM art 15) — if.ee

Kellele: [märkige ettevõtte aadress — DPO / tugi / juriidiline osakond]
Kellelt: [Teie nimi], [kontakt-e-post]

Palun anda mulle juurdepääs minu isikuandmetele, mida töödeldakse seoses veebisaidi if.ee kasutamisega.

1. Andmekategooriad ja töötlemise eesmärgid (IKÜM art 15(1)(a)-(c))
Sõltumatu tehnilise analüüsi põhjal palun kinnitada ja üksikasjalikult avaldada järgmised töötlemiskategooriad:

1) Küpsiste deklaratsioonis (ODT-s) nimetatakse saajaid nime järgi: EPIServer, Google reCAPTCHA, Microsoft Application Insights, Visual Website Optimizer, Google Analytics, Confirmit, Sleeknote, HotJar, Adform, Bing, DoubleClick/Google Ads, Facebook, LinkedIn, Microsoft Ads, YouTube. Kuid Puzzeli vestlusplatvorm (app-cdn/state/commsrv/statistics). puzzel.com, mis laadib mõõtmisel ja saadab püsiva oleku ja jälgimise analüüsi (app-statistics.puzzel.com/api/v1/tracking), ei ole deklaratsioonis nimeliselt mainitud. Seadistuste paneelis liigitatakse OneTrust vestlus "kohustuslikuks", mis selgitab selle allalaadimist funktsionaalse komponendina, kuid selle eraldi analüüsi (jälgimist) ja Puzzeli saajat deklaratsioonis ei avaldata.

2) OneTrust’i nõusoleku platvorm on installitud ja töötab normaalselt (erinevalt katkistest automaatsetest blokeeringutest mõnedel saitidel – siin on kõik cookielaw.org kõned staatusega 200) ja Google’i nõusolekurežiimi järgitud: GA4 ja Google Adsi sündmused on staatusega gcs=G100. Google Adsi konversioonisilt (pagead2.googlesyndication.com/pagead/conversion/11312138045, en=conversion) ja kuus ccm/collect kõnet käivituvad aga +692 võrra. +1269 ms - enne kasutaja valiku kinnitamist bänneris (POST-otsust selles lühikeses mõõtmises ei järgita, gcs=G100 - vaikimisi keelatud olek). Tegelik andmete edastamine toimub nõusoleku režiimis (gcs=G100, küpsisevaba), kuid konversiooni sild ise on initsialiseeritud ja saadab taotlused enne nõusoleku saamist. Kindlustussaidi puhul, kus külastaja valib tervise-, vara- ja autotooted, peaks reklaamisiltide värav olema range.


2. Vastuvõtjad, säilitustähtajad ja edastamine väljapoole EMP-d (IKÜM art 15(1)(c)-(d), 46)
Palun samuti esitada täielik loetelu kolmandatest isikutest vastuvõtjatest, iga kategooria puhul kohaldatavad säilitustähtajad ning andmete EMP-välisele edastamisele kohaldatav õiguslik alus, kui selline edastamine toimub. Täielik tehniline analüüs koos tõenditega (salvestatud võrgulogi, SHA-256 kontrollsumma) on avaldatud aadressil: https://gdpru.eu/en/audits/ee-if-ee/

3. Automatiseeritud töötlemine ja profiilianalüüs (IKÜM art 15(1)(h))
Palun teatada, kas minu suhtes kohaldatakse automatiseeritud otsuste tegemist või profiilianalüüsi, ning kui jah, siis avaldada selle loogika.

Lugupidamisega,

[Teie nimi]
[kontakt-e-post]
[Riik]


[Kuupäev]
RIA DigiDoc — phone · Smart-ID / Mobile-ID
Where to file: Estonian Data Protection Inspectorate (AKI) — write to info@aki.ee
Important: AKI only handles submissions in Estonian. Translate the letter before sending.
The regulator reviews complaints in its national language. There is an officially translated template from the European Data Protection Board (EDPB) — you can use it instead of or alongside this letter: Official EDPB complaint form (PDF, your language)
Тема: Жалоба на обработку персональных данных — if.ee

1. Предмет жалобы
Я подаю жалобу в отношении обработки моих персональных данных сайтом if.ee.

2. Обстоятельства
Я посетил сайт if.ee и обнаружил признаки несоответствия обработки моих персональных данных требованиям GDPR. Технический разбор, опубликованный на gdpru.eu 12.09.2026 (открытая методология, воспроизводимые измерения), документирует следующие признаки:

1) Куки-декларация (в ODT) называет получателей поимённо: EPIServer, Google reCAPTCHA, Microsoft Application Insights, Visual Website Optimizer, Google Analytics, Confirmit, Sleeknote, HotJar, Adform, Bing, DoubleClick/Google Ads, Facebook, LinkedIn, Microsoft Ads, YouTube. Однако платформа чата Puzzel (app-cdn/state/commsrv/statistics.puzzel.com), которая грузится в замере и отправляет persistent_state и аналитику tracking (app-statistics.puzzel.com/api/v1/tracking), в декларации по имени не упомянута. В панели настроек OneTrust чат отнесён к «обязательным» («общение в чате с нашими специалистами»), что объясняет его загрузку как функционального компонента, — но его отдельная аналитика (tracking) и сам получатель Puzzel в декларации не раскрыты.

2) Платформа согласия OneTrust установлена и работает штатно (в отличие от сломанной автоблокировки на некоторых сайтах — здесь все обращения cookielaw.org со статусом 200), а режим согласия Google соблюдён: события GA4 и Google Ads идут со статусом gcs=G100. Однако конверсионный тег Google Ads (pagead2.googlesyndication.com/pagead/conversion/11312138045, en=conversion) и шесть обращений ccm/collect срабатывают на +692…+1269 мс — до фиксации выбора пользователя в баннере (POST решения в этом коротком замере не наблюдается, gcs=G100 — дефолтное запрещённое состояние). Фактическая передача данных удержана consent mode (gcs=G100, бескуково), но сам конверсионный тег инициализируется и отправляет обращения до согласия. Для страхового сайта, где посетитель выбирает продукты по здоровью, имуществу и авто, гейтинг рекламных тегов должен быть строгим.

Полная техническая документация опубликована по адресу: https://gdpru.eu/en/audits/ee-if-ee/

3. Положения GDPR, соблюдение которых прошу проверить
GDPR Art. 13(1)(e) — нераскрытый получатель (Puzzel); ePrivacy — Директива 2002/58/EC, ст. 5(3) — конверсионный тег Google Ads срабатывает до выбора

4. Требование
Прошу проверить изложенные обстоятельства и, если несоответствие подтвердится, принять меры, предусмотренные статьёй 58(2) GDPR.

5. Приложения
Полная доказательная база — HAR-файл, контрольная сумма SHA-256 и цитата из политики конфиденциальности сайта, документирующая указанное противоречие — опубликована и проверяема по ссылке в пункте 2 выше.

С уважением,

[Ваше имя]
[контактный email]
[Страна]


[Дата]
Subject: Complaint regarding personal data processing — if.ee

1. Subject of the complaint
I am filing a complaint regarding the processing of my personal data by the website if.ee.

2. Circumstances
I visited the website if.ee and found indications that the processing of my personal data does not comply with the GDPR. The technical analysis published on gdpru.eu on 12 September 2026 (open methodology, reproducible measurements) documents the following indications:

1) The cookie declaration (in ODT) names recipients individually: EPIServer, Google reCAPTCHA, Microsoft Application Insights, Visual Website Optimizer, Google Analytics, Confirmit, Sleeknote, HotJar, Adform, Bing, DoubleClick/Google Ads, Facebook, LinkedIn, Microsoft Ads, YouTube. However, the chat platform Puzzel (app-cdn/state/commsrv/statistics.puzzel.com), which loads in the capture and sends persistent_state and tracking analytics (app-statistics.puzzel.com/api/v1/tracking), is not mentioned in the declaration by name. In the OneTrust settings panel the chat is classified as «necessary» («chatting with our customer-service specialists»), which explains its loading as a functional component — but its separate analytics (tracking) and the recipient Puzzel itself are not disclosed.

2) The OneTrust consent platform is installed and runs normally (unlike the broken auto-block on some sites — here all cookielaw.org requests carry status 200), and Google's consent mode is respected: the GA4 and Google Ads events carry status gcs=G100. However, the Google Ads conversion tag (pagead2.googlesyndication.com/pagead/conversion/11312138045, en=conversion) and six ccm/collect requests fire at +692…+1269 ms — before the user's choice is recorded in the banner (no decision POST is observed in this short capture, gcs=G100 being the default denied state). The actual data transfer is held by consent mode (gcs=G100, cookieless), but the conversion tag itself initialises and sends requests before consent. For an insurance site, where the visitor chooses products relating to health, property and vehicles, the gating of advertising tags should be strict.

Full technical documentation is published at: https://gdpru.eu/en/audits/ee-if-ee/

3. GDPR provisions I ask you to examine
GDPR Art. 13(1)(e) — undisclosed recipient (Puzzel); ePrivacy — Directive 2002/58/EC, Art. 5(3) — the Google Ads conversion tag fires before the choice

4. Request
I request that you examine the circumstances described and, if non-compliance is confirmed, apply the measures provided for in Article 58(2) GDPR.

5. Attachments
The full evidence base — the HAR file, its SHA-256 checksum and the quotation from the site's privacy policy documenting the stated contradiction — is published and verifiable at the link in point 2 above.

Sincerely,

[Your name]
[contact email]
[Country]


[Date]
1. Kaebuse ese
Esitan kaebuse seoses minu isikuandmete töötlemisega veebisaidil if.ee.

2. Asjaolud
Külastasin veebisaiti if.ee ja tuvastasin märke sellest, et minu isikuandmete töötlemine ei vasta isikuandmete kaitse üldmääruse (IKÜM) nõuetele. Tehniline analüüs, mis on avaldatud aadressil gdpru.eu 12.09.2026 (avatud metoodika, korratavad mõõtmised), dokumenteerib järgmist:

1) Küpsiste deklaratsioonis (ODT-s) nimetatakse saajaid nime järgi: EPIServer, Google reCAPTCHA, Microsoft Application Insights, Visual Website Optimizer, Google Analytics, Confirmit, Sleeknote, HotJar, Adform, Bing, DoubleClick/Google Ads, Facebook, LinkedIn, Microsoft Ads, YouTube. Kuid Puzzeli vestlusplatvorm (app-cdn/state/commsrv/statistics). puzzel.com, mis laadib mõõtmisel ja saadab püsiva oleku ja jälgimise analüüsi (app-statistics.puzzel.com/api/v1/tracking), ei ole deklaratsioonis nimeliselt mainitud. Seadistuste paneelis liigitatakse OneTrust vestlus "kohustuslikuks", mis selgitab selle allalaadimist funktsionaalse komponendina, kuid selle eraldi analüüsi (jälgimist) ja Puzzeli saajat deklaratsioonis ei avaldata.

2) OneTrust’i nõusoleku platvorm on installitud ja töötab normaalselt (erinevalt katkistest automaatsetest blokeeringutest mõnedel saitidel – siin on kõik cookielaw.org kõned staatusega 200) ja Google’i nõusolekurežiimi järgitud: GA4 ja Google Adsi sündmused on staatusega gcs=G100. Google Adsi konversioonisilt (pagead2.googlesyndication.com/pagead/conversion/11312138045, en=conversion) ja kuus ccm/collect kõnet käivituvad aga +692 võrra. +1269 ms - enne kasutaja valiku kinnitamist bänneris (POST-otsust selles lühikeses mõõtmises ei järgita, gcs=G100 - vaikimisi keelatud olek). Tegelik andmete edastamine toimub nõusoleku režiimis (gcs=G100, küpsisevaba), kuid konversiooni sild ise on initsialiseeritud ja saadab taotlused enne nõusoleku saamist. Kindlustussaidi puhul, kus külastaja valib tervise-, vara- ja autotooted, peaks reklaamisiltide värav olema range.

Täielik tehniline dokumentatsioon on avaldatud aadressil: https://gdpru.eu/en/audits/ee-if-ee/

3. Sätted, mille järgimist palun kontrollida
GDPR art 13(1)(e) Avaldamata saaja (Puzzel); e-privaatsus – direktiiv 2002/58/EÜ, artikli 5 lõige 3 – Google Adsi teisendussilt aktiveeritakse enne valimist

4. Nõue
Palun kontrollida kirjeldatud asjaolusid ja mittevastavuse kinnitamisel kohaldada IKÜM artikli 58 lõikes 2 ette nähtud meetmeid.

5. Lisad
Täielik tõendusmaterjal — HAR-fail, kontrollsumma SHA-256 ning veebisaidi privaatsuspoliitika tsitaat, mis dokumenteerib nimetatud vastuolu — on avaldatud ja kontrollitav punktis 2 viidatud lingil.

Lugupidamisega,

[Teie nimi]
[kontakt-e-post]
[Riik]


[Kuupäev]