
ellex.legal
Website of the Baltic Ellex law firms — one recording, five pages, 360 requests, eleven nodes. A CookieYes banner with three equal-weight buttons, analytics and advertising off, the decision recorded twice, and Google's consent status remaining 'denied' throughout. But Google Analytics 4 in Consent Mode's advanced mode sends page_view and scroll on every page, and the Google tag appends a _gl parameter with an encoded client identifier to internal links. As a result, although no cookies are stored, all requests to Google over four and a half minutes are linked by one visitor identifier: refusing cookies does not break the tracking. The policy says data is passed to third parties only when required by law, and its cookie section describes a banner replaced long ago. The browser did not send a DNT header.
Request timeline
Declared versus actual
Transfer timings
CookieYes, advertising and analytics off by default.
gtag/js GT-WRDDK49, Consent Mode advanced mode, _gl link decoration.
page_view, gcs=G100, cid 524291266.1790287814.
api/v1/consent; Google's status afterwards — G100.
page_view on the home page at an address with _gl; then scroll, careers, policy, home page — the same cid.
Detected trackers
- Google Analytics 4 (G-F79LTMTJ9P) via region1.google-analytics.com — page_view and scroll in the 'denied' consent state (gcs=G100) with one client identifier across all pages
- Google Tag (www.googletagmanager.com, tags GT-WRDDK49 and GTM-MN5MQ4SV) — the Google tag and a container; appends a _gl parameter carrying the client identifier to internal links
- CookieYes (cdn-cookieyes.com, log.cookieyes.com, directory.cookieyes.com) — consent-management platform
- Google reCAPTCHA (www.google.com/recaptcha, www.gstatic.com, csp.withgoogle.com) — form protection, loaded on every page
- Google Fonts (fonts.googleapis.com, fonts.gstatic.com) — the Inter and Arsenal fonts; the visitor's IP address is visible to Google
Indicators of GDPR non-compliance
- ePrivacy — Directive 2002/58/EC, Art. 5(3) (in conjunction with GDPR Art. 6(1)(a)) — transmission in the 'denied' stateThe CookieYes banner offers equal-weight 'Customise', 'Reject All' and 'Accept All', with analytics and advertising off. The Google tag (GT-WRDDK49) runs in Consent Mode's advanced mode: the first page_view to Google Analytics 4 goes out at +1204 ms with the status gcs=G100 (analytics and advertising denied), before any choice. CookieYes records a decision twice (+68093 and +257081 ms), and the status remains 'denied' afterwards, which is consistent with a refusal. Nonetheless on every subsequent page — the home page, careers, the privacy policy — page_view and scroll events go to Google (+83199, +90071, +106853, +120446, +132093, +270220 ms) with the page address and device information. Under EDPB Guidelines 2/2023 on the technical scope of Art. 5(3), reading such information from the device by script requires consent even without the use of cookies.
- ePrivacy — Directive 2002/58/EC, Art. 5(3); GDPR Art. 5(1)(c), Art. 6(1) — a visitor identifier carried in link addressesIn the 'denied' state Google Analytics cookies are not stored; however, the Google tag appends to all internal links a _gl parameter in which the client identifier is encoded: _ga*NTI0MjkxMjY2LjE3OTAyODc4MTQ decodes to 524291266.1790287814. The next page reads the identifier from the address, so all eight Google Analytics requests over 270 seconds — across five pages and after both decisions in the banner — carry one and the same client identifier, with the first-visit flag set only on the first page. The identifier was created at 22:10:14 UTC, 1.5 seconds after the start of the recording. Thus refusing cookies does not break the linking of one visitor's page views: the identity is carried in the page address and, as part of that address, transmitted to Google Analytics.
- GDPR Art. 5(1)(a), Art. 13(1)(e) — transparency: the declared diverges from the actualThe Ellex Circle policy states that personal data is disclosed to third parties only when required under applicable law; its cookie section describes the cookie of a former banner, gotoandplay_cookie_agreement, and the Google Analytics cookies _ga, _gid, _gat, and mentions neither CookieYes, nor Google's consent mode, nor the _gl parameter. The CookieYes declaration promises to store analytics cookies only with prior consent and describes _ga as storing information 'anonymously'. In fact browsing information with a stable identifier goes to Google without consent. reCAPTCHA is not named in the policy.
Context
ellex.legal is the website of the Ellex Circle law firms: Ellex Raidla in Estonia (Ahtri 4, 10117 Tallinn), Ellex Kļaviņš in Latvia and Ellex Valiūnas in Lithuania; each firm is the data controller in its own country. The data-protection contact for Estonia is privacy.estonia@ellex.legal. The site is built on WordPress (WPML), Apache server.
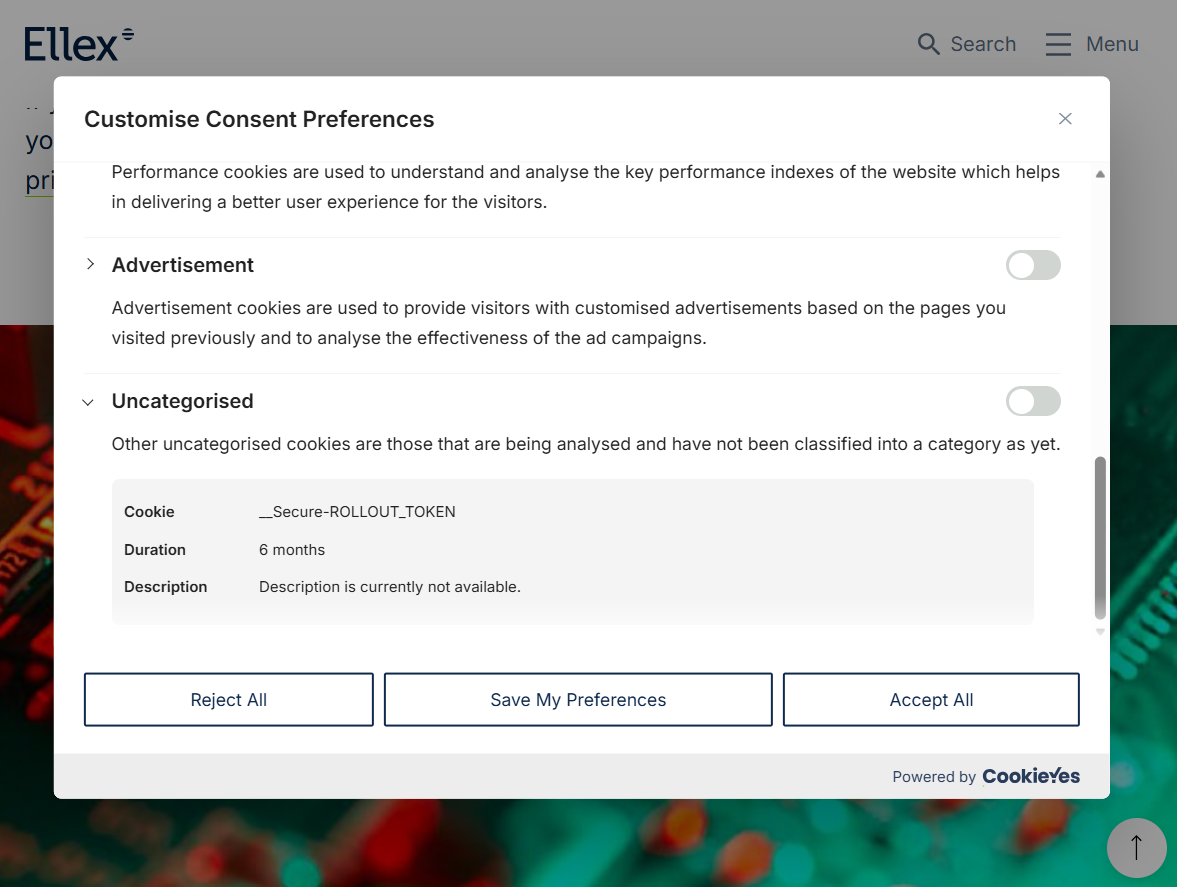
Processing is described by the Ellex Circle privacy policy and the CookieYes cookie declaration. Attached to the material are two screenshots: the consent banner and the settings window.
The measurement consists of one recording of about four and a half minutes: a lawyer’s page, the home page, careers, the privacy policy and the home page twice. Three hundred and sixty requests, eleven nodes. The recording was made on 25 September 2026.
Who data goes to directly
Google (Analytics 4, Google tag, reCAPTCHA, Fonts), CookieYes (the consent platform). There is no advertising, Facebook or RTB in the recording.
Declared versus actual
The policy states that personal data is passed to processors and to Ellex Circle firms, and to third parties only when required under applicable law. Its cookie section describes the gotoandplay_cookie_agreement cookie of a former banner and the Google Analytics cookies _ga, _gid, _gat. The CookieYes declaration promises that third-party analytics and advertising cookies are stored only with prior consent, and that _ga stores information ‘anonymously’.
The measurement shows the following.
The consent platform is correctly configured. The CookieYes banner, as seen in the screenshots, offers three equal-weight buttons — ‘Customise’, ‘Reject All’, ‘Accept All’; advertising and uncategorised cookies are off. A decision is recorded twice (+68093 and +257081 ms). Google’s consent status in every request is gcs=G100, analytics and advertising denied; it does not change after either record, which is consistent with a refusal.
Google Analytics sends data in the ‘denied’ state. The Google tag GT-WRDDK49 runs in Consent Mode’s advanced mode. The first page_view of property G-F79LTMTJ9P goes out at +1204 ms, before any choice; then page_view and scroll go out on every page — the home page, careers, the privacy policy — up to +270220 ms. Each request carries the page address and device information. Under EDPB Guidelines 2/2023 on the technical scope of Art. 5(3), such reading requires consent even without the use of cookies.
The visitor identifier is carried in link addresses. This is the main difference from sites where Consent Mode’s advanced mode merely sends unconnected requests. Here the Google tag appends a _gl parameter to all internal links, in which the client identifier is encoded: the fragment _ga*NTI0MjkxMjY2LjE3OTAyODc4MTQ decodes to 524291266.1790287814. The next page reads the identifier from the address — which is why all eight Google Analytics requests over 270 seconds, across five pages and after both decisions in the banner, carry one and the same identifier, and the first-visit flag is set only on the first page. No cookies are stored, but the linking of one visitor’s page views continues: refusing cookies does not break it. The identifier ends up in the address bar, the browser history, the site’s server logs and — as part of the page address — in Google Analytics. It does not go to third-party nodes via the Referer header: the strict-origin-when-cross-origin referrer policy passes them only the origin.
The documents do not reflect this. The policy’s cookie section describes a banner replaced long ago and mentions neither CookieYes, nor the consent mode, nor the _gl parameter; reCAPTCHA is not named. The statement that data goes to third parties only when required by law diverges from the transmission of browsing information to Google without consent.
Functional nodes: Google reCAPTCHA loads on every page (together with csp.withgoogle.com report collection), and the Inter and Arsenal fonts load from Google Fonts.
Consent: what is proven and what is not
Proven: a banner with an equal-weight refusal, decisions recorded. By the screenshots and two log.cookieyes.com/api/v1/consent requests.
Proven: Google’s consent status throughout is ‘denied’. By the value gcs=G100 in all eight requests.
Proven: page_view and scroll nonetheless go to Google on every page. Eight /g/collect requests.
Proven: the client identifier is the same on all pages and is carried via _gl. By the cid value in the requests and the decoding of the _gl parameter in the navigation addresses.
Not proven and not asserted: the content of the consent records. The bodies of the api/v1/consent requests are redacted in the published file; the conclusion about a refusal rests on the unchanged gcs=G100 status after both records.
Separately: the browser did not send a DNT header in this recording.
Bounds of observation
The measurement covers five pages of the site; no forms were submitted. Observation captures the browser’s behaviour, not the internal side of the services: how Google processes the received requests is not verified by a browser measurement. The legal assessment is made by the competent authority — in Estonia, Andmekaitse Inspektsioon, named in the policy alongside the authorities of Latvia and Lithuania.
The file is published redacted under a “lean” profile: cookie values in requests have been removed, the Cookie and Set-Cookie headers stripped; the redaction registry records 280 redactions and a checksum. The consent-mode parameters, the client identifier and the addresses with the _gl parameter are fully legible from the recording.
The identification of services relies on domains and address patterns: analytics — by google-analytics.com and property G-F79LTMTJ9P; the tag — by googletagmanager.com and GT-WRDDK49; the consent platform — by cookieyes.com; reCAPTCHA — by google.com/recaptcha. The _gl parameter was decoded as the base64 value of the _ga field.
Conclusion
A correctly configured CookieYes banner with an equal-weight refusal operates on the Ellex law firms’ website, the decision is recorded, and Google’s consent status remains ‘denied’ throughout. However, Google Analytics 4 in Consent Mode’s advanced mode sends page_view and scroll on every page, and the Google tag carries the client identifier between pages through the _gl parameter in link addresses. As a result, although no cookies are stored, all of a visitor’s page views in the session are linked in Google by one identifier — the refusal stops the writing of cookies, but not the tracking. The policy promises transfer to third parties only when required by law, and its cookie section describes a banner replaced long ago and reflects neither the current consent platform nor Google’s consent mode.
Remediation: switch Google Analytics to Consent Mode’s basic mode, in which the tag neither loads nor sends requests before consent; disable _gl link decoration for the site’s own domain (the linker is intended for navigation between different domains) or apply it only after consent; update the policy’s cookie section — describe CookieYes, the consent mode, Google Analytics with its legal basis, and reCAPTCHA; bring the wording on transfers to third parties into line with the actual transmission to Google.
How to verify: download the file and compute its checksum — sha256sum file.har (Linux, macOS) or certutil -hashfile file.har SHA256 (Windows); it must match the one shown. The conclusions apply to the scope of this measurement — see the limitations of the method.
fc9827dc1ce2fa361b11e13491a3edc7e118082362329d5fb8dca3772bf22f5a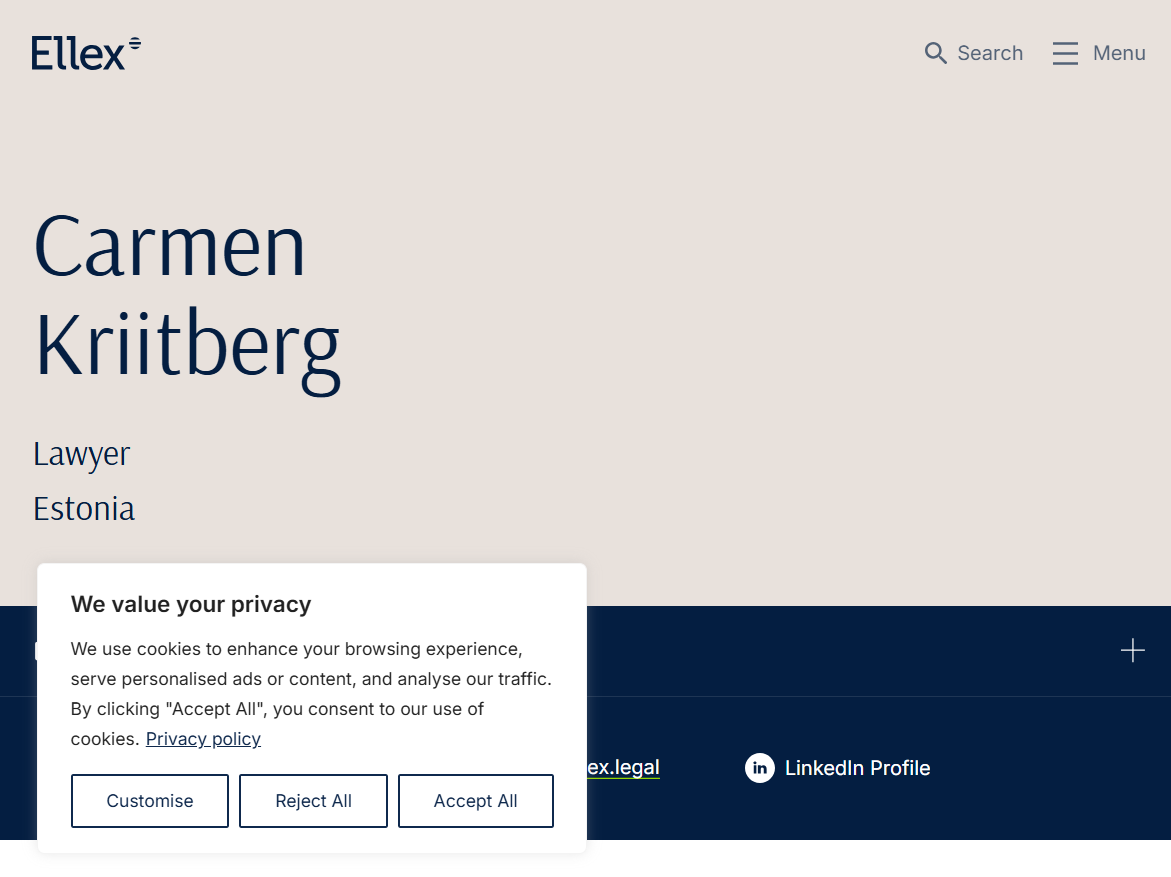
Want a response from the company about this audit? → Open the tool
Fill in once — it will be inserted into every letter below:
All fields are required to print the document — this is a formal requirement of the letter itself (the particulars of an official submission), not data collection: nothing is sent or saved anywhere, it all stays in your browser and disappears when you close the page. See the methodology for details.
RIA DigiDoc — phone · Smart-ID / Mobile-ID
Send this letter directly to the company first — before contacting the regulator it has the right to respond (GDPR Art. 12(3) — 30 days).
Тема: Запрос доступа к персональным данным (ст. 15 GDPR) — ellex.legal

Кому: [укажите адрес компании — DPO / поддержка / юридический отдел]
От: [Ваше имя], [контактный email]

Прошу предоставить доступ к моим персональным данным, обрабатываемым в связи с использованием сайта ellex.legal.

1. Категории данных и цели обработки (ст. 15(1)(a)-(c))
На основании независимого технического анализа сайта прошу подтвердить и подробно раскрыть следующие категории обработки:

1) Баннер CookieYes предлагает равнозначные «Customise», «Reject All» и «Accept All», аналитика и реклама выключены. Тег Google (GT-WRDDK49) работает в расширенном режиме Consent Mode: первый page_view в Google Analytics 4 уходит на +1204 мс со статусом gcs=G100 (аналитика и реклама запрещены), до какого-либо выбора. CookieYes дважды записывает решение (+68093 и +257081 мс), статус после этого остаётся «запрещено», что согласуется с отказом. Тем не менее на каждой следующей странице — главная, вакансии, политика конфиденциальности — в Google уходят page_view и scroll (+83199, +90071, +106853, +120446, +132093, +270220 мс) с адресом страницы и сведениями об устройстве. Согласно Руководству EDPB 2/2023 о техническом охвате ст. 5(3), считывание таких сведений с устройства скриптом требует согласия и без использования cookie.

2) При статусе «запрещено» cookie Google Analytics не сохраняются, однако тег Google добавляет ко всем внутренним ссылкам параметр _gl, в котором закодирован идентификатор клиента: _ga*NTI0MjkxMjY2LjE3OTAyODc4MTQ декодируется в 524291266.1790287814. Следующая страница считывает идентификатор из адреса, поэтому все восемь обращений в Google Analytics за 270 секунд — на пяти страницах и после обоих решений в баннере — несут один и тот же идентификатор клиента, а признак первого визита выставлен только на первой странице. Идентификатор создан в 22:10:14 UTC, через 1,5 секунды после начала записи. Таким образом, отказ от cookie не разрывает связывание просмотров одного посетителя: идентичность переносится в адресе страницы и в составе адреса передаётся в Google Analytics.

3) Политика Ellex Circle сообщает, что персональные данные раскрываются третьим лицам только когда этого требует применимый закон; её раздел о cookie описывает cookie прежнего баннера gotoandplay_cookie_agreement и cookie Google Analytics _ga, _gid, _gat и не упоминает ни CookieYes, ни режим согласия Google, ни параметр _gl. Декларация CookieYes обещает сохранять аналитические cookie только с предварительного согласия и описывает _ga как хранящую информацию «анонимно». Фактически сведения о просмотре со стабильным идентификатором уходят в Google без согласия. reCAPTCHA в политике не названа.


2. Получатели, сроки хранения и передача за пределы ЕЭЗ (ст. 15(1)(c)-(d), 46)
Прошу также указать полный список третьих лиц-получателей, применимые сроки хранения по каждой категории и правовые основания передачи данных за пределы ЕЭЗ, если таковая происходит. Полный технический разбор с доказательствами (сохранённый сетевой журнал, контрольная сумма SHA-256) опубликован по адресу: https://gdpru.eu/en/audits/ee-ellex-legal/

3. Автоматизированная обработка и профилирование (ст. 15(1)(h))
Прошу сообщить, применяется ли в отношении меня автоматизированное принятие решений или профилирование, и если да — раскрыть логику такой обработки.

С уважением,

[Ваше имя]
[контактный email]
[Страна]


[Дата]
Subject: Data access request (GDPR Art. 15) — ellex.legal

To: [insert the company's address — DPO / support / legal department]
From: [Your name], [contact email]

I request access to my personal data processed in connection with the website ellex.legal.

1. Categories of data and purposes of processing (Art. 15(1)(a)-(c))
Based on an independent technical analysis of the site, I request confirmation and detailed disclosure of the following categories of processing:

1) The CookieYes banner offers equal-weight 'Customise', 'Reject All' and 'Accept All', with analytics and advertising off. The Google tag (GT-WRDDK49) runs in Consent Mode's advanced mode: the first page_view to Google Analytics 4 goes out at +1204 ms with the status gcs=G100 (analytics and advertising denied), before any choice. CookieYes records a decision twice (+68093 and +257081 ms), and the status remains 'denied' afterwards, which is consistent with a refusal. Nonetheless on every subsequent page — the home page, careers, the privacy policy — page_view and scroll events go to Google (+83199, +90071, +106853, +120446, +132093, +270220 ms) with the page address and device information. Under EDPB Guidelines 2/2023 on the technical scope of Art. 5(3), reading such information from the device by script requires consent even without the use of cookies.

2) In the 'denied' state Google Analytics cookies are not stored; however, the Google tag appends to all internal links a _gl parameter in which the client identifier is encoded: _ga*NTI0MjkxMjY2LjE3OTAyODc4MTQ decodes to 524291266.1790287814. The next page reads the identifier from the address, so all eight Google Analytics requests over 270 seconds — across five pages and after both decisions in the banner — carry one and the same client identifier, with the first-visit flag set only on the first page. The identifier was created at 22:10:14 UTC, 1.5 seconds after the start of the recording. Thus refusing cookies does not break the linking of one visitor's page views: the identity is carried in the page address and, as part of that address, transmitted to Google Analytics.

3) The Ellex Circle policy states that personal data is disclosed to third parties only when required under applicable law; its cookie section describes the cookie of a former banner, gotoandplay_cookie_agreement, and the Google Analytics cookies _ga, _gid, _gat, and mentions neither CookieYes, nor Google's consent mode, nor the _gl parameter. The CookieYes declaration promises to store analytics cookies only with prior consent and describes _ga as storing information 'anonymously'. In fact browsing information with a stable identifier goes to Google without consent. reCAPTCHA is not named in the policy.


2. Recipients, retention periods, and transfers outside the EEA (Art. 15(1)(c)-(d), 46)
I also request the full list of third-party recipients, the applicable retention period for each category, and the legal basis for any transfer of data outside the EEA. The full technical audit with evidence (saved network log, SHA-256 checksum) is published at: https://gdpru.eu/en/audits/ee-ellex-legal/

3. Automated processing and profiling (Art. 15(1)(h))
Please state whether I am subject to automated decision-making or profiling, and if so, disclose the logic involved.

Sincerely,

[Your name]
[contact email]
[Country]


[Date]
Teema: Isikuandmetele juurdepääsu taotlus (IKÜM art 15) — ellex.legal

Kellele: [märkige ettevõtte aadress — DPO / tugi / juriidiline osakond]
Kellelt: [Teie nimi], [kontakt-e-post]

Palun anda mulle juurdepääs minu isikuandmetele, mida töödeldakse seoses veebisaidi ellex.legal kasutamisega.

1. Andmekategooriad ja töötlemise eesmärgid (IKÜM art 15(1)(a)-(c))
Sõltumatu tehnilise analüüsi põhjal palun kinnitada ja üksikasjalikult avaldada järgmised töötlemiskategooriad:

1) CookieYes bänner pakub võrdväärseid nuppe «Customise», «Reject All» ja «Accept All», analüütika ja reklaam on vaikimisi välja lülitatud. Google'i silt (GT-WRDDK49) töötab laiendatud Consent Mode režiimis: esimene page_view Google Analytics 4-s saadetakse +1204 ms juures staatusega gcs=G100 (analüütika ja reklaam keelatud), enne mistahes valikut. CookieYes salvestab otsuse kahel korral (+68093 ja +257081 ms), staatus jääb pärast seda «keelatud», mis on kooskõlas keeldumisega. Sellegipoolest saadetakse igal järgneval lehel — avaleht, töökohad, privaatsuspoliitika — Google'ile page_view ja scroll (+83199, +90071, +106853, +120446, +132093, +270220 ms) koos lehe aadressi ja seadme andmetega. EDPB juhendi 2/2023 kohaselt, mis käsitleb art 5(3) tehnilist ulatust, vajab selliste seadmeandmete lugemine skripti kaudu nõusolekut ka küpsiseid kasutamata.

2) Staatuse «keelatud» juures Google Analyticsi küpsiseid ei salvestata, kuid Google'i silt lisab kõigile sisemistele linkidele parameetri _gl, millesse on kodeeritud kliendi tuvastaja: _ga*NTI0MjkxMjY2LjE3OTAyODc4MTQ dekodeerub 524291266.1790287814-ks. Järgmine leht loeb tuvastaja aadressist, mistõttu kõik kaheksa Google Analyticsi päringut 270 sekundi jooksul — viiel lehel ja pärast mõlemat bänneri otsust — kannavad sama kliendi tuvastajat, ja esimese külastuse märge on seatud vaid esimesel lehel. Tuvastaja loodi kell 22:10:14 UTC, 1,5 sekundit pärast salvestuse algust. Seega küpsistest keeldumine ei katkesta ühe külastaja vaatamiste seostamist: identiteet kantakse edasi lehe aadressis ja edastatakse aadressi koosseisus Google Analyticsile.

3) Ellex Circle'i poliitika teatab, et isikuandmeid avaldatakse kolmandatele isikutele ainult kohaldatava seaduse nõudmisel; selle küpsiste jaotis kirjeldab varasema bänneri küpsist gotoandplay_cookie_agreement ja Google Analyticsi küpsiseid _ga, _gid, _gat, ega maini ei CookieYes'i, Google'i nõusolekurežiimi ega parameetrit _gl. CookieYes'i deklaratsioon lubab salvestada analüütilisi küpsiseid vaid eelneva nõusoleku alusel ja kirjeldab _ga't kui «anonüümselt» säilitavat. Tegelikult saadetakse stabiilse tuvastajaga vaatamisandmed Google'ile nõusolekuta. reCAPTCHA-t poliitikas ei mainita.


2. Vastuvõtjad, säilitustähtajad ja edastamine väljapoole EMP-d (IKÜM art 15(1)(c)-(d), 46)
Palun samuti esitada täielik loetelu kolmandatest isikutest vastuvõtjatest, iga kategooria puhul kohaldatavad säilitustähtajad ning andmete EMP-välisele edastamisele kohaldatav õiguslik alus, kui selline edastamine toimub. Täielik tehniline analüüs koos tõenditega (salvestatud võrgulogi, SHA-256 kontrollsumma) on avaldatud aadressil: https://gdpru.eu/en/audits/ee-ellex-legal/

3. Automatiseeritud töötlemine ja profiilianalüüs (IKÜM art 15(1)(h))
Palun teatada, kas minu suhtes kohaldatakse automatiseeritud otsuste tegemist või profiilianalüüsi, ning kui jah, siis avaldada selle loogika.

Lugupidamisega,

[Teie nimi]
[kontakt-e-post]
[Riik]


[Kuupäev]
RIA DigiDoc — phone · Smart-ID / Mobile-ID
Where to file: Estonian Data Protection Inspectorate (AKI) — write to info@aki.ee
Important: AKI only handles submissions in Estonian. Translate the letter before sending.
The regulator reviews complaints in its national language. There is an officially translated template from the European Data Protection Board (EDPB) — you can use it instead of or alongside this letter: Official EDPB complaint form (PDF, your language)
Тема: Жалоба на обработку персональных данных — ellex.legal

1. Предмет жалобы
Я подаю жалобу в отношении обработки моих персональных данных сайтом ellex.legal.

2. Обстоятельства
Я посетил сайт ellex.legal и обнаружил признаки несоответствия обработки моих персональных данных требованиям GDPR. Технический разбор, опубликованный на gdpru.eu 25.09.2026 (открытая методология, воспроизводимые измерения), документирует следующие признаки:

1) Баннер CookieYes предлагает равнозначные «Customise», «Reject All» и «Accept All», аналитика и реклама выключены. Тег Google (GT-WRDDK49) работает в расширенном режиме Consent Mode: первый page_view в Google Analytics 4 уходит на +1204 мс со статусом gcs=G100 (аналитика и реклама запрещены), до какого-либо выбора. CookieYes дважды записывает решение (+68093 и +257081 мс), статус после этого остаётся «запрещено», что согласуется с отказом. Тем не менее на каждой следующей странице — главная, вакансии, политика конфиденциальности — в Google уходят page_view и scroll (+83199, +90071, +106853, +120446, +132093, +270220 мс) с адресом страницы и сведениями об устройстве. Согласно Руководству EDPB 2/2023 о техническом охвате ст. 5(3), считывание таких сведений с устройства скриптом требует согласия и без использования cookie.

2) При статусе «запрещено» cookie Google Analytics не сохраняются, однако тег Google добавляет ко всем внутренним ссылкам параметр _gl, в котором закодирован идентификатор клиента: _ga*NTI0MjkxMjY2LjE3OTAyODc4MTQ декодируется в 524291266.1790287814. Следующая страница считывает идентификатор из адреса, поэтому все восемь обращений в Google Analytics за 270 секунд — на пяти страницах и после обоих решений в баннере — несут один и тот же идентификатор клиента, а признак первого визита выставлен только на первой странице. Идентификатор создан в 22:10:14 UTC, через 1,5 секунды после начала записи. Таким образом, отказ от cookie не разрывает связывание просмотров одного посетителя: идентичность переносится в адресе страницы и в составе адреса передаётся в Google Analytics.

3) Политика Ellex Circle сообщает, что персональные данные раскрываются третьим лицам только когда этого требует применимый закон; её раздел о cookie описывает cookie прежнего баннера gotoandplay_cookie_agreement и cookie Google Analytics _ga, _gid, _gat и не упоминает ни CookieYes, ни режим согласия Google, ни параметр _gl. Декларация CookieYes обещает сохранять аналитические cookie только с предварительного согласия и описывает _ga как хранящую информацию «анонимно». Фактически сведения о просмотре со стабильным идентификатором уходят в Google без согласия. reCAPTCHA в политике не названа.

Полная техническая документация опубликована по адресу: https://gdpru.eu/en/audits/ee-ellex-legal/

3. Положения GDPR, соблюдение которых прошу проверить
ePrivacy — Директива 2002/58/EC, ст. 5(3) (в связке с GDPR Art. 6(1)(a)) — передача при статусе «запрещено»; ePrivacy — Директива 2002/58/EC, ст. 5(3); GDPR Art. 5(1)(c), Art. 6(1) — идентификатор посетителя через адрес ссылок; GDPR Art. 5(1)(a), Art. 13(1)(e) — прозрачность: заявленное расходится с фактическим

4. Требование
Прошу проверить изложенные обстоятельства и, если несоответствие подтвердится, принять меры, предусмотренные статьёй 58(2) GDPR.

5. Приложения
Полная доказательная база — HAR-файл, контрольная сумма SHA-256 и цитата из политики конфиденциальности сайта, документирующая указанное противоречие — опубликована и проверяема по ссылке в пункте 2 выше.

С уважением,

[Ваше имя]
[контактный email]
[Страна]


[Дата]
Subject: Complaint regarding personal data processing — ellex.legal

1. Subject of the complaint
I am filing a complaint regarding the processing of my personal data by the website ellex.legal.

2. Circumstances
I visited the website ellex.legal and found indications that the processing of my personal data does not comply with the GDPR. The technical analysis published on gdpru.eu on 25 September 2026 (open methodology, reproducible measurements) documents the following indications:

1) The CookieYes banner offers equal-weight 'Customise', 'Reject All' and 'Accept All', with analytics and advertising off. The Google tag (GT-WRDDK49) runs in Consent Mode's advanced mode: the first page_view to Google Analytics 4 goes out at +1204 ms with the status gcs=G100 (analytics and advertising denied), before any choice. CookieYes records a decision twice (+68093 and +257081 ms), and the status remains 'denied' afterwards, which is consistent with a refusal. Nonetheless on every subsequent page — the home page, careers, the privacy policy — page_view and scroll events go to Google (+83199, +90071, +106853, +120446, +132093, +270220 ms) with the page address and device information. Under EDPB Guidelines 2/2023 on the technical scope of Art. 5(3), reading such information from the device by script requires consent even without the use of cookies.

2) In the 'denied' state Google Analytics cookies are not stored; however, the Google tag appends to all internal links a _gl parameter in which the client identifier is encoded: _ga*NTI0MjkxMjY2LjE3OTAyODc4MTQ decodes to 524291266.1790287814. The next page reads the identifier from the address, so all eight Google Analytics requests over 270 seconds — across five pages and after both decisions in the banner — carry one and the same client identifier, with the first-visit flag set only on the first page. The identifier was created at 22:10:14 UTC, 1.5 seconds after the start of the recording. Thus refusing cookies does not break the linking of one visitor's page views: the identity is carried in the page address and, as part of that address, transmitted to Google Analytics.

3) The Ellex Circle policy states that personal data is disclosed to third parties only when required under applicable law; its cookie section describes the cookie of a former banner, gotoandplay_cookie_agreement, and the Google Analytics cookies _ga, _gid, _gat, and mentions neither CookieYes, nor Google's consent mode, nor the _gl parameter. The CookieYes declaration promises to store analytics cookies only with prior consent and describes _ga as storing information 'anonymously'. In fact browsing information with a stable identifier goes to Google without consent. reCAPTCHA is not named in the policy.

Full technical documentation is published at: https://gdpru.eu/en/audits/ee-ellex-legal/

3. GDPR provisions I ask you to examine
ePrivacy — Directive 2002/58/EC, Art. 5(3) (in conjunction with GDPR Art. 6(1)(a)) — transmission in the 'denied' state; ePrivacy — Directive 2002/58/EC, Art. 5(3); GDPR Art. 5(1)(c), Art. 6(1) — a visitor identifier carried in link addresses; GDPR Art. 5(1)(a), Art. 13(1)(e) — transparency: the declared diverges from the actual

4. Request
I request that you examine the circumstances described and, if non-compliance is confirmed, apply the measures provided for in Article 58(2) GDPR.

5. Attachments
The full evidence base — the HAR file, its SHA-256 checksum and the quotation from the site's privacy policy documenting the stated contradiction — is published and verifiable at the link in point 2 above.

Sincerely,

[Your name]
[contact email]
[Country]


[Date]
1. Kaebuse ese
Esitan kaebuse seoses minu isikuandmete töötlemisega veebisaidil ellex.legal.

2. Asjaolud
Külastasin veebisaiti ellex.legal ja tuvastasin märke sellest, et minu isikuandmete töötlemine ei vasta isikuandmete kaitse üldmääruse (IKÜM) nõuetele. Tehniline analüüs, mis on avaldatud aadressil gdpru.eu 25.09.2026 (avatud metoodika, korratavad mõõtmised), dokumenteerib järgmist:

1) CookieYes bänner pakub võrdväärseid nuppe «Customise», «Reject All» ja «Accept All», analüütika ja reklaam on vaikimisi välja lülitatud. Google'i silt (GT-WRDDK49) töötab laiendatud Consent Mode režiimis: esimene page_view Google Analytics 4-s saadetakse +1204 ms juures staatusega gcs=G100 (analüütika ja reklaam keelatud), enne mistahes valikut. CookieYes salvestab otsuse kahel korral (+68093 ja +257081 ms), staatus jääb pärast seda «keelatud», mis on kooskõlas keeldumisega. Sellegipoolest saadetakse igal järgneval lehel — avaleht, töökohad, privaatsuspoliitika — Google'ile page_view ja scroll (+83199, +90071, +106853, +120446, +132093, +270220 ms) koos lehe aadressi ja seadme andmetega. EDPB juhendi 2/2023 kohaselt, mis käsitleb art 5(3) tehnilist ulatust, vajab selliste seadmeandmete lugemine skripti kaudu nõusolekut ka küpsiseid kasutamata.

2) Staatuse «keelatud» juures Google Analyticsi küpsiseid ei salvestata, kuid Google'i silt lisab kõigile sisemistele linkidele parameetri _gl, millesse on kodeeritud kliendi tuvastaja: _ga*NTI0MjkxMjY2LjE3OTAyODc4MTQ dekodeerub 524291266.1790287814-ks. Järgmine leht loeb tuvastaja aadressist, mistõttu kõik kaheksa Google Analyticsi päringut 270 sekundi jooksul — viiel lehel ja pärast mõlemat bänneri otsust — kannavad sama kliendi tuvastajat, ja esimese külastuse märge on seatud vaid esimesel lehel. Tuvastaja loodi kell 22:10:14 UTC, 1,5 sekundit pärast salvestuse algust. Seega küpsistest keeldumine ei katkesta ühe külastaja vaatamiste seostamist: identiteet kantakse edasi lehe aadressis ja edastatakse aadressi koosseisus Google Analyticsile.

3) Ellex Circle'i poliitika teatab, et isikuandmeid avaldatakse kolmandatele isikutele ainult kohaldatava seaduse nõudmisel; selle küpsiste jaotis kirjeldab varasema bänneri küpsist gotoandplay_cookie_agreement ja Google Analyticsi küpsiseid _ga, _gid, _gat, ega maini ei CookieYes'i, Google'i nõusolekurežiimi ega parameetrit _gl. CookieYes'i deklaratsioon lubab salvestada analüütilisi küpsiseid vaid eelneva nõusoleku alusel ja kirjeldab _ga't kui «anonüümselt» säilitavat. Tegelikult saadetakse stabiilse tuvastajaga vaatamisandmed Google'ile nõusolekuta. reCAPTCHA-t poliitikas ei mainita.

Täielik tehniline dokumentatsioon on avaldatud aadressil: https://gdpru.eu/en/audits/ee-ellex-legal/

3. Sätted, mille järgimist palun kontrollida
ePrivacy direktiiv 2002/58/EU art 5(3) (koos IKÜM art 6(1)(a)-ga) — andmete edastamine keelatud staatuse juures; ePrivacy direktiiv 2002/58/EU art 5(3); IKÜM art 5(1)(c), art 6(1) — külastaja tuvastus lingi aadressi kaudu; IKÜM art 5(1)(a), art 13(1)(e) — läbipaistvus: väidetu erineb tegelikust

4. Nõue
Palun kontrollida kirjeldatud asjaolusid ja mittevastavuse kinnitamisel kohaldada IKÜM artikli 58 lõikes 2 ette nähtud meetmeid.

5. Lisad
Täielik tõendusmaterjal — HAR-fail, kontrollsumma SHA-256 ning veebisaidi privaatsuspoliitika tsitaat, mis dokumenteerib nimetatud vastuolu — on avaldatud ja kontrollitav punktis 2 viidatud lingil.

Lugupidamisega,

[Teie nimi]
[kontakt-e-post]
[Riik]


[Kuupäev]