
cinamonkino.com
Website of the CINAMON cinema chain — one recording, the Kosmos cinema in Tallinn, 290 requests, twenty-three nodes. There is no consent mechanism at all: no banner, no consent platform, and the page itself is marked with the attribute data-consent=0. Within the first two-odd seconds, without any choice, Microsoft Clarity with session recording, the Snapchat Pixel with cookie matching, Bing identifier synchronisation, the Facebook Pixel and SDK with a login-status check, Google Analytics in two versions and Google Ads remarketing all start. The session recording captures page content — including the privacy-policy page. The policy names no recipient at all and states that data is not sold to third parties. The browser did not send a DNT header.
Request timeline
Declared versus actual
Transfer timings
Facebook Pixel fbevents.js, then the SDK of app 1060196564143970.
Microsoft Clarity, tag 3wicrgzcgg.
ads/ga-audiences, property G-07ZEM5025W.
cm/i — matching iframe, pixel 359032b5-e110-43b6-9a30-6872cf05463a.
x/oauth/status, client_id 1060196564143970.
collect — 67,183 bytes, a page snapshot.
c.gif — Microsoft Bing Ads.
Detected trackers
Show data recipients (13)
- Microsoft Clarity (www.clarity.ms, tag 3wicrgzcgg; scripts.clarity.ms, h.clarity.ms/collect, c.clarity.ms) — session recording: a page snapshot and its changes, 58 transmissions
- Microsoft Bing Ads (c.bing.com/c.gif) — identifier synchronisation triggered by Clarity
- Snapchat Pixel (359032b5-e110-43b6-9a30-6872cf05463a) via sc-static.net, tr.snapchat.com, tr6.snapchat.com — PAGE_VIEW, engagement events and a cookie-matching iframe (tr.snapchat.com/cm/i)
- Meta — Facebook Pixel (connect.facebook.net/fbevents.js; no /tr events in the recording) and the Facebook JavaScript SDK (app 1060196564143970) with a login-status check www.facebook.com/x/oauth/status
- Google Analytics 4 (G-07ZEM5025W) via region1.analytics.google.com and www.google-analytics.com/j/collect — page_view, scroll
- Universal Analytics (UA-109852361-1) via www.google-analytics.com — Google's legacy counter
- Google Ads / DoubleClick (stats.g.doubleclick.net, www.google.ee/ads/ga-audiences) — the Google Ads link and remarketing audiences
- Google Tag Manager (www.googletagmanager.com, container GTM-K5RCC8R) — tag container
- Movio (cdn-cinema-ui-assets-prod.movio.co/webtracker) — web tracker of a marketing platform for cinemas; the script loads, no transmissions in the recording
- Adobe Fonts (use.typekit.net, p.typekit.net/p.gif) — web fonts and a page-view counter for licensing
- Google Fonts (fonts.googleapis.com, fonts.gstatic.com) — the Geist font
- YouTube (www.youtube.com/iframe_api) — embedded-video API
- Cloudflare Insights (static.cloudflareinsights.com) — web analytics of the delivery provider
Indicators of GDPR non-compliance
- ePrivacy — Directive 2002/58/EC, Art. 5(3) (in conjunction with GDPR Art. 6(1)(a))There is no consent mechanism on the site: no cookie banner, no consent-management platform, and the page's root element carries the attribute data-consent=0. Nonetheless, within the first 2.3 seconds the following load and begin transmitting: the Facebook Pixel (+515 ms), Google Tag Manager GTM-K5RCC8R (+517 ms), Microsoft Clarity (+851 ms), Universal Analytics and Google Analytics 4 (+1466…+1638 ms), the Google Ads link and remarketing audiences (+1640…+1641 ms), the Snapchat Pixel with a PAGE_VIEW event (+1751 ms) and cookie matching (+1756 ms), the Facebook login-status check (+1792 ms), Clarity session recording (+1922 ms) and Bing identifier synchronisation (+2233 ms). Google's consent mode is not configured: gcd=13l3l3l2l1l1 ('not set'), and the gcs parameter is absent.
- GDPR Art. 6(1), Art. 5(1)(c) — session recording without a legal basisFrom +1922 ms Microsoft Clarity records the session: the first transmission to h.clarity.ms/collect weighs 67,183 bytes (a page snapshot), followed by 57 increments. The surviving bodies show that Clarity serialises the structure and text of the pages — titles, link labels and the root element <HTML data-consent=0>; the privacy-policy page is recorded too. Recording the visitor's behaviour on the site without consent has no legal basis and goes beyond what is necessary for the declared 'statistics'.
- GDPR Art. 6(1), Art. 5(1)(b) — advertising identifier matchingThree separate advertising-identifier matching mechanisms run without consent: Snapchat's tr.snapchat.com/cm/i iframe (+1756 ms and +45426 ms), Microsoft's c.bing.com/c.gif synchronisation (+2233 ms) and the passing of the visitor into Google Ads remarketing audiences (www.google.ee/ads/ga-audiences, three times) with a single client identifier created one and a half seconds after the start of the session. The Facebook JavaScript SDK calls www.facebook.com/x/oauth/status, which allows Meta to link the visit to a Facebook account. The policy declares no advertising purposes at all.
- GDPR Art. 5(1)(a), Art. 13(1)(a), (c), (e), (f), Art. 44 — transparency and disclosureThe policy names 'CINAMON Group' as the controller without a registration code or address, describes cookies as needed 'for the operation of the site and statistics' and 'remembering preferences', suggests managing them in the browser, and states: 'we do not sell your data to third parties'. Not a single recipient is named — not Microsoft (Clarity, Bing), Snap, Meta, Google, Movio or Adobe; legal bases per purpose are not stated; nothing is said about transfers to third countries (Snap Inc., Meta Platforms — USA).
Context
cinamonkino.com is the website of the CINAMON cinema chain, with cinemas in Kaunas (MEGA), Tallinn (Kosmos) and Liepāja (BALLE); tickets are sold here and the CINAMON KEY loyalty programme runs here. The controller per the policy is ‘CINAMON Group’, with no registration code or address stated; the contact is kosmos@cinamonkino.com. The site is built on Nuxt and served via Cloudflare.
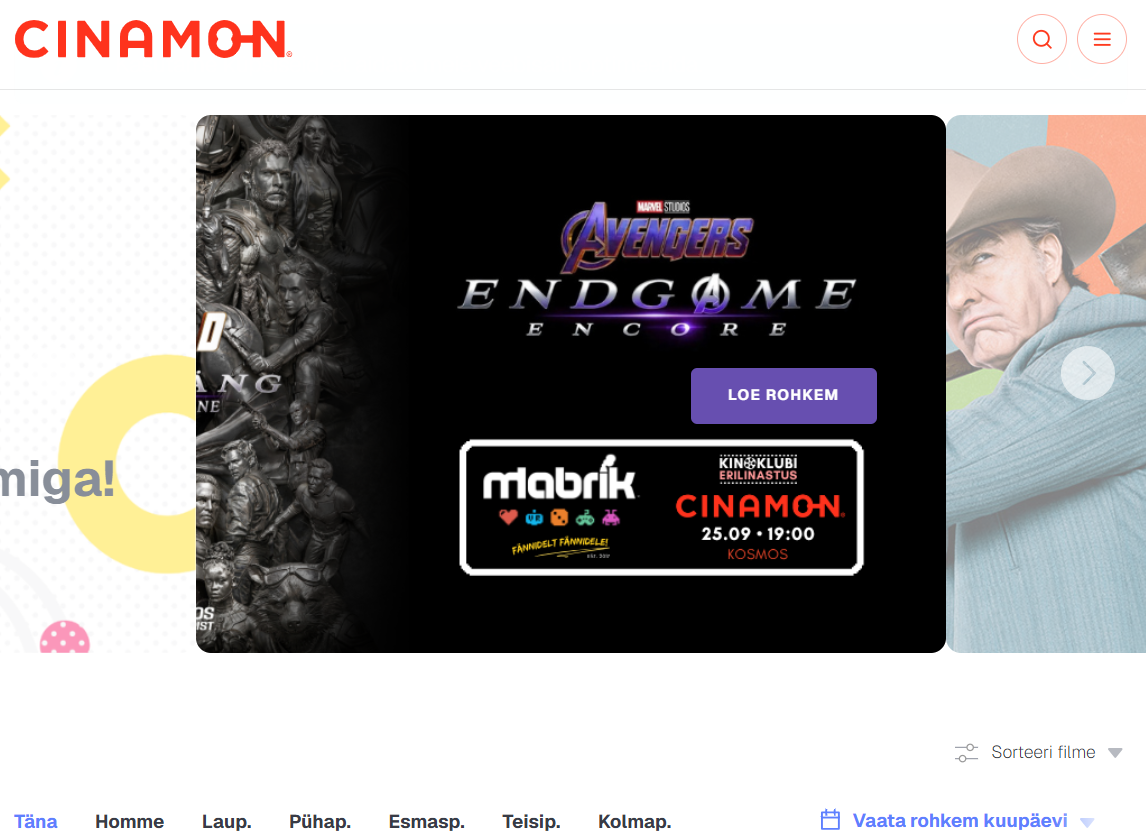
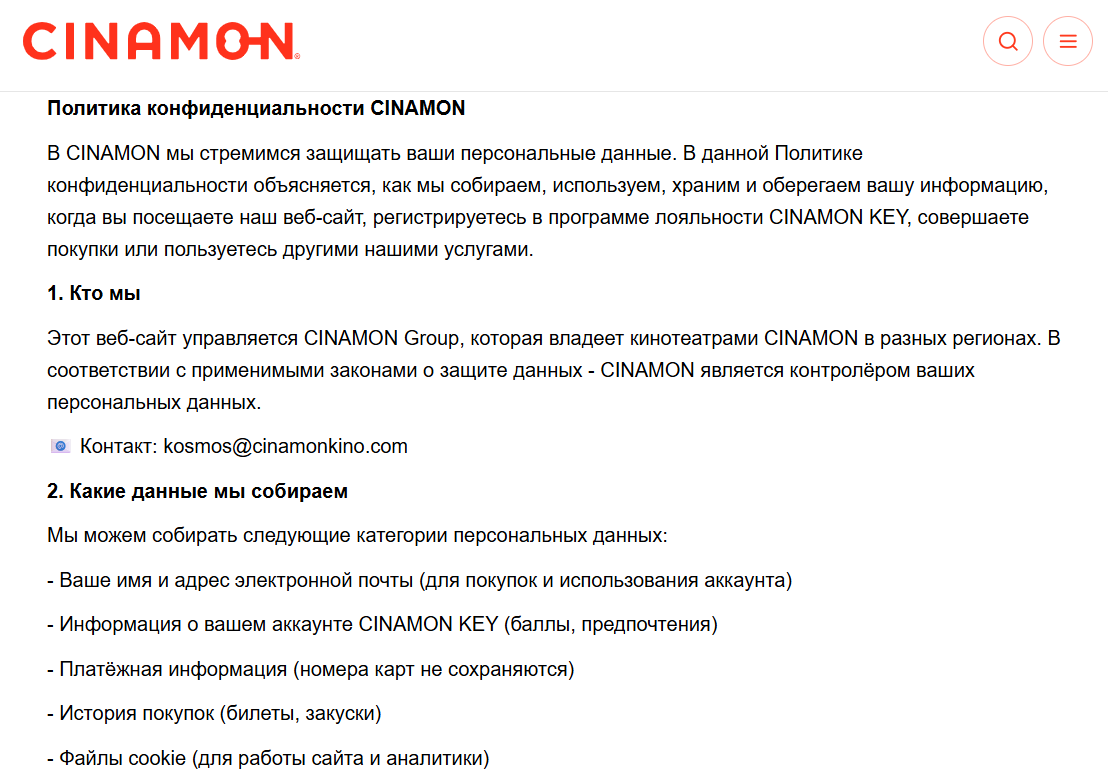
Processing is described by the ‘CINAMON kino privaatsuspoliitika’ — a short document of eight sections. Attached to the material are screenshots of the start page, the Kosmos cinema home page and the privacy policy.
The measurement consists of one recording lasting about four minutes: the start page, then the Kosmos cinema pages — the home page, the privacy policy and the terms in Estonian and Russian. Two hundred and ninety requests, twenty-three nodes. The recording was made on 24 September 2026.
Who data goes to directly
Microsoft (Clarity, Bing Ads), Snap (Snapchat Pixel), Meta (Facebook Pixel and SDK), Google (Analytics 4, Universal Analytics, Ads, Tag Manager, Fonts, YouTube), Adobe (Fonts), Cloudflare (Insights); the Movio script loads with no transmissions in the recording.
Declared versus actual
The policy states that cookies are needed ‘for the operation of the site and statistics’ and to ‘remember preferences’, that they can be managed in the browser, and promises plainly: ‘we do not sell your data to third parties’. Advertising purposes, session recording and specific recipients are not mentioned.
The measurement shows something quite different.
There is no consent mechanism, and the page records this itself. Neither a cookie banner nor a consent-management platform appears in the recording — the screenshots of the start page and the Kosmos home page confirm it. The page’s root element carries the attribute data-consent=0: the site itself marks that consent has not been obtained. Google’s consent mode is not configured (gcd=13l3l3l2l1l1, gcs absent).
Everything starts within the first two seconds. From the markup and the site’s own scripts, the Facebook Pixel (+515 ms, the pixel.js script), Google Tag Manager GTM-K5RCC8R (+517 ms), Microsoft Clarity (+851 ms) and the Facebook SDK (+853 ms) load. By +2233 ms the following have gone out: Universal Analytics UA-109852361-1 and Google Analytics 4 G-07ZEM5025W pageviews, a request to the Google Ads link, a Google Ads remarketing-audiences request, a Snapchat Pixel PAGE_VIEW event, the Snapchat cookie-matching iframe, the Facebook login-status check, the first Clarity session-recording transmission and Bing identifier synchronisation. All Google requests carry a single client identifier created at 20:30:07 UTC — one and a half seconds after the start of the session.
Session recording captures page content. Microsoft Clarity sends 58 packets to h.clarity.ms/collect; the first is 67,183 bytes — a snapshot of the whole page. Most bodies are redacted in the published file, but three survived, and they show that Clarity serialises page titles (‘CINAMON Kosmos | Privaatsuspoliitika’, ‘CINAMON Kosmos | Tingimused ja reeglid’), link texts and the root element itself, <HTML lang=ru data-consent=0>. Recording continues on the privacy-policy page as well.
Three advertising identifier-matching mechanisms. Snapchat opens a tr.snapchat.com/cm/i iframe for cookie matching (twice), Clarity triggers Microsoft Bing Ads identifier synchronisation (c.bing.com/c.gif), and Google passes the visitor into remarketing audiences three times. The Facebook SDK calls www.facebook.com/x/oauth/status, which allows Meta to link the visit to a Facebook account. Over the session Snapchat sends 32 requests with events.
Recipients are not disclosed. Neither Microsoft, nor Snap, nor Meta, nor Google, nor Movio, nor Adobe is named in the policy; nothing is said about transfers of data to the USA. The statement ‘we do not sell your data to third parties’ does not change the fact that browsing data and identifiers are transmitted to six advertising and analytics companies without consent and without disclosure.
Other nodes: the Movio web tracker (a marketing platform for cinemas) loads but makes no transmissions in the recording; Adobe Fonts (use.typekit.net) serves fonts and sends a page-view counter p.typekit.net/p.gif; Google Fonts, YouTube iframe_api and Cloudflare Insights load from the markup.
Consent: what is proven and what is not
Proven: there is no consent mechanism. No banner, no consent platform; the page is marked data-consent=0.
Proven: advertising, analytics and session recording operate without consent. By the identifiers GTM-K5RCC8R, G-07ZEM5025W, UA-109852361-1, the Clarity tag 3wicrgzcgg, the Snapchat pixel 359032b5-e110-43b6-9a30-6872cf05463a, and the Facebook app 1060196564143970.
Proven: the session recording contains the structure and text of pages. By the surviving bodies of the Clarity transmissions.
Proven: advertising identifier matching takes place. By the requests tr.snapchat.com/cm/i, c.bing.com/c.gif, google.ee/ads/ga-audiences.
Not proven and not asserted: sending of Facebook Pixel events. The pixel script is loaded, but there are no /tr requests in the recording; transmission to Meta in the recording is limited to loading the SDK and the login-status check.
Not proven and not asserted: transmission of data to Movio. The web-tracker script is loaded, but there are no transmissions in the recording.
Separately: the browser did not send a DNT header in this recording.
Bounds of observation
The measurement covers the start page and the Kosmos cinema pages; no tickets were purchased and no account login was performed. Observation captures the browser’s behaviour, not the internal side of the services. The legal assessment is made by the competent authority — in Estonia, Andmekaitse Inspektsioon.
The file is published redacted under a “lean” profile: cookie values in requests have been removed, the Cookie and Set-Cookie headers stripped; the redaction registry records 278 redactions and a checksum. Most bodies of the Clarity and Snapchat transmissions are redacted; their sizes and timings are fully legible, and three Clarity bodies survived and are quoted above. The domain’s Content-Security-Policy header contains the internal IP address 10.223.240.54 — this does not concern the protection of visitors’ data, but it discloses information about internal infrastructure.
The identification of services relies on domains and address patterns: Clarity — by clarity.ms and the tag; Bing — by c.bing.com; Snapchat — by snapchat.com, sc-static.net and the pixel identifier; Meta — by connect.facebook.net, facebook.com and client_id; Google — by google-analytics.com, analytics.google.com, doubleclick.net, google.ee/ads/ga-audiences and the property identifiers; Movio — by movio.co; Adobe — by typekit.net. The gcd values are interpreted according to Google’s documentation on consent-mode parameters.
Conclusion
The CINAMON cinema chain’s website has no consent mechanism at all — the page itself marks itself with the attribute data-consent=0 — and yet within the first two-odd seconds it launches Microsoft Clarity with session recording, the Snapchat Pixel with cookie matching, Bing identifier synchronisation, the Facebook Pixel and SDK with a login-status check, Google Analytics in two versions and Google Ads remarketing. The session recording captures the structure and text of pages, including the privacy-policy page; the visitor is passed into advertising audiences and matched against the identifiers of three advertising platforms. The policy describes cookies as needed ‘for the operation of the site and statistics’, names no recipient at all, gives no controller details or legal bases, and promises that data is not sold to third parties.
Remediation: introduce a consent-management platform with an equal-weight reject button and prior blocking, so that Microsoft Clarity, the Snapchat Pixel, the Facebook Pixel and SDK, Google Analytics, Google Ads and Bing neither load nor transmit data before explicit consent; connect Google’s consent mode; abandon session recording or restrict it strictly to consent with content masking; disable the legacy Universal Analytics; rewrite the policy — state the controller’s registration code and address, name all recipients, the purposes including advertising, session recording and identifier matching, the legal bases, retention periods and transfers to third countries; remove the internal IP address from the Content-Security-Policy header and add proper directives to it.
How to verify: download the file and compute its checksum — sha256sum file.har (Linux, macOS) or certutil -hashfile file.har SHA256 (Windows); it must match the one shown. The conclusions apply to the scope of this measurement — see the limitations of the method.
9699a75f03adf221ddadc9f52a2dfbf1cbcc8e99deecbeb8a1a53ecf29fe768b
Want a response from the company about this audit? → Open the tool
Fill in once — it will be inserted into every letter below:
All fields are required to print the document — this is a formal requirement of the letter itself (the particulars of an official submission), not data collection: nothing is sent or saved anywhere, it all stays in your browser and disappears when you close the page. See the methodology for details.
RIA DigiDoc — phone · Smart-ID / Mobile-ID
Send this letter directly to the company first — before contacting the regulator it has the right to respond (GDPR Art. 12(3) — 30 days).
Тема: Запрос доступа к персональным данным (ст. 15 GDPR) — cinamonkino.com

Кому: [укажите адрес компании — DPO / поддержка / юридический отдел]
От: [Ваше имя], [контактный email]

Прошу предоставить доступ к моим персональным данным, обрабатываемым в связи с использованием сайта cinamonkino.com.

1. Категории данных и цели обработки (ст. 15(1)(a)-(c))
На основании независимого технического анализа сайта прошу подтвердить и подробно раскрыть следующие категории обработки:

1) Механизма согласия на сайте нет: ни cookie-баннера, ни платформы управления согласием, а корневой элемент страницы помечен атрибутом data-consent=0. Несмотря на это, за первые 2,3 секунды загружаются и начинают передачу: Facebook Pixel (+515 мс), Google Tag Manager GTM-K5RCC8R (+517 мс), Microsoft Clarity (+851 мс), Universal Analytics и Google Analytics 4 (+1466…+1638 мс), связка Google Ads и ремаркетинг-аудитории (+1640…+1641 мс), Snapchat Pixel с событием PAGE_VIEW (+1751 мс) и сопоставлением cookie (+1756 мс), проверка статуса входа Facebook (+1792 мс), запись сеанса Clarity (+1922 мс) и синхронизация идентификатора Bing (+2233 мс). Режим согласия Google не настроен: gcd=13l3l3l2l1l1 («не задано»), параметр gcs отсутствует.

2) Microsoft Clarity с +1922 мс записывает сеанс: первая отправка на h.clarity.ms/collect весит 67 183 байта (снимок страницы), далее следуют 57 инкрементов. В уцелевших телах видно, что Clarity сериализует структуру и тексты страниц — заголовки, подписи ссылок и корневой элемент <HTML data-consent=0>; в запись попадает в том числе страница политики конфиденциальности. Запись поведения посетителя на сайте без согласия не имеет правового основания и выходит за пределы необходимого для заявленной «статистики».

3) Без согласия выполняются три отдельных механизма сопоставления рекламных идентификаторов: iframe tr.snapchat.com/cm/i Snapchat (+1756 мс и +45426 мс), синхронизация c.bing.com/c.gif Microsoft (+2233 мс) и передача посетителя в ремаркетинг-аудитории Google Ads (www.google.ee/ads/ga-audiences, трижды) с единым идентификатором клиента, созданным через полторы секунды после начала сеанса. Facebook JavaScript SDK обращается к www.facebook.com/x/oauth/status, что позволяет Meta сопоставить визит с учётной записью Facebook. Политика рекламных целей не заявляет вовсе.

4) Политика называет контролёром «CINAMON Group» без регистрационного кода и адреса, описывает cookie как нужные «для работы сайта и статистики» и «запоминания предпочтений», предлагает управлять ими в браузере и заявляет: «мы не продаём ваши данные третьим лицам». Ни один получатель не назван — ни Microsoft (Clarity, Bing), ни Snap, ни Meta, ни Google, ни Movio, ни Adobe; правовые основания по целям не указаны; о передаче в третьи страны (Snap Inc., Meta Platforms — США) не сказано ничего.


2. Получатели, сроки хранения и передача за пределы ЕЭЗ (ст. 15(1)(c)-(d), 46)
Прошу также указать полный список третьих лиц-получателей, применимые сроки хранения по каждой категории и правовые основания передачи данных за пределы ЕЭЗ, если таковая происходит. Полный технический разбор с доказательствами (сохранённый сетевой журнал, контрольная сумма SHA-256) опубликован по адресу: https://gdpru.eu/en/audits/ee-cinamonkino-com/

3. Автоматизированная обработка и профилирование (ст. 15(1)(h))
Прошу сообщить, применяется ли в отношении меня автоматизированное принятие решений или профилирование, и если да — раскрыть логику такой обработки.

С уважением,

[Ваше имя]
[контактный email]
[Страна]


[Дата]
Subject: Data access request (GDPR Art. 15) — cinamonkino.com

To: [insert the company's address — DPO / support / legal department]
From: [Your name], [contact email]

I request access to my personal data processed in connection with the website cinamonkino.com.

1. Categories of data and purposes of processing (Art. 15(1)(a)-(c))
Based on an independent technical analysis of the site, I request confirmation and detailed disclosure of the following categories of processing:

1) There is no consent mechanism on the site: no cookie banner, no consent-management platform, and the page's root element carries the attribute data-consent=0. Nonetheless, within the first 2.3 seconds the following load and begin transmitting: the Facebook Pixel (+515 ms), Google Tag Manager GTM-K5RCC8R (+517 ms), Microsoft Clarity (+851 ms), Universal Analytics and Google Analytics 4 (+1466…+1638 ms), the Google Ads link and remarketing audiences (+1640…+1641 ms), the Snapchat Pixel with a PAGE_VIEW event (+1751 ms) and cookie matching (+1756 ms), the Facebook login-status check (+1792 ms), Clarity session recording (+1922 ms) and Bing identifier synchronisation (+2233 ms). Google's consent mode is not configured: gcd=13l3l3l2l1l1 ('not set'), and the gcs parameter is absent.

2) From +1922 ms Microsoft Clarity records the session: the first transmission to h.clarity.ms/collect weighs 67,183 bytes (a page snapshot), followed by 57 increments. The surviving bodies show that Clarity serialises the structure and text of the pages — titles, link labels and the root element <HTML data-consent=0>; the privacy-policy page is recorded too. Recording the visitor's behaviour on the site without consent has no legal basis and goes beyond what is necessary for the declared 'statistics'.

3) Three separate advertising-identifier matching mechanisms run without consent: Snapchat's tr.snapchat.com/cm/i iframe (+1756 ms and +45426 ms), Microsoft's c.bing.com/c.gif synchronisation (+2233 ms) and the passing of the visitor into Google Ads remarketing audiences (www.google.ee/ads/ga-audiences, three times) with a single client identifier created one and a half seconds after the start of the session. The Facebook JavaScript SDK calls www.facebook.com/x/oauth/status, which allows Meta to link the visit to a Facebook account. The policy declares no advertising purposes at all.

4) The policy names 'CINAMON Group' as the controller without a registration code or address, describes cookies as needed 'for the operation of the site and statistics' and 'remembering preferences', suggests managing them in the browser, and states: 'we do not sell your data to third parties'. Not a single recipient is named — not Microsoft (Clarity, Bing), Snap, Meta, Google, Movio or Adobe; legal bases per purpose are not stated; nothing is said about transfers to third countries (Snap Inc., Meta Platforms — USA).


2. Recipients, retention periods, and transfers outside the EEA (Art. 15(1)(c)-(d), 46)
I also request the full list of third-party recipients, the applicable retention period for each category, and the legal basis for any transfer of data outside the EEA. The full technical audit with evidence (saved network log, SHA-256 checksum) is published at: https://gdpru.eu/en/audits/ee-cinamonkino-com/

3. Automated processing and profiling (Art. 15(1)(h))
Please state whether I am subject to automated decision-making or profiling, and if so, disclose the logic involved.

Sincerely,

[Your name]
[contact email]
[Country]


[Date]
Teema: Isikuandmetele juurdepääsu taotlus (IKÜM art 15) — cinamonkino.com Kellele: [märkige ettevõtte aadress — DPO / tugi / juriidiline osakond] Kellelt: [Teie nimi], [kontakt-e-post] Palun anda mulle juurdepääs minu isikuandmetele, mida töödeldakse seoses veebisaidi cinamonkino.com kasutamisega. 1. Andmekategooriad ja töötlemise eesmärgid (IKÜM art 15(1)(a)-(c)) Sõltumatu tehnilise analüüsi põhjal palun kinnitada ja üksikasjalikult avaldada järgmised töötlemiskategooriad: 1) Saidil puudub nõusolekumehhanism: pole ei küpsisebännerit ega nõusolekuhalduse platvormi ning lehe juurelement on märgistatud atribuudiga data-consent=0. Sellest hoolimata laaditakse esimese 2,3 sekundi jooksul ja alustavad andmete edastamist: Facebook Pixel (+515 ms), Google Tag Manager GTM-K5RCC8R (+517 ms), Microsoft Clarity (+851 ms), Universal Analytics ja Google Analytics 4 (+1466…+1638 ms), Google Adsi sidumine ja remarketingu sihtrühmad (+1640…+1641 ms), Snapchat Pixel sündmusega PAGE_VIEW (+1751 ms) ja küpsiste sobitamisega (+1756 ms), Facebooki sisselogimisoleku kontroll (+1792 ms), Clarity seansisalvestus (+1922 ms) ning Bingi identifikaatori sünkroonimine (+2233 ms). Google'i nõusolekurežiim ei ole seadistatud: gcd=13l3l3l2l1l1 (määramata), parameeter gcs puudub. 2) Microsoft Clarity salvestab alates +1922 ms seanssi: esimene saadetis aadressile h.clarity.ms/collect on 67 183 baiti (lehe hetktõmmis), sellele järgneb 57 täiendust. Säilinud päringukehadest nähtub, et Clarity serialiseerib lehtede struktuuri ja tekstid — pealkirjad, linkide tekstid ja juurelemendi <HTML data-consent=0>; salvestisse jõuab ka privaatsuspoliitika leht. Külastaja käitumise salvestamisel ilma nõusolekuta puudub õiguslik alus ning see väljub deklareeritud statistika jaoks vajaliku piiridest. 3) Ilma nõusolekuta rakendatakse kolme eraldi reklaamiidentifikaatorite sobitamise mehhanismi: Snapchati iframe tr.snapchat.com/cm/i (+1756 ms ja +45426 ms), Microsofti sünkroonimine c.bing.com/c.gif (+2233 ms) ning külastaja edastamine Google Adsi remarketingu sihtrühmadesse (www.google.ee/ads/ga-audiences, kolm korda) ühtse kliendiidentifikaatoriga, mis luuakse poolteist sekundit pärast seansi algust. Facebooki JavaScripti SDK pöördub aadressile www.facebook.com/x/oauth/status, mis võimaldab Metal siduda külastuse Facebooki kasutajakontoga. Poliitika ei deklareeri reklaamieesmärke üldse. 4) Poliitika nimetab vastutava töötlejana CINAMON Groupi ilma registrikoodi ja aadressita, kirjeldab küpsiseid kui saidi toimimiseks, statistikaks ja eelistuste meelespidamiseks vajalikke, soovitab neid hallata brauseris ja kinnitab, et andmeid kolmandatele isikutele ei müüda. Ühtegi vastuvõtjat ei nimetata — ei Microsofti (Clarity, Bing), Snapi, Metat, Google'it, Moviot ega Adobet; õiguslikke aluseid eesmärkide kaupa ei ole märgitud; edastamisest kolmandatesse riikidesse (Snap Inc., Meta Platforms — USA) ei ole midagi öeldud. 2. Vastuvõtjad, säilitustähtajad ja edastamine väljapoole EMP-d (IKÜM art 15(1)(c)-(d), 46) Palun samuti esitada täielik loetelu kolmandatest isikutest vastuvõtjatest, iga kategooria puhul kohaldatavad säilitustähtajad ning andmete EMP-välisele edastamisele kohaldatav õiguslik alus, kui selline edastamine toimub. Täielik tehniline analüüs koos tõenditega (salvestatud võrgulogi, SHA-256 kontrollsumma) on avaldatud aadressil: https://gdpru.eu/en/audits/ee-cinamonkino-com/ 3. Automatiseeritud töötlemine ja profiilianalüüs (IKÜM art 15(1)(h)) Palun teatada, kas minu suhtes kohaldatakse automatiseeritud otsuste tegemist või profiilianalüüsi, ning kui jah, siis avaldada selle loogika. Lugupidamisega, [Teie nimi] [kontakt-e-post] [Riik] [Kuupäev]
RIA DigiDoc — phone · Smart-ID / Mobile-ID
Where to file: Estonian Data Protection Inspectorate (AKI) — write to info@aki.ee
Important: AKI only handles submissions in Estonian. Translate the letter before sending.
The regulator reviews complaints in its national language. There is an officially translated template from the European Data Protection Board (EDPB) — you can use it instead of or alongside this letter: Official EDPB complaint form (PDF, your language)
Тема: Жалоба на обработку персональных данных — cinamonkino.com

1. Предмет жалобы
Я подаю жалобу в отношении обработки моих персональных данных сайтом cinamonkino.com.

2. Обстоятельства
Я посетил сайт cinamonkino.com и обнаружил признаки несоответствия обработки моих персональных данных требованиям GDPR. Технический разбор, опубликованный на gdpru.eu 24.09.2026 (открытая методология, воспроизводимые измерения), документирует следующие признаки:

1) Механизма согласия на сайте нет: ни cookie-баннера, ни платформы управления согласием, а корневой элемент страницы помечен атрибутом data-consent=0. Несмотря на это, за первые 2,3 секунды загружаются и начинают передачу: Facebook Pixel (+515 мс), Google Tag Manager GTM-K5RCC8R (+517 мс), Microsoft Clarity (+851 мс), Universal Analytics и Google Analytics 4 (+1466…+1638 мс), связка Google Ads и ремаркетинг-аудитории (+1640…+1641 мс), Snapchat Pixel с событием PAGE_VIEW (+1751 мс) и сопоставлением cookie (+1756 мс), проверка статуса входа Facebook (+1792 мс), запись сеанса Clarity (+1922 мс) и синхронизация идентификатора Bing (+2233 мс). Режим согласия Google не настроен: gcd=13l3l3l2l1l1 («не задано»), параметр gcs отсутствует.

2) Microsoft Clarity с +1922 мс записывает сеанс: первая отправка на h.clarity.ms/collect весит 67 183 байта (снимок страницы), далее следуют 57 инкрементов. В уцелевших телах видно, что Clarity сериализует структуру и тексты страниц — заголовки, подписи ссылок и корневой элемент <HTML data-consent=0>; в запись попадает в том числе страница политики конфиденциальности. Запись поведения посетителя на сайте без согласия не имеет правового основания и выходит за пределы необходимого для заявленной «статистики».

3) Без согласия выполняются три отдельных механизма сопоставления рекламных идентификаторов: iframe tr.snapchat.com/cm/i Snapchat (+1756 мс и +45426 мс), синхронизация c.bing.com/c.gif Microsoft (+2233 мс) и передача посетителя в ремаркетинг-аудитории Google Ads (www.google.ee/ads/ga-audiences, трижды) с единым идентификатором клиента, созданным через полторы секунды после начала сеанса. Facebook JavaScript SDK обращается к www.facebook.com/x/oauth/status, что позволяет Meta сопоставить визит с учётной записью Facebook. Политика рекламных целей не заявляет вовсе.

4) Политика называет контролёром «CINAMON Group» без регистрационного кода и адреса, описывает cookie как нужные «для работы сайта и статистики» и «запоминания предпочтений», предлагает управлять ими в браузере и заявляет: «мы не продаём ваши данные третьим лицам». Ни один получатель не назван — ни Microsoft (Clarity, Bing), ни Snap, ни Meta, ни Google, ни Movio, ни Adobe; правовые основания по целям не указаны; о передаче в третьи страны (Snap Inc., Meta Platforms — США) не сказано ничего.

Полная техническая документация опубликована по адресу: https://gdpru.eu/en/audits/ee-cinamonkino-com/

3. Положения GDPR, соблюдение которых прошу проверить
ePrivacy — Директива 2002/58/EC, ст. 5(3) (в связке с GDPR Art. 6(1)(a)); GDPR Art. 6(1), Art. 5(1)(c) — запись сеансов без правового основания; GDPR Art. 6(1), Art. 5(1)(b) — рекламное сопоставление идентификаторов; GDPR Art. 5(1)(a), Art. 13(1)(a), (c), (e), (f), Art. 44 — прозрачность и раскрытие

4. Требование
Прошу проверить изложенные обстоятельства и, если несоответствие подтвердится, принять меры, предусмотренные статьёй 58(2) GDPR.

5. Приложения
Полная доказательная база — HAR-файл, контрольная сумма SHA-256 и цитата из политики конфиденциальности сайта, документирующая указанное противоречие — опубликована и проверяема по ссылке в пункте 2 выше.

С уважением,

[Ваше имя]
[контактный email]
[Страна]


[Дата]
Subject: Complaint regarding personal data processing — cinamonkino.com

1. Subject of the complaint
I am filing a complaint regarding the processing of my personal data by the website cinamonkino.com.

2. Circumstances
I visited the website cinamonkino.com and found indications that the processing of my personal data does not comply with the GDPR. The technical analysis published on gdpru.eu on 24 September 2026 (open methodology, reproducible measurements) documents the following indications:

1) There is no consent mechanism on the site: no cookie banner, no consent-management platform, and the page's root element carries the attribute data-consent=0. Nonetheless, within the first 2.3 seconds the following load and begin transmitting: the Facebook Pixel (+515 ms), Google Tag Manager GTM-K5RCC8R (+517 ms), Microsoft Clarity (+851 ms), Universal Analytics and Google Analytics 4 (+1466…+1638 ms), the Google Ads link and remarketing audiences (+1640…+1641 ms), the Snapchat Pixel with a PAGE_VIEW event (+1751 ms) and cookie matching (+1756 ms), the Facebook login-status check (+1792 ms), Clarity session recording (+1922 ms) and Bing identifier synchronisation (+2233 ms). Google's consent mode is not configured: gcd=13l3l3l2l1l1 ('not set'), and the gcs parameter is absent.

2) From +1922 ms Microsoft Clarity records the session: the first transmission to h.clarity.ms/collect weighs 67,183 bytes (a page snapshot), followed by 57 increments. The surviving bodies show that Clarity serialises the structure and text of the pages — titles, link labels and the root element <HTML data-consent=0>; the privacy-policy page is recorded too. Recording the visitor's behaviour on the site without consent has no legal basis and goes beyond what is necessary for the declared 'statistics'.

3) Three separate advertising-identifier matching mechanisms run without consent: Snapchat's tr.snapchat.com/cm/i iframe (+1756 ms and +45426 ms), Microsoft's c.bing.com/c.gif synchronisation (+2233 ms) and the passing of the visitor into Google Ads remarketing audiences (www.google.ee/ads/ga-audiences, three times) with a single client identifier created one and a half seconds after the start of the session. The Facebook JavaScript SDK calls www.facebook.com/x/oauth/status, which allows Meta to link the visit to a Facebook account. The policy declares no advertising purposes at all.

4) The policy names 'CINAMON Group' as the controller without a registration code or address, describes cookies as needed 'for the operation of the site and statistics' and 'remembering preferences', suggests managing them in the browser, and states: 'we do not sell your data to third parties'. Not a single recipient is named — not Microsoft (Clarity, Bing), Snap, Meta, Google, Movio or Adobe; legal bases per purpose are not stated; nothing is said about transfers to third countries (Snap Inc., Meta Platforms — USA).

Full technical documentation is published at: https://gdpru.eu/en/audits/ee-cinamonkino-com/

3. GDPR provisions I ask you to examine
ePrivacy — Directive 2002/58/EC, Art. 5(3) (in conjunction with GDPR Art. 6(1)(a)); GDPR Art. 6(1), Art. 5(1)(c) — session recording without a legal basis; GDPR Art. 6(1), Art. 5(1)(b) — advertising identifier matching; GDPR Art. 5(1)(a), Art. 13(1)(a), (c), (e), (f), Art. 44 — transparency and disclosure

4. Request
I request that you examine the circumstances described and, if non-compliance is confirmed, apply the measures provided for in Article 58(2) GDPR.

5. Attachments
The full evidence base — the HAR file, its SHA-256 checksum and the quotation from the site's privacy policy documenting the stated contradiction — is published and verifiable at the link in point 2 above.

Sincerely,

[Your name]
[contact email]
[Country]


[Date]
1. Kaebuse ese Esitan kaebuse seoses minu isikuandmete töötlemisega veebisaidil cinamonkino.com. 2. Asjaolud Külastasin veebisaiti cinamonkino.com ja tuvastasin märke sellest, et minu isikuandmete töötlemine ei vasta isikuandmete kaitse üldmääruse (IKÜM) nõuetele. Tehniline analüüs, mis on avaldatud aadressil gdpru.eu 24.09.2026 (avatud metoodika, korratavad mõõtmised), dokumenteerib järgmist: 1) Saidil puudub nõusolekumehhanism: pole ei küpsisebännerit ega nõusolekuhalduse platvormi ning lehe juurelement on märgistatud atribuudiga data-consent=0. Sellest hoolimata laaditakse esimese 2,3 sekundi jooksul ja alustavad andmete edastamist: Facebook Pixel (+515 ms), Google Tag Manager GTM-K5RCC8R (+517 ms), Microsoft Clarity (+851 ms), Universal Analytics ja Google Analytics 4 (+1466…+1638 ms), Google Adsi sidumine ja remarketingu sihtrühmad (+1640…+1641 ms), Snapchat Pixel sündmusega PAGE_VIEW (+1751 ms) ja küpsiste sobitamisega (+1756 ms), Facebooki sisselogimisoleku kontroll (+1792 ms), Clarity seansisalvestus (+1922 ms) ning Bingi identifikaatori sünkroonimine (+2233 ms). Google'i nõusolekurežiim ei ole seadistatud: gcd=13l3l3l2l1l1 (määramata), parameeter gcs puudub. 2) Microsoft Clarity salvestab alates +1922 ms seanssi: esimene saadetis aadressile h.clarity.ms/collect on 67 183 baiti (lehe hetktõmmis), sellele järgneb 57 täiendust. Säilinud päringukehadest nähtub, et Clarity serialiseerib lehtede struktuuri ja tekstid — pealkirjad, linkide tekstid ja juurelemendi <HTML data-consent=0>; salvestisse jõuab ka privaatsuspoliitika leht. Külastaja käitumise salvestamisel ilma nõusolekuta puudub õiguslik alus ning see väljub deklareeritud statistika jaoks vajaliku piiridest. 3) Ilma nõusolekuta rakendatakse kolme eraldi reklaamiidentifikaatorite sobitamise mehhanismi: Snapchati iframe tr.snapchat.com/cm/i (+1756 ms ja +45426 ms), Microsofti sünkroonimine c.bing.com/c.gif (+2233 ms) ning külastaja edastamine Google Adsi remarketingu sihtrühmadesse (www.google.ee/ads/ga-audiences, kolm korda) ühtse kliendiidentifikaatoriga, mis luuakse poolteist sekundit pärast seansi algust. Facebooki JavaScripti SDK pöördub aadressile www.facebook.com/x/oauth/status, mis võimaldab Metal siduda külastuse Facebooki kasutajakontoga. Poliitika ei deklareeri reklaamieesmärke üldse. 4) Poliitika nimetab vastutava töötlejana CINAMON Groupi ilma registrikoodi ja aadressita, kirjeldab küpsiseid kui saidi toimimiseks, statistikaks ja eelistuste meelespidamiseks vajalikke, soovitab neid hallata brauseris ja kinnitab, et andmeid kolmandatele isikutele ei müüda. Ühtegi vastuvõtjat ei nimetata — ei Microsofti (Clarity, Bing), Snapi, Metat, Google'it, Moviot ega Adobet; õiguslikke aluseid eesmärkide kaupa ei ole märgitud; edastamisest kolmandatesse riikidesse (Snap Inc., Meta Platforms — USA) ei ole midagi öeldud. Täielik tehniline dokumentatsioon on avaldatud aadressil: https://gdpru.eu/en/audits/ee-cinamonkino-com/ 3. Sätted, mille järgimist palun kontrollida e-privaatsuse direktiiv 2002/58/EÜ art 5 lg 3 (koostoimes IKÜM art 6 lg 1 p-ga a); IKÜM art 6 lg 1, art 5 lg 1 p c — seansside salvestamine ilma õigusliku aluseta; IKÜM art 6 lg 1, art 5 lg 1 p b — reklaamiidentifikaatorite sobitamine; IKÜM art 5 lg 1 p a, art 13 lg 1 p a, c, e, f, art 44 — läbipaistvus ja avalikustamine 4. Nõue Palun kontrollida kirjeldatud asjaolusid ja mittevastavuse kinnitamisel kohaldada IKÜM artikli 58 lõikes 2 ette nähtud meetmeid. 5. Lisad Täielik tõendusmaterjal — HAR-fail, kontrollsumma SHA-256 ning veebisaidi privaatsuspoliitika tsitaat, mis dokumenteerib nimetatud vastuolu — on avaldatud ja kontrollitav punktis 2 viidatud lingil. Lugupidamisega, [Teie nimi] [kontakt-e-post] [Riik] [Kuupäev]