
chopsticks.ee
Website of the Chopsticks Asian fast-food chain in Estonia, built on the Tilda site builder — one recording, the home page, 121 requests, fourteen nodes. There is no Google Analytics, Facebook or advertising in the recording, but at +3280 ms Tilda's built-in statistics sends a user identifier, a session identifier and a browser fingerprint. There is no consent-management platform: the Tilda cookie notice declares continued browsing itself to be consent, and the detailed panel offers only an 'Agree' button. Neither Tilda nor Google Maps is named in the documents. The attached policy relates to the online shop menu.chopsticks.ee, not to chopsticks.ee itself. The browser did not send a DNT header.
Request timeline
Declared versus actual
Transfer timings
Scripts and styles of the Tilda builder.
tilda-stat-1.0.min.js, loaded by the page's script.
/event/ — userid, sessionid, user_agent, language, page address, fingerprint.
Google Maps API, initiated by the Tilda map script.
The Roboto font for the Google map.
Detected trackers
- Tilda Statistics (stat.tildaapi.one/event/) — the built-in statistics of the Tilda site builder; transmits a user identifier, a session identifier, the User-Agent, the language, the page address and a browser fingerprint
- Tilda — site platform and CDN: static.tildacdn.net, thb.tildacdn.net, optim.tildacdn.net, static.tildacdn.one, neo.tildacdn.com, static.tildacdn.com, upwidget.tildacdn.com
- Google Maps (maps.google.com, maps.googleapis.com, maps.gstatic.com) — an embedded map; the visitor's IP address is visible to Google
- Google Fonts (fonts.googleapis.com, fonts.gstatic.com) — the Roboto font, loaded by the Google map; the visitor's IP address is visible to Google
Indicators of GDPR non-compliance
- ePrivacy — Directive 2002/58/EC, Art. 5(3) (in conjunction with GDPR Art. 6(1)(a))There is no dedicated consent-management platform on the site; the built-in Tilda cookie notice is displayed, whose text reads: 'If you continue browsing the site or click "Jah, nõustun", you agree to the use of cookies'. Consent by continued browsing is not valid consent under ePrivacy and the case law of the Court of Justice. Under these conditions the Tilda statistics script (tilda-stat-1.0.min.js) is loaded by the page's own script at +2717 ms, and at +3280 ms a POST request to stat.tildaapi.one/event/ goes out with the fields userid, sessionid, user_agent, user_language, page and fingerprint. Accessing the device to build a browser fingerprint and assign a user identifier falls under Article 5(3) regardless of whether cookies are used.
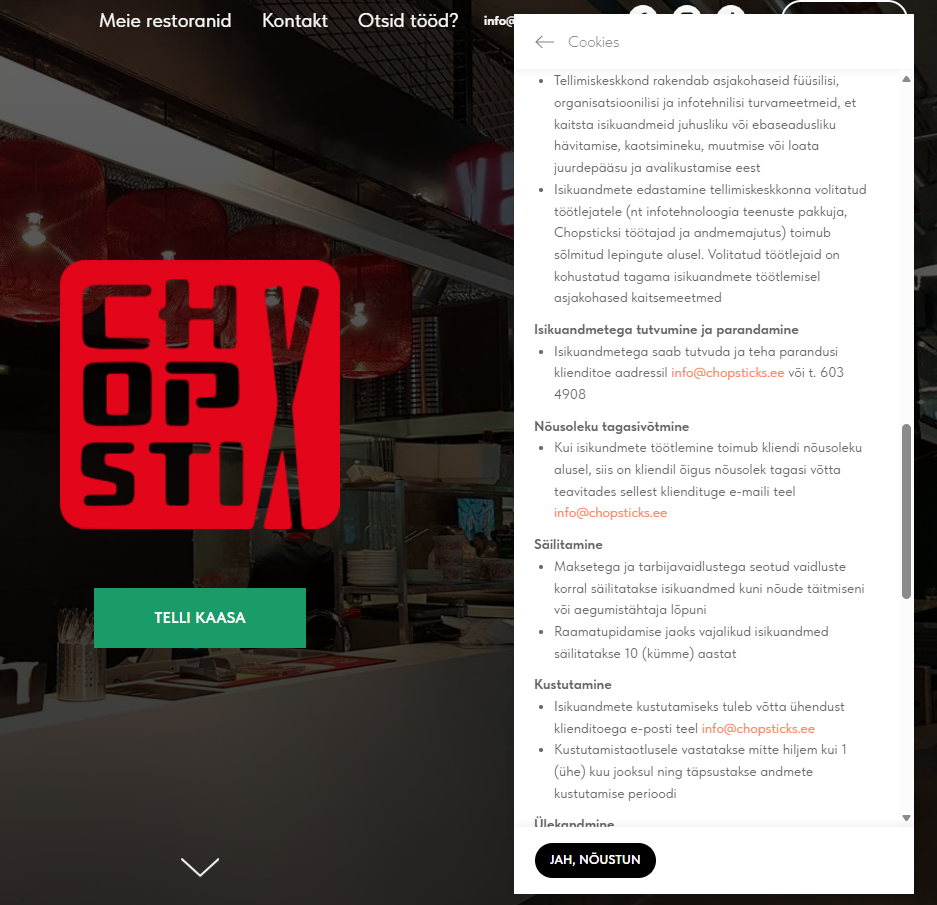
- GDPR Art. 13(1)(e) — disclosure of recipientsNeither the attached policy nor the text about data on the site itself (the 'Loe edasi' panel) names Tilda as a recipient of statistics or Google as a recipient of data when the map is shown; only 'service providers', an 'IT service provider' and 'hosting' are mentioned. The building of a browser fingerprint is disclosed nowhere.
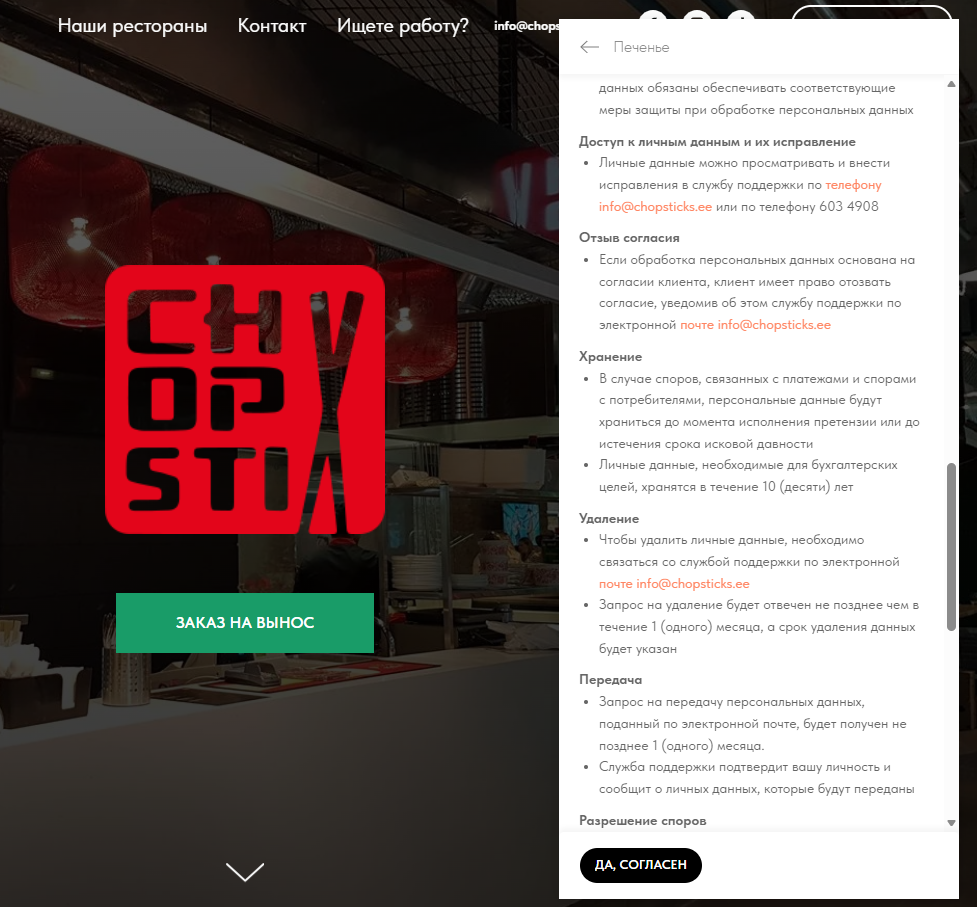
- GDPR Art. 5(1)(a) — transparency: the declared diverges from the actualThe attached policy ends with the formula 'by using our website you consent to the terms of this privacy policy', while the cookie notice declares continued browsing to be consent; in the detailed 'Loe edasi' panel (Estonian and Russian versions) only an 'Agree' button is available. In fact statistics carrying a user identifier and a browser fingerprint are transmitted on page load, and the way of obtaining consent that the site declares is not valid consent.
Context
chopsticks.ee is the website of the Chopsticks Asian fast-food chain in Estonia, built on the Tilda site builder. The contact given on the site itself is info@chopsticks.ee, tel. 603 4908.
Attached to the material are a privacy policy and three screenshots: the cookie notice and the detailed data panel in Estonian and Russian. The attached policy is titled as the policy of the online shop menu.chopsticks.ee, whose owner is OÜ McKenzie Invest (registration code 10951185); there is no separate policy specifically for chopsticks.ee in the material. On chopsticks.ee itself, the text about data is shown in the cookie notice’s ‘Loe edasi’ panel.
The measurement consists of one recording, one navigation — the home page. One hundred and twenty-one requests, fourteen nodes. The recording was made on 18 September 2026.
Who data goes to directly
Tilda (site platform and built-in statistics), Google (Maps, Fonts). There is no Google Analytics, Facebook, advertising or RTB in the recording.
Declared versus actual
The attached policy describes the collection of device data (IP address, browser type, operating system) and site-usage data (pages, time of the visit, session duration) for the purpose of analytics, sharing with unnamed ’third-party service providers’, and ends with the formula ‘by using our website you consent to the terms of this privacy policy’. It has no cookie section, no controller address, no data-protection contact and no supervisory authority. The text on the site itself (the ‘Loe edasi’ panel) names as recipients authorised processors — an IT service provider, Chopsticks staff and hosting.
The measurement shows the following.
Tilda statistics transmit identifiers and a browser fingerprint. The page’s own script loads tilda-stat-1.0.min.js at +2717 ms, and at +3280 ms a POST request to stat.tildaapi.one/event/ goes out. It transmits the page address, a user identifier (userid), a session identifier (sessionid), the User-Agent, the interface language, project and page identifiers, and fingerprint — a browser fingerprint. The values are redacted in the published file, but the set of fields is legible from the recording.
There is no valid consent mechanism. There is no dedicated consent-management platform in the recording. The built-in Tilda cookie notice declares continued browsing of the site to be consent on a par with clicking ‘Jah, nõustun’; the ‘Ei nõustu’ refusal is shown as a text link next to a large consent button, and in the detailed ‘Loe edasi’ panel — in both the Estonian and Russian versions — only an ‘Agree’ button is available. The notice offers withdrawal of consent by changing the device settings and deleting cookies. Consent by continued browsing is not valid consent.
Recipients are not named. Neither Tilda as a recipient of statistics nor Google as a recipient of data when the embedded map is shown is named in the documents; the building of a browser fingerprint is disclosed nowhere.
Functional nodes: the Tilda platform (static.tildacdn.net, thb.tildacdn.net, optim.tildacdn.net, static.tildacdn.one, neo.tildacdn.com, static.tildacdn.com, upwidget.tildacdn.com) — scripts, styles, images, fonts and the file-upload module; Google Maps (maps.google.com, maps.googleapis.com, maps.gstatic.com) — an embedded map loaded at +17667 ms on the initiative of the Tilda map script, with the Roboto font from Google Fonts.
Consent: what is proven and what is not
Proven: there is no dedicated consent-management platform. A check against the domains of known consent platforms and against consent-mode signals yielded no matches.
Proven: the notice declares continued browsing to be consent. This is visible in the screenshots; the detailed panel offers only a consent button.
Proven: Tilda statistics transmit identifiers and a browser fingerprint. By the set of fields in the POST request to stat.tildaapi.one/event/ at +3280 ms.
Not proven and not asserted: whether the user clicked any button before +3280 ms. A choice in the Tilda notice produces no network request, so the timing and content of the choice cannot be established from the recording. The conclusion rests not on the order of clicks but on the fact that the consent model declared by the site — continued browsing — is not valid consent.
Separately: the browser did not send a DNT header in this recording.
Bounds of observation
The measurement covers a single page — the home page. Observation captures the browser’s behaviour, not the internal side of the services: server-side processing and contractual relationships with recipients are not verified by a browser measurement. The legal assessment is made by the competent authority — in Estonia, Andmekaitse Inspektsioon.
The attached policy relates to the online shop menu.chopsticks.ee; whether it extends to chopsticks.ee, and whether OÜ McKenzie Invest is the controller of the data of chopsticks.ee, cannot be established from the material. Information about sharing with authorised processors is taken from the ‘Loe edasi’ panel on the site itself, visible in the screenshots.
The file is published redacted under a “lean” profile: cookie values in requests have been removed, the Cookie and Set-Cookie headers stripped; the redaction registry records 237 redactions and a checksum. The values of the Tilda statistics fields and the Google Maps key are redacted in the file; the set of fields is fully legible.
The identification of services relies on domains and address patterns: the statistics — by stat.tildaapi.one and the tilda-stat-1.0.min.js script; the platform — by tildacdn.net, tildacdn.one, tildacdn.com; the map — by maps.google.com, maps.googleapis.com, maps.gstatic.com; the fonts — by fonts.googleapis.com, fonts.gstatic.com.
Conclusion
The Chopsticks fast-food chain’s website uses neither Google Analytics, nor Facebook, nor advertising, but the Tilda builder’s built-in statistics, on loading the home page, sends a user identifier, a session identifier and a browser fingerprint. There is no valid consent mechanism: the cookie notice declares continued browsing to be consent, the refusal is shown as a text link, and the detailed panel offers only an ‘Agree’ button. Neither Tilda as a recipient of statistics nor Google as a recipient of the embedded map’s data is named in the documents, and the building of a browser fingerprint is not disclosed. The attached policy relates to the online shop menu.chopsticks.ee and contains no cookie section, no data-protection contact and no supervisory authority.
Remediation: do not launch Tilda statistics before valid consent is obtained — abandon the ‘continued browsing means consent’ model, present refusal on equal footing with consent on both levels of the notice, and place the loading of tilda-stat under actual blocking until the user’s choice; name Tilda and Google Maps in the documents and disclose the collection of a browser fingerprint; publish a policy relating directly to chopsticks.ee, stating the controller, a data-protection contact and the supervisory authority; set security headers on the domain.
How to verify: download the file and compute its checksum — sha256sum file.har (Linux, macOS) or certutil -hashfile file.har SHA256 (Windows); it must match the one shown. The conclusions apply to the scope of this measurement — see the limitations of the method.
319b021c270d9b8d1f074d265da757d5014750d7656da8ca1fed4620e1babcf9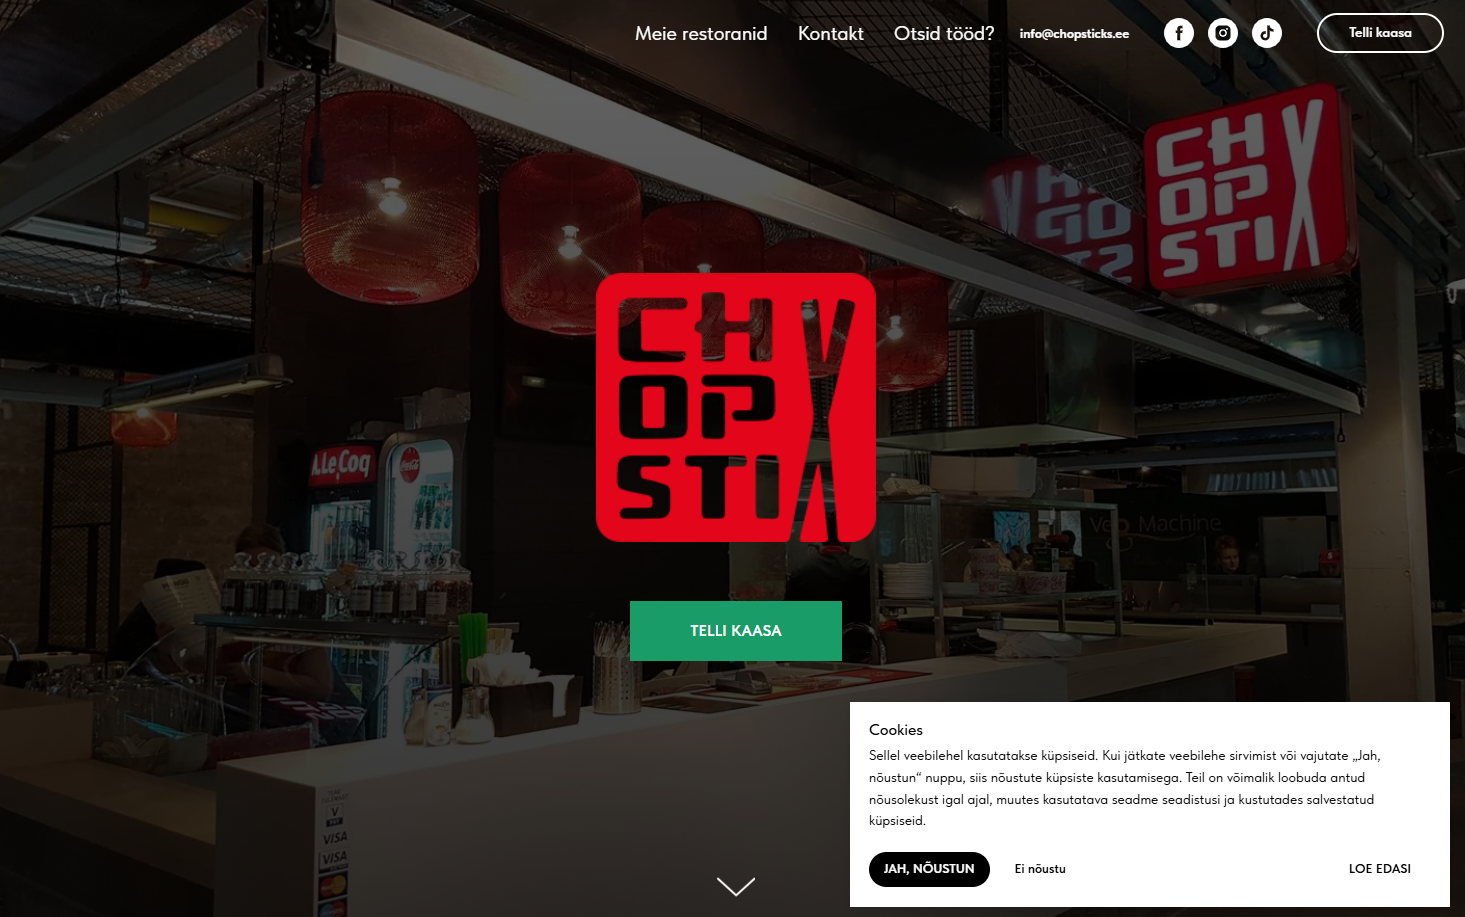
Want a response from the company about this audit? → Open the tool
Fill in once — it will be inserted into every letter below:
All fields are required to print the document — this is a formal requirement of the letter itself (the particulars of an official submission), not data collection: nothing is sent or saved anywhere, it all stays in your browser and disappears when you close the page. See the methodology for details.
RIA DigiDoc — phone · Smart-ID / Mobile-ID
Send this letter directly to the company first — before contacting the regulator it has the right to respond (GDPR Art. 12(3) — 30 days).
Тема: Запрос доступа к персональным данным (ст. 15 GDPR) — chopsticks.ee

Кому: [укажите адрес компании — DPO / поддержка / юридический отдел]
От: [Ваше имя], [контактный email]

Прошу предоставить доступ к моим персональным данным, обрабатываемым в связи с использованием сайта chopsticks.ee.

1. Категории данных и цели обработки (ст. 15(1)(a)-(c))
На основании независимого технического анализа сайта прошу подтвердить и подробно раскрыть следующие категории обработки:

1) Отдельной платформы управления согласием на сайте нет; выводится встроенная cookie-плашка Tilda, текст которой гласит: «Если вы продолжаете просмотр сайта или нажимаете „Jah, nõustun“, вы соглашаетесь с использованием cookie». Согласие через продолжение просмотра действительным согласием по ePrivacy и практике Суда ЕС не является. В этих условиях скрипт статистики Tilda (tilda-stat-1.0.min.js) подгружается собственным скриптом страницы на +2717 мс, и на +3280 мс уходит POST-обращение stat.tildaapi.one/event/ с полями userid, sessionid, user_agent, user_language, page и fingerprint. Доступ к устройству для построения отпечатка браузера и присвоения идентификатора пользователя подпадает под статью 5(3) независимо от того, используются ли cookie.

2) Ни в приложенной политике, ни в тексте о данных на самом сайте (панель «Loe edasi») Tilda как получатель статистики и Google как получатель данных при показе карты поимённо не названы; упоминаются лишь «поставщики услуг», «поставщик ИТ-услуг» и «хостинг». Факт построения отпечатка браузера нигде не раскрыт.

3) Приложенная политика заканчивается формулой «используя наш сайт, вы даёте согласие с условиями настоящей политики», а cookie-плашка объявляет согласием продолжение просмотра; в подробной панели «Loe edasi» (эстонская и русская версии) доступна только кнопка «Согласен». Фактически статистика с идентификатором пользователя и отпечатком браузера передаётся при загрузке страницы, а порядок получения согласия, который декларирует сайт, действительным согласием не является.


2. Получатели, сроки хранения и передача за пределы ЕЭЗ (ст. 15(1)(c)-(d), 46)
Прошу также указать полный список третьих лиц-получателей, применимые сроки хранения по каждой категории и правовые основания передачи данных за пределы ЕЭЗ, если таковая происходит. Полный технический разбор с доказательствами (сохранённый сетевой журнал, контрольная сумма SHA-256) опубликован по адресу: https://gdpru.eu/en/audits/ee-chopsticks-ee/

3. Автоматизированная обработка и профилирование (ст. 15(1)(h))
Прошу сообщить, применяется ли в отношении меня автоматизированное принятие решений или профилирование, и если да — раскрыть логику такой обработки.

С уважением,

[Ваше имя]
[контактный email]
[Страна]


[Дата]
Subject: Data access request (GDPR Art. 15) — chopsticks.ee

To: [insert the company's address — DPO / support / legal department]
From: [Your name], [contact email]

I request access to my personal data processed in connection with the website chopsticks.ee.

1. Categories of data and purposes of processing (Art. 15(1)(a)-(c))
Based on an independent technical analysis of the site, I request confirmation and detailed disclosure of the following categories of processing:

1) There is no dedicated consent-management platform on the site; the built-in Tilda cookie notice is displayed, whose text reads: 'If you continue browsing the site or click "Jah, nõustun", you agree to the use of cookies'. Consent by continued browsing is not valid consent under ePrivacy and the case law of the Court of Justice. Under these conditions the Tilda statistics script (tilda-stat-1.0.min.js) is loaded by the page's own script at +2717 ms, and at +3280 ms a POST request to stat.tildaapi.one/event/ goes out with the fields userid, sessionid, user_agent, user_language, page and fingerprint. Accessing the device to build a browser fingerprint and assign a user identifier falls under Article 5(3) regardless of whether cookies are used.

2) Neither the attached policy nor the text about data on the site itself (the 'Loe edasi' panel) names Tilda as a recipient of statistics or Google as a recipient of data when the map is shown; only 'service providers', an 'IT service provider' and 'hosting' are mentioned. The building of a browser fingerprint is disclosed nowhere.

3) The attached policy ends with the formula 'by using our website you consent to the terms of this privacy policy', while the cookie notice declares continued browsing to be consent; in the detailed 'Loe edasi' panel (Estonian and Russian versions) only an 'Agree' button is available. In fact statistics carrying a user identifier and a browser fingerprint are transmitted on page load, and the way of obtaining consent that the site declares is not valid consent.


2. Recipients, retention periods, and transfers outside the EEA (Art. 15(1)(c)-(d), 46)
I also request the full list of third-party recipients, the applicable retention period for each category, and the legal basis for any transfer of data outside the EEA. The full technical audit with evidence (saved network log, SHA-256 checksum) is published at: https://gdpru.eu/en/audits/ee-chopsticks-ee/

3. Automated processing and profiling (Art. 15(1)(h))
Please state whether I am subject to automated decision-making or profiling, and if so, disclose the logic involved.

Sincerely,

[Your name]
[contact email]
[Country]


[Date]
Teema: Isikuandmetele juurdepääsu taotlus (IKÜM art 15) — chopsticks.ee

Kellele: [märkige ettevõtte aadress — DPO / tugi / juriidiline osakond]
Kellelt: [Teie nimi], [kontakt-e-post]

Palun anda mulle juurdepääs minu isikuandmetele, mida töödeldakse seoses veebisaidi chopsticks.ee kasutamisega.

1. Andmekategooriad ja töötlemise eesmärgid (IKÜM art 15(1)(a)-(c))
Sõltumatu tehnilise analüüsi põhjal palun kinnitada ja üksikasjalikult avaldada järgmised töötlemiskategooriad:

1) Saidil puudub eraldi nõusolekuhalduse platvorm; kuvatakse Tilda sisseehitatud küpsiseteade, mille kohaselt nõustub külastaja küpsiste kasutamisega, kui ta jätkab saidi sirvimist või vajutab nuppu „Jah, nõustun“. Sirvimise jätkamine ei ole e-privaatsuse direktiivi ja Euroopa Liidu Kohtu praktika kohaselt kehtiv nõusolek. Neis tingimustes laadib lehe enda skript +2717 ms juures Tilda statistikaskripti (tilda-stat-1.0.min.js) ning +3280 ms juures saadetakse POST-päring aadressile stat.tildaapi.one/event/ väljadega userid, sessionid, user_agent, user_language, page ja fingerprint. Juurdepääs seadmele brauseri sõrmejälje loomiseks ja kasutajatunnuse omistamiseks kuulub artikli 5 lõike 3 kohaldamisalasse sõltumata sellest, kas kasutatakse küpsiseid.

2) Ei lisatud privaatsuspoliitikas ega saidi andmeid käsitlevas tekstis (paneel „Loe edasi“) nimetata Tildat statistika vastuvõtjana ega Google'it kaardi kuvamisel andmete vastuvõtjana; mainitakse üksnes üldiselt teenusepakkujaid, IT-teenuse pakkujat ja majutust. Brauseri sõrmejälje loomist ei ole kusagil avalikustatud.

3) Lisatud privaatsuspoliitika lõpeb sõnastusega, mille kohaselt saidi kasutamine tähendab nõusolekut poliitika tingimustega; küpsiseteade loeb nõusolekuks sirvimise jätkamise ning üksikasjalikus paneelis „Loe edasi“ (eesti- ja venekeelne versioon) on saadaval ainult nõustumise nupp. Tegelikult edastatakse kasutajatunnuse ja brauseri sõrmejäljega statistika juba lehe laadimisel ning saidi deklareeritud nõusoleku saamise kord ei anna kehtivat nõusolekut.


2. Vastuvõtjad, säilitustähtajad ja edastamine väljapoole EMP-d (IKÜM art 15(1)(c)-(d), 46)
Palun samuti esitada täielik loetelu kolmandatest isikutest vastuvõtjatest, iga kategooria puhul kohaldatavad säilitustähtajad ning andmete EMP-välisele edastamisele kohaldatav õiguslik alus, kui selline edastamine toimub. Täielik tehniline analüüs koos tõenditega (salvestatud võrgulogi, SHA-256 kontrollsumma) on avaldatud aadressil: https://gdpru.eu/en/audits/ee-chopsticks-ee/

3. Automatiseeritud töötlemine ja profiilianalüüs (IKÜM art 15(1)(h))
Palun teatada, kas minu suhtes kohaldatakse automatiseeritud otsuste tegemist või profiilianalüüsi, ning kui jah, siis avaldada selle loogika.

Lugupidamisega,

[Teie nimi]
[kontakt-e-post]
[Riik]


[Kuupäev]
RIA DigiDoc — phone · Smart-ID / Mobile-ID
Where to file: Estonian Data Protection Inspectorate (AKI) — write to info@aki.ee
Important: AKI only handles submissions in Estonian. Translate the letter before sending.
The regulator reviews complaints in its national language. There is an officially translated template from the European Data Protection Board (EDPB) — you can use it instead of or alongside this letter: Official EDPB complaint form (PDF, your language)
Тема: Жалоба на обработку персональных данных — chopsticks.ee

1. Предмет жалобы
Я подаю жалобу в отношении обработки моих персональных данных сайтом chopsticks.ee.

2. Обстоятельства
Я посетил сайт chopsticks.ee и обнаружил признаки несоответствия обработки моих персональных данных требованиям GDPR. Технический разбор, опубликованный на gdpru.eu 18.09.2026 (открытая методология, воспроизводимые измерения), документирует следующие признаки:

1) Отдельной платформы управления согласием на сайте нет; выводится встроенная cookie-плашка Tilda, текст которой гласит: «Если вы продолжаете просмотр сайта или нажимаете „Jah, nõustun“, вы соглашаетесь с использованием cookie». Согласие через продолжение просмотра действительным согласием по ePrivacy и практике Суда ЕС не является. В этих условиях скрипт статистики Tilda (tilda-stat-1.0.min.js) подгружается собственным скриптом страницы на +2717 мс, и на +3280 мс уходит POST-обращение stat.tildaapi.one/event/ с полями userid, sessionid, user_agent, user_language, page и fingerprint. Доступ к устройству для построения отпечатка браузера и присвоения идентификатора пользователя подпадает под статью 5(3) независимо от того, используются ли cookie.

2) Ни в приложенной политике, ни в тексте о данных на самом сайте (панель «Loe edasi») Tilda как получатель статистики и Google как получатель данных при показе карты поимённо не названы; упоминаются лишь «поставщики услуг», «поставщик ИТ-услуг» и «хостинг». Факт построения отпечатка браузера нигде не раскрыт.

3) Приложенная политика заканчивается формулой «используя наш сайт, вы даёте согласие с условиями настоящей политики», а cookie-плашка объявляет согласием продолжение просмотра; в подробной панели «Loe edasi» (эстонская и русская версии) доступна только кнопка «Согласен». Фактически статистика с идентификатором пользователя и отпечатком браузера передаётся при загрузке страницы, а порядок получения согласия, который декларирует сайт, действительным согласием не является.

Полная техническая документация опубликована по адресу: https://gdpru.eu/en/audits/ee-chopsticks-ee/

3. Положения GDPR, соблюдение которых прошу проверить
ePrivacy — Директива 2002/58/EC, ст. 5(3) (в связке с GDPR Art. 6(1)(a)); GDPR Art. 13(1)(e) — раскрытие получателей; GDPR Art. 5(1)(a) — прозрачность: заявленное расходится с фактическим

4. Требование
Прошу проверить изложенные обстоятельства и, если несоответствие подтвердится, принять меры, предусмотренные статьёй 58(2) GDPR.

5. Приложения
Полная доказательная база — HAR-файл, контрольная сумма SHA-256 и цитата из политики конфиденциальности сайта, документирующая указанное противоречие — опубликована и проверяема по ссылке в пункте 2 выше.

С уважением,

[Ваше имя]
[контактный email]
[Страна]


[Дата]
Subject: Complaint regarding personal data processing — chopsticks.ee

1. Subject of the complaint
I am filing a complaint regarding the processing of my personal data by the website chopsticks.ee.

2. Circumstances
I visited the website chopsticks.ee and found indications that the processing of my personal data does not comply with the GDPR. The technical analysis published on gdpru.eu on 18 September 2026 (open methodology, reproducible measurements) documents the following indications:

1) There is no dedicated consent-management platform on the site; the built-in Tilda cookie notice is displayed, whose text reads: 'If you continue browsing the site or click "Jah, nõustun", you agree to the use of cookies'. Consent by continued browsing is not valid consent under ePrivacy and the case law of the Court of Justice. Under these conditions the Tilda statistics script (tilda-stat-1.0.min.js) is loaded by the page's own script at +2717 ms, and at +3280 ms a POST request to stat.tildaapi.one/event/ goes out with the fields userid, sessionid, user_agent, user_language, page and fingerprint. Accessing the device to build a browser fingerprint and assign a user identifier falls under Article 5(3) regardless of whether cookies are used.

2) Neither the attached policy nor the text about data on the site itself (the 'Loe edasi' panel) names Tilda as a recipient of statistics or Google as a recipient of data when the map is shown; only 'service providers', an 'IT service provider' and 'hosting' are mentioned. The building of a browser fingerprint is disclosed nowhere.

3) The attached policy ends with the formula 'by using our website you consent to the terms of this privacy policy', while the cookie notice declares continued browsing to be consent; in the detailed 'Loe edasi' panel (Estonian and Russian versions) only an 'Agree' button is available. In fact statistics carrying a user identifier and a browser fingerprint are transmitted on page load, and the way of obtaining consent that the site declares is not valid consent.

Full technical documentation is published at: https://gdpru.eu/en/audits/ee-chopsticks-ee/

3. GDPR provisions I ask you to examine
ePrivacy — Directive 2002/58/EC, Art. 5(3) (in conjunction with GDPR Art. 6(1)(a)); GDPR Art. 13(1)(e) — disclosure of recipients; GDPR Art. 5(1)(a) — transparency: the declared diverges from the actual

4. Request
I request that you examine the circumstances described and, if non-compliance is confirmed, apply the measures provided for in Article 58(2) GDPR.

5. Attachments
The full evidence base — the HAR file, its SHA-256 checksum and the quotation from the site's privacy policy documenting the stated contradiction — is published and verifiable at the link in point 2 above.

Sincerely,

[Your name]
[contact email]
[Country]


[Date]
1. Kaebuse ese
Esitan kaebuse seoses minu isikuandmete töötlemisega veebisaidil chopsticks.ee.

2. Asjaolud
Külastasin veebisaiti chopsticks.ee ja tuvastasin märke sellest, et minu isikuandmete töötlemine ei vasta isikuandmete kaitse üldmääruse (IKÜM) nõuetele. Tehniline analüüs, mis on avaldatud aadressil gdpru.eu 18.09.2026 (avatud metoodika, korratavad mõõtmised), dokumenteerib järgmist:

1) Saidil puudub eraldi nõusolekuhalduse platvorm; kuvatakse Tilda sisseehitatud küpsiseteade, mille kohaselt nõustub külastaja küpsiste kasutamisega, kui ta jätkab saidi sirvimist või vajutab nuppu „Jah, nõustun“. Sirvimise jätkamine ei ole e-privaatsuse direktiivi ja Euroopa Liidu Kohtu praktika kohaselt kehtiv nõusolek. Neis tingimustes laadib lehe enda skript +2717 ms juures Tilda statistikaskripti (tilda-stat-1.0.min.js) ning +3280 ms juures saadetakse POST-päring aadressile stat.tildaapi.one/event/ väljadega userid, sessionid, user_agent, user_language, page ja fingerprint. Juurdepääs seadmele brauseri sõrmejälje loomiseks ja kasutajatunnuse omistamiseks kuulub artikli 5 lõike 3 kohaldamisalasse sõltumata sellest, kas kasutatakse küpsiseid.

2) Ei lisatud privaatsuspoliitikas ega saidi andmeid käsitlevas tekstis (paneel „Loe edasi“) nimetata Tildat statistika vastuvõtjana ega Google'it kaardi kuvamisel andmete vastuvõtjana; mainitakse üksnes üldiselt teenusepakkujaid, IT-teenuse pakkujat ja majutust. Brauseri sõrmejälje loomist ei ole kusagil avalikustatud.

3) Lisatud privaatsuspoliitika lõpeb sõnastusega, mille kohaselt saidi kasutamine tähendab nõusolekut poliitika tingimustega; küpsiseteade loeb nõusolekuks sirvimise jätkamise ning üksikasjalikus paneelis „Loe edasi“ (eesti- ja venekeelne versioon) on saadaval ainult nõustumise nupp. Tegelikult edastatakse kasutajatunnuse ja brauseri sõrmejäljega statistika juba lehe laadimisel ning saidi deklareeritud nõusoleku saamise kord ei anna kehtivat nõusolekut.

Täielik tehniline dokumentatsioon on avaldatud aadressil: https://gdpru.eu/en/audits/ee-chopsticks-ee/

3. Sätted, mille järgimist palun kontrollida
e-privaatsuse direktiiv 2002/58/EÜ art 5 lg 3 (koostoimes IKÜM art 6 lg 1 p-ga a); IKÜM art 13 lg 1 p e — vastuvõtjate avalikustamine; IKÜM art 5 lg 1 p a — läbipaistvus: deklareeritu erineb tegelikust

4. Nõue
Palun kontrollida kirjeldatud asjaolusid ja mittevastavuse kinnitamisel kohaldada IKÜM artikli 58 lõikes 2 ette nähtud meetmeid.

5. Lisad
Täielik tõendusmaterjal — HAR-fail, kontrollsumma SHA-256 ning veebisaidi privaatsuspoliitika tsitaat, mis dokumenteerib nimetatud vastuolu — on avaldatud ja kontrollitav punktis 2 viidatud lingil.

Lugupidamisega,

[Teie nimi]
[kontakt-e-post]
[Riik]


[Kuupäev]