
The marketplace for experiences and gift cards Chilli — a single capture of an updates page, 100 requests, 19 nodes. The CookieScript consent management platform is on the site, and the banner offers refusal («Keeldu kõigist»). But it loads last — at +7391 ms, after the entire advertising stack has already run: the Facebook pixel sent the page view with the full URL twice, GA4 and DoubleClick went out with status gcs=- (consent mode not configured at all), Google's remarketing audiences fired. By the time the consent mechanism appears, the data has already been transferred. And the policy is almost empty — it names not a single recipient: neither Facebook, nor Google, nor DoubleClick, nor CookieScript itself.
Request timeline
Declared versus actual
Transfer timings
fbevents.js; the CMP appears only at +7391 ms.
/ccm/s/collect; consent mode not configured.
GA4 page_view; no consent signal passed.
/ads/ga-audiences.
/tr ev=PageView, dl=full page address; twice (two pixels).
About 4.3 s after the stack had already sent everything.
Detected trackers
- Facebook / Meta (connect.facebook.net, www.facebook.com — two pixels 1508542746055171 and ...172) — advertising pixel; a /tr event with ev=PageView fires TWICE at +3051…+3063 ms, with the full page address (dl=chilli.ee/et/info/uuendused-platvormil). Before the CMP loads. The _fbp cookie is set. NOT named in the policy
- Google Analytics 4 (region1.analytics.google.com) — analytics; a page_view event at +2981 ms with status gcs=- (consent mode NOT configured, no signal passed). Before the CMP. Not named in the policy
- Google Ads / DoubleClick (ad.doubleclick.net/ccm/s/collect, www.google.com/ccm/collect, www.google.ee/ads/ga-audiences) — advertising and remarketing audiences; requests at +2932…+2984 ms with status gcs=-. Before the CMP. The _gcl_au cookie is set. Not named in the policy
- CookieScript (cdn.cookie-script.com) — consent management platform; loads LAST, at +7391 ms — about 4.3 seconds after Facebook, GA and DoubleClick have already sent data. A banner with the buttons «Nõustu kõigiga» / «Keeldu kõigist». Not named in the policy
- Google Tag Manager (www.googletagmanager.com) — tag container; +2107 ms
- Adobe Typekit (use.typekit.net, p.typekit.net) — fonts; jQuery, jsDelivr — libraries; functional
- First party and infrastructure: chilli.ee, cdn2.chilli.ee, zback2.chilli.ee, static.chilli.ee
- Capture-tool artefact: edge.microsoft.com/translate — the browser translation feature, not a site component
Indicators of GDPR non-compliance
- ePrivacy — Directive 2002/58/EC, Art. 5(3) (in conjunction with GDPR Art. 6(1)(a)) — the entire advertising stack runs before the CMP loadsThe CookieScript consent management platform is on the site, and the banner offers refusal («Keeldu kõigist»). But the CMP loads LAST — at +7391 ms, whereas the entire advertising and analytics stack runs earlier and with an actual transfer of data: the GTM container (+2107 ms), the Facebook pixel (fbevents.js +2130 ms), then at +2932…+3063 ms — DoubleClick /ccm/s/collect, Google Ads /ccm/collect, GA4 /g/collect, the remarketing audiences google.ee/ads/ga-audiences, and the Facebook pixel /tr, firing TWICE with the full page address (dl=chilli.ee/et/info/uuendused-platvormil). That is, by the time the CMP finally loaded (+7391 ms), Facebook had already received the page view with the URL, and Google an event and a remarketing signal. Worse: GA4 and DoubleClick carry status gcs=- — Google's consent mode is not configured at all (not the denied state G100, but the absence of a signal). The cookies _fbp (Facebook) and _gcl_au (Google Ads) are written to the device. A banner with refusal exists, but in fact it changes nothing — the stack ran seconds before the consent mechanism appeared.
- GDPR Art. 13(1)(e) — recipients not disclosed (an almost empty policy)The cookie policy is extremely sparse: it states that «the site uses cookies to improve service» and offers refusal only via browser settings (with a link to aki.ee). Not a single actual recipient is named — neither Facebook/Meta (two pixels, /tr with the page address), nor Google Analytics, nor Google Ads/DoubleClick (advertising and remarketing), nor the CookieScript platform itself. A visitor reading the policy does not learn that their page view goes to Meta and Google with the full URL and is used for advertising remarketing.
Context
chilli.ee is a marketplace for experiences, leisure and gift cards (spa, entertainment, food, gift ideas; a map of venues). The processing is described by a short cookie policy; consent is managed by the CookieScript platform.
The capture is a single recording of a platform-updates page (/et/info/uuendused-platvormil): 100 requests, 19 nodes.
Who data goes to directly
Facebook/Meta (two pixels, page view with the full URL), Google Analytics, Google Ads/DoubleClick (advertising and remarketing audiences) — all before the CMP loads. Consent management — CookieScript (loads last). Functionally — Typekit fonts, jQuery. The first party is Chilli’s infrastructure. The requests to edge.microsoft.com/translate are a capture-tool artefact (translation in the browser).
Declared versus actual
The discrepancy here is twofold and severe: the consent mechanism is physically late, and the policy discloses almost nothing.
The CMP loads after the entire advertising stack. The site has the CookieScript platform, and the banner offers refusal («Keeldu kõigist») — by its buttons it is acceptable. But the platform itself loads last, at +7391 ms, whereas the rest of the stack runs seconds before it. The GTM container — +2107 ms, the Facebook pixel (fbevents.js) — +2130 ms. Then at +2932…+3063 ms: DoubleClick (/ccm/s/collect), Google Ads (/ccm/collect), GA4 (/g/collect), the remarketing audiences (google.ee/ads/ga-audiences) and the Facebook pixel /tr, firing twice (two pixels, ev=PageView) with the full page address in dl. That is, by the time the consent mechanism finally appears (+7391 ms), Facebook has already received the page view with the URL, and Google an event and a remarketing signal. A banner with refusal exists, but in fact it changes nothing — it is four seconds too late.
Google’s consent mode is not configured. Unlike many sites, where GA runs at least with status gcs=G100 (denial respected), here GA4 and DoubleClick carry gcs=- — there is no consent signal at all, Google’s consent mode is not connected. The cookies _fbp (Facebook) and _gcl_au (Google Ads) are written to the device.
The policy is almost empty. The cookie document states only that «the site uses cookies to improve service» and offers refusal via browser settings (with a link to aki.ee). Not a single actual recipient is named — neither Facebook/Meta, nor Google Analytics, nor Google Ads/DoubleClick, nor CookieScript itself. A visitor does not learn from the policy that their page view goes to Meta and Google with the full URL and is used for advertising remarketing.
Consent: what is proven and what is not
Proven: the CMP loads last. CookieScript — +7391 ms; GTM, Facebook, GA, DoubleClick — +2107…+3063 ms, that is, about 4.3 seconds before the CMP.
Proven: the Facebook pixel fired before the CMP, with the URL. www.facebook.com/tr twice, ev=PageView, dl=chilli.ee/et/info/uuendused-platvormil (the full address).
Proven: GA and DoubleClick carry gcs=-. Google’s consent mode is not configured; the requests /g/collect, /ccm/collect, /ccm/s/collect carry gcs=-.
Proven: remarketing fired. google.ee/ads/ga-audiences at +2984 ms.
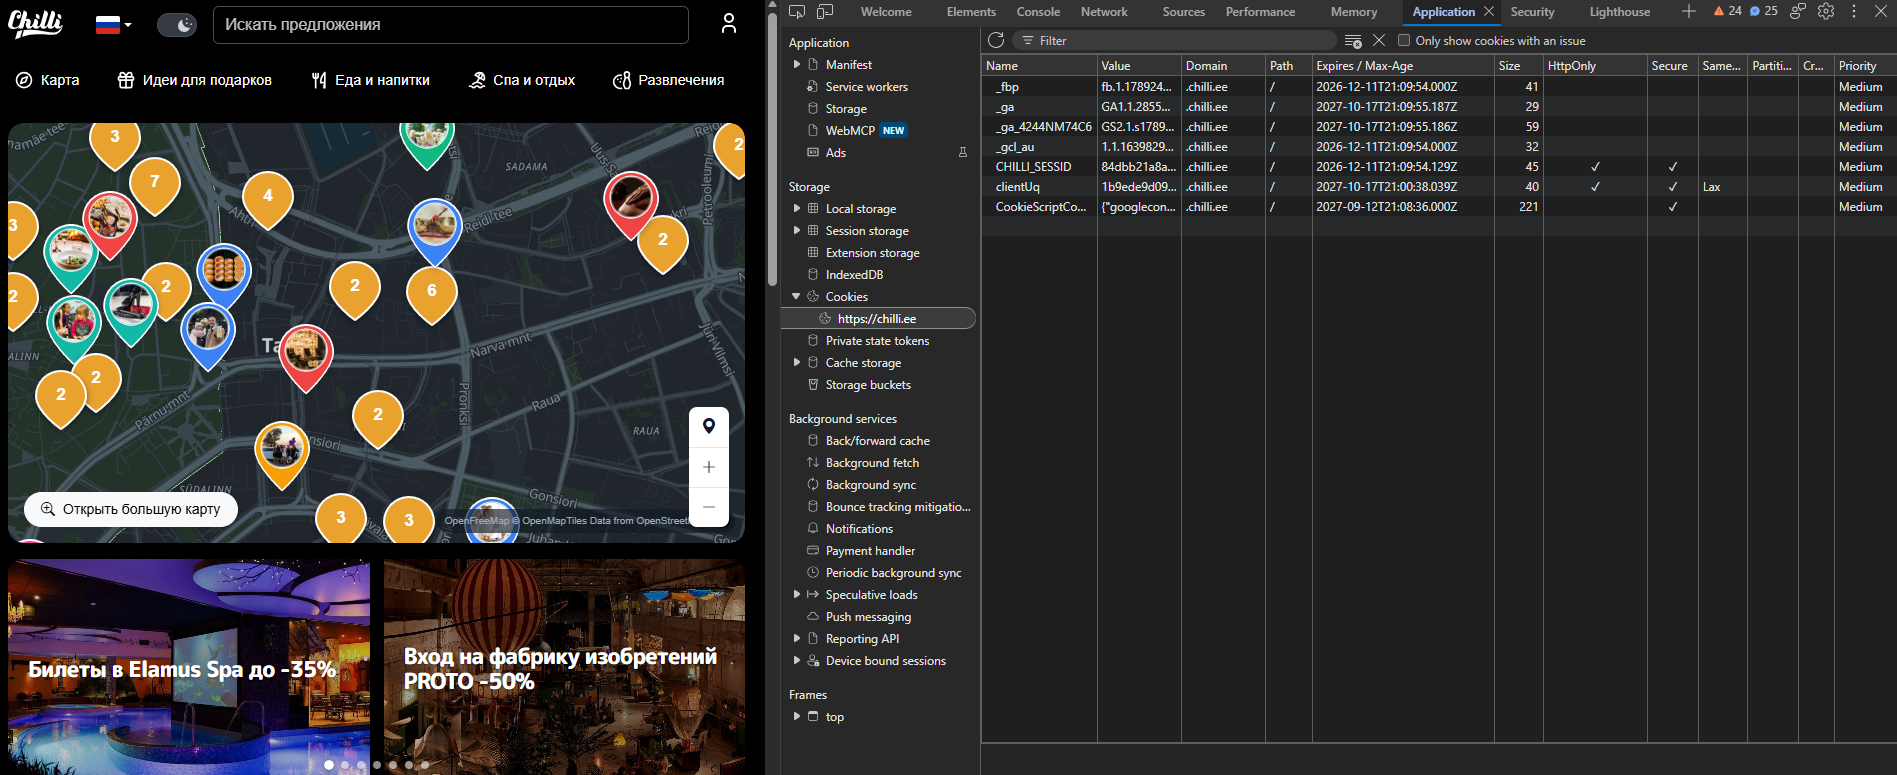
Proven: identifiers are written. The Application panel shows _fbp, _ga, _gcl_au.
Proven: the policy names no recipients. A search of the document finds neither Facebook, Google, DoubleClick, nor CookieScript.
Not established: the consent decision. The user’s choice is not recorded in the capture; the key fact is that the stack ran BEFORE the CMP appeared.
Not proven: the content of the Facebook and GA events. The full bodies in the published file are redacted; ev, id, dl, gcs are readable.
Observation boundaries
The capture covers a single page and records browser behaviour, not server-side processing: what Meta and Google do with the received data is not verified by a browser capture. What is established: the advertising stack ran before the CMP loaded, Facebook received the page URL, GA/DoubleClick went out with no consent signal. Why CookieScript loads so late (initialisation order, a markup error) is not determined from the recording; the fact of the late start is established. The requests to edge.microsoft.com/translate are attributed to capture-tool artefacts. Typekit, jQuery, jsDelivr — to the functional part.
The file is published cleaned of personal data (99 redactions, self-check clean); the load order (the CMP last), the firing of Facebook /tr with the URL, the gcs=- status of GA/DoubleClick and the presence of identification cookies can be verified directly against the published file and the screenshots. The banner and the cookies are from the screenshots (live UI).
The legal assessment is made by the competent authority — Andmekaitse Inspektsioon.
Conclusion
The experiences marketplace keeps the CookieScript consent platform, and the banner offers refusal — in form everything is in place. But in substance the consent mechanism is late: it loads last, at +7391 ms, four seconds after the entire advertising stack has already run. The Facebook pixel sent the page view with the full address twice, GA4 and DoubleClick went out with no consent signal (gcs=-, consent mode not even configured), Google’s remarketing audiences fired. A banner with a «reject» button exists, but by the time the user could press it, the data has already been transferred to Meta and Google.
On top of that the policy is almost empty: it names not a single recipient — neither Facebook, nor Google, nor DoubleClick, nor CookieScript itself — offering refusal only via browser settings. So the visitor gets neither control from the banner (which is late) nor information from the policy (which is empty) about their page view going to advertising networks.
Remediation: load the CookieScript consent platform FIRST and gate the entire advertising stack on the decision, so that the Facebook pixel, GA4, DoubleClick and remarketing do not fire before the choice; configure Google’s consent mode (currently gcs=-), so that when consent has not been given the storages are denied; fill the policy with real content — name all recipients (Facebook/Meta, Google Analytics, Google Ads/DoubleClick, CookieScript) with their purposes and the fields passed; bring the «consent → processing» order to a strict form, in which a banner with refusal actually affects tag loading.
How to verify: download the file and compute its checksum — sha256sum file.har (Linux, macOS) or certutil -hashfile file.har SHA256 (Windows); it must match the one shown. The conclusions apply to the scope of this measurement — see the limitations of the method.
4de2cc870c5deb48083fd403730e31c0be4992beafe8e5e3bf034aff08150906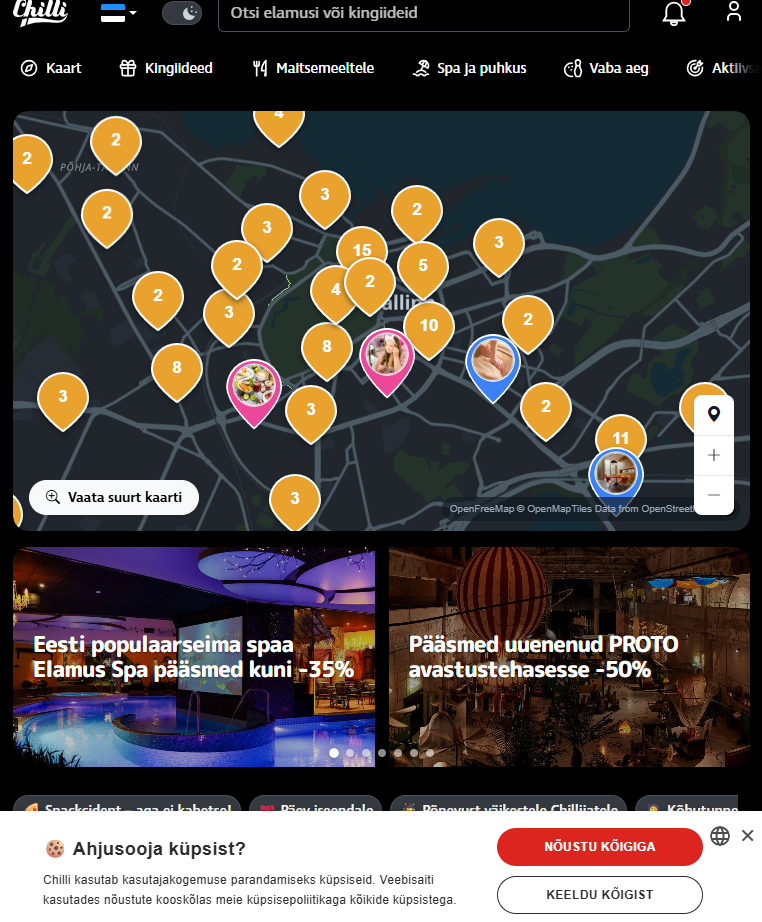
Want a response from the company about this audit? → Open the tool
Fill in once — it will be inserted into every letter below:
All fields are required to print the document — this is a formal requirement of the letter itself (the particulars of an official submission), not data collection: nothing is sent or saved anywhere, it all stays in your browser and disappears when you close the page. See the methodology for details.
RIA DigiDoc — phone · Smart-ID / Mobile-ID
Send this letter directly to the company first — before contacting the regulator it has the right to respond (GDPR Art. 12(3) — 30 days).
Тема: Запрос доступа к персональным данным (ст. 15 GDPR) — chilli.ee

Кому: [укажите адрес компании — DPO / поддержка / юридический отдел]
От: [Ваше имя], [контактный email]

Прошу предоставить доступ к моим персональным данным, обрабатываемым в связи с использованием сайта chilli.ee.

1. Категории данных и цели обработки (ст. 15(1)(a)-(c))
На основании независимого технического анализа сайта прошу подтвердить и подробно раскрыть следующие категории обработки:

1) Платформа управления согласием CookieScript на сайте есть, и баннер даёт отказ («Keeldu kõigist»). Но CMP загружается ПОСЛЕДНЕЙ — на +7391 мс, тогда как весь рекламный и аналитический стек отрабатывает раньше и с фактической передачей данных: контейнер GTM (+2107 мс), Facebook-пиксель (fbevents.js +2130 мс), затем на +2932…+3063 мс — DoubleClick /ccm/s/collect, Google Ads /ccm/collect, GA4 /g/collect, ремаркетинг-аудитории google.ee/ads/ga-audiences, и Facebook-пиксель /tr, срабатывающий ДВАЖДЫ с полным адресом страницы (dl=chilli.ee/et/info/uuendones-platvormil). То есть к моменту, когда CMP наконец загрузилась (+7391 мс), Facebook уже получил просмотр страницы с URL, а Google — событие и сигнал для ремаркетинга. Хуже того: GA4 и DoubleClick идут со статусом gcs=- — режим согласия Google не настроен вовсе (не запрещённое состояние G100, а отсутствие сигнала). Куки _fbp (Facebook) и _gcl_au (Google Ads) записаны на устройство. Баннер с отказом существует, но фактически ни на что не влияет — стек отработал за секунды до появления механизма согласия.

2) Политика использования cookie предельно скудна: она сообщает, что «сайт использует файлы cookie для улучшения обслуживания», и предлагает отказ только через настройки браузера (со ссылкой на aki.ee). Ни один фактический получатель не назван — ни Facebook/Meta (два пикселя, /tr с адресом страницы), ни Google Analytics, ни Google Ads/DoubleClick (реклама и ремаркетинг), ни сама платформа CookieScript. Посетитель, читающий политику, не узнаёт, что его просмотр страницы уходит в Meta и Google с полным URL и используется для рекламного ремаркетинга.


2. Получатели, сроки хранения и передача за пределы ЕЭЗ (ст. 15(1)(c)-(d), 46)
Прошу также указать полный список третьих лиц-получателей, применимые сроки хранения по каждой категории и правовые основания передачи данных за пределы ЕЭЗ, если таковая происходит. Полный технический разбор с доказательствами (сохранённый сетевой журнал, контрольная сумма SHA-256) опубликован по адресу: https://gdpru.eu/en/audits/ee-chilli-ee/

3. Автоматизированная обработка и профилирование (ст. 15(1)(h))
Прошу сообщить, применяется ли в отношении меня автоматизированное принятие решений или профилирование, и если да — раскрыть логику такой обработки.

С уважением,

[Ваше имя]
[контактный email]
[Страна]


[Дата]
Subject: Data access request (GDPR Art. 15) — chilli.ee

To: [insert the company's address — DPO / support / legal department]
From: [Your name], [contact email]

I request access to my personal data processed in connection with the website chilli.ee.

1. Categories of data and purposes of processing (Art. 15(1)(a)-(c))
Based on an independent technical analysis of the site, I request confirmation and detailed disclosure of the following categories of processing:

1) The CookieScript consent management platform is on the site, and the banner offers refusal («Keeldu kõigist»). But the CMP loads LAST — at +7391 ms, whereas the entire advertising and analytics stack runs earlier and with an actual transfer of data: the GTM container (+2107 ms), the Facebook pixel (fbevents.js +2130 ms), then at +2932…+3063 ms — DoubleClick /ccm/s/collect, Google Ads /ccm/collect, GA4 /g/collect, the remarketing audiences google.ee/ads/ga-audiences, and the Facebook pixel /tr, firing TWICE with the full page address (dl=chilli.ee/et/info/uuendused-platvormil). That is, by the time the CMP finally loaded (+7391 ms), Facebook had already received the page view with the URL, and Google an event and a remarketing signal. Worse: GA4 and DoubleClick carry status gcs=- — Google's consent mode is not configured at all (not the denied state G100, but the absence of a signal). The cookies _fbp (Facebook) and _gcl_au (Google Ads) are written to the device. A banner with refusal exists, but in fact it changes nothing — the stack ran seconds before the consent mechanism appeared.

2) The cookie policy is extremely sparse: it states that «the site uses cookies to improve service» and offers refusal only via browser settings (with a link to aki.ee). Not a single actual recipient is named — neither Facebook/Meta (two pixels, /tr with the page address), nor Google Analytics, nor Google Ads/DoubleClick (advertising and remarketing), nor the CookieScript platform itself. A visitor reading the policy does not learn that their page view goes to Meta and Google with the full URL and is used for advertising remarketing.


2. Recipients, retention periods, and transfers outside the EEA (Art. 15(1)(c)-(d), 46)
I also request the full list of third-party recipients, the applicable retention period for each category, and the legal basis for any transfer of data outside the EEA. The full technical audit with evidence (saved network log, SHA-256 checksum) is published at: https://gdpru.eu/en/audits/ee-chilli-ee/

3. Automated processing and profiling (Art. 15(1)(h))
Please state whether I am subject to automated decision-making or profiling, and if so, disclose the logic involved.

Sincerely,

[Your name]
[contact email]
[Country]


[Date]
Teema: Isikuandmetele juurdepääsu taotlus (IKÜM art 15) — chilli.ee

Kellele: [märkige ettevõtte aadress — DPO / tugi / juriidiline osakond]
Kellelt: [Teie nimi], [kontakt-e-post]

Palun anda mulle juurdepääs minu isikuandmetele, mida töödeldakse seoses veebisaidi chilli.ee kasutamisega.

1. Andmekategooriad ja töötlemise eesmärgid (IKÜM art 15(1)(a)-(c))
Sõltumatu tehnilise analüüsi põhjal palun kinnitada ja üksikasjalikult avaldada järgmised töötlemiskategooriad:

1) Veebisaidil on CookieScripti nõusoleku haldamise platvorm ja bänner keeldub («Keeldu kõigist»). Kuid CMP laaditakse +7391 ms-le LAST-ile, samas kui kogu reklaami- ja analüütiline pinu on välja töötatud varem ja tegeliku andmeedastusega: GTM-konteiner (+2107 ms), Facebooki piksel (fbevents.js +2130 ms), seejärel +2932. +3063 ms – DoubleClick /ccm/s/collect, Google Reklaamid / ccm / kollekt, GA4 / g / kogu, uuesti turundatud vaatajaskond google.ee/ads/ga-audiences ja Facebooki piksel /tr käivitasid TWICE täislehe aadressiga (dl=chilli.ee/et/info/uuendones-platvormil). See tähendab, et selleks ajaks, kui CMP lõpuks laadis (+7391 ms), oli Facebook juba saanud URL-iga lehevaate ja Google oli saanud uuesti turundamiseks sündmuse ja signaali. Veelgi hullem, GA4 ja DoubleClick tulevad staatusega gcs=- Google'i nõusolekurežiim ei ole üldse konfigureeritud (mitte G100 keelatud olek, vaid signaali puudumine). Seadmesse salvestatakse küpsised fbp (Facebook) ja gcl au (Google Ads). Keeldumisega bänner on olemas, kuid tegelikult ei mõjuta see midagi - virna töötas sekundit enne nõusoleku mehhanismi ilmumist.

2) Küpsiste poliitika on äärmiselt halb: see teavitab, et „sait kasutab küpsiseid teenuse parandamiseks ja pakub loobumist ainult brauseri seadete kaudu (viide aki.ee-le). Tegelikku saajat ei nimetata – ei Facebook/Meta (kaks pikslit, /tr lehe aadressiga), Google Analytics, Google Ads/DoubleClick (reklaam ja uuesti turundamine) ega CookieScripti platvorm ise. Poliitikat lugev külastaja ei tea, et tema lehe sirvimine läheb Metasse ja Google'isse koos täieliku URL-iga ja seda kasutatakse reklaamide uuesti turundamiseks.


2. Vastuvõtjad, säilitustähtajad ja edastamine väljapoole EMP-d (IKÜM art 15(1)(c)-(d), 46)
Palun samuti esitada täielik loetelu kolmandatest isikutest vastuvõtjatest, iga kategooria puhul kohaldatavad säilitustähtajad ning andmete EMP-välisele edastamisele kohaldatav õiguslik alus, kui selline edastamine toimub. Täielik tehniline analüüs koos tõenditega (salvestatud võrgulogi, SHA-256 kontrollsumma) on avaldatud aadressil: https://gdpru.eu/en/audits/ee-chilli-ee/

3. Automatiseeritud töötlemine ja profiilianalüüs (IKÜM art 15(1)(h))
Palun teatada, kas minu suhtes kohaldatakse automatiseeritud otsuste tegemist või profiilianalüüsi, ning kui jah, siis avaldada selle loogika.

Lugupidamisega,

[Teie nimi]
[kontakt-e-post]
[Riik]


[Kuupäev]
RIA DigiDoc — phone · Smart-ID / Mobile-ID
Where to file: Estonian Data Protection Inspectorate (AKI) — write to info@aki.ee
Important: AKI only handles submissions in Estonian. Translate the letter before sending.
The regulator reviews complaints in its national language. There is an officially translated template from the European Data Protection Board (EDPB) — you can use it instead of or alongside this letter: Official EDPB complaint form (PDF, your language)
Тема: Жалоба на обработку персональных данных — chilli.ee

1. Предмет жалобы
Я подаю жалобу в отношении обработки моих персональных данных сайтом chilli.ee.

2. Обстоятельства
Я посетил сайт chilli.ee и обнаружил признаки несоответствия обработки моих персональных данных требованиям GDPR. Технический разбор, опубликованный на gdpru.eu 13.09.2026 (открытая методология, воспроизводимые измерения), документирует следующие признаки:

1) Платформа управления согласием CookieScript на сайте есть, и баннер даёт отказ («Keeldu kõigist»). Но CMP загружается ПОСЛЕДНЕЙ — на +7391 мс, тогда как весь рекламный и аналитический стек отрабатывает раньше и с фактической передачей данных: контейнер GTM (+2107 мс), Facebook-пиксель (fbevents.js +2130 мс), затем на +2932…+3063 мс — DoubleClick /ccm/s/collect, Google Ads /ccm/collect, GA4 /g/collect, ремаркетинг-аудитории google.ee/ads/ga-audiences, и Facebook-пиксель /tr, срабатывающий ДВАЖДЫ с полным адресом страницы (dl=chilli.ee/et/info/uuendones-platvormil). То есть к моменту, когда CMP наконец загрузилась (+7391 мс), Facebook уже получил просмотр страницы с URL, а Google — событие и сигнал для ремаркетинга. Хуже того: GA4 и DoubleClick идут со статусом gcs=- — режим согласия Google не настроен вовсе (не запрещённое состояние G100, а отсутствие сигнала). Куки _fbp (Facebook) и _gcl_au (Google Ads) записаны на устройство. Баннер с отказом существует, но фактически ни на что не влияет — стек отработал за секунды до появления механизма согласия.

2) Политика использования cookie предельно скудна: она сообщает, что «сайт использует файлы cookie для улучшения обслуживания», и предлагает отказ только через настройки браузера (со ссылкой на aki.ee). Ни один фактический получатель не назван — ни Facebook/Meta (два пикселя, /tr с адресом страницы), ни Google Analytics, ни Google Ads/DoubleClick (реклама и ремаркетинг), ни сама платформа CookieScript. Посетитель, читающий политику, не узнаёт, что его просмотр страницы уходит в Meta и Google с полным URL и используется для рекламного ремаркетинга.

Полная техническая документация опубликована по адресу: https://gdpru.eu/en/audits/ee-chilli-ee/

3. Положения GDPR, соблюдение которых прошу проверить
ePrivacy — Директива 2002/58/EC, ст. 5(3) (в связке с GDPR Art. 6(1)(a)) — весь рекламный стек отрабатывает до загрузки CMP; GDPR Art. 13(1)(e) — получатели не раскрыты (политика почти пустая)

4. Требование
Прошу проверить изложенные обстоятельства и, если несоответствие подтвердится, принять меры, предусмотренные статьёй 58(2) GDPR.

5. Приложения
Полная доказательная база — HAR-файл, контрольная сумма SHA-256 и цитата из политики конфиденциальности сайта, документирующая указанное противоречие — опубликована и проверяема по ссылке в пункте 2 выше.

С уважением,

[Ваше имя]
[контактный email]
[Страна]


[Дата]
Subject: Complaint regarding personal data processing — chilli.ee

1. Subject of the complaint
I am filing a complaint regarding the processing of my personal data by the website chilli.ee.

2. Circumstances
I visited the website chilli.ee and found indications that the processing of my personal data does not comply with the GDPR. The technical analysis published on gdpru.eu on 13 September 2026 (open methodology, reproducible measurements) documents the following indications:

1) The CookieScript consent management platform is on the site, and the banner offers refusal («Keeldu kõigist»). But the CMP loads LAST — at +7391 ms, whereas the entire advertising and analytics stack runs earlier and with an actual transfer of data: the GTM container (+2107 ms), the Facebook pixel (fbevents.js +2130 ms), then at +2932…+3063 ms — DoubleClick /ccm/s/collect, Google Ads /ccm/collect, GA4 /g/collect, the remarketing audiences google.ee/ads/ga-audiences, and the Facebook pixel /tr, firing TWICE with the full page address (dl=chilli.ee/et/info/uuendused-platvormil). That is, by the time the CMP finally loaded (+7391 ms), Facebook had already received the page view with the URL, and Google an event and a remarketing signal. Worse: GA4 and DoubleClick carry status gcs=- — Google's consent mode is not configured at all (not the denied state G100, but the absence of a signal). The cookies _fbp (Facebook) and _gcl_au (Google Ads) are written to the device. A banner with refusal exists, but in fact it changes nothing — the stack ran seconds before the consent mechanism appeared.

2) The cookie policy is extremely sparse: it states that «the site uses cookies to improve service» and offers refusal only via browser settings (with a link to aki.ee). Not a single actual recipient is named — neither Facebook/Meta (two pixels, /tr with the page address), nor Google Analytics, nor Google Ads/DoubleClick (advertising and remarketing), nor the CookieScript platform itself. A visitor reading the policy does not learn that their page view goes to Meta and Google with the full URL and is used for advertising remarketing.

Full technical documentation is published at: https://gdpru.eu/en/audits/ee-chilli-ee/

3. GDPR provisions I ask you to examine
ePrivacy — Directive 2002/58/EC, Art. 5(3) (in conjunction with GDPR Art. 6(1)(a)) — the entire advertising stack runs before the CMP loads; GDPR Art. 13(1)(e) — recipients not disclosed (an almost empty policy)

4. Request
I request that you examine the circumstances described and, if non-compliance is confirmed, apply the measures provided for in Article 58(2) GDPR.

5. Attachments
The full evidence base — the HAR file, its SHA-256 checksum and the quotation from the site's privacy policy documenting the stated contradiction — is published and verifiable at the link in point 2 above.

Sincerely,

[Your name]
[contact email]
[Country]


[Date]
1. Kaebuse ese
Esitan kaebuse seoses minu isikuandmete töötlemisega veebisaidil chilli.ee.

2. Asjaolud
Külastasin veebisaiti chilli.ee ja tuvastasin märke sellest, et minu isikuandmete töötlemine ei vasta isikuandmete kaitse üldmääruse (IKÜM) nõuetele. Tehniline analüüs, mis on avaldatud aadressil gdpru.eu 13.09.2026 (avatud metoodika, korratavad mõõtmised), dokumenteerib järgmist:

1) Veebisaidil on CookieScripti nõusoleku haldamise platvorm ja bänner keeldub («Keeldu kõigist»). Kuid CMP laaditakse +7391 ms-le LAST-ile, samas kui kogu reklaami- ja analüütiline pinu on välja töötatud varem ja tegeliku andmeedastusega: GTM-konteiner (+2107 ms), Facebooki piksel (fbevents.js +2130 ms), seejärel +2932. +3063 ms – DoubleClick /ccm/s/collect, Google Reklaamid / ccm / kollekt, GA4 / g / kogu, uuesti turundatud vaatajaskond google.ee/ads/ga-audiences ja Facebooki piksel /tr käivitasid TWICE täislehe aadressiga (dl=chilli.ee/et/info/uuendones-platvormil). See tähendab, et selleks ajaks, kui CMP lõpuks laadis (+7391 ms), oli Facebook juba saanud URL-iga lehevaate ja Google oli saanud uuesti turundamiseks sündmuse ja signaali. Veelgi hullem, GA4 ja DoubleClick tulevad staatusega gcs=- Google'i nõusolekurežiim ei ole üldse konfigureeritud (mitte G100 keelatud olek, vaid signaali puudumine). Seadmesse salvestatakse küpsised fbp (Facebook) ja gcl au (Google Ads). Keeldumisega bänner on olemas, kuid tegelikult ei mõjuta see midagi - virna töötas sekundit enne nõusoleku mehhanismi ilmumist.

2) Küpsiste poliitika on äärmiselt halb: see teavitab, et „sait kasutab küpsiseid teenuse parandamiseks ja pakub loobumist ainult brauseri seadete kaudu (viide aki.ee-le). Tegelikku saajat ei nimetata – ei Facebook/Meta (kaks pikslit, /tr lehe aadressiga), Google Analytics, Google Ads/DoubleClick (reklaam ja uuesti turundamine) ega CookieScripti platvorm ise. Poliitikat lugev külastaja ei tea, et tema lehe sirvimine läheb Metasse ja Google'isse koos täieliku URL-iga ja seda kasutatakse reklaamide uuesti turundamiseks.

Täielik tehniline dokumentatsioon on avaldatud aadressil: https://gdpru.eu/en/audits/ee-chilli-ee/

3. Sätted, mille järgimist palun kontrollida
e-privaatsus - direktiiv 2002/58/EÜ, artikli 5 lõige 3 (koostoimes GDPRi artikli 6 lõike 1 punktiga a) - kogu reklaamikomplekt töötatakse välja enne CMP laadimist; GDPR artikli 13 lõike 1 punkt e – saajad avalikustamata (poliitika peaaegu tühi)

4. Nõue
Palun kontrollida kirjeldatud asjaolusid ja mittevastavuse kinnitamisel kohaldada IKÜM artikli 58 lõikes 2 ette nähtud meetmeid.

5. Lisad
Täielik tõendusmaterjal — HAR-fail, kontrollsumma SHA-256 ning veebisaidi privaatsuspoliitika tsitaat, mis dokumenteerib nimetatud vastuolu — on avaldatud ja kontrollitav punktis 2 viidatud lingil.

Lugupidamisega,

[Teie nimi]
[kontakt-e-post]
[Riik]


[Kuupäev]