
The Bigbank website — four page loads, 1132 requests. The first layer of the banner has an equivalent 'Nõustu vajalike küpsistega' button, and optional categories are switched off by default. Google Analytics and Google Ads run only in denied mode from the first second, with a new identifier on every page, and the bank itself describes these anonymous signals in its cookie rules. The data processing policy is complete. No violations were recorded.
Request timeline
Declared versus actual
Transfer timings
Server-side Google Tag Manager container on the bank's subdomain.
Google Ads, gcs=G100.
GA4 page_view, gcs=G100, a new identifier.
cookie_consent_completed, gcs=G100.
Detected trackers
- Google Analytics 4 (G-F45HM0NL5B) via a server-side container on sgtm.bigbank.ee — every request with gcs=G100, a new identifier on every page. The denial is respected
- Google Ads AW-1041357430 (pagead2.googlesyndication.com) — every request with gcs=G100. The denial is respected
- Google Tag Manager (GTM-KZGVK5K) — container on every page; server-side container — sgtm.bigbank.ee
- The bank's own cookie banner (PolarisCookieNotification) — refusal on the first layer exists, categories switched off by default; the decision is sent as a cookie_consent_completed event
- First party: www.bigbank.ee, static.bigbank.ee, static.bigbank.eu, sgtm.bigbank.ee
Context
bigbank.ee is the website of Bigbank: accounts, loans, deposits and an investor section. The controller is Bigbank AS (Narva mnt 11, Tallinn), and the group has a data protection officer. The cookie banner is the bank’s own, and Google tags run through a server-side container on the sgtm.bigbank.ee subdomain.
The measurement is a single capture of four page loads: the Estonian and Russian homepage, then both again. In total, 1132 requests, most of them the bank’s static files.
Processing is described by the cookie rules (in force from 29.01.2026) and the client data processing principles.
Who receives data directly
Google — Analytics via the bank’s server-side container, and Ads, in denied mode. No other third-party recipients in the capture.
Declared versus actual
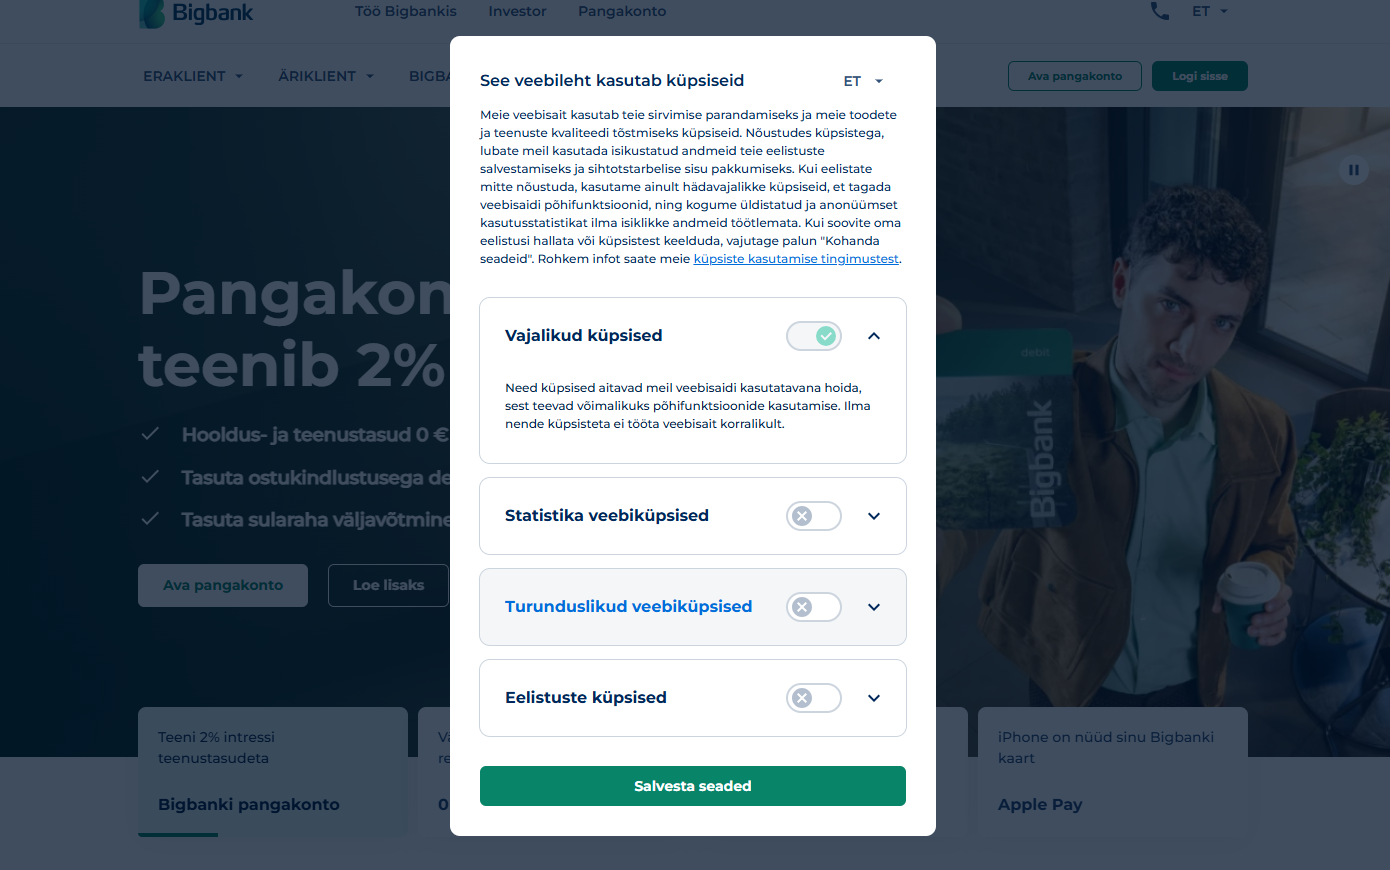
First — the choice is fair. The first layer has three equivalent buttons, and refusal — “Nõustu vajalike küpsistega” — takes one click. In the settings, all optional categories are switched off.
Second — Google runs in denied mode. Before and after the decision, every request to Google Analytics and Google Ads carries gcs=G100, with a new identifier on every page. The bank itself states in its cookie rules that on refusal Google receives anonymous consent mode signals — and the traffic confirms this.
Third — the documents are complete. The controller, the data protection officer, purposes and legal bases, recipients, transfers outside the EEA with safeguards, retention periods, profiling and automated decisions, all rights and the right to lodge a complaint with the Andmekaitse Inspektsioon.
Consent: what is proven and what is not
Proven: there is a refusal on the first layer. The “Nõustu vajalike küpsistega” button on screenshot 1.
Proven: optional categories are switched off by default. Screenshot 3.
Proven: Google respects the denial. Every request carries gcs=G100; the identifiers differ from page to page.
Proven: the decision is recorded. A cookie_consent_completed event at +119.1 s, after which consent mode remains in denied state.
Not established: what happens after consent. The “Nõustu kõigiga” scenario was not examined.
Boundaries of this observation
The measurement covers the homepage in Estonian and Russian. Internet banking, applications and calculators were not examined. The observation records browser behavior, not server-side processing; what the server-side container passes on to Google is not visible from the browser. The file has been published cleaned: Cookie headers were removed. Google identifiers are not reproduced in full in this review.
Legal assessment falls to the competent authority — the Andmekaitse Inspektsioon, which is named in the data processing principles themselves.
Conclusion
Bigbank has configured consent carefully: an equivalent refusal on the first layer, optional categories switched off by default, Google only in denied mode, and the anonymous signals Google receives on refusal are honestly described in the cookie rules. No violations were recorded.
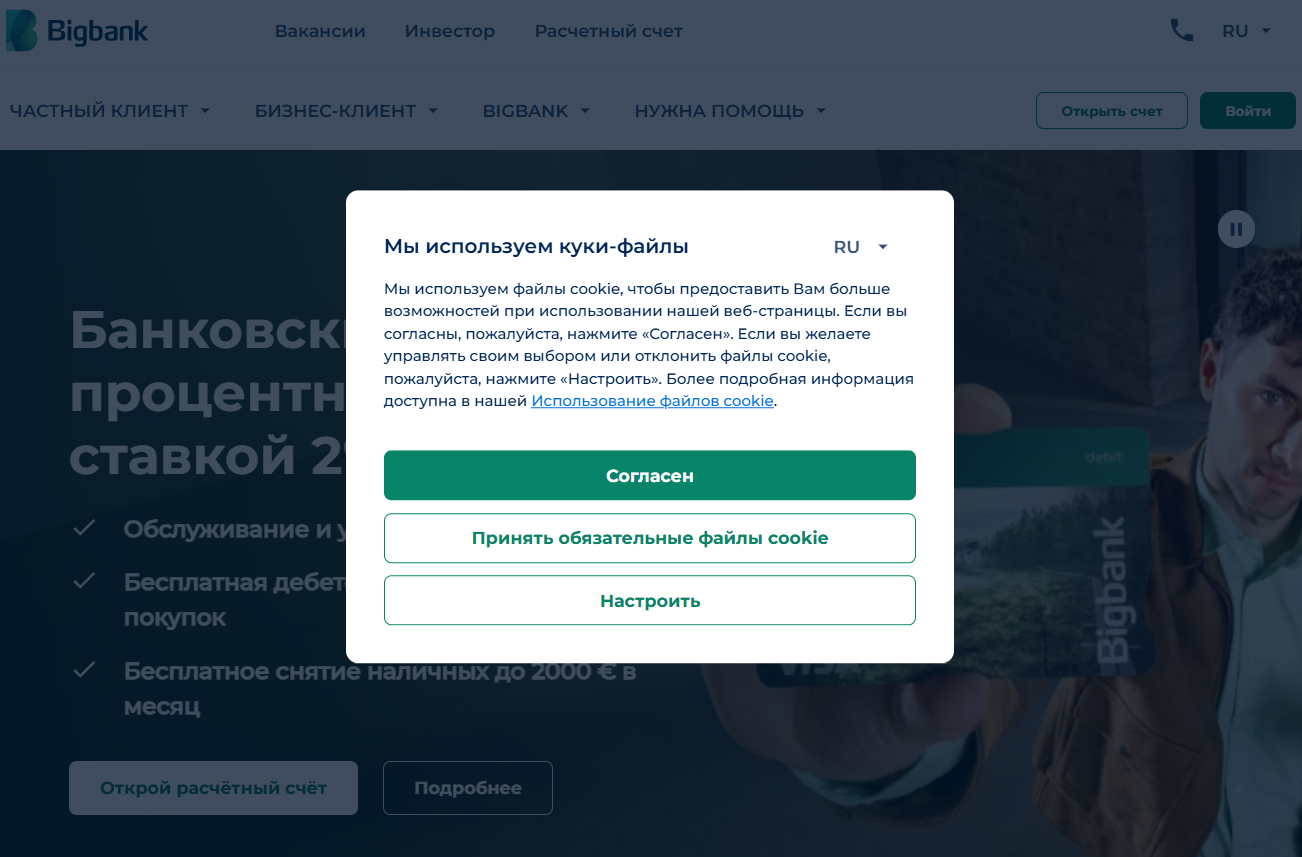
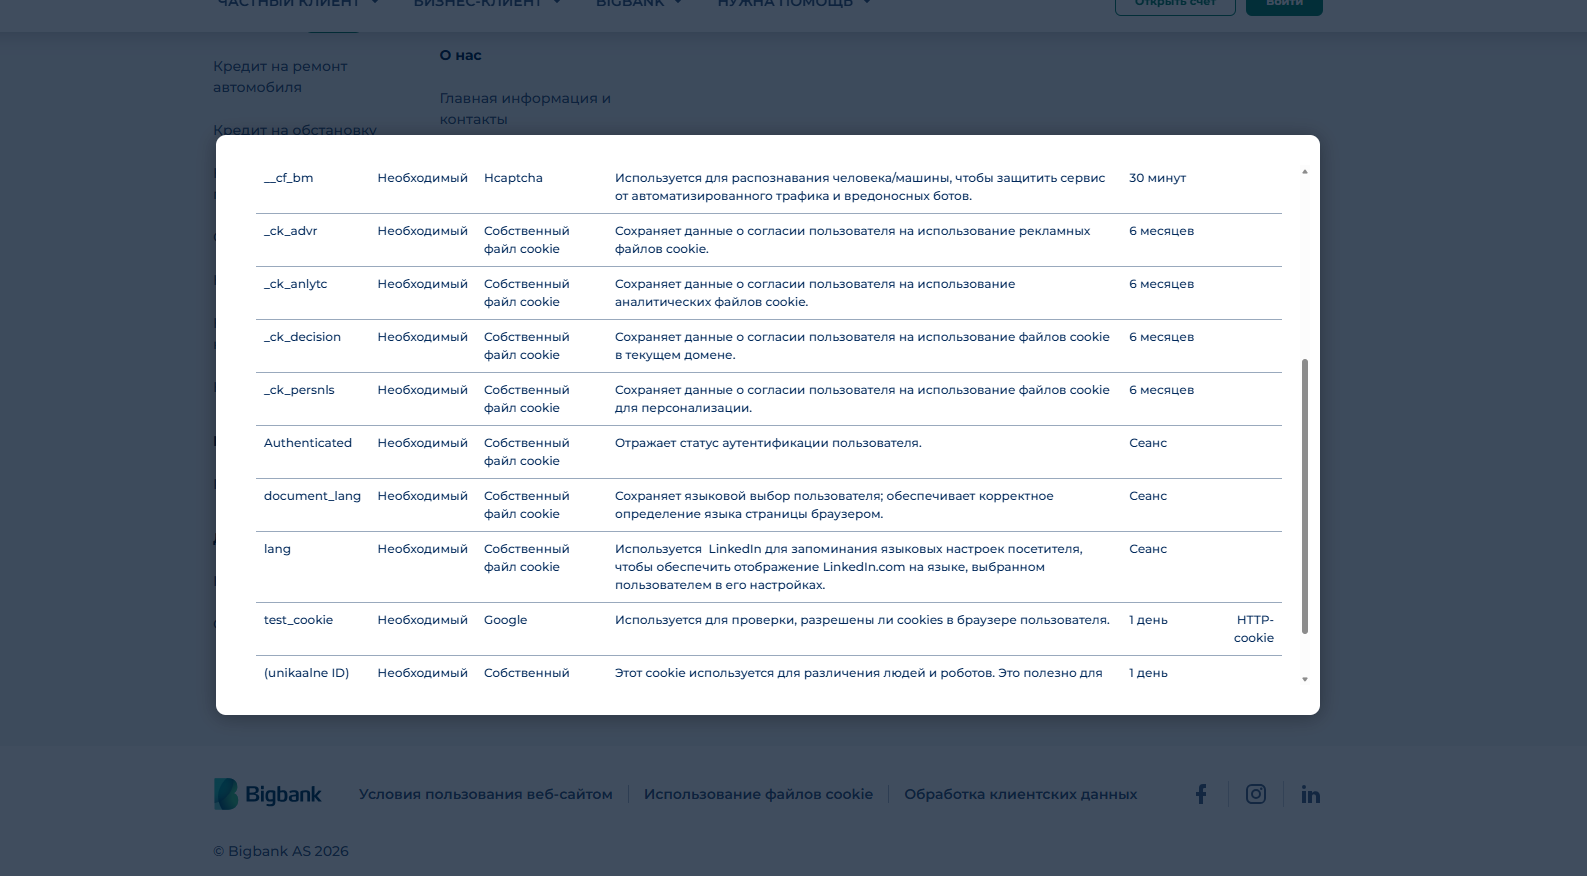
Suggestion: do not call Google Analytics statistics cookies “anonymous” — after consent they work with an identifier; remove LinkedIn’s lang from the table of necessary cookies if LinkedIn is not used on the site; in the Russian banner text, state that refusal is possible with the “Принять обязательные файлы cookie” button, not only via “Настроить”.
How to verify: download the file and compute its checksum — sha256sum file.har (Linux, macOS) or certutil -hashfile file.har SHA256 (Windows); it must match the one shown. The conclusions apply to the scope of this measurement — see the limitations of the method.
d7815d8ad92e293a20ab8c62110a04551541a6a995157a295be7e4b6589c4fe2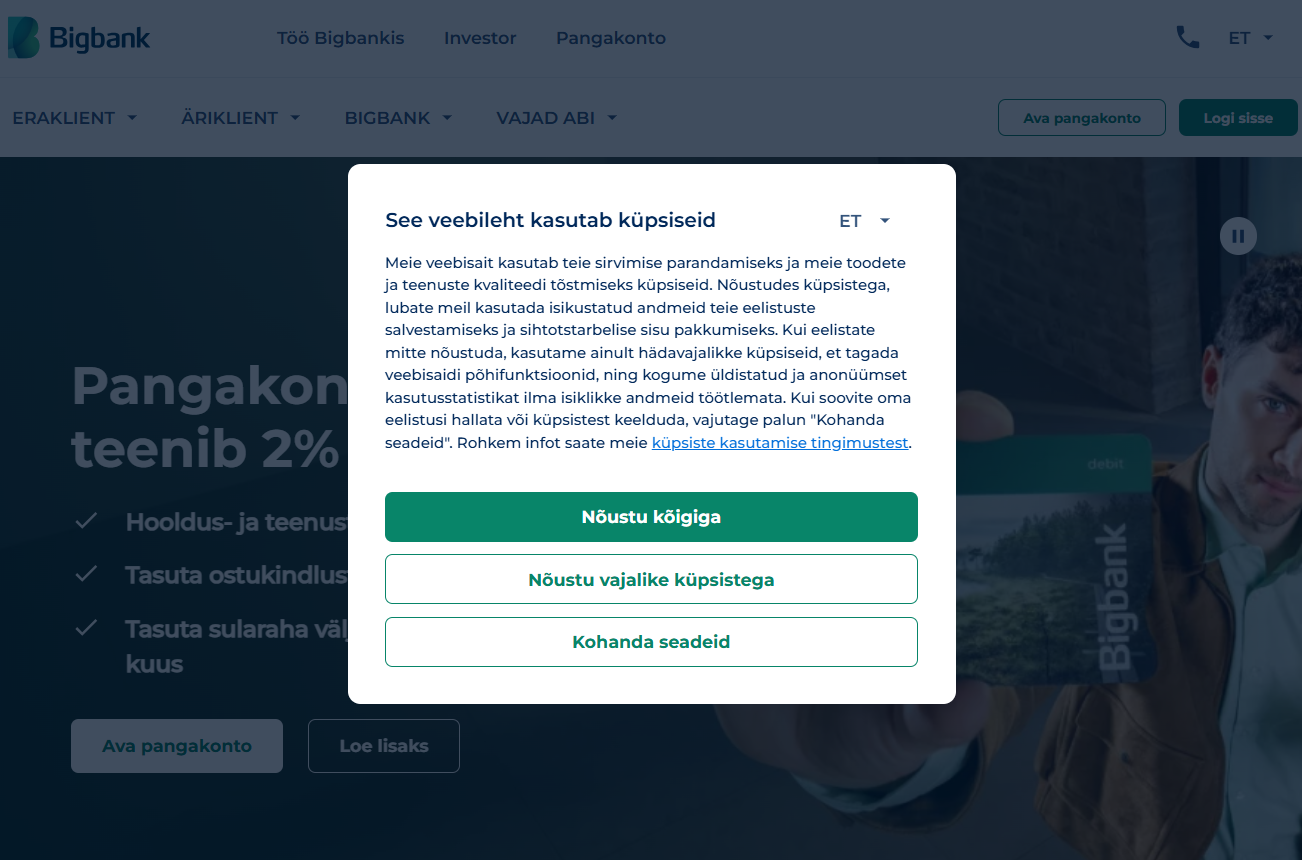
Want a response from the company about this audit? → Open the tool
Fill in once — it will be inserted into every letter below:
All fields are required to print the document — this is a formal requirement of the letter itself (the particulars of an official submission), not data collection: nothing is sent or saved anywhere, it all stays in your browser and disappears when you close the page. See the methodology for details.
RIA DigiDoc — phone · Smart-ID / Mobile-ID
Send this letter directly to the company first — before contacting the regulator it has the right to respond (GDPR Art. 12(3) — 30 days).
Тема: Запрос доступа к персональным данным (ст. 15 GDPR) — bigbank.ee

Кому: [укажите адрес компании — DPO / поддержка / юридический отдел]
От: [Ваше имя], [контактный email]

Прошу предоставить доступ к моим персональным данным, обрабатываемым в связи с использованием сайта bigbank.ee.

1. Категории данных и цели обработки (ст. 15(1)(a)-(c))
Прошу предоставить информацию по всем категориям, целям и получателям обработки моих данных на этом сайте — независимо от того, выявлены ли на сегодняшний день какие-либо несоответствия.

2. Получатели, сроки хранения и передача за пределы ЕЭЗ (ст. 15(1)(c)-(d), 46)
Прошу также указать полный список третьих лиц-получателей, применимые сроки хранения по каждой категории и правовые основания передачи данных за пределы ЕЭЗ, если таковая происходит. Полный технический разбор с доказательствами (сохранённый сетевой журнал, контрольная сумма SHA-256) опубликован по адресу: https://gdpru.eu/en/audits/ee-bigbank-ee/

3. Автоматизированная обработка и профилирование (ст. 15(1)(h))
Прошу сообщить, применяется ли в отношении меня автоматизированное принятие решений или профилирование, и если да — раскрыть логику такой обработки.

С уважением,

[Ваше имя]
[контактный email]
[Страна]


[Дата]
Subject: Data access request (GDPR Art. 15) — bigbank.ee

To: [insert the company's address — DPO / support / legal department]
From: [Your name], [contact email]

I request access to my personal data processed in connection with the website bigbank.ee.

1. Categories of data and purposes of processing (Art. 15(1)(a)-(c))
I request information on all categories, purposes, and recipients of my data processed on this site — regardless of whether any non-compliance has been identified to date.

2. Recipients, retention periods, and transfers outside the EEA (Art. 15(1)(c)-(d), 46)
I also request the full list of third-party recipients, the applicable retention period for each category, and the legal basis for any transfer of data outside the EEA. The full technical audit with evidence (saved network log, SHA-256 checksum) is published at: https://gdpru.eu/en/audits/ee-bigbank-ee/

3. Automated processing and profiling (Art. 15(1)(h))
Please state whether I am subject to automated decision-making or profiling, and if so, disclose the logic involved.

Sincerely,

[Your name]
[contact email]
[Country]


[Date]
Teema: Isikuandmetele juurdepääsu taotlus (IKÜM art 15) — bigbank.ee

Kellele: [märkige ettevõtte aadress — DPO / tugi / juriidiline osakond]
Kellelt: [Teie nimi], [kontakt-e-post]

Palun anda mulle juurdepääs minu isikuandmetele, mida töödeldakse seoses veebisaidi bigbank.ee kasutamisega.

1. Andmekategooriad ja töötlemise eesmärgid (IKÜM art 15(1)(a)-(c))
Palun esitada teave kõigi minu andmete töötlemise kategooriate, eesmärkide ja vastuvõtjate kohta sellel veebisaidil — sõltumata sellest, kas praeguseks on tuvastatud mingeid mittevastavusi.

2. Vastuvõtjad, säilitustähtajad ja edastamine väljapoole EMP-d (IKÜM art 15(1)(c)-(d), 46)
Palun samuti esitada täielik loetelu kolmandatest isikutest vastuvõtjatest, iga kategooria puhul kohaldatavad säilitustähtajad ning andmete EMP-välisele edastamisele kohaldatav õiguslik alus, kui selline edastamine toimub. Täielik tehniline analüüs koos tõenditega (salvestatud võrgulogi, SHA-256 kontrollsumma) on avaldatud aadressil: https://gdpru.eu/en/audits/ee-bigbank-ee/

3. Automatiseeritud töötlemine ja profiilianalüüs (IKÜM art 15(1)(h))
Palun teatada, kas minu suhtes kohaldatakse automatiseeritud otsuste tegemist või profiilianalüüsi, ning kui jah, siis avaldada selle loogika.

Lugupidamisega,

[Teie nimi]
[kontakt-e-post]
[Riik]


[Kuupäev]