
A car classifieds portal — a single capture across 22 pages, 2291 requests, 23 nodes. The OneTrust consent platform loads first on almost every page, and the stored TCF consent string encodes a full refusal: zero consent across all 24 purposes, zero on legitimate interest; the browser also sent DNT: 1. Despite this, the Facebook / Meta Pixel sends a PageView with a browser identifier on /ostuabi/ pages, Adform transmits screen resolution, language and device type, and Google DoubleClick sends an impression tracker. Facebook, meanwhile, is named neither in the policy nor even in the TCF vendor list. The binding data-protection terms state that the operator does not transfer data to third parties and does not transfer it outside the EU.
Request timeline
Declared versus actual
Transfer timings
OneTrust (CMP ID 28), first on almost every page. Stored TCF consent — zero across all purposes.
fbevents.js and the pixel configuration, despite zero consent.
PageView, pixel ID 323626075634293, fbp browser identifier, /ostuabi/ URL, referrer, timezone, screen. 200 response.
adfscript, bn=89789059.
adfserve: language, screen resolution 1920x1080, device type, slot dimensions. cmpgdprconsent with zero content. 302→gif response.
1x1inv=1 pixel on the news page, bn=90066863.
Impression tracker /ddm/trackimp. 302→gif response.
DoubleClick ad creative, pulled from reklaam2.auto24.ee/images.
Detected trackers
- OneTrust (cdn.cookielaw.org, privacyportal-eu.onetrust.com) — consent management platform (CMP ID 28); 290 requests, loads first on almost every page
- Facebook / Meta Pixel (connect.facebook.net, www.facebook.com/tr) — pixel ID 323626075634293; sends PageView with the fbp browser identifier, the page URL and referrer, timezone and screen parameters on /ostuabi/ pages; absent from the TCF vendor list
- Adform (track.adform.net, s1.adform.net, site.adform.com) — advertising network; adfserve transmits language, screen resolution 1920x1080, device type and ad-slot dimensions, and carries the cmpgdprconsent consent string; on news pages — an invisible 1x1 pixel (bn=90066863, 1x1inv=1)
- Google DoubleClick (ad.doubleclick.net, s0.2mdn.net) — /ddm/trackimp impression tracker and ad creative
- media.adcanvas.com — ad asset pulled from the OneTrust panel templates
- www.gstatic.com — Google static, pulled from the OneTrust panel templates
- reklaam2.auto24.ee — the operator's own ad server (first party)
- Baltic Classifieds Group infrastructure (img13.img-bcg.eu, a24-static.img-bcg.eu, img.auto24.ee, img-kb.ee, img-osta.ee, img-kv.ee, static.img-city24.ee, www.kuldnebors.ee, imgsrv.kuldnebors.ee, www.osta.ee) — shared image CDNs and sister sites of the group, functional delivery
Indicators of GDPR non-compliance
- ePrivacy — Directive 2002/58/EC, Art. 5(3) (in conjunction with GDPR Art. 6(1)(a)) — tracking despite a recorded refusal of consentThe portal has the OneTrust consent platform installed, and it loads first on almost every page. The stored TCF v2 consent string (CMP ID 28, created 2026-09-05, the day before the capture) encodes zero consent: all 24 processing purposes are 0, all legitimate-interest bases are 0. The browser additionally sent the DNT: 1 header (in 1013 requests). Despite this, third-party trackers fire and transmit data. On /ostuabi/ pages the Facebook / Meta Pixel (ID 323626075634293) sends a PageView event with the fbp browser identifier, the page URL and referrer, timezone and screen parameters — the pixel is not conditioned on consent at all and fires unconditionally. At +1032 ms Adform transmits language, screen resolution 1920x1080, device type and ad-slot dimensions; it carries a cmpgdprconsent string with zero content — that is, the 'no consent' signal itself is passed, yet the request with device data goes out anyway. Google DoubleClick sends the /ddm/trackimp impression tracker. All requests are delivered (FB /tr → 200, DoubleClick → 302→gif, Adform → 302→gif).
- GDPR Art. 5(1)(a) / Art. 13(1)(e) — transparency and recipients, a contradiction within the operator's own documentsAllePal's binding data-protection terms (revision of 10.02.2026), in clause 4.1, state plainly: 'Me ei edasta Isikuandmeid kolmandatele isikutele' (we do not transfer personal data to third parties, except on a legal basis) and 'Samuti me ei edasta Isikuandmeid Euroopa Liidust väljapoole' (we also do not transfer personal data outside the EU). The wording is confirmed on the live site. In fact data goes to Meta (US) via the Facebook Pixel, to Google (US) via DoubleClick, and to Adform. The list of processors in clause 4.2 is reduced to categories ('accounting and others'); no web recipient is named. The cookie-use terms (clause 1.4) admit that behavioural data 'may be shared with advertising networks and ad service providers', and the partner list at auto24.ee/cookies names Google and Adform. But Facebook / Meta is named nowhere — neither in the binding terms nor in the TCF vendor list (Meta is absent from it). So the transfer to Meta is undisclosed at every level, while clause 4.1 denies both it and the transfer to Google.
Context
auto24.ee is a car classifieds portal operated by AllePal OÜ, registry code 12209337, Pärnu mnt 141, Tallinn 11314; part of the Baltic Classifieds group. Under its own terms, AllePal acts as the controller. Contact is info@auto24.ee, +372 733 7230; the document does not name a dedicated data-protection officer. The site is served via Cloudflare and sets a full set of security headers (HSTS, Content-Security-Policy, Referrer-Policy, Permissions-Policy, nosniff, X-Frame-Options) — at the header level there is nothing to object to.
The capture is a single recording across 22 pages: the homepage, the buying, financing, forum, news, catalogue, rental and listing sections, and the new- and used-car pages. In total 2291 requests, 23 nodes, about eight minutes, recorded on 6 September 2026, in a browser with language ru. The site runs the OneTrust consent management platform (CMP ID 28); there is no Google analytics on the portal — the tracker set is advertising.
Processing is described by the operator’s documents: the AllePal data-protection terms (revision of 10.02.2026), the cookie-use terms, and an external partner list at auto24.ee/cookies.
Who receives data directly
Meta (Facebook Pixel), Google (DoubleClick), Adform. Functionally — the operator’s own ad server reklaam2.auto24.ee and the shared Baltic Classifieds group infrastructure.
Declared vs. actual
AllePal’s document is tidy, but on data transfer it is categorical — and it is in that categoricalness that the discrepancy arises.
First — trackers fire under a recorded refusal. Here the load order is correct: the OneTrust consent platform starts first on almost every one of the 22 pages, before any third-party tracker. The problem is not the order but that the active consent is negative, and that does not stop the trackers. The stored TCF v2 consent string (CMP ID 28, created the day before the capture) encodes zero consent: all twenty-four processing purposes are set to 0, all legitimate interest to 0. The browser additionally sent the DNT: 1 header. In this state the Facebook / Meta Pixel, on the buying-help pages /ostuabi/, sends Meta a PageView event with the fbp browser identifier, the page URL and referrer, timezone and screen parameters. Adform transmits language, screen resolution, device type and ad-slot dimensions. Google DoubleClick sends an impression tracker. All three recipients receive requests despite the refusal.
Second — Adform transmits data and the refusal signal at once. The Adform request is curiously arranged: it carries cmpgdpr=1 and a cmpgdprconsent string with zero content — that is, it correctly tells the partner there is no consent. But together with that signal, the same request carries screen resolution 1920x1080, language, device type and ad-slot parameters. Passing the ’no consent’ signal and passing the device data happen in one and the same request.
Third — Facebook is named nowhere, yet data goes to Meta. The binding data-protection terms in clause 4.1 deny transfers to third parties and outside the EU. The cookie-use terms are more honest: clause 1.4 admits that targeting cookies show personalised advertising and that data ‘may be shared with advertising networks and ad service providers’, and the partner list names Google and Adform. But Facebook / Meta is absent there too: it is nowhere in the binding terms, nowhere in the partner list, and not even in the TCF vendor list on which the consent panel is built. And it is precisely to Meta that a persistent browser identifier goes, together with the URL of the page being visited. A recipient whose transfer the documents deny is, on top of that, undisclosed at every level.
Fourth — a contradiction between the terms and the facts regarding the EU. Clause 4.1 states that data is not transferred outside the EU. The Facebook Pixel sends data to Meta, DoubleClick to Google; both recipients are in the US. The document denies exactly the kind of transfer that the capture records.
Consent: what is proven and what is not
Proven: the active consent is a refusal. The stored TCF v2 consent string reads directly: version 2, CMP ID 28, all twenty-four processing purposes — 0, all legitimate interest — 0. The created and updated timestamps are 2026-09-05, meaning the consent in this state existed before the capture began; the banner was not touched during the session itself.
Proven: the consent platform loads before the trackers. On almost every one of the 22 pages cdn.cookielaw.org starts in the +267…+530 ms range, before the first third-party request. So the trackers fire not because of an earlier load, but in spite of the consent state.
Proven: the trackers transmit data in this state. Facebook /tr goes out at +1024 ms with a PageView event and the fbp identifier; Adform adfserve at +1524 ms with screen resolution and device type; DoubleClick /ddm/trackimp is an impression tracker. All requests are delivered (200 and 302→gif responses).
Proven: the browser signalled a refusal to be tracked. The DNT: 1 header is present in 1013 requests of the session, including the initial page document. It had no effect on the composition or volume of the transfers.
Not proven, and not required: processing on the recipients’ side. How Meta, Google and Adform handle the data they receive on their side, and whether they honour the zero consent string server-side, is not verified by a browser-level capture. What matters is that the data was in fact sent to them under an active refusal.
Observation boundaries
The capture covers 22 pages of the portal and records browser behaviour, not the services’ internal workings: server-side processing, contracts with recipients and their settings are not verified by a browser-level capture. The resources media.adcanvas.com and www.gstatic.com in the recording are pulled from the OneTrust panel templates and are resources of the CMP itself, not advertising requests. The operator’s own ad server reklaam2.auto24.ee and the shared Baltic Classifieds group infrastructure (the img-bcg.eu image CDNs, the sister sites kv, osta, kuldnebors, city24) are classified as the group’s functional delivery.
The file is published redacted of personal data: cookie values in requests have been removed. Response bodies and markup are preserved, so tag insertion, load order and request parameters are verified directly against the published file. The Facebook pixel identifier and the fbp marker are established from the requests themselves; the TCF consent string is decoded from the parameter that Adform passes in its requests. Service identification relies on domains and URL schemes: Meta — by connect.facebook.net and facebook.com/tr with the pixel identifier; Adform — by adform.net and the adfserve scheme; Google — by doubleclick.net and 2mdn.net.
The legal assessment is made by the competent authority — Andmekaitse Inspektsioon, whose supervision is named in clause 5.2.8 of the terms themselves.
Conclusion
The car classifieds portal has built the correct load order — the OneTrust consent platform starts first — but the consent state is negative, and the trackers ignore it. The stored TCF string encodes a full refusal, the browser sends DNT: 1, yet the Facebook / Meta Pixel sends Meta a PageView event with a browser identifier, Adform transmits screen resolution, language and device type, and Google DoubleClick an impression tracker. Adform even manages, in a single request, to pass both the ’no consent’ signal and the device data.
The binding data-protection terms, in clause 4.1, state plainly that the operator does not transfer data to third parties and does not transfer it outside the EU — whereas the data in fact goes to Meta and Google (both in the US) and to Adform. Facebook / Meta, meanwhile, is named nowhere: not in the terms, not in the partner list, not in the TCF vendor list on which the consent panel itself is built.
Remediation: condition the loading and firing of the Facebook Pixel, Adform and DoubleClick on active consent, so that under a refusal (a zero TCF string) these requests do not go out and device data is not transmitted; stop the transfer of data to Meta before consent is obtained and disclose Meta as a recipient, or cease that transfer; and bring clause 4.1 of the data-protection terms into line with the facts — name Google, Adform and Meta as recipients and disclose the transfer to the US under Chapter V, or stop those transfers.
How to verify: download the file and compute its checksum — sha256sum file.har (Linux, macOS) or certutil -hashfile file.har SHA256 (Windows); it must match the one shown. The conclusions apply to the scope of this measurement — see the limitations of the method.
0334c62e8ca9c64e5439131ab6a93620b0ac6db80cf6ca3a05713da3417e6e80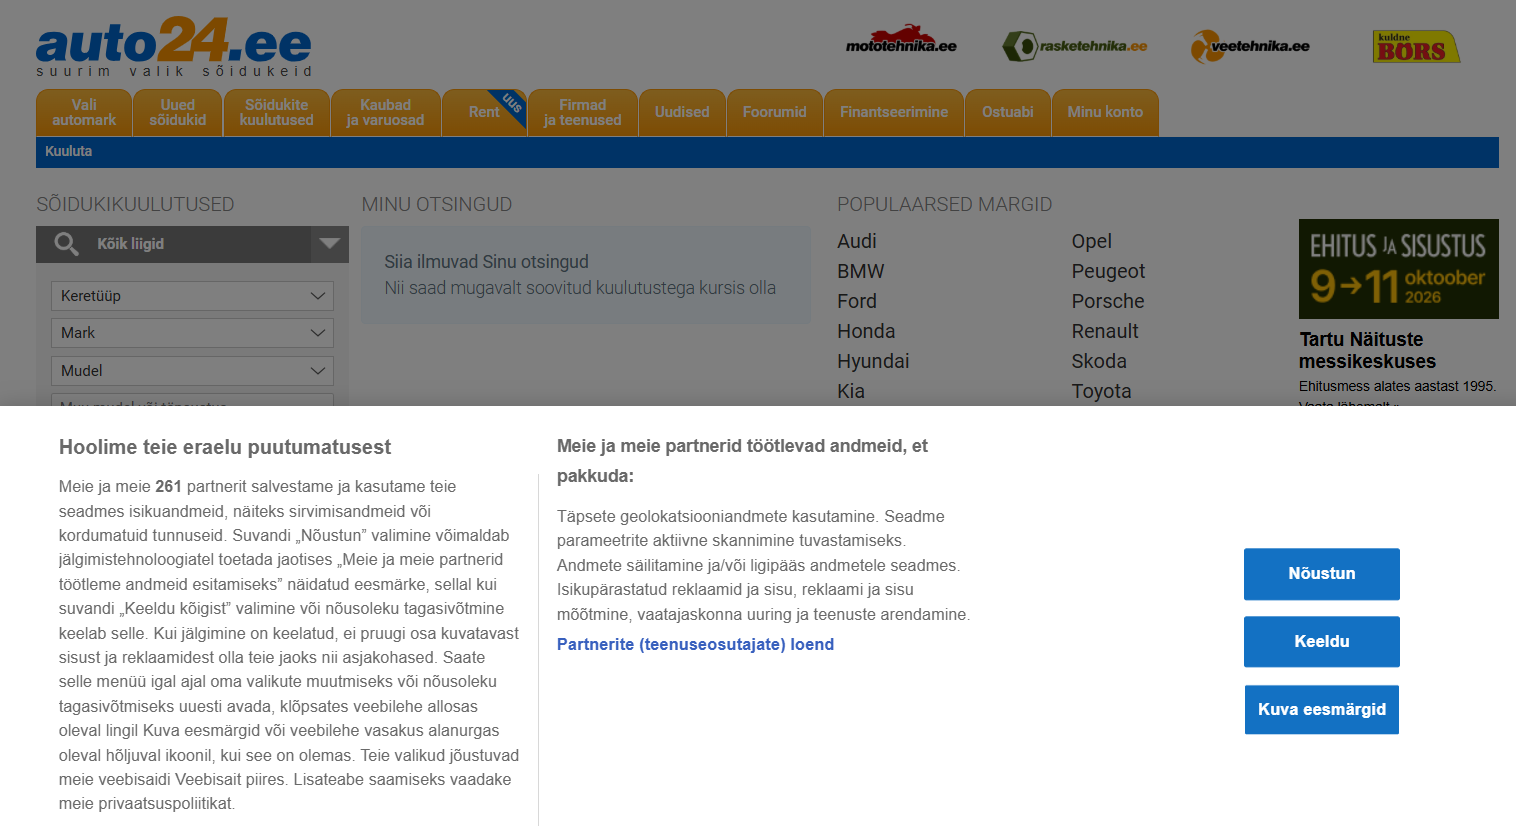
Want a response from the company about this audit? → Open the tool
Fill in once — it will be inserted into every letter below:
All fields are required to print the document — this is a formal requirement of the letter itself (the particulars of an official submission), not data collection: nothing is sent or saved anywhere, it all stays in your browser and disappears when you close the page. See the methodology for details.
RIA DigiDoc — phone · Smart-ID / Mobile-ID
Send this letter directly to the company first — before contacting the regulator it has the right to respond (GDPR Art. 12(3) — 30 days).
Тема: Запрос доступа к персональным данным (ст. 15 GDPR) — auto24.ee

Кому: [укажите адрес компании — DPO / поддержка / юридический отдел]
От: [Ваше имя], [контактный email]

Прошу предоставить доступ к моим персональным данным, обрабатываемым в связи с использованием сайта auto24.ee.

1. Категории данных и цели обработки (ст. 15(1)(a)-(c))
На основании независимого технического анализа сайта прошу подтвердить и подробно раскрыть следующие категории обработки:

1) На портале установлена платформа согласия OneTrust, которая загружается первой почти на каждой странице. Сохранённая строка согласия TCF v2 (CMP ID 28, создана 2026-09-05, за день до съёмки) кодирует ноль согласий: все 24 цели обработки — 0, все основания правомерного интереса — 0. Браузер вдобавок отправлял заголовок DNT: 1 (в 1013 запросах). Несмотря на это, сторонние трекеры срабатывают и передают данные. Facebook / Meta Pixel (ID 323626075634293) на страницах /ostuabi/ отправляет событие PageView с идентификатором браузера fbp, адресом и реферером страницы, часовым поясом и параметрами экрана — пиксель не завязан на согласие вовсе и срабатывает безусловно. Adform на +1032 мс передаёт язык, разрешение экрана 1920x1080, тип устройства и размеры рекламных мест; при этом он несёт строку согласия cmpgdprconsent с нулевым содержанием — то есть сам сигнал «согласия нет» передаётся, но обращение с данными об устройстве всё равно уходит. Google DoubleClick отправляет трекер показов /ddm/trackimp. Все обращения доставлены (FB /tr → 200, DoubleClick → 302→gif, Adform → 302→gif).

2) Обязывающие условия защиты данных AllePal (редакция от 10.02.2026) в пункте 4.1 прямо заявляют: «Me ei edasta Isikuandmeid kolmandatele isikutele» (данные третьим лицам не передаём, кроме законного основания) и «Samuti me ei edasta Isikuandmeid Euroopa Liidust väljapoole» (за пределы ЕС не передаём). Формулировка подтверждена на живом сайте. Фактически данные уходят в Meta (США) через Facebook Pixel, в Google (США) через DoubleClick и в Adform. Перечень обработчиков в пункте 4.2 сведён к категориям («бухгалтерия и прочие»); поимённо не назван ни один веб-получатель. Условия использования cookie (пункт 1.4) признают, что данные о поведении «могут передаваться рекламным сетям и поставщикам рекламных услуг», а список партнёров по адресу auto24.ee/cookies называет Google и Adform. Но Facebook / Meta не назван нигде — ни в обязывающих условиях, ни в вендорском списке TCF (Meta в нём отсутствует). То есть передача в Meta не раскрыта ни на одном уровне, а пункт 4.1 отрицает и её, и передачу в Google.


2. Получатели, сроки хранения и передача за пределы ЕЭЗ (ст. 15(1)(c)-(d), 46)
Прошу также указать полный список третьих лиц-получателей, применимые сроки хранения по каждой категории и правовые основания передачи данных за пределы ЕЭЗ, если таковая происходит. Полный технический разбор с доказательствами (сохранённый сетевой журнал, контрольная сумма SHA-256) опубликован по адресу: https://gdpru.eu/en/audits/ee-auto24-ee/

3. Автоматизированная обработка и профилирование (ст. 15(1)(h))
Прошу сообщить, применяется ли в отношении меня автоматизированное принятие решений или профилирование, и если да — раскрыть логику такой обработки.

С уважением,

[Ваше имя]
[контактный email]
[Страна]


[Дата]
Subject: Data access request (GDPR Art. 15) — auto24.ee

To: [insert the company's address — DPO / support / legal department]
From: [Your name], [contact email]

I request access to my personal data processed in connection with the website auto24.ee.

1. Categories of data and purposes of processing (Art. 15(1)(a)-(c))
Based on an independent technical analysis of the site, I request confirmation and detailed disclosure of the following categories of processing:

1) The portal has the OneTrust consent platform installed, and it loads first on almost every page. The stored TCF v2 consent string (CMP ID 28, created 2026-09-05, the day before the capture) encodes zero consent: all 24 processing purposes are 0, all legitimate-interest bases are 0. The browser additionally sent the DNT: 1 header (in 1013 requests). Despite this, third-party trackers fire and transmit data. On /ostuabi/ pages the Facebook / Meta Pixel (ID 323626075634293) sends a PageView event with the fbp browser identifier, the page URL and referrer, timezone and screen parameters — the pixel is not conditioned on consent at all and fires unconditionally. At +1032 ms Adform transmits language, screen resolution 1920x1080, device type and ad-slot dimensions; it carries a cmpgdprconsent string with zero content — that is, the 'no consent' signal itself is passed, yet the request with device data goes out anyway. Google DoubleClick sends the /ddm/trackimp impression tracker. All requests are delivered (FB /tr → 200, DoubleClick → 302→gif, Adform → 302→gif).

2) AllePal's binding data-protection terms (revision of 10.02.2026), in clause 4.1, state plainly: 'Me ei edasta Isikuandmeid kolmandatele isikutele' (we do not transfer personal data to third parties, except on a legal basis) and 'Samuti me ei edasta Isikuandmeid Euroopa Liidust väljapoole' (we also do not transfer personal data outside the EU). The wording is confirmed on the live site. In fact data goes to Meta (US) via the Facebook Pixel, to Google (US) via DoubleClick, and to Adform. The list of processors in clause 4.2 is reduced to categories ('accounting and others'); no web recipient is named. The cookie-use terms (clause 1.4) admit that behavioural data 'may be shared with advertising networks and ad service providers', and the partner list at auto24.ee/cookies names Google and Adform. But Facebook / Meta is named nowhere — neither in the binding terms nor in the TCF vendor list (Meta is absent from it). So the transfer to Meta is undisclosed at every level, while clause 4.1 denies both it and the transfer to Google.


2. Recipients, retention periods, and transfers outside the EEA (Art. 15(1)(c)-(d), 46)
I also request the full list of third-party recipients, the applicable retention period for each category, and the legal basis for any transfer of data outside the EEA. The full technical audit with evidence (saved network log, SHA-256 checksum) is published at: https://gdpru.eu/en/audits/ee-auto24-ee/

3. Automated processing and profiling (Art. 15(1)(h))
Please state whether I am subject to automated decision-making or profiling, and if so, disclose the logic involved.

Sincerely,

[Your name]
[contact email]
[Country]


[Date]
Teema: Isikuandmetele juurdepääsu taotlus (IKÜM art 15) — auto24.ee Kellele: [märkige ettevõtte aadress — DPO / tugi / juriidiline osakond] Kellelt: [Teie nimi], [kontakt-e-post] Palun anda mulle juurdepääs minu isikuandmetele, mida töödeldakse seoses veebisaidi auto24.ee kasutamisega. 1. Andmekategooriad ja töötlemise eesmärgid (IKÜM art 15(1)(a)-(c)) Sõltumatu tehnilise analüüsi põhjal palun kinnitada ja üksikasjalikult avaldada järgmised töötlemiskategooriad: 1) Portaalil on OneTrusti nõusoleku platvorm, mis laadib peaaegu igal lehel esimesena. Salvestatud TCF v2 nõusoleku string (CMP ID 28, loodud 2026-09-05, päev enne pildistamist) kodeerib nulli nõusolekud: kõik 24 töötlemise eesmärki on 0, kõik õigustatud huvi alused on 0. Brauser saatis ka DNT päise: 1 (1013 taotluses). Sellest hoolimata käivitavad ja edastavad kolmanda osapoole jälgijad andmeid. Facebook / Meta Pixel (ID 323626075634293) lehekülgedel /ostuabi/ saadab PageView sündmuse koos fbp brauseri ID, aadressi ja lehe suunaja, ajavööndi ja ekraani parameetritega - piksel ei ole üldse seotud nõusolekuga ja töötab tingimusteta. +1032 ms Adform edastab keele, ekraani eraldusvõime 1920x1080, seadme tüübi ja reklaamipindade suuruse; samal ajal kui see kannab nõusoleku stringi cmpgdprconsent null-sisuga - see tähendab, et edastatakse signaal "nõusolekuta", kuid seadme andmete käitlemine siiski lahkub. Google DoubleClick saadab kuvamise jälgija / ddm/trackimp. Kõik päringud toimetatakse kohale (FB /tr → 200, DoubleClick → 302→gif, Adform → 302→gif). 2) AllePal’i siduvad andmekaitsetingimused (muudetud 10.02.2026) punktis 4.1 on otseselt sätestatud: «Me ei edasta Isikuandmeid kolmandatele isikutele» (andmeid ei edastata kolmandatele isikutele, välja arvatud õiguslikul alusel) ja «Samuti me ei edasta Isikuandmeid Euroopa Liidust väljapoole» (me ei edastata väljapoole ELi). Sõnastus on kinnitatud otse veebilehel. Tegelikult lähevad andmed Metasse (USA) Facebooki Pixeli kaudu, Google'isse (USA) DoubleClicki ja Adformi kaudu. Punktis 4.2 esitatud volitatud töötlejate nimekiri on piiratud kategooriatega („raamatupidamine ja muu); veebisaajat ei nimetata. Küpsiste kasutustingimused (punkt 1.4) tunnistavad, et käitumuslikke andmeid „võib jagada reklaamivõrgustike ja reklaamiteenuste pakkujatega ning auto24.ee/cookies partnerite nimekiri viitab Google'ile ja Adformile. Kuid Facebook / Meta ei ole kuskil nimetatud, kas kohustuslikes terminites või TCF müüjate loendis (Meta puudub). See tähendab, et ülekannet Metale ei avalikustata ühelgi tasandil ja punkt 4.1 eitab nii seda kui ka edastamist Google'ile. 2. Vastuvõtjad, säilitustähtajad ja edastamine väljapoole EMP-d (IKÜM art 15(1)(c)-(d), 46) Palun samuti esitada täielik loetelu kolmandatest isikutest vastuvõtjatest, iga kategooria puhul kohaldatavad säilitustähtajad ning andmete EMP-välisele edastamisele kohaldatav õiguslik alus, kui selline edastamine toimub. Täielik tehniline analüüs koos tõenditega (salvestatud võrgulogi, SHA-256 kontrollsumma) on avaldatud aadressil: https://gdpru.eu/en/audits/ee-auto24-ee/ 3. Automatiseeritud töötlemine ja profiilianalüüs (IKÜM art 15(1)(h)) Palun teatada, kas minu suhtes kohaldatakse automatiseeritud otsuste tegemist või profiilianalüüsi, ning kui jah, siis avaldada selle loogika. Lugupidamisega, [Teie nimi] [kontakt-e-post] [Riik] [Kuupäev]
RIA DigiDoc — phone · Smart-ID / Mobile-ID
Where to file: Estonian Data Protection Inspectorate (AKI) — write to info@aki.ee
Important: AKI only handles submissions in Estonian. Translate the letter before sending.
The regulator reviews complaints in its national language. There is an officially translated template from the European Data Protection Board (EDPB) — you can use it instead of or alongside this letter: Official EDPB complaint form (PDF, your language)
Тема: Жалоба на обработку персональных данных — auto24.ee

1. Предмет жалобы
Я подаю жалобу в отношении обработки моих персональных данных сайтом auto24.ee.

2. Обстоятельства
Я посетил сайт auto24.ee и обнаружил признаки несоответствия обработки моих персональных данных требованиям GDPR. Технический разбор, опубликованный на gdpru.eu 06.09.2026 (открытая методология, воспроизводимые измерения), документирует следующие признаки:

1) На портале установлена платформа согласия OneTrust, которая загружается первой почти на каждой странице. Сохранённая строка согласия TCF v2 (CMP ID 28, создана 2026-09-05, за день до съёмки) кодирует ноль согласий: все 24 цели обработки — 0, все основания правомерного интереса — 0. Браузер вдобавок отправлял заголовок DNT: 1 (в 1013 запросах). Несмотря на это, сторонние трекеры срабатывают и передают данные. Facebook / Meta Pixel (ID 323626075634293) на страницах /ostuabi/ отправляет событие PageView с идентификатором браузера fbp, адресом и реферером страницы, часовым поясом и параметрами экрана — пиксель не завязан на согласие вовсе и срабатывает безусловно. Adform на +1032 мс передаёт язык, разрешение экрана 1920x1080, тип устройства и размеры рекламных мест; при этом он несёт строку согласия cmpgdprconsent с нулевым содержанием — то есть сам сигнал «согласия нет» передаётся, но обращение с данными об устройстве всё равно уходит. Google DoubleClick отправляет трекер показов /ddm/trackimp. Все обращения доставлены (FB /tr → 200, DoubleClick → 302→gif, Adform → 302→gif).

2) Обязывающие условия защиты данных AllePal (редакция от 10.02.2026) в пункте 4.1 прямо заявляют: «Me ei edasta Isikuandmeid kolmandatele isikutele» (данные третьим лицам не передаём, кроме законного основания) и «Samuti me ei edasta Isikuandmeid Euroopa Liidust väljapoole» (за пределы ЕС не передаём). Формулировка подтверждена на живом сайте. Фактически данные уходят в Meta (США) через Facebook Pixel, в Google (США) через DoubleClick и в Adform. Перечень обработчиков в пункте 4.2 сведён к категориям («бухгалтерия и прочие»); поимённо не назван ни один веб-получатель. Условия использования cookie (пункт 1.4) признают, что данные о поведении «могут передаваться рекламным сетям и поставщикам рекламных услуг», а список партнёров по адресу auto24.ee/cookies называет Google и Adform. Но Facebook / Meta не назван нигде — ни в обязывающих условиях, ни в вендорском списке TCF (Meta в нём отсутствует). То есть передача в Meta не раскрыта ни на одном уровне, а пункт 4.1 отрицает и её, и передачу в Google.

Полная техническая документация опубликована по адресу: https://gdpru.eu/en/audits/ee-auto24-ee/

3. Положения GDPR, соблюдение которых прошу проверить
ePrivacy — Директива 2002/58/EC, ст. 5(3) (в связке с GDPR Art. 6(1)(a)) — трекинг при зафиксированном отказе от согласия; GDPR Art. 5(1)(a) / Art. 13(1)(e) — прозрачность и получатели, противоречие внутри документов оператора

4. Требование
Прошу проверить изложенные обстоятельства и, если несоответствие подтвердится, принять меры, предусмотренные статьёй 58(2) GDPR.

5. Приложения
Полная доказательная база — HAR-файл, контрольная сумма SHA-256 и цитата из политики конфиденциальности сайта, документирующая указанное противоречие — опубликована и проверяема по ссылке в пункте 2 выше.

С уважением,

[Ваше имя]
[контактный email]
[Страна]


[Дата]
Subject: Complaint regarding personal data processing — auto24.ee

1. Subject of the complaint
I am filing a complaint regarding the processing of my personal data by the website auto24.ee.

2. Circumstances
I visited the website auto24.ee and found indications that the processing of my personal data does not comply with the GDPR. The technical analysis published on gdpru.eu on 6 September 2026 (open methodology, reproducible measurements) documents the following indications:

1) The portal has the OneTrust consent platform installed, and it loads first on almost every page. The stored TCF v2 consent string (CMP ID 28, created 2026-09-05, the day before the capture) encodes zero consent: all 24 processing purposes are 0, all legitimate-interest bases are 0. The browser additionally sent the DNT: 1 header (in 1013 requests). Despite this, third-party trackers fire and transmit data. On /ostuabi/ pages the Facebook / Meta Pixel (ID 323626075634293) sends a PageView event with the fbp browser identifier, the page URL and referrer, timezone and screen parameters — the pixel is not conditioned on consent at all and fires unconditionally. At +1032 ms Adform transmits language, screen resolution 1920x1080, device type and ad-slot dimensions; it carries a cmpgdprconsent string with zero content — that is, the 'no consent' signal itself is passed, yet the request with device data goes out anyway. Google DoubleClick sends the /ddm/trackimp impression tracker. All requests are delivered (FB /tr → 200, DoubleClick → 302→gif, Adform → 302→gif).

2) AllePal's binding data-protection terms (revision of 10.02.2026), in clause 4.1, state plainly: 'Me ei edasta Isikuandmeid kolmandatele isikutele' (we do not transfer personal data to third parties, except on a legal basis) and 'Samuti me ei edasta Isikuandmeid Euroopa Liidust väljapoole' (we also do not transfer personal data outside the EU). The wording is confirmed on the live site. In fact data goes to Meta (US) via the Facebook Pixel, to Google (US) via DoubleClick, and to Adform. The list of processors in clause 4.2 is reduced to categories ('accounting and others'); no web recipient is named. The cookie-use terms (clause 1.4) admit that behavioural data 'may be shared with advertising networks and ad service providers', and the partner list at auto24.ee/cookies names Google and Adform. But Facebook / Meta is named nowhere — neither in the binding terms nor in the TCF vendor list (Meta is absent from it). So the transfer to Meta is undisclosed at every level, while clause 4.1 denies both it and the transfer to Google.

Full technical documentation is published at: https://gdpru.eu/en/audits/ee-auto24-ee/

3. GDPR provisions I ask you to examine
ePrivacy — Directive 2002/58/EC, Art. 5(3) (in conjunction with GDPR Art. 6(1)(a)) — tracking despite a recorded refusal of consent; GDPR Art. 5(1)(a) / Art. 13(1)(e) — transparency and recipients, a contradiction within the operator's own documents

4. Request
I request that you examine the circumstances described and, if non-compliance is confirmed, apply the measures provided for in Article 58(2) GDPR.

5. Attachments
The full evidence base — the HAR file, its SHA-256 checksum and the quotation from the site's privacy policy documenting the stated contradiction — is published and verifiable at the link in point 2 above.

Sincerely,

[Your name]
[contact email]
[Country]


[Date]
1. Kaebuse ese Esitan kaebuse seoses minu isikuandmete töötlemisega veebisaidil auto24.ee. 2. Asjaolud Külastasin veebisaiti auto24.ee ja tuvastasin märke sellest, et minu isikuandmete töötlemine ei vasta isikuandmete kaitse üldmääruse (IKÜM) nõuetele. Tehniline analüüs, mis on avaldatud aadressil gdpru.eu 06.09.2026 (avatud metoodika, korratavad mõõtmised), dokumenteerib järgmist: 1) Portaalil on OneTrusti nõusoleku platvorm, mis laadib peaaegu igal lehel esimesena. Salvestatud TCF v2 nõusoleku string (CMP ID 28, loodud 2026-09-05, päev enne pildistamist) kodeerib nulli nõusolekud: kõik 24 töötlemise eesmärki on 0, kõik õigustatud huvi alused on 0. Brauser saatis ka DNT päise: 1 (1013 taotluses). Sellest hoolimata käivitavad ja edastavad kolmanda osapoole jälgijad andmeid. Facebook / Meta Pixel (ID 323626075634293) lehekülgedel /ostuabi/ saadab PageView sündmuse koos fbp brauseri ID, aadressi ja lehe suunaja, ajavööndi ja ekraani parameetritega - piksel ei ole üldse seotud nõusolekuga ja töötab tingimusteta. +1032 ms Adform edastab keele, ekraani eraldusvõime 1920x1080, seadme tüübi ja reklaamipindade suuruse; samal ajal kui see kannab nõusoleku stringi cmpgdprconsent null-sisuga - see tähendab, et edastatakse signaal "nõusolekuta", kuid seadme andmete käitlemine siiski lahkub. Google DoubleClick saadab kuvamise jälgija / ddm/trackimp. Kõik päringud toimetatakse kohale (FB /tr → 200, DoubleClick → 302→gif, Adform → 302→gif). 2) AllePal’i siduvad andmekaitsetingimused (muudetud 10.02.2026) punktis 4.1 on otseselt sätestatud: «Me ei edasta Isikuandmeid kolmandatele isikutele» (andmeid ei edastata kolmandatele isikutele, välja arvatud õiguslikul alusel) ja «Samuti me ei edasta Isikuandmeid Euroopa Liidust väljapoole» (me ei edastata väljapoole ELi). Sõnastus on kinnitatud otse veebilehel. Tegelikult lähevad andmed Metasse (USA) Facebooki Pixeli kaudu, Google'isse (USA) DoubleClicki ja Adformi kaudu. Punktis 4.2 esitatud volitatud töötlejate nimekiri on piiratud kategooriatega („raamatupidamine ja muu); veebisaajat ei nimetata. Küpsiste kasutustingimused (punkt 1.4) tunnistavad, et käitumuslikke andmeid „võib jagada reklaamivõrgustike ja reklaamiteenuste pakkujatega ning auto24.ee/cookies partnerite nimekiri viitab Google'ile ja Adformile. Kuid Facebook / Meta ei ole kuskil nimetatud, kas kohustuslikes terminites või TCF müüjate loendis (Meta puudub). See tähendab, et ülekannet Metale ei avalikustata ühelgi tasandil ja punkt 4.1 eitab nii seda kui ka edastamist Google'ile. Täielik tehniline dokumentatsioon on avaldatud aadressil: https://gdpru.eu/en/audits/ee-auto24-ee/ 3. Sätted, mille järgimist palun kontrollida e-privaatsus - direktiiv 2002/58/EÜ, artikli 5 lõige 3 (koosmõjus GDPRi artikli 6 lõike 1 punktiga a) - jälgimine registreeritud nõusoleku andmisest keeldumise korral; GDPR artikli 5 lõike 1 punkt a/artikli 13 lõike 1 punkt e – läbipaistvus ja saajad, vastuolud operaatori dokumentides 4. Nõue Palun kontrollida kirjeldatud asjaolusid ja mittevastavuse kinnitamisel kohaldada IKÜM artikli 58 lõikes 2 ette nähtud meetmeid. 5. Lisad Täielik tõendusmaterjal — HAR-fail, kontrollsumma SHA-256 ning veebisaidi privaatsuspoliitika tsitaat, mis dokumenteerib nimetatud vastuolu — on avaldatud ja kontrollitav punktis 2 viidatud lingil. Lugupidamisega, [Teie nimi] [kontakt-e-post] [Riik] [Kuupäev]