
The site of the Apotheka pharmacy chain and its online pharmacy — a single capture of the cookie-policy page, 65 requests, 11 nodes. The stack is modest: there are no ad networks or Facebook pixel in the capture, and of the third-party marketing components there is the CRM platform Custobar. The cookie banner offers refusal on the first screen («I accept necessary»), but its text treats continued browsing as consent, and the marketing platform Custobar itself loads and requests campaigns before any choice. Custobar is not named in the available documents. There is no consent-management platform (to gate the tags) in the capture. All of this on a pharmacy site, where the personal ID code for digi-prescriptions and data on medicine purchases are processed.
Request timeline
Declared versus actual
Transfer timings
custobar-*.js, the first third-party request; not named in the documents.
api/js/campaigns with an access_token — personalisation/advertising.
Form protection.
Detected trackers
- Custobar (script.custobar.com, api.custobar.com) — marketing CRM platform (marketing automation for retail); the script loads as the first third-party request at +371 ms, and at +2022 ms requests api/js/campaigns with an access_token. Before any choice in the banner. Not named in the available documents
- Google reCAPTCHA (www.google.com/recaptcha, www.gstatic.com) — form protection, functional
- First party and infrastructure: www.apotheka.ee (Magento platform), rx.apotheka.ee (prescription subdomain, digi-prescriptions), fonts.gstatic.com
- Capture-tool artefacts: edge.microsoft.com/translate, translate.googleapis.com, translate-pa.googleapis.com — the browser/page translation feature, not site components
Indicators of GDPR non-compliance
- ePrivacy — Directive 2002/58/EC, Art. 5(3) (in conjunction with GDPR Art. 6(1)(a)) — consent by continued browsing and marketing before the choiceThere is a cookie banner on the site and it offers refusal on the first screen (three buttons: «Cookie settings», «I accept necessary», «I accept all»). However, its text declares consent by continued browsing: «By continuing to use our site, you agree to the use of cookies» — the implied-consent model, which by the EDPB's position does not constitute valid consent. Meanwhile the marketing CRM platform Custobar loads as the very first third-party request at +371 ms and at +2022 ms requests campaigns (api.custobar.com/api/js/campaigns with an access_token) — before any choice by the user. The banner states its purpose as «personalising content and advertising», for which consent is required, but the marketing platform runs before the choice. There are no requests to a consent-management platform (Cookiebot/OneTrust/CookieYes etc.) in the capture — the banner is implemented by an in-house script and does not gate tag loading. On a pharmacy site, which processes the personal ID code for digi-prescriptions and data on medicine purchases, this matters especially.
- GDPR Art. 13(1)(e) — undisclosed recipient (Custobar)The available documents (a policy summary and the official apotheka.ee cookie policy) describe technical cookies (PHPSESSID, form_key, Magento store) and mention Google Analytics (_ga/_gid/_gat) as analytics. However, the marketing CRM platform Custobar, which actually loads in the capture and requests marketing campaigns, is not named in the documents. The official cookie policy meanwhile directly acknowledges that in certain situations information collected via cookies is passed to third parties, and that cookies are used for «offers directed specifically at you» — but the specific recipient (Custobar) is not disclosed.
Context
apotheka.ee is the site of the Apotheka pharmacy chain and its online pharmacy (e-apteek). The legal entity of the online pharmacy is OÜ Mustamäe Apteek (licence 285, Vae 16, Laagri); the loyalty programme is run by Allium UPI OÜ. A pharmacy is a specially sensitive category, close to medical: per the documents, the name, the personal ID code (needed to verify digi-prescriptions) and the history of medicine purchases are processed. The processing is described by a policy summary (in the set) and the official cookie policy on the site; the site runs on the Magento platform.
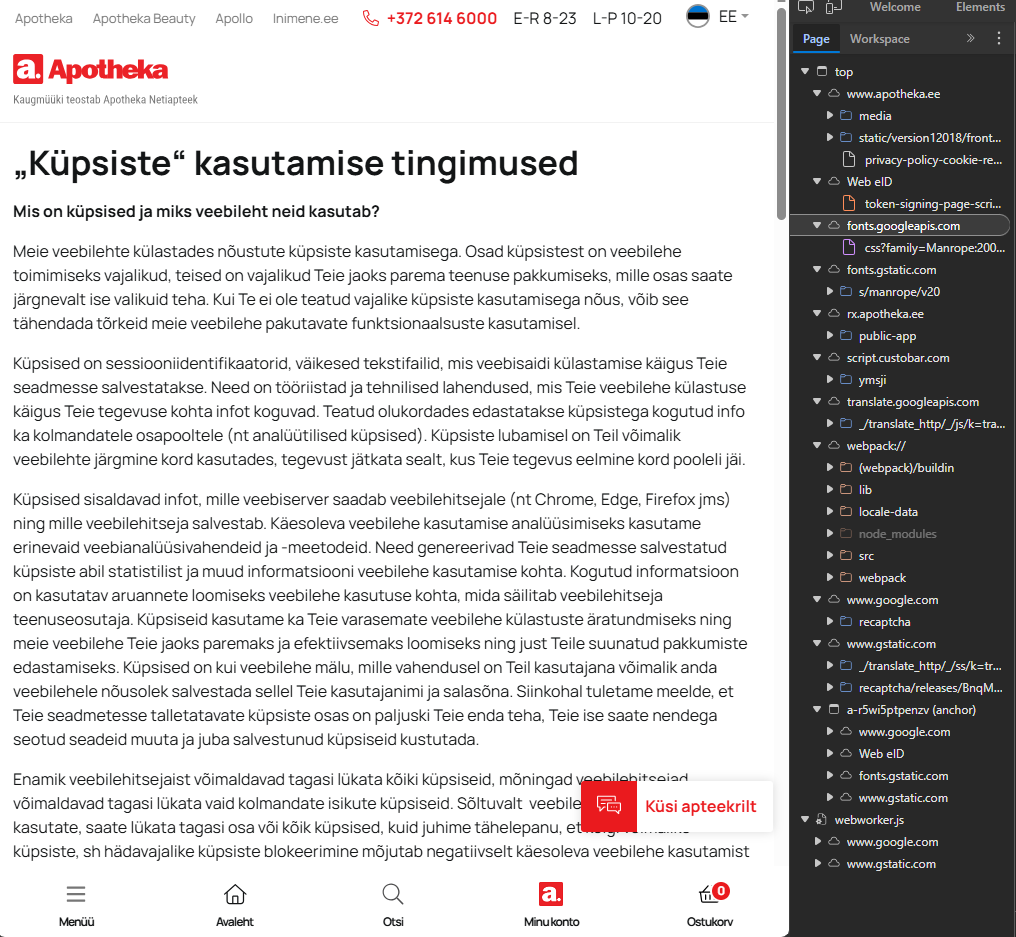
The capture is a single recording of the cookie-policy page (/privacy-policy-cookie-restriction-mode/): 65 requests, 11 nodes. The full policy was confirmed via its direct link: it confirms the consent-by-continued-browsing model.
Who data goes to directly
The marketing CRM platform Custobar (loads before the choice, requests campaigns). Functionally — reCAPTCHA, fonts, the prescription module rx.apotheka.ee. The requests to the translators (edge.microsoft.com/translate, translate.googleapis.com) are a capture-tool artefact (page translation in the browser), not site components. Google Analytics did not fire in this capture, although the policy mentions it.
Declared versus actual
The discrepancy here is at two points, both significant for the pharmacy context.
Consent is declared by continued browsing, and marketing loads before the choice. There is a cookie banner on the site and, it should be noted, it offers refusal on the first screen — three buttons: «Cookie settings», «I accept necessary», «I accept all». But its text directly treats passivity as consent: «By continuing to use our site, you agree to the use of cookies» — the implied-consent model, which the EDPB does not consider valid consent. And, more importantly, the marketing CRM platform Custobar loads as the very first third-party request at +371 ms, and at +2022 ms requests marketing campaigns (api.custobar.com/api/js/campaigns with an access_token) — before any choice by the user. The banner itself states its purpose as «personalising content and advertising», for which consent is required — but the personalisation platform runs before the user has chosen anything. There are no requests to a consent-management platform in the capture: the banner is implemented by an in-house script and does not hold tag loading back.
And the marketing recipient is not disclosed. The available documents describe technical cookies (PHPSESSID, form_key, Magento) and mention Google Analytics. But Custobar — a Finnish marketing-automation platform that actually loads and requests campaigns — is not named in the documents. The official cookie policy meanwhile directly acknowledges that information collected via cookies is passed to third parties in certain situations and used for «offers directed specifically at you». That is, the fact of transfer is acknowledged in general terms, but the specific recipient (Custobar) is not named — and on a pharmacy site, where the visitor views and buys medicines, personalising marketing on this data is especially sensitive.
Consent: what is proven and what is not
Proven: Custobar loads and requests campaigns before the choice. custobar-*.js at +371 ms, api/js/campaigns at +2022 ms; there is no consent-management platform in the capture.
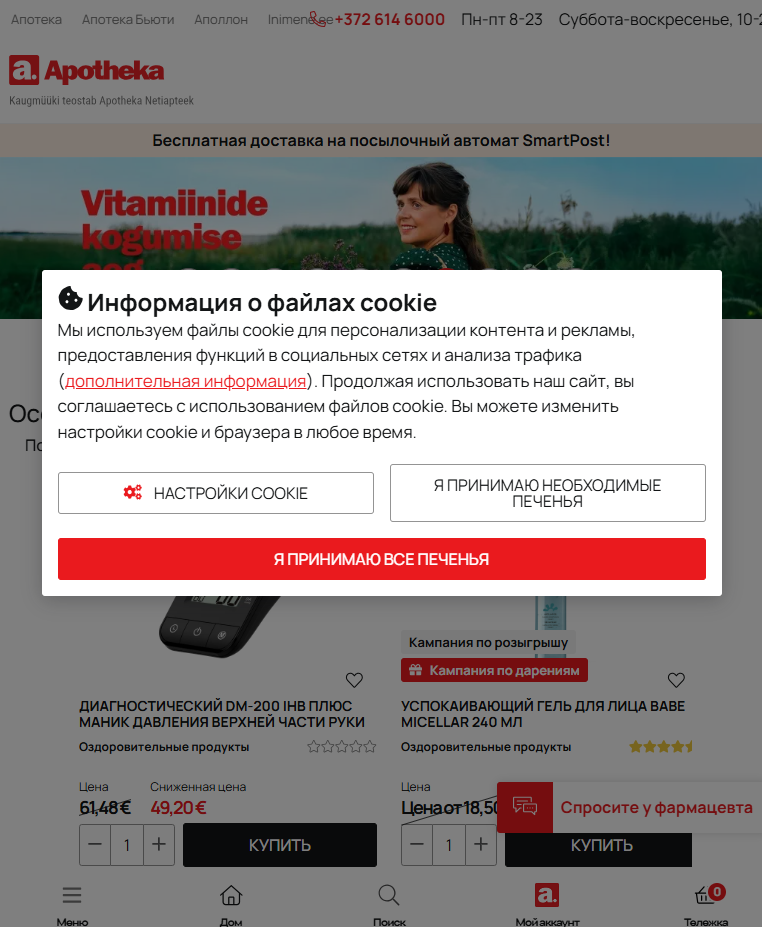
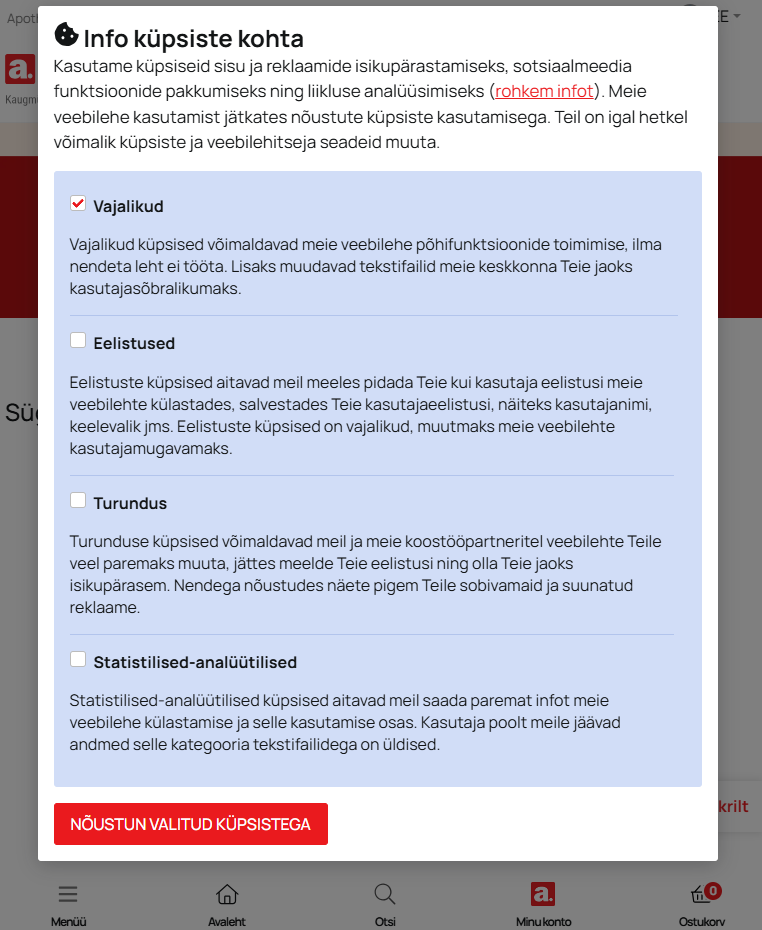
Proven: the banner declares consent by continued browsing. The screenshots record the text «By continuing to use our site, you agree» alongside three buttons (refusal on the first screen is present).
Proven: Custobar is not named in the documents. Neither the policy summary nor the official cookie policy contains the name Custobar.
Not established: the consent decision. There is no record of a choice in the capture; the key fact is that Custobar ran before the choice.
Not proven: the content of the Custobar requests and any transfer of medicine data. What exactly goes to Custobar beyond the campaign request and the access_token cannot be read from the cleaned file; the capture was made on the policy page, not on a medicine product page or in the basket, so the transfer of specific purchase data was not observed in this capture.
Not proven: the operation of Google Analytics. There are no GA requests in this capture, although the policy mentions _ga/_gid/_gat; behaviour may differ on other pages.
Observation boundaries
The capture covers a single page (the cookie policy) and records browser behaviour, not server-side processing: what Custobar does with the received data and how it is linked to the loyalty programme (Allium UPI OÜ) is not verified by a browser capture. The capture was made on the policy page, not on a medicine product page, in the prescription module or in the basket, so the processing of the personal ID code and data on medicine purchases was not observed in this capture — it relates to the ordering scenarios and is not verified by a browser capture on this page. The requests to the browser translators (edge.microsoft.com, translate.googleapis.com) are attributed to capture-tool artefacts. The full cookie policy could be confirmed via its direct link through search (the site did not respond on a direct visit); the consent-by-continued-browsing model reads directly from it.
The file is published cleaned of personal data (67 redactions, self-check clean); Custobar’s loading before the choice, the campaign request and the absence of requests to a consent platform can be verified directly against the published file and the screenshots. The banner and its buttons are from the screenshots (live UI).
The legal assessment is made by the competent authority — Andmekaitse Inspektsioon.
Conclusion
The pharmacy site keeps a cookie banner that offers refusal on the first screen («I accept necessary») — this is better than notice-only stubs. But the banner’s text treats continued browsing as consent (implied consent), which the European regulator does not recognise as valid, and the marketing CRM platform Custobar loads and requests campaigns before any choice — even though the banner itself names personalising advertising as its purpose. There is no consent-management platform that would hold the tags back until the choice in the capture.
Separately: Custobar is not named in the available documents, although the official cookie policy acknowledges in general terms the transfer of collected information to third parties and its use for directed offers. On a pharmacy site, where the personal ID code for digi-prescriptions and data on medicine purchases are processed, precision about who receives data and when it goes out matters especially.
Remediation: condition the loading of the marketing platform Custobar on actual consent, so that before the choice it neither loads nor requests campaigns; replace the «by continuing to browse, you agree» wording with a mechanism offering an active choice and tag gating by the decision (introduce a consent-management platform that holds loading back); name Custobar in the cookie policy as a recipient with its purpose stated; preserve the presence of a refusal button on the first screen and extend the «consent → loading» principle to the marketing stack, which is especially important for the pharmacy context.
How to verify: download the file and compute its checksum — sha256sum file.har (Linux, macOS) or certutil -hashfile file.har SHA256 (Windows); it must match the one shown. The conclusions apply to the scope of this measurement — see the limitations of the method.
55f3d0b041cedec467d2afb2d034a155335b49730a3dce1a1fb536b107317ad2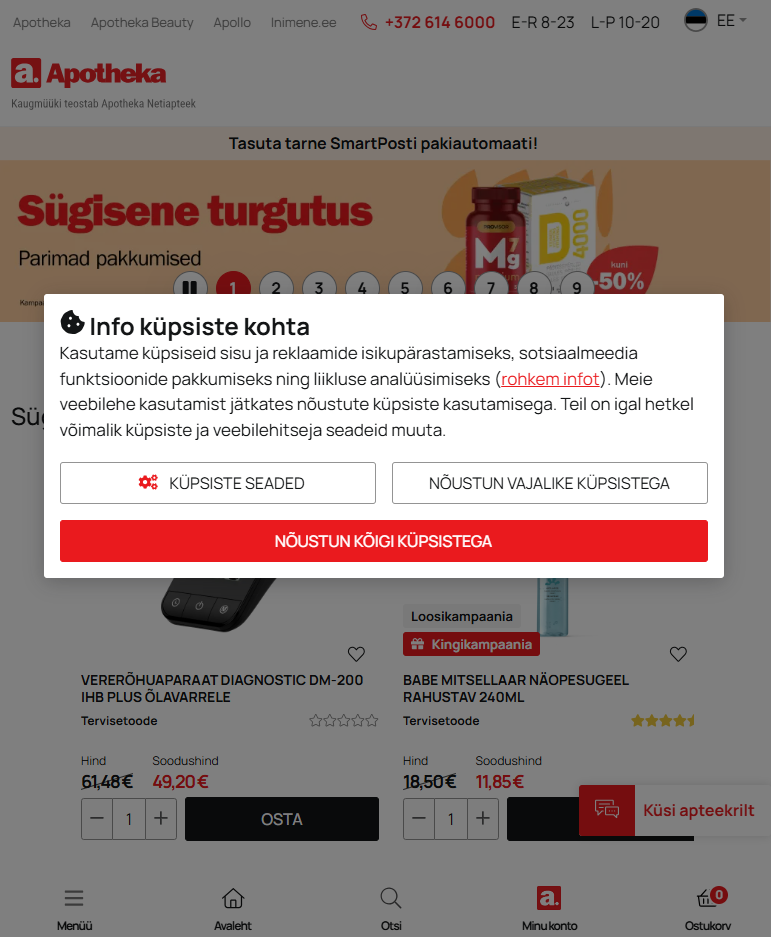
Want a response from the company about this audit? → Open the tool
Fill in once — it will be inserted into every letter below:
All fields are required to print the document — this is a formal requirement of the letter itself (the particulars of an official submission), not data collection: nothing is sent or saved anywhere, it all stays in your browser and disappears when you close the page. See the methodology for details.
RIA DigiDoc — phone · Smart-ID / Mobile-ID
Send this letter directly to the company first — before contacting the regulator it has the right to respond (GDPR Art. 12(3) — 30 days).
Тема: Запрос доступа к персональным данным (ст. 15 GDPR) — apotheka.ee

Кому: [укажите адрес компании — DPO / поддержка / юридический отдел]
От: [Ваше имя], [контактный email]

Прошу предоставить доступ к моим персональным данным, обрабатываемым в связи с использованием сайта apotheka.ee.

1. Категории данных и цели обработки (ст. 15(1)(a)-(c))
На основании независимого технического анализа сайта прошу подтвердить и подробно раскрыть следующие категории обработки:

1) Баннер cookie на сайте есть и даёт отказ на первом экране (три кнопки: «Настройки cookie», «Я принимаю необходимые», «Я принимаю все»). Однако его текст декларирует согласие через продолжение просмотра: «Продолжая использовать наш сайт, вы соглашаетесь с использованием файлов cookie» — модель implied consent, которая по позиции EDPB действительного согласия не образует. При этом маркетинговая CRM-платформа Custobar грузится первым же сторонним запросом на +371 мс и на +2022 мс запрашивает кампании (api.custobar.com/api/js/campaigns с access_token) — до какого-либо выбора пользователя. Баннер заявляет целью «персонализацию контента и рекламы», для чего требуется согласие, но рекламно-маркетинговая платформа отрабатывает раньше выбора. Обращений к платформе управления согласием (Cookiebot/OneTrust/CookieYes и т.п.) в замере нет — баннер реализован собственным скриптом и загрузку тегов не гейтит. На сайте аптеки, обрабатывающем личный код для диги-рецептов и данные о покупке лекарств, это особенно значимо.

2) Доступные документы (выжимка политики и официальная куки-политика apotheka.ee) описывают технические куки (PHPSESSID, form_key, Magento store) и упоминают Google Analytics (_ga/_gid/_gat) как аналитику. Однако маркетинговая CRM-платформа Custobar, которая фактически грузится в замере и запрашивает маркетинговые кампании, в документах по имени не названа. Официальная куки-политика при этом прямо признаёт, что в определённых ситуациях информация, собранная через cookie, передаётся третьим сторонам, и что cookie используются для «направленных именно вам предложений», — но конкретный получатель (Custobar) не раскрыт.


2. Получатели, сроки хранения и передача за пределы ЕЭЗ (ст. 15(1)(c)-(d), 46)
Прошу также указать полный список третьих лиц-получателей, применимые сроки хранения по каждой категории и правовые основания передачи данных за пределы ЕЭЗ, если таковая происходит. Полный технический разбор с доказательствами (сохранённый сетевой журнал, контрольная сумма SHA-256) опубликован по адресу: https://gdpru.eu/en/audits/ee-apotheka-ee/

3. Автоматизированная обработка и профилирование (ст. 15(1)(h))
Прошу сообщить, применяется ли в отношении меня автоматизированное принятие решений или профилирование, и если да — раскрыть логику такой обработки.

С уважением,

[Ваше имя]
[контактный email]
[Страна]


[Дата]
Subject: Data access request (GDPR Art. 15) — apotheka.ee

To: [insert the company's address — DPO / support / legal department]
From: [Your name], [contact email]

I request access to my personal data processed in connection with the website apotheka.ee.

1. Categories of data and purposes of processing (Art. 15(1)(a)-(c))
Based on an independent technical analysis of the site, I request confirmation and detailed disclosure of the following categories of processing:

1) There is a cookie banner on the site and it offers refusal on the first screen (three buttons: «Cookie settings», «I accept necessary», «I accept all»). However, its text declares consent by continued browsing: «By continuing to use our site, you agree to the use of cookies» — the implied-consent model, which by the EDPB's position does not constitute valid consent. Meanwhile the marketing CRM platform Custobar loads as the very first third-party request at +371 ms and at +2022 ms requests campaigns (api.custobar.com/api/js/campaigns with an access_token) — before any choice by the user. The banner states its purpose as «personalising content and advertising», for which consent is required, but the marketing platform runs before the choice. There are no requests to a consent-management platform (Cookiebot/OneTrust/CookieYes etc.) in the capture — the banner is implemented by an in-house script and does not gate tag loading. On a pharmacy site, which processes the personal ID code for digi-prescriptions and data on medicine purchases, this matters especially.

2) The available documents (a policy summary and the official apotheka.ee cookie policy) describe technical cookies (PHPSESSID, form_key, Magento store) and mention Google Analytics (_ga/_gid/_gat) as analytics. However, the marketing CRM platform Custobar, which actually loads in the capture and requests marketing campaigns, is not named in the documents. The official cookie policy meanwhile directly acknowledges that in certain situations information collected via cookies is passed to third parties, and that cookies are used for «offers directed specifically at you» — but the specific recipient (Custobar) is not disclosed.


2. Recipients, retention periods, and transfers outside the EEA (Art. 15(1)(c)-(d), 46)
I also request the full list of third-party recipients, the applicable retention period for each category, and the legal basis for any transfer of data outside the EEA. The full technical audit with evidence (saved network log, SHA-256 checksum) is published at: https://gdpru.eu/en/audits/ee-apotheka-ee/

3. Automated processing and profiling (Art. 15(1)(h))
Please state whether I am subject to automated decision-making or profiling, and if so, disclose the logic involved.

Sincerely,

[Your name]
[contact email]
[Country]


[Date]
Teema: Isikuandmetele juurdepääsu taotlus (IKÜM art 15) — apotheka.ee

Kellele: [märkige ettevõtte aadress — DPO / tugi / juriidiline osakond]
Kellelt: [Teie nimi], [kontakt-e-post]

Palun anda mulle juurdepääs minu isikuandmetele, mida töödeldakse seoses veebisaidi apotheka.ee kasutamisega.

1. Andmekategooriad ja töötlemise eesmärgid (IKÜM art 15(1)(a)-(c))
Sõltumatu tehnilise analüüsi põhjal palun kinnitada ja üksikasjalikult avaldada järgmised töötlemiskategooriad:

1) Saidil on küpsisebänner ja esimesel ekraanil keeldutakse (kolm nuppu: „Küpsiste sätted, „Ma nõustun vajalikega, „Ma nõustun kõigiga). Kuid selle tekst kinnitab nõusolekut jätkuva sirvimise kaudu: „Jätkates meie saidi kasutamist, nõustute küpsiste kasutamisega – kaudne nõusoleku mudel, mis ei moodusta kehtivat nõusolekut EDPB positsiooni alusel. Samal ajal laaditakse turundus CRM-platvorm Custobar esimese kolmanda osapoole taotlusega +371 ms ja +2022 ms päringute kampaaniatele (api.custobar.com/api/js/campaigns koos juurdepääsuloaga) - kuni kasutaja valikuni. Bänneris on kirjas eesmärk „sisu ja reklaami isikupärastamine, mis nõuab nõusolekut, kuid reklaami- ja turundusplatvorm töötab enne valikut. Mõõtmisel nõusoleku haldamise platvormile (Cookiebot/OneTrust/CookieYes jne) kaebusi ei esitata - bännerit rakendatakse oma skriptiga ja siltide allalaadimine ei õnnestu. Eriti oluline on see apteegi veebilehel, kus töödeldakse digiretseptide isikukoodi ja ravimite ostmise andmeid.

2) Olemasolevad dokumendid (policy squeeze ja ametlik küpsisepoliitika apotheka.ee) kirjeldavad tehnilisi küpsiseid (PHPSESSID, vormivõti, Magento kauplus) ja viitavad Google Analyticsile (ga/ gid/ gat) kui analüüsile. Kuid Custobar turundus CRM-platvormi, mis on tegelikult laaditud arvestisse ja taotleb turunduskampaaniaid, dokumentides ei nimetata. Ametlik küpsisepoliitika tunnistab selgesõnaliselt, et teatud olukordades jagatakse küpsiste kaudu kogutud teavet kolmandate osapooltega ja et küpsiseid kasutatakse „konkreetselt teile suunatud pakkumiste jaoks, kuid konkreetset saajat (Custobar) ei avaldata.


2. Vastuvõtjad, säilitustähtajad ja edastamine väljapoole EMP-d (IKÜM art 15(1)(c)-(d), 46)
Palun samuti esitada täielik loetelu kolmandatest isikutest vastuvõtjatest, iga kategooria puhul kohaldatavad säilitustähtajad ning andmete EMP-välisele edastamisele kohaldatav õiguslik alus, kui selline edastamine toimub. Täielik tehniline analüüs koos tõenditega (salvestatud võrgulogi, SHA-256 kontrollsumma) on avaldatud aadressil: https://gdpru.eu/en/audits/ee-apotheka-ee/

3. Automatiseeritud töötlemine ja profiilianalüüs (IKÜM art 15(1)(h))
Palun teatada, kas minu suhtes kohaldatakse automatiseeritud otsuste tegemist või profiilianalüüsi, ning kui jah, siis avaldada selle loogika.

Lugupidamisega,

[Teie nimi]
[kontakt-e-post]
[Riik]


[Kuupäev]
RIA DigiDoc — phone · Smart-ID / Mobile-ID
Where to file: Estonian Data Protection Inspectorate (AKI) — write to info@aki.ee
Important: AKI only handles submissions in Estonian. Translate the letter before sending.
The regulator reviews complaints in its national language. There is an officially translated template from the European Data Protection Board (EDPB) — you can use it instead of or alongside this letter: Official EDPB complaint form (PDF, your language)
Тема: Жалоба на обработку персональных данных — apotheka.ee

1. Предмет жалобы
Я подаю жалобу в отношении обработки моих персональных данных сайтом apotheka.ee.

2. Обстоятельства
Я посетил сайт apotheka.ee и обнаружил признаки несоответствия обработки моих персональных данных требованиям GDPR. Технический разбор, опубликованный на gdpru.eu 13.09.2026 (открытая методология, воспроизводимые измерения), документирует следующие признаки:

1) Баннер cookie на сайте есть и даёт отказ на первом экране (три кнопки: «Настройки cookie», «Я принимаю необходимые», «Я принимаю все»). Однако его текст декларирует согласие через продолжение просмотра: «Продолжая использовать наш сайт, вы соглашаетесь с использованием файлов cookie» — модель implied consent, которая по позиции EDPB действительного согласия не образует. При этом маркетинговая CRM-платформа Custobar грузится первым же сторонним запросом на +371 мс и на +2022 мс запрашивает кампании (api.custobar.com/api/js/campaigns с access_token) — до какого-либо выбора пользователя. Баннер заявляет целью «персонализацию контента и рекламы», для чего требуется согласие, но рекламно-маркетинговая платформа отрабатывает раньше выбора. Обращений к платформе управления согласием (Cookiebot/OneTrust/CookieYes и т.п.) в замере нет — баннер реализован собственным скриптом и загрузку тегов не гейтит. На сайте аптеки, обрабатывающем личный код для диги-рецептов и данные о покупке лекарств, это особенно значимо.

2) Доступные документы (выжимка политики и официальная куки-политика apotheka.ee) описывают технические куки (PHPSESSID, form_key, Magento store) и упоминают Google Analytics (_ga/_gid/_gat) как аналитику. Однако маркетинговая CRM-платформа Custobar, которая фактически грузится в замере и запрашивает маркетинговые кампании, в документах по имени не названа. Официальная куки-политика при этом прямо признаёт, что в определённых ситуациях информация, собранная через cookie, передаётся третьим сторонам, и что cookie используются для «направленных именно вам предложений», — но конкретный получатель (Custobar) не раскрыт.

Полная техническая документация опубликована по адресу: https://gdpru.eu/en/audits/ee-apotheka-ee/

3. Положения GDPR, соблюдение которых прошу проверить
ePrivacy — Директива 2002/58/EC, ст. 5(3) (в связке с GDPR Art. 6(1)(a)) — согласие через продолжение просмотра и маркетинг до выбора; GDPR Art. 13(1)(e) — нераскрытый получатель (Custobar)

4. Требование
Прошу проверить изложенные обстоятельства и, если несоответствие подтвердится, принять меры, предусмотренные статьёй 58(2) GDPR.

5. Приложения
Полная доказательная база — HAR-файл, контрольная сумма SHA-256 и цитата из политики конфиденциальности сайта, документирующая указанное противоречие — опубликована и проверяема по ссылке в пункте 2 выше.

С уважением,

[Ваше имя]
[контактный email]
[Страна]


[Дата]
Subject: Complaint regarding personal data processing — apotheka.ee

1. Subject of the complaint
I am filing a complaint regarding the processing of my personal data by the website apotheka.ee.

2. Circumstances
I visited the website apotheka.ee and found indications that the processing of my personal data does not comply with the GDPR. The technical analysis published on gdpru.eu on 13 September 2026 (open methodology, reproducible measurements) documents the following indications:

1) There is a cookie banner on the site and it offers refusal on the first screen (three buttons: «Cookie settings», «I accept necessary», «I accept all»). However, its text declares consent by continued browsing: «By continuing to use our site, you agree to the use of cookies» — the implied-consent model, which by the EDPB's position does not constitute valid consent. Meanwhile the marketing CRM platform Custobar loads as the very first third-party request at +371 ms and at +2022 ms requests campaigns (api.custobar.com/api/js/campaigns with an access_token) — before any choice by the user. The banner states its purpose as «personalising content and advertising», for which consent is required, but the marketing platform runs before the choice. There are no requests to a consent-management platform (Cookiebot/OneTrust/CookieYes etc.) in the capture — the banner is implemented by an in-house script and does not gate tag loading. On a pharmacy site, which processes the personal ID code for digi-prescriptions and data on medicine purchases, this matters especially.

2) The available documents (a policy summary and the official apotheka.ee cookie policy) describe technical cookies (PHPSESSID, form_key, Magento store) and mention Google Analytics (_ga/_gid/_gat) as analytics. However, the marketing CRM platform Custobar, which actually loads in the capture and requests marketing campaigns, is not named in the documents. The official cookie policy meanwhile directly acknowledges that in certain situations information collected via cookies is passed to third parties, and that cookies are used for «offers directed specifically at you» — but the specific recipient (Custobar) is not disclosed.

Full technical documentation is published at: https://gdpru.eu/en/audits/ee-apotheka-ee/

3. GDPR provisions I ask you to examine
ePrivacy — Directive 2002/58/EC, Art. 5(3) (in conjunction with GDPR Art. 6(1)(a)) — consent by continued browsing and marketing before the choice; GDPR Art. 13(1)(e) — undisclosed recipient (Custobar)

4. Request
I request that you examine the circumstances described and, if non-compliance is confirmed, apply the measures provided for in Article 58(2) GDPR.

5. Attachments
The full evidence base — the HAR file, its SHA-256 checksum and the quotation from the site's privacy policy documenting the stated contradiction — is published and verifiable at the link in point 2 above.

Sincerely,

[Your name]
[contact email]
[Country]


[Date]
1. Kaebuse ese
Esitan kaebuse seoses minu isikuandmete töötlemisega veebisaidil apotheka.ee.

2. Asjaolud
Külastasin veebisaiti apotheka.ee ja tuvastasin märke sellest, et minu isikuandmete töötlemine ei vasta isikuandmete kaitse üldmääruse (IKÜM) nõuetele. Tehniline analüüs, mis on avaldatud aadressil gdpru.eu 13.09.2026 (avatud metoodika, korratavad mõõtmised), dokumenteerib järgmist:

1) Saidil on küpsisebänner ja esimesel ekraanil keeldutakse (kolm nuppu: „Küpsiste sätted, „Ma nõustun vajalikega, „Ma nõustun kõigiga). Kuid selle tekst kinnitab nõusolekut jätkuva sirvimise kaudu: „Jätkates meie saidi kasutamist, nõustute küpsiste kasutamisega – kaudne nõusoleku mudel, mis ei moodusta kehtivat nõusolekut EDPB positsiooni alusel. Samal ajal laaditakse turundus CRM-platvorm Custobar esimese kolmanda osapoole taotlusega +371 ms ja +2022 ms päringute kampaaniatele (api.custobar.com/api/js/campaigns koos juurdepääsuloaga) - kuni kasutaja valikuni. Bänneris on kirjas eesmärk „sisu ja reklaami isikupärastamine, mis nõuab nõusolekut, kuid reklaami- ja turundusplatvorm töötab enne valikut. Mõõtmisel nõusoleku haldamise platvormile (Cookiebot/OneTrust/CookieYes jne) kaebusi ei esitata - bännerit rakendatakse oma skriptiga ja siltide allalaadimine ei õnnestu. Eriti oluline on see apteegi veebilehel, kus töödeldakse digiretseptide isikukoodi ja ravimite ostmise andmeid.

2) Olemasolevad dokumendid (policy squeeze ja ametlik küpsisepoliitika apotheka.ee) kirjeldavad tehnilisi küpsiseid (PHPSESSID, vormivõti, Magento kauplus) ja viitavad Google Analyticsile (ga/ gid/ gat) kui analüüsile. Kuid Custobar turundus CRM-platvormi, mis on tegelikult laaditud arvestisse ja taotleb turunduskampaaniaid, dokumentides ei nimetata. Ametlik küpsisepoliitika tunnistab selgesõnaliselt, et teatud olukordades jagatakse küpsiste kaudu kogutud teavet kolmandate osapooltega ja et küpsiseid kasutatakse „konkreetselt teile suunatud pakkumiste jaoks, kuid konkreetset saajat (Custobar) ei avaldata.

Täielik tehniline dokumentatsioon on avaldatud aadressil: https://gdpru.eu/en/audits/ee-apotheka-ee/

3. Sätted, mille järgimist palun kontrollida
e-privaatsus - direktiiv 2002/58/EÜ, artikli 5 lõige 3 (koosmõjus GDPRi artikli 6 lõike 1 punktiga a) - nõusolek jätkuva sirvimise ja turustamise kaudu enne valikut; GDPR artikkel 13(1)(e) Avaldamata saaja (Custobar)

4. Nõue
Palun kontrollida kirjeldatud asjaolusid ja mittevastavuse kinnitamisel kohaldada IKÜM artikli 58 lõikes 2 ette nähtud meetmeid.

5. Lisad
Täielik tõendusmaterjal — HAR-fail, kontrollsumma SHA-256 ning veebisaidi privaatsuspoliitika tsitaat, mis dokumenteerib nimetatud vastuolu — on avaldatud ja kontrollitav punktis 2 viidatud lingil.

Lugupidamisega,

[Teie nimi]
[kontakt-e-post]
[Riik]


[Kuupäev]